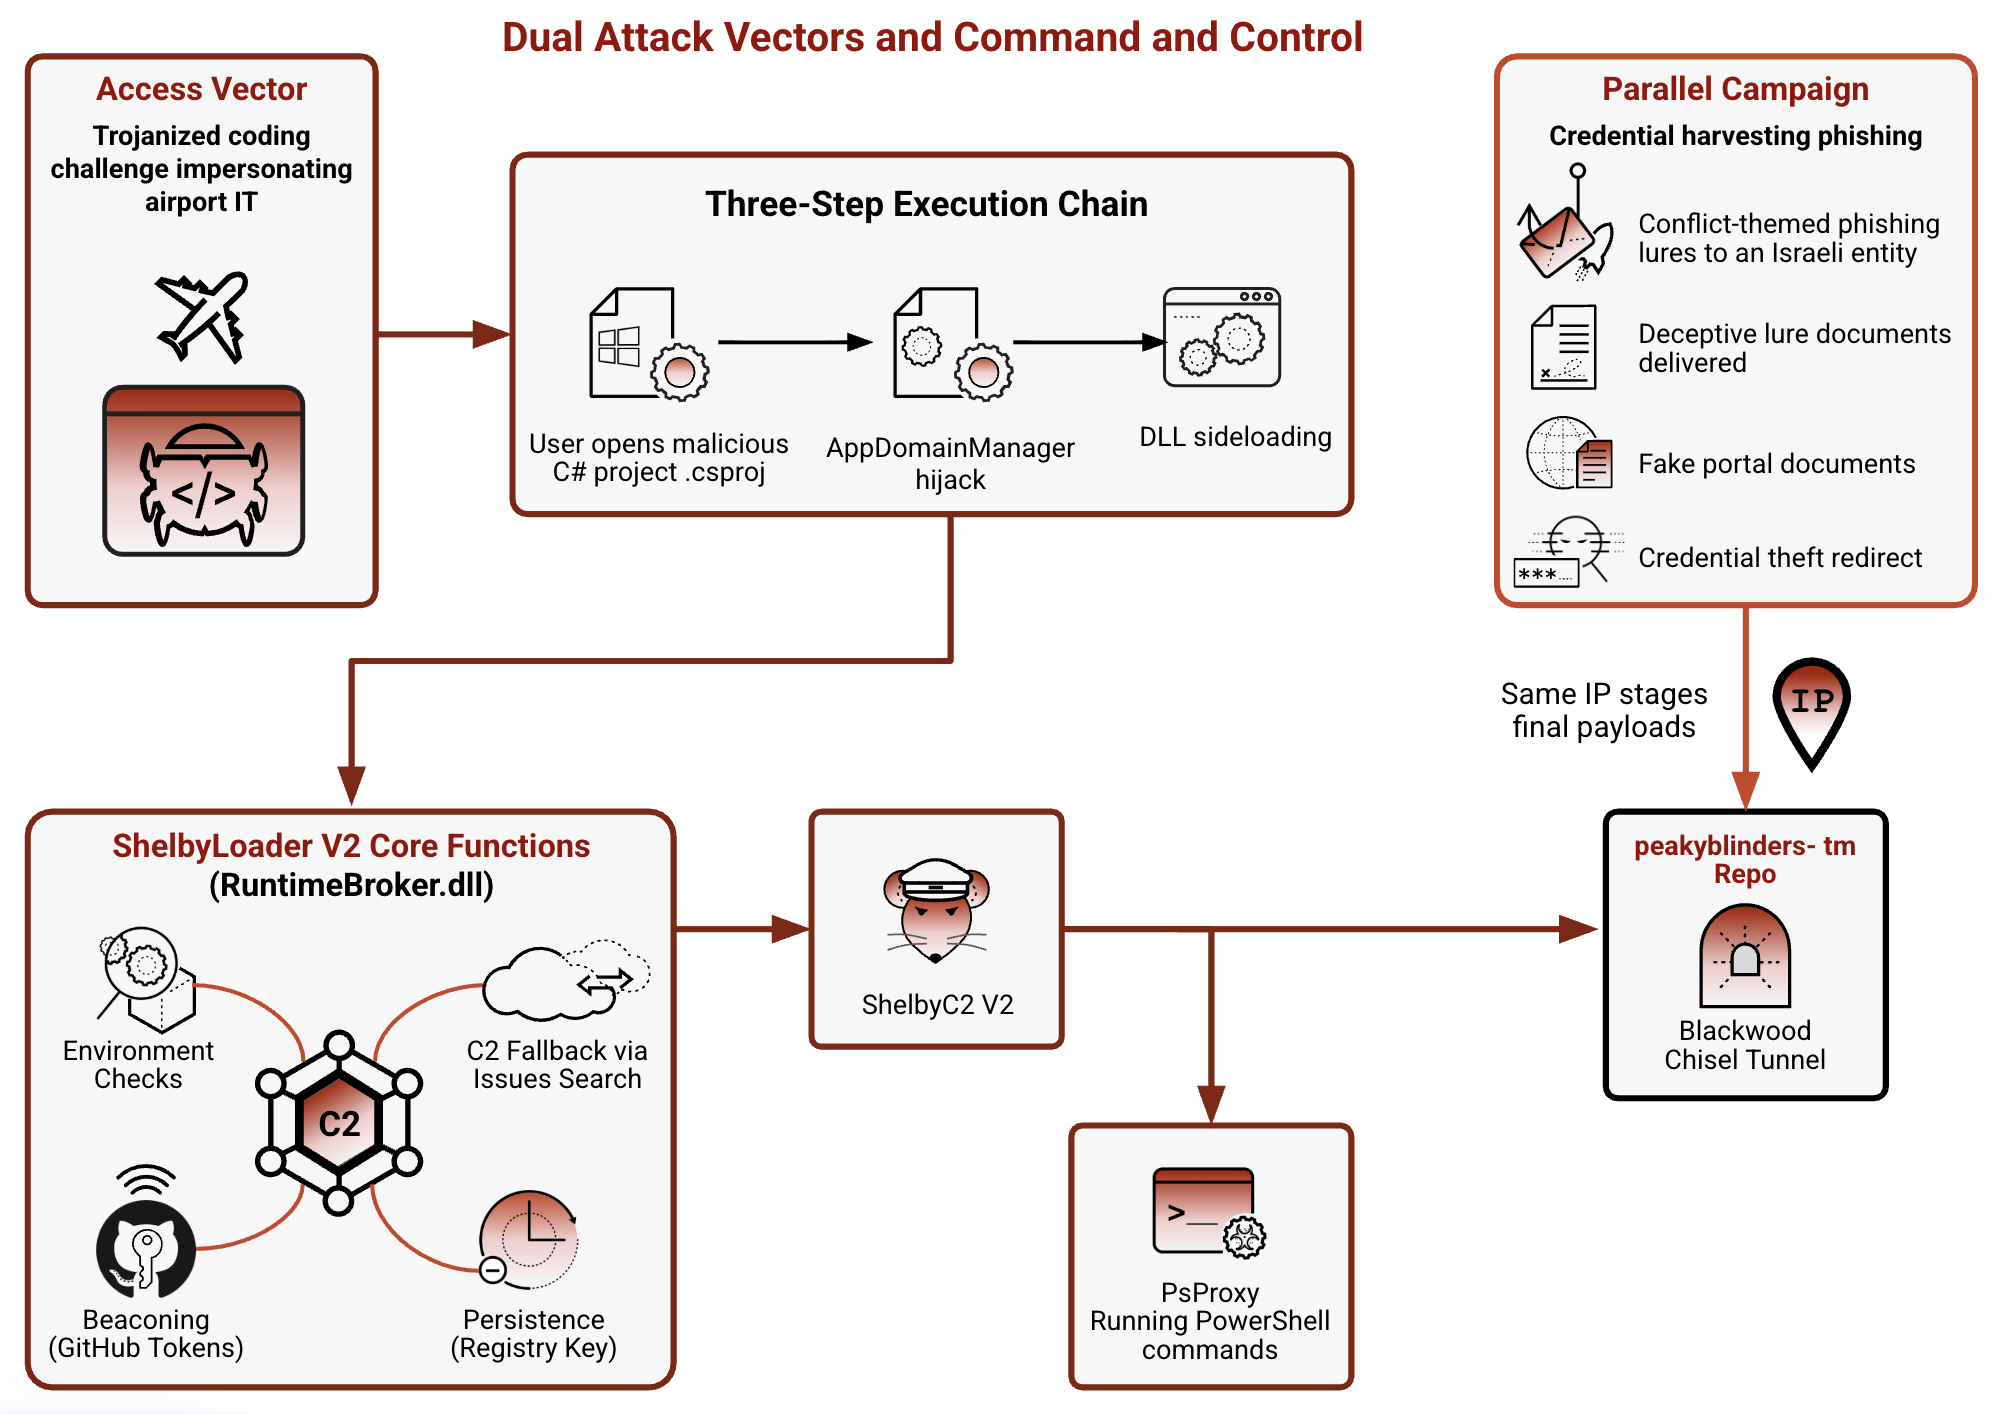
An Iranian state-aligned threat actor tracked as CL-STA-1178 ran the Blinder Tunnel campaign by impersonating the Dubai Airports IT department to deliver trojanized coding challenges, then used GitHub-based C2, AppDomainManager hijacking, DLL sideloading, and custom malware to target Iraqi critical infrastructure and other Middle East entities. The operation also overlapped with a separate credential-harvesting campaign against an Israeli entity and exposed strong ties to Peaky Blinders-themed infrastructure, ShelbyLoader V2, ShelbyC2 V2, and Blackwood. #CLSTA1178 #BlinderTunnel #ShelbyLoaderV2 #ShelbyC2V2 #Blackwood #DubaiAirports #GitHub
Keypoints
- Unit 42 attributes the activity cluster CL-STA-1178 to an Iranian state-aligned threat actor with high confidence.
- The main campaign, named Blinder Tunnel, targeted Iraqi critical infrastructure after staging activity observed as early as November 2025.
- Attackers impersonated the Dubai Airports IT department and used a trojanized coding challenge to lure a high-value target in Iraq.
- The initial infection chain used a malicious .csproj file, AppDomainManager hijacking, and DLL sideloading to execute payloads covertly.
- Custom malware included ShelbyLoader V2, ShelbyC2 V2, PsProxy.dll, and Blackwood, with Blackwood used to load Chisel for tunneling.
- GitHub was heavily abused for command-and-control, including repository files, GitHub Issues, and encrypted comments as a resilient fallback channel.
- Operational mistakes and reused infrastructure linked the campaign to a separate phishing and credential-harvesting operation targeting an Israeli entity.
MITRE Techniques
- [T1566.001] Phishing: Spearphishing Attachment – Used recruitment-themed archives and installers to deliver the malicious payloads to targets (‘trojanized coding challenges’ and ‘download and install a file named Dubai Airport Careers’).
- [T1204.002] User Execution: Malicious File – The target was instructed to open, build, and run the project so the malicious code would execute (‘build and run the project to find and fix the bug’).
- [T1127.001] Trusted Developer Utilities Proxy Execution: MSBuild – The attackers weaponized a .csproj file so Visual Studio/MSBuild executed their code during design-time build (‘Visual Studio runs a specific command called GetFrameworkPaths’ and ‘executed the payload’).
- [T1574.004] Hijack Execution Flow: .NET AppDomainManager Hijacking – They modified the RuntimeBroker.exe.config file to replace the default startup manager and run malicious code first (‘replace the application’s default startup manager with their own malicious version’).
- [T1574.002] Hijack Execution Flow: DLL Side-Loading – The campaign used a renamed Microsoft binary to load malicious DLLs into memory (‘perform DLL sideloading, executing the malicious payload by loading RuntimeBroker.dll into memory’).
- [T1112] Modify Registry – Persistence was established by creating a registry Run value (‘creating a MicrosoftRuntime value under the current user startup registry key’).
- [T1027] Obfuscated Files or Information – The .NET binaries were obscured with Obfuscar and used runtime string decryption (‘using the open-source obfuscator Obfuscar’).
- [T1027.013] Obfuscated Files or Information: Encrypted/Encoded File – Payloads, configuration data, and tunnel components were AES/RC4/Base64 protected (‘AES-256-CBC’, ‘Base64-encoded machine fingerprint’, ‘RC4 algorithm’).
- [T1090.001] Proxy: Internal Proxy – Blackwood/Chisel established reverse SOCKS proxying to bridge into internal networks (‘establish a reverse SOCKS proxy’).
- [T1090.003] Proxy: Multi-hop Proxy – The attackers used tunneling infrastructure to route traffic across compromised networks (‘enabled the attackers to route traffic to the target’s internal network’).
- [T1071.001] Application Layer Protocol: Web Protocols – GitHub API traffic was used for C2 to blend with normal cloud activity (‘misuses legitimate GitHub API infrastructure’ and ‘blend their malicious network activity with standard enterprise traffic’).
- [T1102.001] Web Service: Dead Drop Resolver – GitHub Issues comments and repository files were used as a dead-drop mechanism for fallback C2 (‘leveraged the GitHub Issues Search API’ and ‘hidden within HTML comments’).
- [T1059.001] Command and Scripting Interpreter: PowerShell – PsProxy.dll executed PowerShell without spawning PowerShell.exe (‘executing PowerShell commands without invoking the PowerShell.exe binary’).
- [T1055] Process Injection – The malware ran code inside trusted/hijacked host processes and in-memory execution contexts (‘customized runspace … within the hijacked host process’).
- [T1497.001] Virtualization/Sandbox Evasion: System Checks – The loader checked for virtualization markers and host characteristics (‘checked for virtualization markers’ and verified CPU, RAM, disk space).
- [T1036] Masquerading – The attackers used fake Dubai Airports files and renamed binaries to appear legitimate (‘masquerading as a career portal’ and ‘renamed to RuntimeBroker.exe’).
- [T1218.010] System Binary Proxy Execution: Regsvr32/Trusted Binary Similarity Noted via Signed Microsoft Binaries – The campaign relied on signed Microsoft binaries and trusted process behavior to launch malware (‘trusted Microsoft binary’ and ‘trusted developer tool’).
- [T1219] Remote Access Software – ShelbyC2 V2 functioned as a backdoor/RAT for remote command execution (‘operated as the primary RAT’).
- [T1105] Ingress Tool Transfer – The malware downloaded second-stage payloads and payload content from GitHub repositories (‘download and decrypt a second-stage payload’).
Indicators of Compromise
- [Files/Archives ] malicious recruiter lure and project archives – DubaiAirport_Carrers_IT_Test.zip, FlightManager.csproj, and WarUnPublishedDocuments.zip
- [File names ] malware and payload components – RuntimeBroker.dll, PsProxy.dll, Blackwood.dll, RuntimeBrokerApi.dll, Blackwood.dll.conf
- [SHA-256 hashes ] identified malware and archive hashes – 6e7d9b33f1e72ea1ede71373a604ecdb060dab7d42055179c1eede9ecd1fd239, f5b12772db6817f7a765a6fe7565fd3d4f87edc28e42fe3ec0244a372a410fc9, and 4 more hashes
- [IP addresses ] tunneling, phishing, and staging servers – 91.107.156[.]29, 65.109.214[.]145, and other 2 IPs
- [Domains ] phishing/lookalike and staging domains – cloud.g-drive[.]cam, googeldrive[.]cam, and other 4 domains
- [Registry keys ] persistence location used by the loader – HKCUSOFTWAREMicrosoftWindowsCurrentVersionRunMicrosoftRuntime
- [GitHub repositories/accounts ] C2 and staging infrastructure – hxxps[:]//github[.]com/peakyblinders-tm, hxxps[:]//github[.]com/GreenBeret0
- [URLs ] phishing and API endpoints used for delivery/C2 – hxxps[:]//api.github[.]com/repos/peakyblinders-tm/myLic/contents/{machineId}/Lic.txt, hxxps[:]//cloud.g-drive[.]cam/drive/file/d/[generated id]/view
Read more: https://unit42.paloaltonetworks.com/blinder-tunnel-targets-critical-infrastructure/