At least 14 people in Serbia, including a parliamentarian, an opposition politician, and student protesters, were targeted with advanced spyware, with Citizen Lab confirming one Pegasus infection and Amnesty International identifying NoviSpy in at least two cases. The spying campaign appears to have intensified around the March local elections, highlighting a…

Researchers uncovered BraZetsu, a Python-based Windows malware framework used by Exilware to turn compromised systems into tradable access points on the Infected Marketplace. The malware targets Iberian and Latin American organizations, uses AI-assisted triage and stealthy reconnaissance, and overlaps in function and infrastructure with CNABHunter and AgenteV2. #BraZetsu #Exilware #InfectedMarketplace #CNABHunter…

Blanco & Etcheverry in Uruguay was targeted by the gunra ransomware group, disrupting operations in the law firm sector. The incident is estimated to affect a company with approximately US$ 5,000,000 in revenue, with impacts reported across #Uruguay

ASEC found attack cases where threat actors used Radmin and UltraVNC to take over infected systems, then deployed Netch, CCProxy, and SoftEther VPN to turn them into proxy nodes and VPN servers. The activity involved downloads from 103.86.86[.]244 and used Chinese-language scripts and configuration files, suggesting a Chinese-speaking operator. #Radmin #UltraVNC…
OpenAI is committing $1 billion in credits to expand access to its Daybreak cyber models for defenders of water and wastewater systems, the electric grid, governments, banks, nonprofits, and open-source projects. The program starts in the United States and will expand to partner countries soon, offering training, technical support, and tools to analyze code, validate vulnerabilities, and develop fixes. #OpenAI #Daybreak #MSISAC
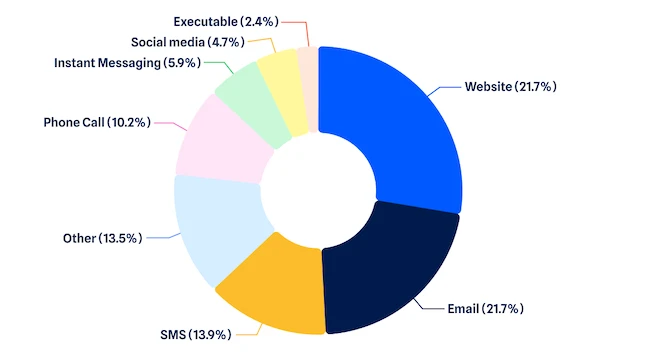
Malwarebytes says scammers are increasingly matching each scam type to the platform that produces the best results, with web, email, SMS, phone, social media, and gaming communities all used in different ways. The data also shows heavy impersonation of MrBeast, Google, Microsoft, Apple, Roblox, and Amazon, while scam activity peaks on Friday and around midday. #Malwarebytes #MrBeast #Google #Microsoft #Apple #Roblox #Amazon #Steam #Discord #Minecraft

Roy Katmor explains that AI agents are often trusted in approved studios and apps while the credentials behind them go unreviewed, creating hidden access risks. He recommends inventorying each agent’s owner, tools, credentials, effective authority, and behavior, then enforcing scoped controls and a targeted kill switch. #Orchid #RoyKatmor #HelpNetSecurity #AIagents

The article explains how AI can help cybersecurity companies build stronger moats in three areas: systems of intelligence, AI-native security services, and frontier security. It argues that the real advantage comes from accumulated context, expert judgment, and ownership of new threat models rather than from simply wrapping an LLM around existing products. #SIEM #MSSP #AndreessenHorowitz #AntonChuvakin #CiscoSecurity

There was 1 defacement incident targeting a site in Brazil, and the attacker involved was Simsimi. The reported target was https://invernoculturalmemoria.ufsj.edu.br/simipeler.json, with no other countries mentioned. #Brazil…
The ransomware claim alleges that AuditTeam targeted PIT.local in CO, resulting in unauthorized access and encrypted files while demanding a ransom, per the provided details. The threat actor identity is listed as unknown, with no additional verified information in the claim. #Colombia
AuditTeam ransomware activity claimed against mansurovogroup, an integrated agricultural enterprise based in Kursk Oblast, Russia, operating in grain cultivation, cattle and sheep farming, and horse breeding with a focus on agricultural innovation and precision farming. The claim indicates ransomware impact on resources tied to the enterprise in #Russia

A forum actor using the name caustic claims to be selling 675 GB of data allegedly taken from Réso, including about 530,000 files, a full file listing, and sample folders. The alleged trove is said to contain invoices, customer records, partner data, private conversations, orders, business strategy documents, and technical drawings,…
Symantec reports that attackers have revived abuse of Node.js since February 2026, using the trusted node.exe runtime for persistence and execution against victims including government departments, technology companies, and hotels. In the observed campaigns, actors tied to Woodgnat/KongTuke and other threats used ClickFix, AdaptixC2, Cobalt Strike, ModeloRAT, Backdoor.Mistic, C2Looper, and EtherHiding-style Ethereum blockchain lookups to maintain access and evade defenses. #Node.js #AdaptixC2 #CobaltStrike #ModeloRAT #BackdoorMistic #C2Looper #EtherHiding #Woodgnat #KongTuke

SonicWall has disclosed and patched two actively exploited zero-day vulnerabilities, CVE-2026-83548 and CVE-2026-83549, in its SMA 1000 appliances after researchers said they could be chained to achieve unauthenticated remote-code execution. CISA added the flaws to its KEV catalog, while SonicWall urged customers to hunt for compromise, reimage affected devices if needed, and reset credentials and tokens. #SonicWall #SMA1000 #CVE-2026-83548 #CVE-2026-83549 #CISA #KEV
DFIR Report identified BengalSEO, a Rajasthan-based scam operation that has used SEO poisoning, malicious lure pages, and a traffic distribution system to deliver the MayaBot malware and drive tech support fraud since at least 2015. The campaign relies on companies such as WeConnect Solutions LLC and Garage2Global, along with infrastructure spanning GitHub, Hostmaza, Cloudflare, Matomo, and numerous redirector and payload domains. #BengalSEO #MayaBot #WeConnectSolutionsLLC #Garage2Global #Hostmaza #Cloudflare #Matomo