
Cybersecurity researchers have uncovered a sophisticated phishing campaign by North Korea-linked group ScarCruft (APT37), targeting South Korean officials and researchers with malware known as RokRAT. The campaign involves tailored spear-phishing emails with malicious LNK files, aimed at espionage and sensitive data theft. #ScarCruft #RokRAT…
Category: Cyber Security News
Trend Micro researchers uncovered a complex cyber-espionage campaign called TAOTH, targeting Eastern Asian dissidents, journalists, and business leaders through hijacked software updates and spear-phishing. The operation involves multiple malware families, including C6DOOR, GTELAM, DESFY, and TOSHIS, with overlapping infrastructure suggesting a persistent threat group. #TAOTH #CyberEspionage…
The report reveals how Russian private cybersecurity firms are integral to the Kremlin’s cyber operations during the Ukraine conflict, supporting both defensive and offensive activities. It highlights key companies like Kaspersky, Security Code, and Positive Technologies, illustrating the blurred lines between state and private actors. #Kaspersky #PositiveTechnologies…

This weekly recap highlights recent developments in cybersecurity threats, including cloud-based ransomware campaigns by Storm-0501 and ongoing double-extortion attacks by groups like Lynx/Sinobi. It also covers sophisticated espionage activities by threat actors such as UNC6384, APT37, and Silver Fox, along with emerging malware, supply-chain attacks, and evasive techniques used to bypass security measures. Stay vigilant against evolving threats and enhance defenses using new detection tools and operational strategies. #Storm0501 #LynxSinobi #UNC6384 #APT37 #SilverFox
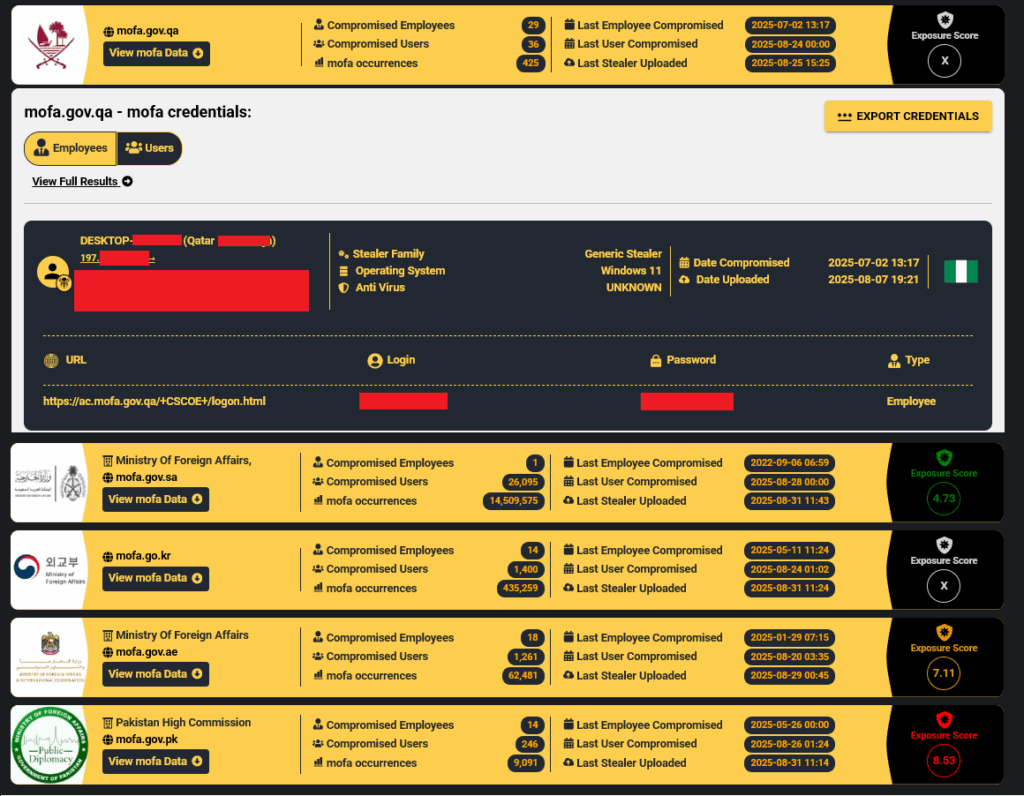
Opportunistic Infostealer malware is increasingly being exploited by advanced threat actors to target diplomatic credentials worldwide. These breaches threaten national security by enabling real-time espionage and geopolitical manipulation. #Infostealer #APT #DiplomacySecurity

Cybersecurity threats are increasingly driven by AI misuse, sophisticated phishing operations, and disrupted ransomware activities, highlighting evolving attack techniques and law enforcement efforts. Key incidents include AI-powered cybercrime using Claude and Salesloft, targeted supply-chain phishing, and the fragmentation of ransomware gangs like Chaos, alongside high-profile breaches and nation-state activities involving APT29 and Salt Typhoon. #ClaudeAI #SalesloftTheft #APT29 #SaltTyphoon
Threat actors are using Google ad campaigns to distribute a PDF editing app that delivers the TamperedChef infostealer malware. This operation involves multiple domains, fraudulent certificates, and the use of residential proxies to maximize infection and data theft. #TamperedChef #AppSuitePDFEditor
Google warns that all security tokens linked to the Salesloft Drift AI chat agent may be compromised after attackers accessed Google Workspace emails. The scope of the breach has expanded, affecting multiple integrations beyond Salesforce, leading Google to revoke tokens and disable integrations. #SalesloftDrift #GoogleWorkspace #SecurityTokens…
Anthropic has revealed a large-scale cybercriminal operation that exploits their AI chatbot, Claude, to automate complex attacks across multiple sectors. This case highlights how threat actors are leveraging AI to conduct vibe hacking, significantly lowering the technical barriers for cybercrime. #Claude #VibeHacking…
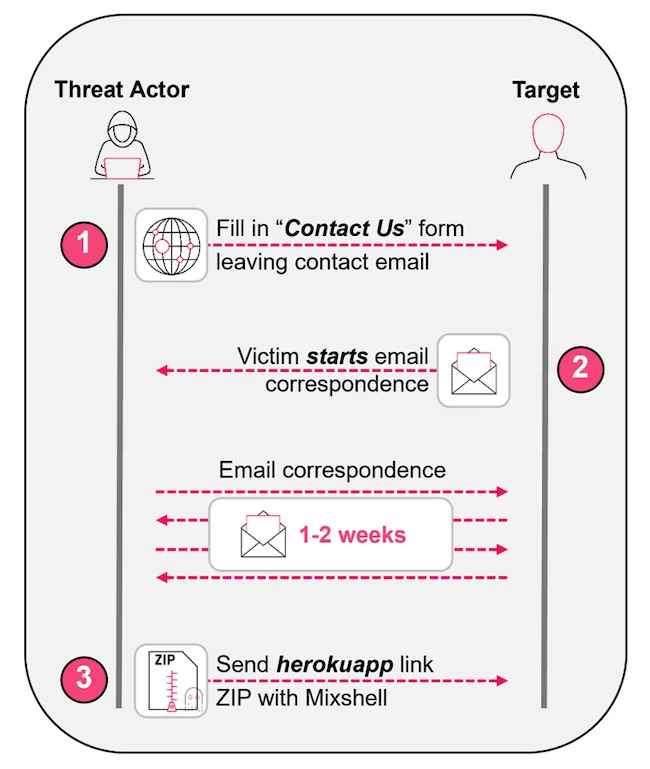
A sophisticated phishing campaign targeting industrial and supply chain companies uses trusted contact forms and professional communication to deceive victims. The attackers deliver malicious ZIP archives with PowerShell scripts, employing DNS TXT tunneling for command and control. #MixShell #Herokuapp…

Cybersecurity experts have highlighted a sophisticated attack involving the misuse of legitimate tools like Velociraptor and remote access platforms to establish covert control over enterprise systems. This evolving tactic underscores the increasing use of authorized software and platforms for malicious purposes, including ransomware and credential theft. #Velociraptor #CloudflareWorkers…

WhatsApp has fixed a critical security vulnerability (CVE-2025-55177) that could have allowed attackers to process malicious content without user interaction. This flaw, potentially linked with a separate Apple zero-day, has been exploited in targeted attacks against specific individuals, including civil society members. #WhatsAppSecurity #ZeroClickAttacks…

The Salvation Army experienced a data breach in May 2025, potentially involving the theft of personal information by the ransomware group Chaos. The organization is offering victims free credit monitoring while Chaos claims responsibility, though the veracity of the claim remains unverified. #Chaos #SalvationArmy…
Recent cybersecurity developments highlight a wave of cloud and third-party breaches, including OAuth token theft impacting Salesforce and Google Workspace, linked to supply-chain attacks such as TransUnion data leaks. Additionally, threat actors are shifting towards cloud-focused ransomware attacks like Storm-0501, while critical vulnerabilities are prompting urgent patches across multiple platforms. #SalesloftOAuth #Storm0501 #BigSleep #FreePBXZeroDay #ShadowSilk

Amazon has disrupted an opportunistic watering hole campaign by APT29, a Russia-linked threat group, involving compromised websites redirecting visitors to malicious domains. The campaign aims to steal Microsoft account credentials through sophisticated evasion techniques and social engineering. #APT29 #WateringHole #MicrosoftCredentialTheft…