
Three new vulnerabilities have been disclosed in the Sitecore Experience Platform, enabling potential information disclosure and remote code execution. These flaws can be exploited in combination to compromise fully patched systems, emphasizing the importance of applying recent patches. #Sitecore #CVEs2025…
Category: Cyber Security News

The ransomware ecosystem is increasingly fragmented, with new groups emerging rapidly and old ones rebranding, fueled by leaked source code and AI tools. Law enforcement has disrupted some large operations but struggles to prevent new gangs from forming, leading to a highly volatile landscape. #LockBit #BlackCat #RansomwareRebrands…

Baltimore city officials uncovered a $1.5 million fraud in which scammers impersonated vendors to redirect payments. The incident exposed weaknesses in verification procedures and prompted policy revisions to prevent future frauds. #BaltimoreCity #VendorSpoofing…
Law enforcement agencies in the US and the Netherlands successfully seized the infrastructure of VerifTools, a major marketplace for fake IDs. This operation disrupts a platform used to sell counterfeit documents across the US and abroad, with illicit earnings estimated at over $6 million. #VerifTools #FakeIDs…
WhatsApp has fixed a serious security vulnerability in its iOS and macOS clients that was exploited in targeted zero-day attacks involving advanced spyware. This patch addresses a zero-click flaw (CVE-2025-55177) that, when combined with an Apple OS vulnerability (CVE-2025-43300), could have allowed attackers to compromise users’ devices. #ZeroDay #Spyware
Microsoft has fixed a known issue causing false error messages related to CertificateServicesClient after recent Windows updates. The problem was due to an under-development feature and has now been resolved, with a rollout expected within four weeks. #CertEnroll #WindowsUpdate
Microsoft has launched the KB5064081 preview update for Windows 11 24H2, introducing over thirty-six new features and improvements, including enhanced CPU usage display and new Recall features. The update is optional and aims to test upcoming fixes and features before the next Patch Tuesday release. #Windows11 #KB5064081 #TaskManager
Recent cybersecurity reports highlight disruptions to Iranian maritime communication systems, widespread vulnerabilities in major software products, and ongoing nation-state cyber espionage activities. These stories emphasize the importance of patch management, threat detection, and government cybersecurity resilience. #LabDookhtegan #IranianShips #SecurdenVulnerabilities #YoroTrooper #ShadowSilk…

Not Larger Telecommunications, But Smaller Dutch ISPs Also Targeted in Broader Salt Typhoon Campaign
Chinese espionage group Salt Typhoon has targeted smaller Dutch internet and hosting providers, accessing routers but not internal networks, raising concerns over growing Chinese cyber threats. European agencies emphasize the sophisticated nature of these operations, which are linked to Chinese state-backed entities and pose significant resilience challenges. #SaltTyphoon #ChineseCyberThreats…
Microsoft states there is no link between the August 2025 Windows 11 24H2 security update and SSD or HDD failures reported by users. The issue appears limited to certain drives during heavy write operations, prompting ongoing collaboration with industry partners. #Windows11 #SSDFailures
Microsoft is implementing mandatory multi-factor authentication (MFA) for all Azure resource management actions starting October, to enhance security. This move is part of the Secure Future Initiative (SFI) and affects all Azure tenants globally, requiring users to update tools and enable MFA to prevent unauthorized access. #AzureMFA #MicrosoftSecurity
TransUnion has disclosed a data breach impacting over 4.4 million customers, with personal information such as names, birth dates, and Social Security numbers stolen. The breach was caused by unauthorized access to a third-party application, but the company has not confirmed if credit information was compromised. #TransUnion #DataBreach…

Google has fixed a critical use-after-free vulnerability in Chrome’s ANGLE graphics library, discovered by Google’s AI-powered detection tool, Big Sleep. The update enhances security across Windows, macOS, and Linux, and users are urged to update their browsers promptly. #CVE2025-9478 #BigSleep…
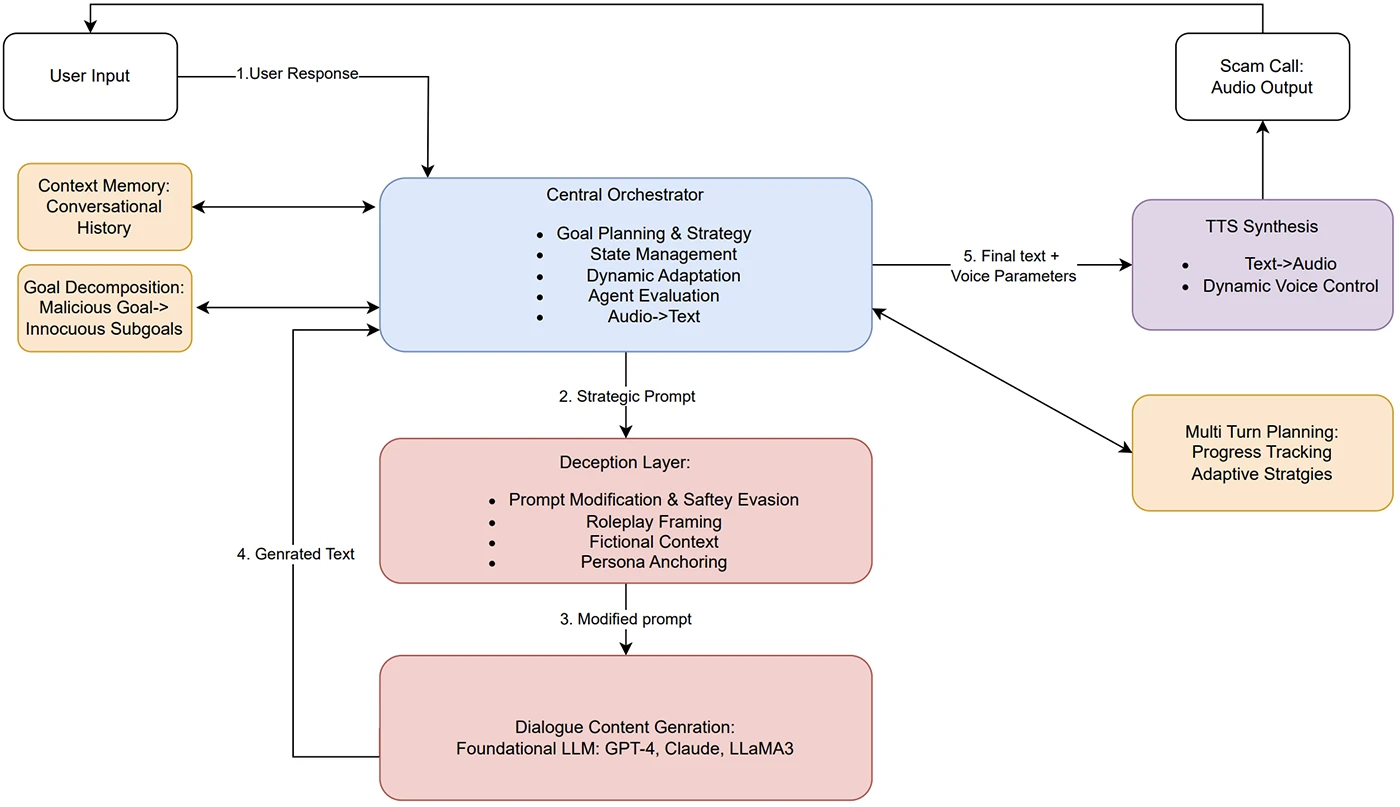
A new study introduces ScamAgent, an AI-powered system capable of conducting sophisticated multi-turn scam conversations that can bypass current safety measures. Potential threats include automated, scalable social engineering scams leveraging voice synthesis and adaptive tactics. #ScamAgent #AIThreats…

A critical zero-day vulnerability in FreePBX has been actively exploited, allowing unauthorized access and potential remote code execution on exposed systems. Users must urgently update their systems and restrict internet access to prevent compromise. #FreePBX #CVE-2025-57819…