
Researchers uncovered a sophisticated Iranian-linked spear-phishing campaign targeting international organizations through compromised diplomatic mailboxes. The operation used malicious Microsoft Word documents and advanced obfuscation techniques to gather system information and establish persistent access. #HomelandJustice #IranianCyberActors…
Category: Cyber Security News
Seqrite Lab reveals Operation HanKook Phantom, a sophisticated spear-phishing campaign by North Korean threat actor APT-37 targeting South Korean government and research institutions. The campaign employs malicious LNK files, fileless malware, and cloud services for covert command-and-control operations. #APT37 #ROKRAT…
Zscaler reports a data breach caused by threat actors accessing its Salesforce instance through stolen credentials linked to the Salesloft Drift attack. The incident exposed customer information, prompting enhanced security measures and ongoing investigation. #Salesforce #ThreatActors

Cybersecurity researchers highlight a shift in Android malware, where dropper apps now distribute not only banking trojans but also simpler malware like SMS stealers. These campaigns utilize dropper apps disguised as trusted government or banking apps, evading security measures like Google Play Protect. #AndroidDropper #ThreatFabric…

The Spanish government reversed its decision to use Huawei equipment in the RedIRIS research network due to concerns over digital strategy and national security. The move highlights ongoing geopolitical tensions and different approaches within Europe regarding Chinese technology providers. #Huawei #RedIRIS #Spain #CyberEspionage…
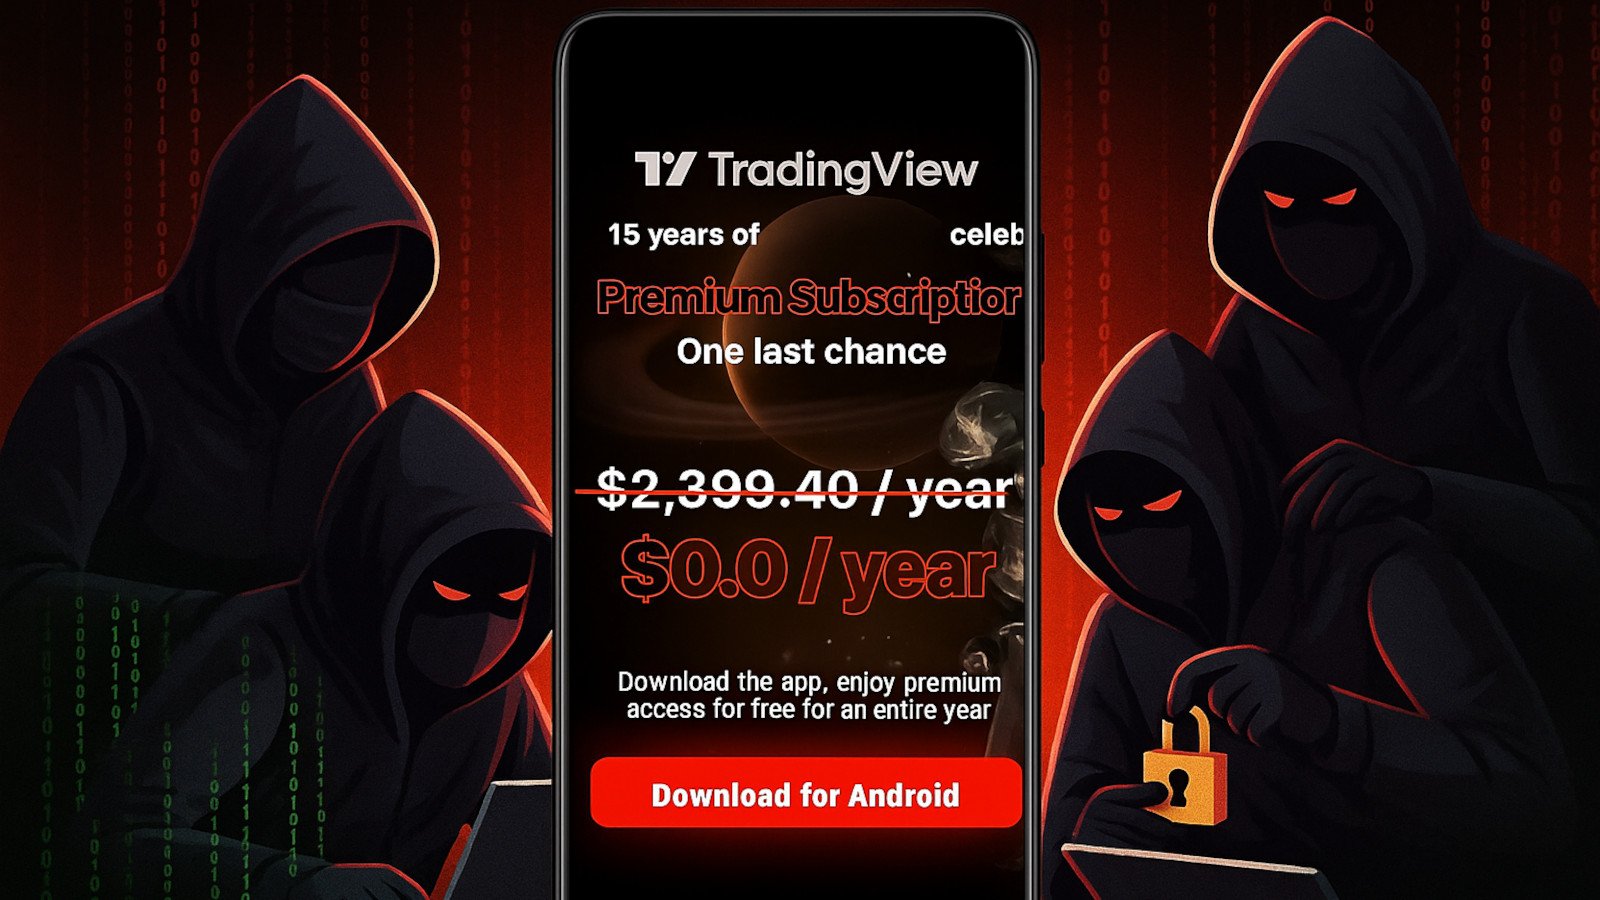
Cybercriminals are exploiting Meta’s advertising platform with fake offers of a free TradingView Premium app to spread the Brokewell Android malware. This sophisticated campaign targets cryptocurrency users and allows remote access, data theft, and device control. #Brokewell #TradingView #AndroidMalware
Researchers disrupted an operation by the Russian threat group Midnight Blizzard, also known as APT29, targeting Microsoft 365 accounts through sophisticated watering hole campaigns. The attack involved malicious redirects mimicking Cloudflare sites to trick users into authenticating attacker-controlled devices. #MidnightBlizzard #APT29 #Microsoft365 #WateringHole
A critical SQL injection vulnerability, CVE-2025-0165, affects certain versions of IBM Watsonx Orchestrate Cartridge in IBM Cloud Pak for Data, risking data breaches and service disruption. Organizations running vulnerable versions are urged to update to version 5.2.0.1 to mitigate these high-severity threats. #CVE20250165 #IBMWatsonx…

Amazon disrupted a watering hole campaign conducted by the Russia-linked APT29 group, leveraging compromised websites to steal credentials. This campaign targeted academics and critics of Russia and showcased advanced tactics like obfuscated JavaScript and server-side redirects. #APT29 #Nobelium…

A scammer conducted a Business Email Compromise attack on Baltimore, stealing over $1.5 million by spoofing a vendor and manipulating bank details. The city’s internal controls were weak, enabling repeated fraud attempts and financial losses. #BusinessEmailCompromise #BaltimoreFraud…

WhatsApp has fixed a critical zero-day vulnerability, CVE-2025-55177, that may have been exploited in targeted spyware attacks. This security flaw, combined with an Apple OS vulnerability, underscores the threat of sophisticated cyber espionage campaigns targeting specific users. #WhatsApp #NSOGroup…

Pennsylvania’s Office of Attorney General experienced a ransomware attack that disrupted court proceedings and temporarily offline services. The investigation is ongoing, with no evidence yet of data theft, and efforts are underway to restore full operational capacity. #Ransomware #PennsylvaniaOAG #CyberAttack #LegalSystemDisruption…

Threat actors are exploiting Meta ads to distribute fake TradingView Premium apps on Android, deploying the sophisticated Brokewell malware to steal crypto and personal data. This campaign highlights the growing danger of mobile-targeted malvertising and advanced spyware threats. #Brokewell #AndroidMalware…

Enterprise security is increasingly challenged by threats targeting web browsers, with over 80% of incidents originating from browser-based vulnerabilities. The cyber adversary Scattered Spider exemplifies sophisticated tactics such as credential theft and session hijacking, emphasizing the need for robust browser security strategies. #ScatteredSpider #BrowserSecurity…

Homeland Security completed a major shakeup at FEMA’s IT department after a cybersecurity breach revealed severe vulnerabilities. Despite investments and internal dissent, DHS insists the firings were necessary to safeguard national security. #FEMA #cybersecurityfailures…