
The article discusses the growing challenge of Shadow AI, where employees use unauthorized AI tools, often bypassing corporate controls. It emphasizes the importance of AI discovery and governance to ensure regulatory compliance and data security. #ShadowAI #HarmonicSecurity…
Category: Cyber Security News

Jaguar Land Rover has experienced a severe cybersecurity incident that disrupted its global IT systems, affecting both manufacturing and retail operations. The company responded by shutting down systems and is working to restore services, though no customer data appears to have been compromised. #JaguarLandRover #CyberAttack #NCSC…

Moscow authorities have recruited hackers who previously targeted the Moscow Electronic School (MES) to work on improving the city’s digital services. This move highlights a controversial approach of employing former malicious hackers rather than pursuing traditional legal actions. #MoscowElectronicSchool #DDoSattack…
WhatsApp addressed a zero-day vulnerability (CVE-2025-55177) that could have been exploited for targeted attacks, especially when combined with an Apple OS-level vulnerability (CVE-2025-43300). The flaw involved incomplete device authorization and could allow malicious URLs to be processed on targeted devices, potentially leading to sophisticated attacks. #WhatsApp #CVE2025-55177 #AppleVulnerabilities #NSOGroup #Pegasus…

Amazon has disrupted a Russian state-sponsored cyberespionage campaign targeting Microsoft users through compromised websites that redirect visitors to malicious domains. The attack, attributed to the APT29 group (also known as Cozy Bear), involved credential harvesting and intelligence gathering efforts. #MidnightBlizzard #APT29 #RussianForeignIntelligenceService…
Varonis Systems has acquired email security provider SlashNext to enhance its cybersecurity platform, focusing on protecting users from spearphishing and social engineering threats using AI technology. This strategic move aims to expand Varonis’s market reach and improve threat detection from email and collaboration tools. #SlashNext #VaronisSystems #SpearPhishing #AIThreatDetection…
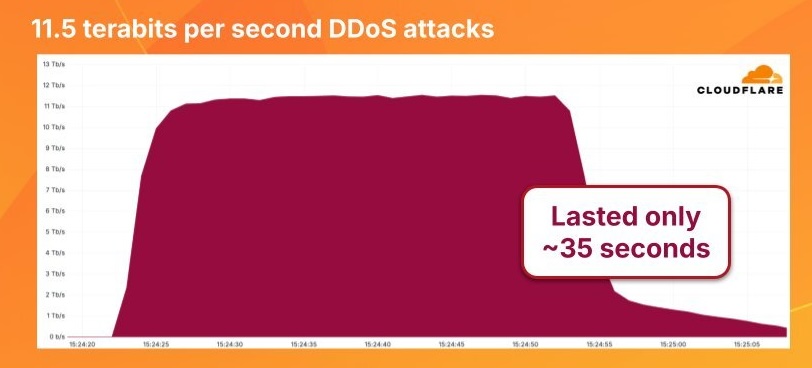
Cloudflare successfully blocked the largest DDoS attack ever recorded, reaching 11.5 Tbps, which lasted approximately 35 seconds. The attack was a UDP flood primarily originating from Google Cloud infrastructure, highlighting the ongoing threat of hyper-volumetric cyberattacks. #Cloudflare #DDoS #GoogleCloud #UDPflood…

This article summarizes the fourth episode of the Black Hat USA 2025 CISO Podcast Series, which emphasizes cost-effective strategies for maturing cybersecurity programs amid budget constraints. It highlights the importance of smart prioritization, AI, automation, and aligning security efforts with business goals. #BlackHatUSA #CISO #CyberResilience #AI #SecurityBudget…

Zscaler was targeted in a supply chain attack that involved the theft of OAuth tokens from the Salesloft Drift application, leading to data exposure within its Salesforce system. The incident highlights the risks of third-party application vulnerabilities and the importance of cybersecurity vigilance. #Salesloft #OAuthTokens…
The Pennsylvania Attorney General’s Office experienced a ransomware attack causing a two-week service outage and disruption of key communication channels. The office refuses to pay the ransom, and an investigation is ongoing to determine if any data was stolen. #DoppelPaymer #PennsylvaniaStateCyberattack

Silver Fox has been exploiting signed but vulnerable drivers, like WatchDog Anti-malware, to disable security solutions and deploy malware such as ValleyRAT. This sophisticated campaign uses signature manipulation and evasive techniques, highlighting the evolving nature of threat actor strategies. #SilverFox #ValleyRAT…

Cybersecurity researchers have uncovered a malicious npm package called nodejs-smtp that stealthily injects code into cryptocurrency wallet applications like Atomic and Exodus. This campaign demonstrates how simple dependencies can be exploited to modify desktop apps and divert digital assets. #AtomicWallet #Exodus #ElectronExploitation…

This report reveals how the Lazarus Group continues to evolve its attack strategies targeting the financial and cryptocurrency sectors using sophisticated remote access tools. Their multi-stage infection process involves social engineering, custom malware, and advanced persistence techniques to maintain long-term control. #LazarusGroup #RemotePE…

A critical SQL injection vulnerability was found in the WordPress Paid Membership Subscriptions plugin, affecting versions 2.15.1 and below. The issue has been fixed in version 2.15.2, emphasizing the importance of updating for security. #WordPress #SQLInjection…

Recent cybersecurity disruptions include Amazon halting a Russian APT29 campaign targeting Microsoft 365, and new research exposing private Russian firms supporting Kremlin operations amidst Ukraine conflict. Additionally, cybereth threats span from Asia-targeted espionage campaigns like TAOTH and ScarCruft, to mobile malvertising via Meta ads pushing Brokewell malware.
#APT29 #ScarCruft