
A man from Tennessee admitted to hacking into multiple U.S. government systems, including the Supreme Court’s filing system, AmeriCorps, and the Department of Veterans Affairs. The case highlights the ongoing threat of credential theft and unauthorized access to sensitive government data. #SupremeCourtHacking #CredentialTheft…
Category: Cyber Security News

GootLoader malware uses malicious ZIP archives with obfuscation techniques to evade detection and deliver JavaScript payloads. It exploits Windows’ default unarchiver, bypassing most automated analysis tools, to infect systems via SEO poisoning and malicious WordPress sites. #GootLoader #ZIPArchiveSecurity…
A Jordanian national pleaded guilty to selling network access and malware that disables endpoint detection tools, affecting numerous companies and linked to a ransomware attack. The case highlights the role of initial access brokers and the ongoing threat posed by the “r1z” cybercrime forum account. #CVE-2022-26134 #CobaltStrike…
A cybersecurity researcher exploited a cross-site scripting (XSS) vulnerability in the StealC malware control panel to observe attacker activity and gather intelligence. The flaw enabled session hijacking and operator profiling, potentially disrupting the malware’s operations. #StealC #XSSvulnerability

Daily Recap, The latest funding rounds show Depthfirst raising $40 million, Novee securing $51.5 million, and isVerified entering stealth with voice-deepfake detection, signaling ongoing investor interest in vulnerability management and identity assurance. It further catalogs vulnerabilities, breaches, and attacks across FortiSIEM, Desktop Windows Manager, Node.js async_hooks, c-ares, Belgian Hospital, Monroe University, Pax8, Victorian Department of Education, RedVDS, Predator spyware, PLUGGYAPE, ConsentFix, Reprompt, third-party risk, and Windows 365/Cloud PC service disruptions. #Depthfirst #Novee #isVerified #FortiSIEM #DesktopWindowsManager #NodeJS #async_hooks #c-ares #BelgianHospital #MonroeUniversity #Pax8 #VictorianDepartmentOfEducation #RedVDS #PredatorSpyware #PLUGGYAPE #ConsentFix #Reprompt #Windows365 #CloudPC
Cisco has released a patch for a critical AsyncOS zero-day vulnerability (CVE-2025-20393) that has been exploited since November 2025. Threat actors, believed to be a Chinese hacking group UAT-9686, have been using this flaw to deploy malicious tools and maintain persistence. #AsyncOS #UAT9686
A critical vulnerability (CVE-2025-64155) in Fortinet FortiSIEM is currently being exploited by attackers using publicly available proof-of-concept code. The flaw allows unauthenticated remote code execution and privilege escalation, prompting urgent security updates and mitigations. #Fortinet #FortiSIEM #CVE-2025-64155
A recent Windows 11 security update (KB5074109) has caused the classic Outlook desktop client to freeze for users with POP email accounts. Microsoft is investigating the issue and has suggested uninstalling the update as a temporary workaround. #Windows11 #KB5074109
Verizon issued a $20 account credit to customers affected by a nationwide wireless outage caused by a software issue. Customers are instructed on how to redeem the credit through their online accounts, with the outage affecting calls and data access. #Verizon #SoftwareIssue
An advanced China-linked threat actor, UAT-8837, has been targeting North American critical infrastructure by exploiting vulnerabilities, including a recent zero-day in Sitecore. Researchers link this activity to broader Chinese espionage efforts, with tools aimed at credential theft and network reconnaissance. #UAT-8837 #SitecoreCVE2025-53690
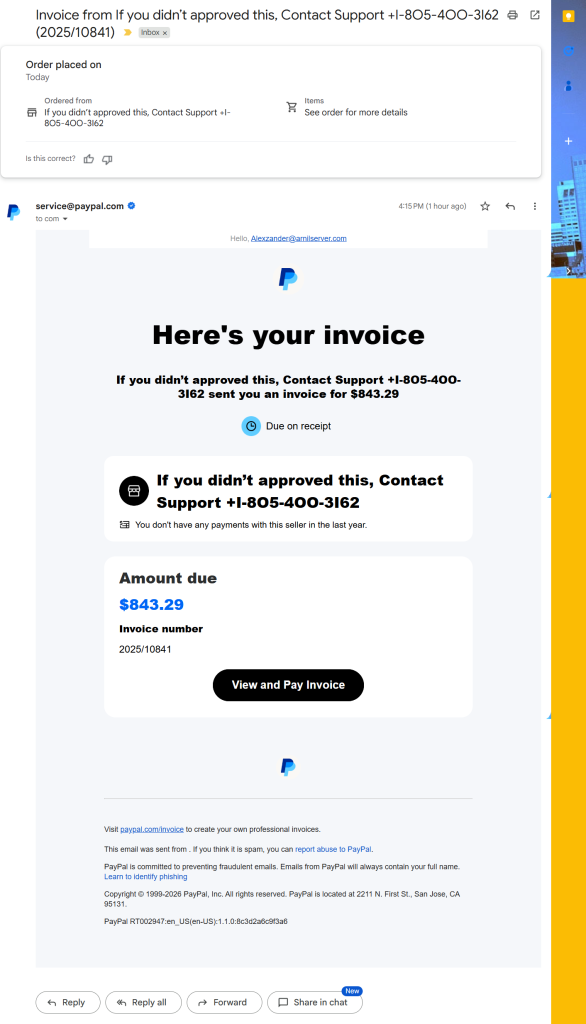
A new phishing scam exploits PayPal’s genuine invoice system and BIMI verification to deceive users with authentic-looking emails. This sophisticated attack includes callback phishing to scam individuals, emphasizing the importance of vigilance. #PayPal #BlueTick #PhishingScam #CallbackPhishing…

Kyowon Group experienced a ransomware attack affecting most of its subsidiaries, leading to potential data leakage and service disruptions. Authorities estimate that around 9.6 million accounts may have been impacted, highlighting a significant cybersecurity threat in South Korea. #KyowonGroup #Ransomware #SouthKorea #DataLeak…

A vulnerability was discovered in CISA’s Software Acquisition Guide: Supplier Response Web Tool, which could have allowed attackers to inject malicious JavaScript. The issue was reported by Jeff Williams and was eventually fixed after delays, highlighting the importance of vulnerability management within government cybersecurity tools. #CrossSiteScripting #CISAVulnerability…
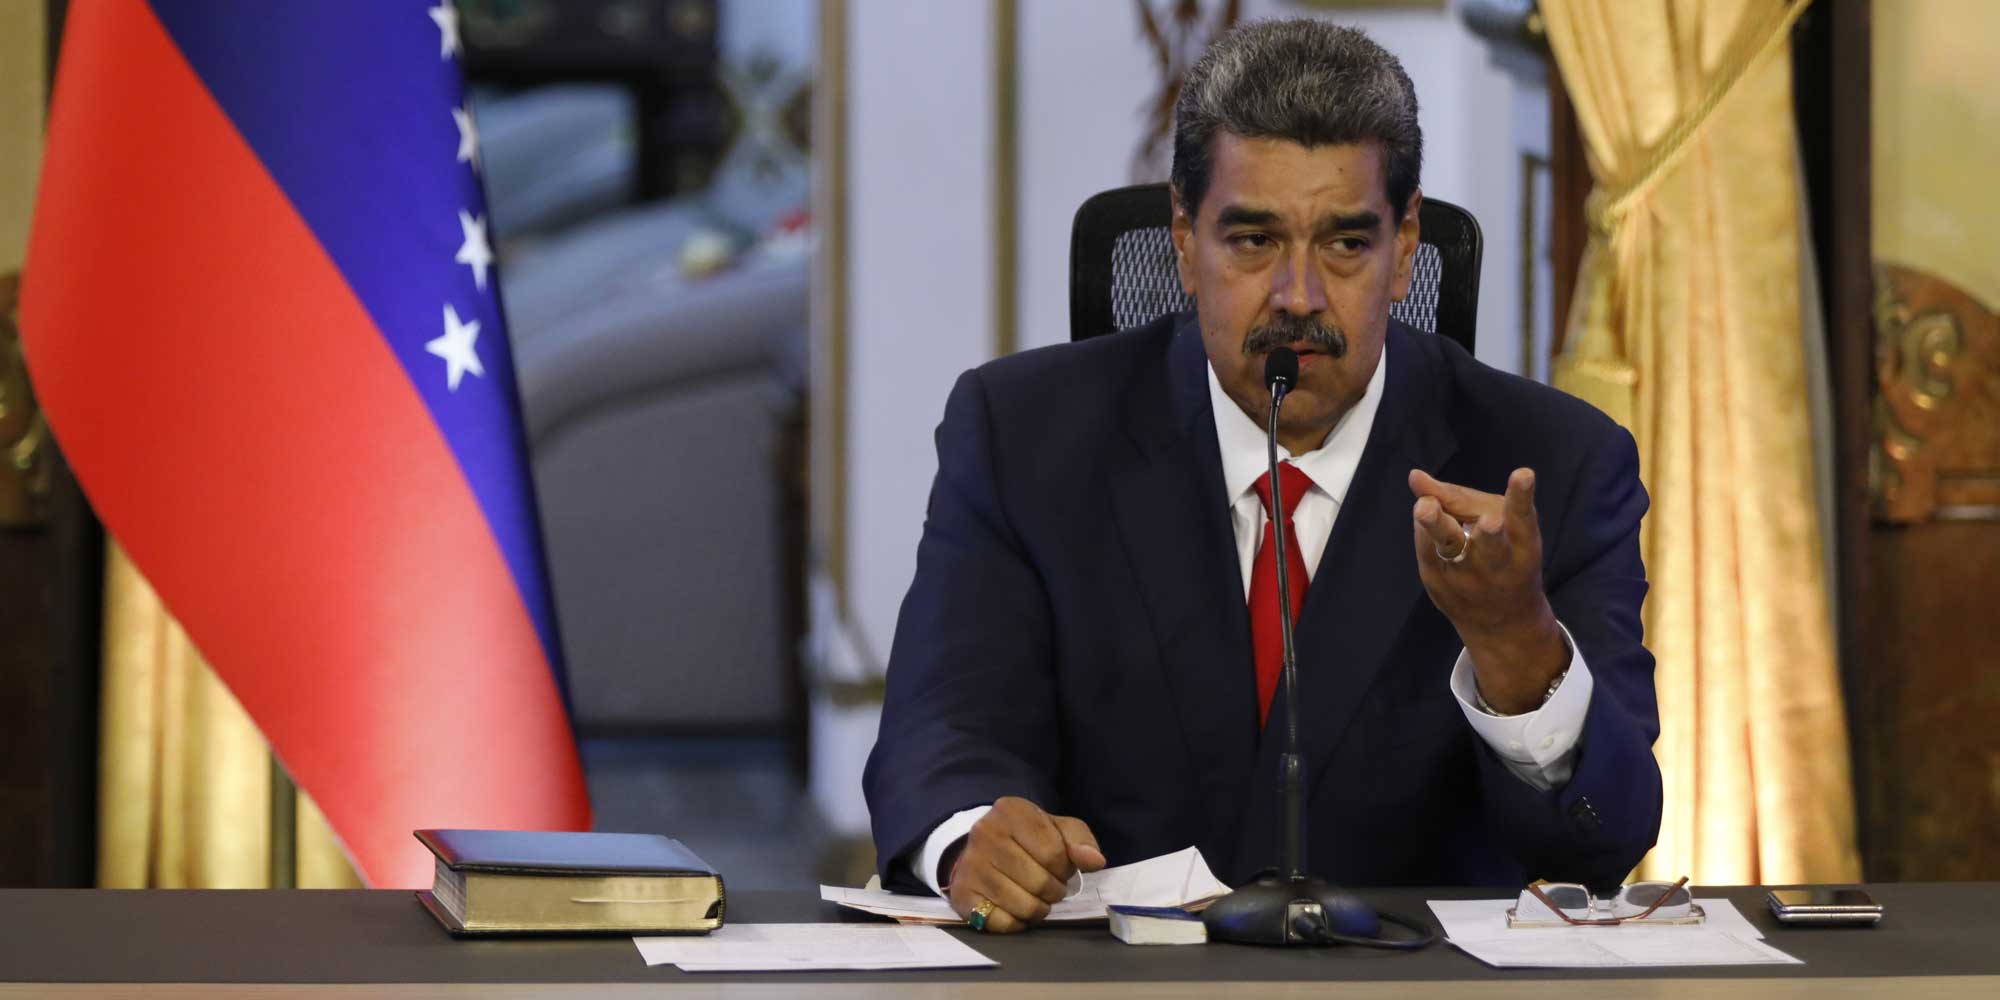
Chinese cyberspies, linked to Mustang Panda, targeted US government agencies with a phishing campaign exploiting geopolitical events like Maduro’s capture. The campaign involved a backdoor called Lotuslite that could steal data and maintain persistence. #MustangPanda #Lotuslite…
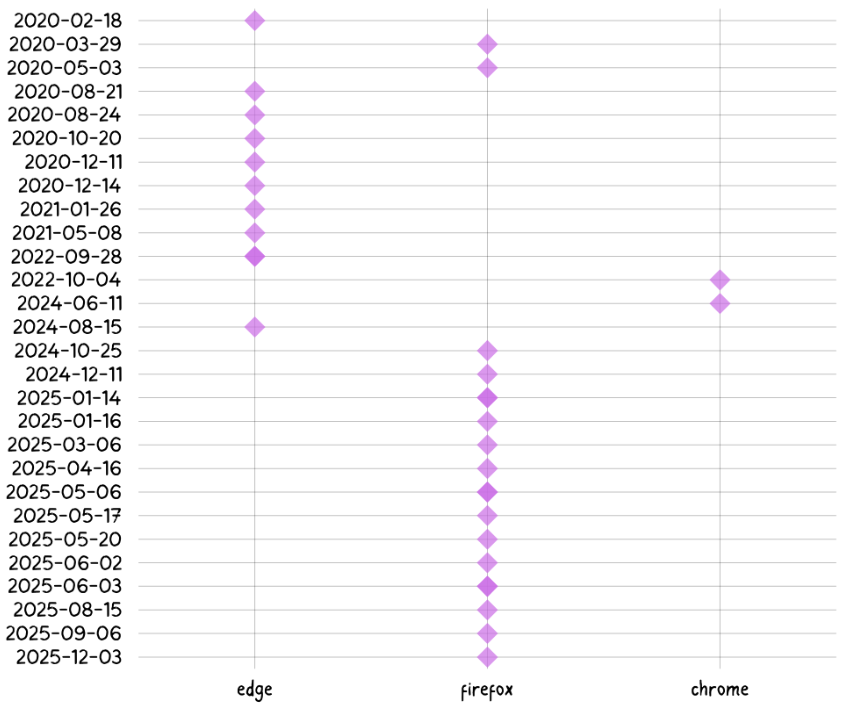
A series of malicious browser extensions, starting with GhostPoster, exploited cloaking techniques to evade detection across multiple platforms, including Firefox, Chrome, and Edge. Over 840,000 users were affected by these extensions, which remained active for years despite being removed from official marketplaces. #GhostPoster #LayerX #BrowserExtensions…