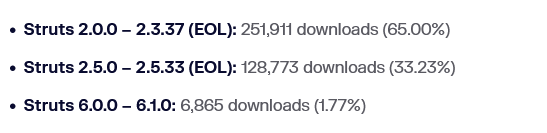
Cybersecurity researchers have identified a significant risk with outdated Apache Struts versions, especially involving CVE-2025-68493, discovered by an autonomous AI system. The vulnerability allows attackers to cause system crashes through crafted input, putting many organizations at risk. #ApacheStruts #CVE202568493…
Category: Cyber Security News

This article emphasizes the importance of protecting personal information available online, which can pose serious safety threats. Using data removal tools like Incogni can help individuals eliminate their sensitive data from public sites, enhancing their privacy and security. #DataProtection #PersonalPrivacy…

Cybersecurity researchers have uncovered five malicious Google Chrome extensions impersonating HR and ERP platforms like Workday and NetSuite to hijack user sessions and steal authentication tokens. Although most have been removed from the Chrome Web Store, they are still accessible on third-party sites and pose a significant threat to victim accounts….
The Canadian Investment Regulatory Organization (CIRO) experienced a data breach affecting approximately 750,000 investors. The attack involved a sophisticated phishing scheme, exposing sensitive personal information but not login credentials. #Phishing #DataBreach #CIRO #InvestorSecurity…

Ukrainian and German authorities have identified suspects linked to the Black Basta ransomware group, with a Russian national on an international wanted list. Black Basta has caused extensive damage globally by stealing credentials, deploying ransomware, and extorting victims in various sectors. #BlackBasta #OlegNefedov #Ryuk #Conti #Interpoolisthreats…
A threat actor linked to China is actively targeting North American critical infrastructure using advanced tactics, including zero-day exploits and open-source tools. This group demonstrates a high level of sophistication, potentially enabling future supply chain attacks and persistent infiltration. #UAT-8837 #ChinaNexus…

Project Eleven has secured $20 million in Series A funding to develop post-quantum cryptographic solutions for digital assets and blockchain networks. The startup aims to help organizations migrate securely to quantum-resistant cryptography amidst growing quantum threats. #PostQuantumCryptography #QuantumThreats…

Monnai has secured $12 million in funding, boosting its total funding to $23 million to develop AI-driven identity and risk data infrastructure for global financial and e-commerce sectors. The company’s technology supports real-time fraud reduction, onboarding, and decision-making with low-latency risk signals and scalable performance monitoring. #MotivePartners #Monnai #FintechSecurity #AIInfrastructure…

This cybersecurity roundup covers recent vulnerabilities, cyberattacks, data breaches, and regulatory actions affecting various organizations and sectors. Notable topics include the BodySnatcher AI hijacking, Fortinet FortiSIEM exploitation, and the Russian-backed cyberattack on Poland’s power system. #BodySnatcher #FortiSIEM #PolandCyberattack…
Elon Musk’s platform X has introduced new restrictions to prevent nonconsensual sexualized images generated by its Grok AI chatbot, amid scrutiny over abuse reports. The company is working with authorities and implementing technological measures to enhance safety and accountability. #GrokAI #ChildProtection #XPlatform…

The 2026 cybersecurity landscape continues to evolve with significant incidents impacting national security, public trust, and business continuity. Key themes include AI regulation, state internet blackouts, data breaches, and the disruption of cybercrime services. #GrokAI #RedVDS…
Germany and Israel have expanded their cybersecurity partnership through a new agreement that enhances cooperation, knowledge exchange, and joint development of cyber defense technologies. This collaboration aims to strengthen national cyber resilience and address digital threats while reinforcing their long-standing security relationship. #Germany #Israel #CyberDome #CybersecurityPartnership…
Hackers are exploiting a critical security flaw in the Modular DS WordPress plugin to gain admin access remotely. This vulnerability, tracked as CVE-2026-23550, has prompted rapid patching and security advisories for affected sites. #CVE-2026-23550 #ModularDS
Food delivery platform Grubhub has confirmed a recent data breach involving unauthorized access and extortion demands from cybercriminals. The incident may be connected to previous breaches and scams involving stolen Salesforce and Zendesk data. #ShinyHunters #SalesforceBreach
The Gootloader malware now employs highly sophisticated obfuscation techniques by concatenating up to 1,000 ZIP archives to evade detection. Researchers highlight how these methods challenge analysis tools and can be identified through specific ZIP header anomalies. #Gootloader #WinRAR #YARA