Google now allows users to change their @gmail.com addresses, offering greater flexibility to manage their email identities. This feature is gradually rolling out and does not affect existing account data. #GmailAddressChange #AccountAliases
Category: Cyber Security News
The Kimwolf botnet, a successor to the Aisuru DDoS network, rapidly expanded to over 2 million Android TV devices using residential proxies. Its activities include frequent DDoS attacks, mainly targeting Minecraft servers, posing significant threats if used against critical infrastructure. #Kimwolf #Aisuru #DDoS #AndroidTV #CyberThreats…

The Department of Homeland Security is developing a new advisory body called ANCHOR to replace CIPAC, aiming to improve communication between industry and government on critical infrastructure threats. The initiative seeks to streamline engagement, open some meetings to the public, and maintain important liability protections. #CIPAC #ANCHOR…
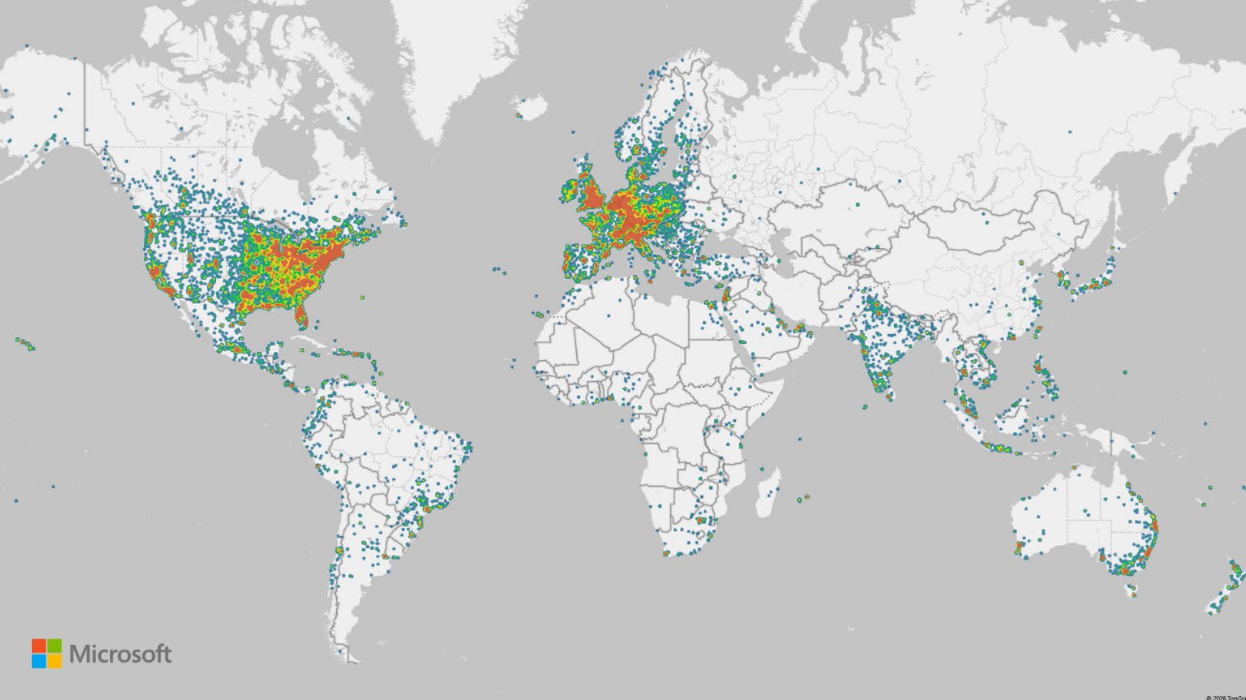
Microsoft collaborated with international law enforcement to dismantle the RedVDS cybercrime infrastructure, which facilitated mass phishing, fraud, and account compromises affecting thousands of organizations worldwide. The takedown highlights the importance of coordinated global efforts in combating cybercrime networks using disposable virtual servers. #RedVDS #Storm-2470…
DeadLock is a ransomware operation that exploits Polygon blockchain smart contracts to manage proxy server addresses, showcasing a novel and resilient command-and-control technique. Its use of decentralized blockchain technology presents new challenges for cybersecurity defenses and indicates a potential trend in blockchain abuse by cybercriminals. #DeadLock #Polygon #BlockchainAbuse…

Cybersecurity researchers have revealed a new attack technique called Reprompt that enables attackers to exfiltrate sensitive data from AI chatbots like Microsoft Copilot with a single click, bypassing security controls. Microsoft has addressed the vulnerability, which primarily affects consumer-facing versions, while enterprise users remain protected. #Reprompt #AIChatbots…

A critical security flaw in the Modular DS WordPress plugin has been actively exploited, allowing attackers to escalate privileges to administrator level. Users are urged to update to version 2.5.2 to patch the vulnerability. #CVE-2026-23550 #ModularDS #WordPressSecurity…

A critical misconfiguration in AWS CodeBuild related to webhook filters allowed potential unauthorized access to AWS GitHub repositories, risking supply chain attacks. Amazon addressed the vulnerability, but the incident highlights the importance of securing CI/CD pipelines against untrusted contributions and misconfigured regex patterns. #CodeBreach #AWSCodeBuild #GitHubSecurity #CI/CDVulnerability…

Lt. Gen. Joshua Rudd, nominated to lead U.S. Cyber Command and NSA, emphasizes his military background and operational experience over technical cybersecurity expertise. He aims to strengthen coordination, industry relationships, and digital threat responses, despite limited cyber policy opinions. #CyberCommand #NSA #JoshuaRudd…
Chinese hackers, affiliated with Chinese government-backed groups, have successfully infiltrated critical infrastructure in North America by exploiting vulnerabilities and compromised credentials. Their campaigns involve sophisticated tools like Earthworm and zero-day exploits such as CVE-2025-53690. #UAT8837 #Earthworm…

The Anchorage Police Department responded to a cyberattack involving its service provider, Whitebox Technologies, by shutting down affected systems and removing data. Authorities reassure that no evidence of system compromise or data theft has been found so far, while continuing to monitor and enhance security measures. #WhiteboxTechnologies #ThirdPartyCyberattack…
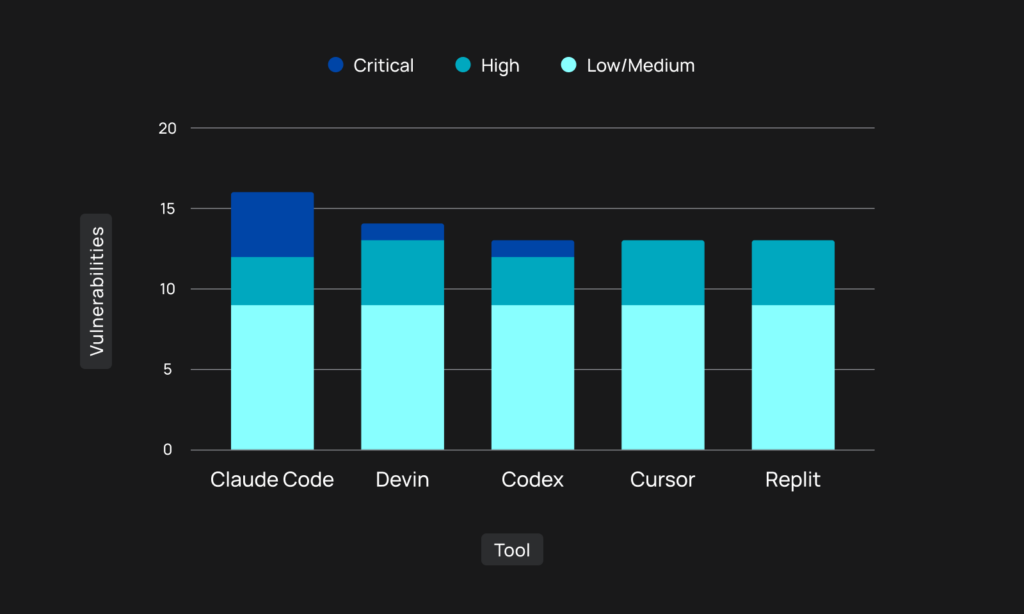
Vibe coding, powered by AI, offers rapid and cost-effective software development but presents significant security vulnerabilities. Testing of various AI coding tools revealed numerous weaknesses, especially in security controls and complex logic. #OpenAICodex #APIVulnerabilities…
Researchers from CISPA have revealed a new hardware vulnerability named StackWarp affecting AMD Zen processors, which can compromise virtual machine security. This flaw allows attackers to hijack control, extract keys, and bypass security measures like SEV-SNP without direct memory access. #StackWarp #AMDZen #CVE202529943…
Security leaders believe that managing third-party supply chain resilience and leveraging AI for automation will be the key to cybersecurity efficiency in 2026. They emphasize the importance of simplifying security processes, industry-wide AI governance, and fostering collaborative threat intelligence. #DORA #NIS2 #AIautomation #ThreatSharing…
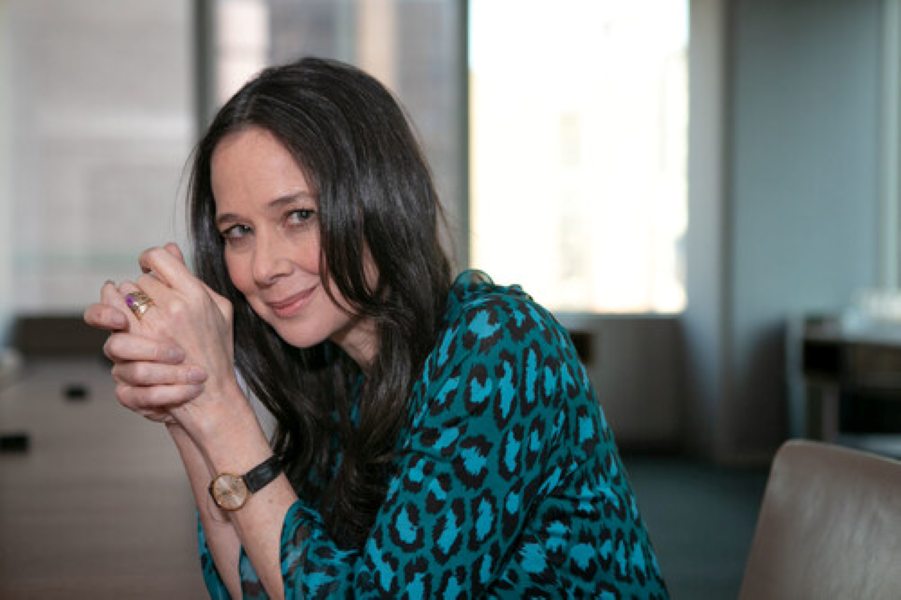
Jen Easterly, former CISA Director, is appointed CEO of RSAC, leading its global growth amidst the AI and cybersecurity convergence. The organization aims to expand its international presence and foster secure-by-design technology through its flagship conference and year-round initiatives. #JenEasterly #RSAC #AIcybersecurity #MosconeCenter…