The FTC has settled a case with General Motors (GM) for collecting and selling drivers’ geolocation data without consent, implementing a five-year ban on data sharing and requiring increased consumer control over data. This action follows broader concerns about data privacy violations across the automotive and insurance sectors, highlighting the need for stricter regulations. #FTC #DataPrivacy #GMOnStar
Category: Cyber Security News
This article introduces a pre-built Tines workflow designed to automate the granting and revoking of temporary application access, improving security and efficiency for organizations. It highlights how orchestration tools streamline JIT access management, ensuring compliance and reducing privilege creep. #TinesWorkflow #IAMOrchestration

Many SOCs are struggling to adapt to the evolving cyber threat landscape due to outdated practices and disjointed tools. Modern solutions like automation, dynamic analysis, and integrated workflows can significantly improve incident response times and detection rates. #ANY.RUN #SOCautomation…

Recent cybersecurity incidents reveal that the primary threat to AI-assisted workflows lies in the surrounding processes rather than the AI models themselves. Protecting the entire workflow, including integrations and inputs, is essential to mitigate risks such as data theft and malicious prompt injections. #ChatGPT #DeepSeek…

This week highlights emerging cybersecurity threats including a critical Redis remote code execution vulnerability and sophisticated malware evasion techniques by BaoLoader. It also covers global efforts to regulate and monitor cyber activities, such as the arrest related to AVCheck and China’s ban on foreign cybersecurity tools. #RedisCVE2025-62507 #BaoLoader #TurlaKazuar #CrazyHunter…

Elon Musk’s platform X is implementing new measures to prevent the creation of non-consensual sexual images using its AI tool Grok, following a scandal involving offensive images of women and children. Despite these steps, authorities in multiple regions continue to investigate X for potential violations related to child sexual abuse material…
Researchers have uncovered a new attack method called Reprompt that exploits Microsoft Copilot to exfiltrate user data via a malicious link. This attack bypasses data leak protections and enables ongoing data extraction even after the AI chat session ends. #Reprompt #MicrosoftCopilot #AIDataLeak…
isVerified, an Israeli startup spun off from Hudson Rock, has launched mobile apps to protect enterprises from voice deepfake attacks. These solutions enable real-time detection of synthetic audio during calls, addressing the growing risk of AI-based vishing and impersonation threats. #AIDeepfakes #VoicePhishing…
Depthfirst, a cybersecurity startup specializing in AI-powered vulnerability detection, raised $40 million to expand its innovative security platform. Its AI-driven approach significantly improves flaw identification, helping organizations stay ahead of emerging threats. #Depthfirst #AIsecurity…
Microsoft has successfully disrupted the RedVDS cybercrime platform, which facilitated extensive fraud and malware attacks globally. This operation involved legal actions, infrastructure seizure, and collaboration with international law enforcement to dismantle the service and protect victims. #RedVDS #Storm-0259
Palo Alto Networks addressed a critical vulnerability (CVE-2026-0227) that could enable attackers to cause a denial-of-service attack by disabling firewalls. Although most affected systems have been patched, the vulnerability highlights ongoing risks faced by organizations using PAN-OS and GlobalProtect. #CVE-2026-0227 #GlobalProtect
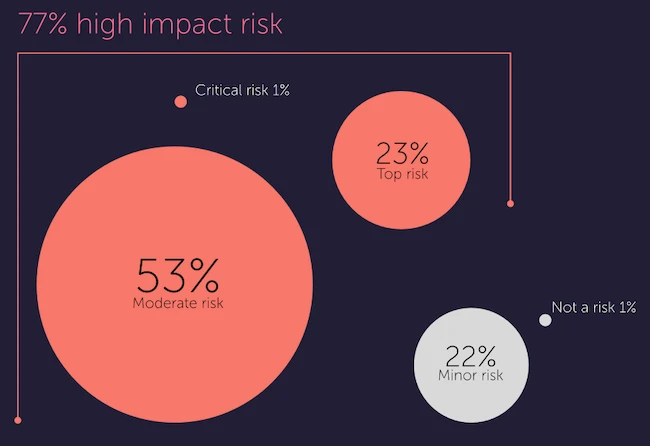
Third-party cyber risks are increasing due to expanding vendor ecosystems, yet visibility into extended supply chains remains limited. Regulatory pressures are growing, but many organizations are not fully prepared to address complex third-party threats. #Panorays #ThirdPartyRisk…

Cyberattacks using PLUGGYAPE malware target Ukraine’s defense with links to the Russian group Void Blizzard. The malicious campaigns employ social engineering and advanced backdoors to infiltrate systems and maintain persistence. #VoidBlizzard #PLUGGYAPE…
Eurail has revealed a data breach affecting customers’ personal, reservation, and passport information, including DiscoverEU program participants. The company is investigating the incident in collaboration with the European Commission, emphasizing security measures and monitoring, while alerting impacted individuals to potential phishing and identity theft threats. #Eurail #DiscoverEU…
Several industrial giants including Siemens, Schneider Electric, Phoenix Contact, and Aveva released Patch Tuesday advisories addressing critical and high-severity vulnerabilities in their ICS/OT products. These advisories highlight issues such as authorization bypass, privilege escalation, remote code execution, and command injection, emphasizing the importance of timely patching for industrial security. #Siemens #SchneiderElectric…