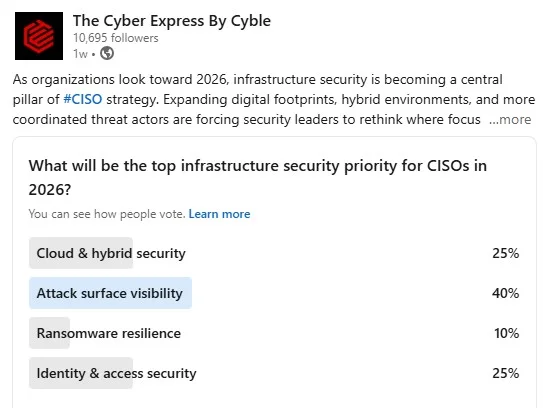
Modern organizations are prioritizing attack surface visibility as a key component of infrastructure security in 2026 due to the increasing complexity of digital assets across cloud, API, and hybrid environments. Industry experts highlight how interconnected priorities like identity management and governance are essential for effective cybersecurity strategies. #AttackSurfaceVisibility #APISecurity…
Category: Cyber Security News
Proactive threat hunting focuses on understanding attacker behaviors, patterns, and evidence left behind, rather than relying solely on reactive measures. The integration of AI and automation allows threat hunters to prioritize and respond to threats more effectively, emphasizing long-term defense strategies. #Log4Shell #MarathonCVEs…

A new espionage campaign targeting U.S. government entities has been identified, involving a custom backdoor called LOTUSLITE likely linked to Mustang Panda. The campaign uses spear-phishing with geopolitical lures and DLL sideloading to establish persistence, highlighting ongoing targeted cyber espionage efforts. #MustangPanda #LOTUSLITE…

Cybersecurity Threat Research ‘Weekly’ Recap. The report highlights a surge in encryptionless extortion and the rise of new RaaS groups such as Qilin, Akira, and LockBit 5.0, tracks the December 2025 ransomware activity, surveys infostealers, phishing campaigns, RATs and loaders, and web skimming, notes notable vulnerabilities like MongoBleed (CVE-2025-14847), CVE-2020-8554 and CVE-2017-11882, and points to defense tools such as Landlock telemetry and AuraInspector along with AI/LLM attack surface insights and Validin’s research. #Qilin #Akira #LockBit5_0 #Sicarii #CrazyHunter #Medusa #Remcos #AsyncRAT #CastleLoader #VoidLink #KONGTUKE #LOTUSLITE #AshTag #AshenLepus #RustDesk #Winos4_0 #RedVDS #Magecart #SilentPush #MongoBleed #CVE2025_14847 #CVE2020_8554 #CVE2017_11882 #SolyxImmortal #ACRStealer #LummaC2 #Stealc #MonetaStealer #MEXCApiAutomator #MustangPanda

Daily Recap, Gootloader now uses 1,000-part ZIP archives to evade detection and deliver payloads, while the Kimwolf botnet has infected roughly 2 million devices. Daily Recap, DeadLock leverages Polygon smart contracts to rotate proxies and obscure infrastructure, with further coverage on Modular DS WordPress exploits, AWS CodeBuild misconfigurations, StackWarp on AMD processors, Reprompt attacks against Microsoft Copilot, RedVDS seizures, Grubhub breach, and leadership shifts around the RSA Conference. #Gootloader #DeadLock
The Canadian Investment Regulatory Organization (CIRO) experienced a data breach affecting approximately 750,000 investors, compromising personal financial information. Despite the incident, no evidence of misuse has been found, and affected individuals will receive free credit monitoring services. #CIRO #DataBreach #CanadaFinancialSecurity
Microsoft issued emergency updates for Windows 10, Windows 11, and Windows Server to fix issues caused by the January Patch Tuesday updates. The fixes address remote desktop connection failures and shutdown problems on Secure Launch-enabled systems. #WindowsUpdate #SecureLaunch
A malicious campaign involving 17 browser extensions has infected Chrome, Firefox, and Edge with over 840,000 installations, secretly tracking user activity and injecting ads. Despite being exposed and removed from some stores, the campaign continues to evolve with advanced obfuscation methods, posing ongoing risks to users. #GhostPoster #BrowserExtensions
Malicious Chrome extensions masquerading as productivity and security tools targeted enterprise HR and ERP platforms, stealing credentials and blocking management pages. This coordinated attack threatened thousands of users by exfiltrating session cookies and hijacking accounts, potentially leading to large-scale data breaches and ransomware attacks. #Workday #NetSuite
Daily Recap, AI & ML security dominates the recap with threats ranging from voice cloning, PLC vulnerabilities, and poisoned dependencies to privilege escalation via AI agents and escalating workflow risks. The report highlights a mix of incidents, patches, and enforcement actions across vendors, botnets, data breaches, and regulatory penalties, underscoring the need to secure workflows, access controls, and AI governance. #VoidLink #Kimwolf #Aisuru #FortiSIEM #PLUGGYAPE #GrokBlock #GrokProbe #Eurail #Kyowon #FreeMobile #RedVDS #Verizon #Uganda #Siemens #Schneider #Aveva #PhoenixContact #Tines #Aikido #CrowdStrike #FTC #GM

The TamperedChef malvertising campaign evolved from testing benign applications to widespread credential theft, exploiting ad networks and SEO poisoning. Despite detection efforts, the threat actors continue to evolve and operate covertly across various systems. #TamperedChef #Infostealer…
A critical vulnerability in HPE OneView is being exploited on a large scale by the RondoDox botnet, targeting enterprise management systems. The attacks are automated, widespread, and concentrated mainly on government, financial, and industrial sectors. #CVE-2025-37164 #RondoDox #HPEOneView #botnet #exploit…
An Estonian security researcher unlocked every Äike e-scooter by reverse-engineering its Bluetooth security flaw, exposing critical vulnerabilities in the company’s IoT devices. This highlights the risks of default settings and poor key management in IoT products, especially after a manufacturer goes bankrupt. #Äike #IoTVulnerabilities…

Ukrainian and German authorities have identified suspects linked to the Black Basta ransomware group, with the group’s alleged leader added to international wanted lists. The group, responsible for cyberattacks on over 500 companies since 2022, appears to have disbanded after leaks exposed its inner workings and leader connections to Russian intelligence….

OpenAI plans to introduce advertising in ChatGPT for logged-in adult users in the US, aiming to expand access and generate revenue. The company assures user privacy and control over ad experiences, emphasizing that ads will not influence chatbot responses. #OpenAI #ChatGPTAds…