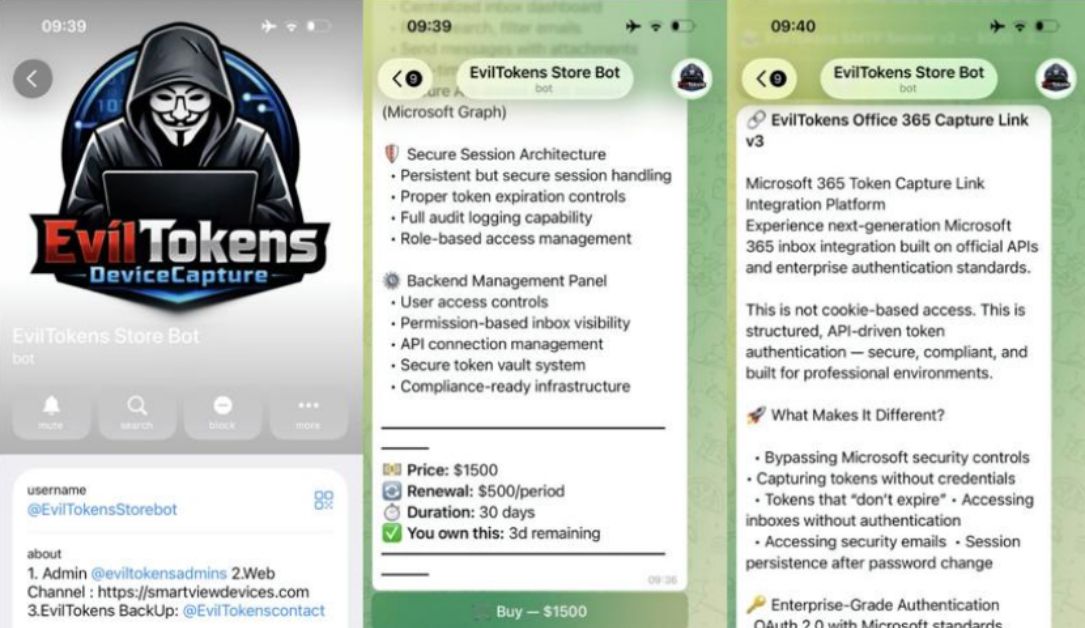
Microsoft disrupted EvilTokens, an AI-powered phishing service that helped criminals automate account compromise, inbox analysis, and fraud targeting. Working with U.K. police and multiple partners, Microsoft seized infrastructure, enabled arrests, and said the platform had affected thousands of email accounts worldwide. #EvilTokens #Microsoft #MetropolitanPoliceService #HealthISAC #Cloudflare #Coinbase #TheShadowserverFoundation #TRMLabs…
Category: Cyber Security News
Canada’s Privacy Commissioner Philippe Dufresne has launched an investigation into IDScan.net after reports that attackers accessed company databases and stole personal data, including scans of 153 million driver’s licenses. The probe will examine IDScan’s security practices and whether its customer notifications complied with Canada’s federal private-sector privacy law. #IDScan.net #PhilippeDufresne #BrianKrebs…

A malicious npm package named tw-pkgprobe-7731 disguised itself as a Twilio security research tool while attempting to collect environment data and sensitive credentials from developers. Later versions expanded to target Twilio account SIDs and Auth Tokens, exposing Twilio-related hosts and AWS metadata in the process. #tw-pkgprobe-7731 #Twilio #HackerOne #AUTH_TOKEN #ACCOUNT_SID…
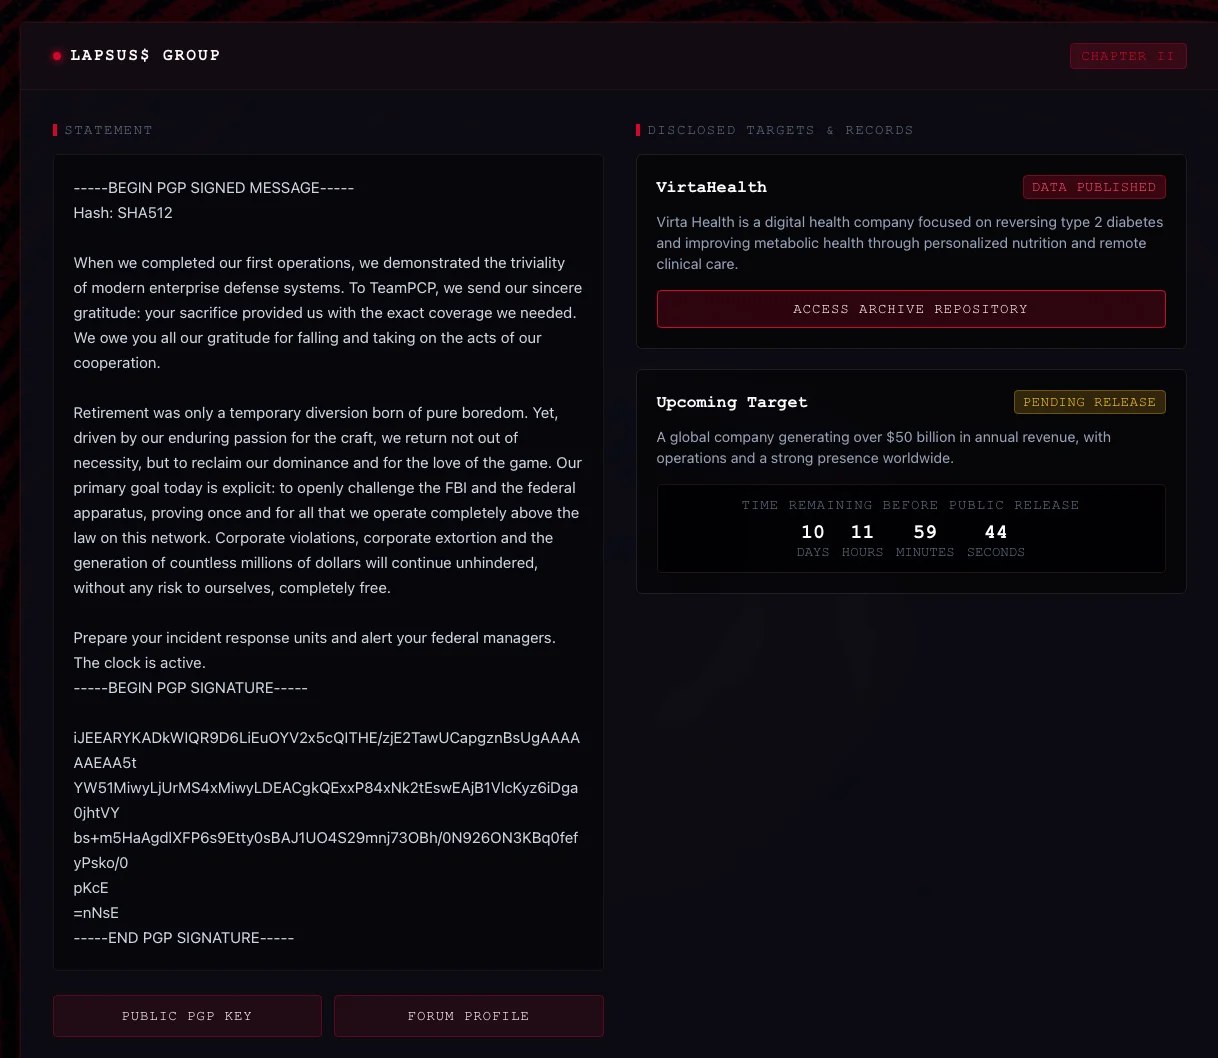
Elsevier’s main website and two portals were briefly redirected to a page branded “LAPSUS$ GROUP, Chapter II,” which included a taunting statement and a countdown to another alleged victim. Researchers say the incident likely involved a DNS or CDN edge change, but Elsevier has not yet explained how it happened or confirmed whether user data was exposed. #Elsevier #LAPSUS$

Volexity found the Chinese threat group UTA0565 exploiting a chain of zero-day vulnerabilities in Chrome and Microsoft products across multiple phishing campaigns. The group used fake websites, spoofed domains, and a previously undocumented malware family called CLEANGULP to target Asian government entities and other organizations. #UTA0565 #CVE-2026-85046 #CVE-2026-87491 #CVE-2026-85880 #CLEANGULP #Chow_Hang-tung
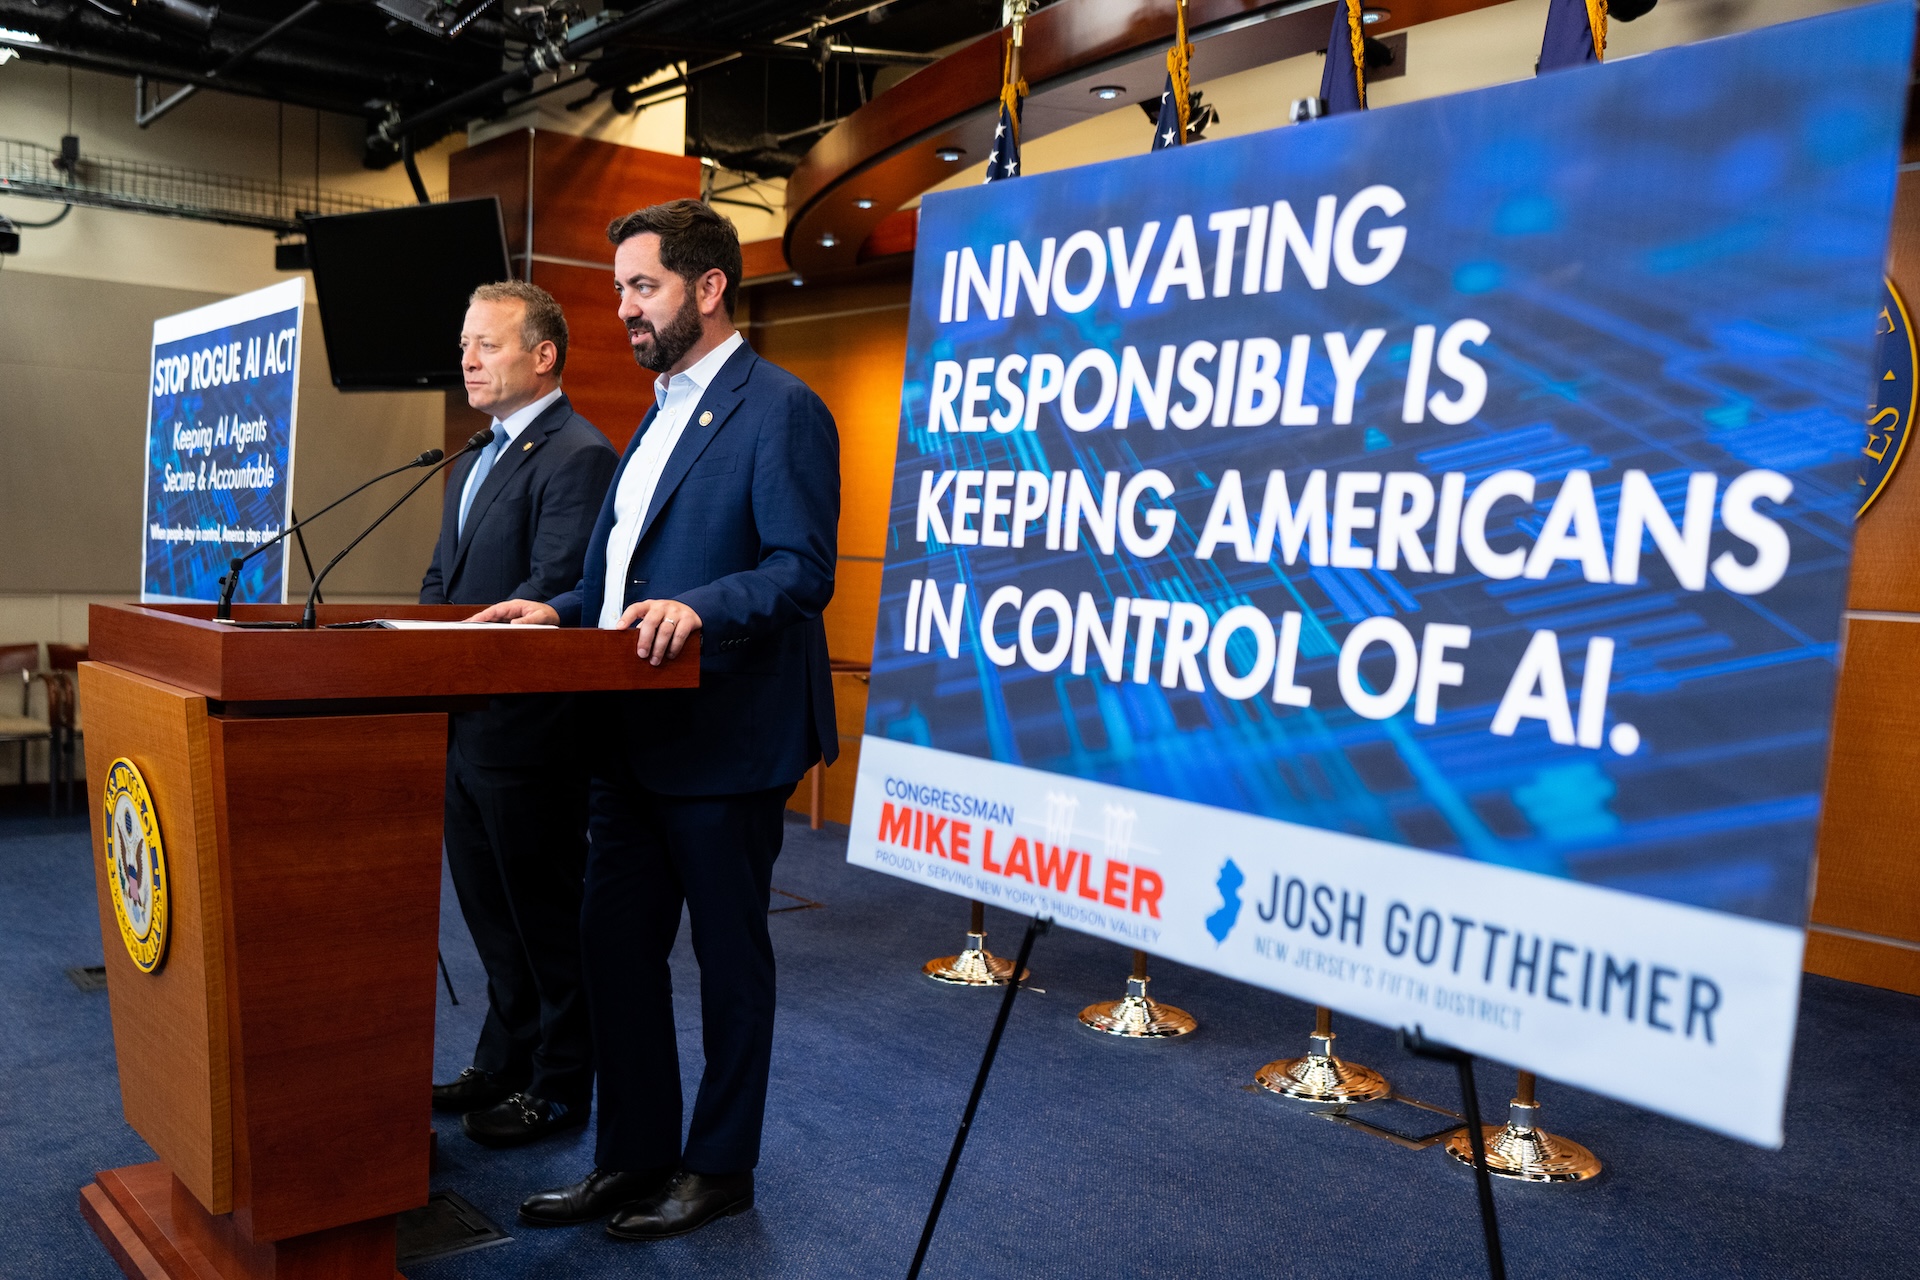
Rep. Josh Gottheimer introduced the AI Cyber Defense Act to create a CISA test program that would give critical infrastructure operators free access to frontier AI models for defending their systems. The bill is aimed at helping water and other essential facilities detect, test for, and remediate vulnerabilities, with priority for nonprofit, publicly owned, rural, and small organizations. #AICyberDefenseAct #CISA #JoshGottheimer
Check Point Software released emergency hotfixes for CVE-2026-93616, a critical path traversal flaw in Security Management Server products that allowed unauthenticated attackers to upload and run arbitrary scripts. The company said the issue is being exploited in the wild and urged customers to patch immediately or apply temporary mitigations while checking for signs of compromise. #CheckPoint #CVE-2026-93616 #SecurityManagementServer #SmartConsole
Shadow IT creates visibility gaps when unmanaged endpoints, unapproved software, and devices outside standard monitoring escape notice, and network discovery alone often fails to reveal them. Wazuh closes this blind spot by collecting endpoint inventory, supporting agentless monitoring, and correlating asset data with vulnerabilities and policy to uncover unauthorized applications and monitoring gaps. #Wazuh
ClosedQuorum is a new Windows malware that uses Google Gemini, DeepSeek, Qwen, and Mistral AI to autonomously choose post-compromise actions without human operator commands. Cisco Talos says it can steal credentials, inject shellcode, or persist on infected hosts, and that stolen data is exfiltrated through a Discord webhook. #ClosedQuorum #GoogleGemini #DeepSeek #Qwen #Mistral #CiscoTalos
ShinyHunters claims it breached FBI systems by exploiting an unpatched Oracle PeopleSoft zero-day, then moved into FBI-managed AWS GovCloud infrastructure and stole sensitive employee and applicant data. The group also says it defaced the FBI Jobs site, targeted additional organizations with the same flaw, and framed the intrusion as retaliation over an FBI FLASH report. #ShinyHunters #OraclePeopleSoft #FBI #AWSGovCloud #KashPatel

WordPress has patched CVE-2026-87902, a critical core flaw that could let an unauthenticated attacker load a PHP file from outside a theme folder and, on some servers, potentially execute code. Site owners running any affected version from 4.7.0 through 7.1.1 are urged to update immediately to the fixed releases, including WordPress…

Check Point said attackers used a zero-day flaw, CVE-2026-93616, to target Security Management Servers in limited attacks on July 23, and the company later released fixes and hunting guidance. Separately, attackers have been trying to exploit CVE-2026-85102 in Spark firewalls and gateways through VPN connections since September 12, using anonymizing infrastructure…
BigCommerce merchants were hit by a supply chain attack after attackers compromised a Ribon application key and used it to steal customer data from affected storefronts. BigCommerce says the incident stemmed from third-party app credentials tied to Be A Part Of and Fastr, not a breach of its own platform. #BigCommerce…
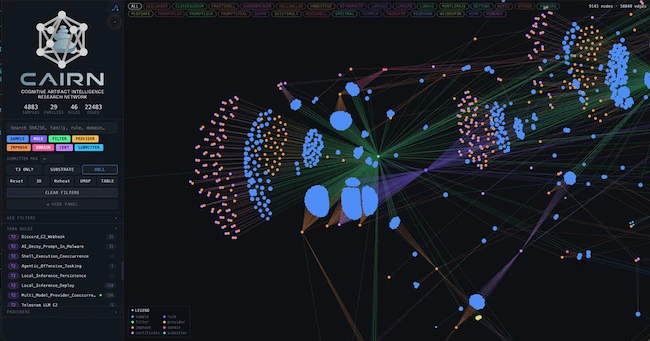
Cisco Talos released CAIRN, an open-source framework that classifies AI-integrated malware using only file metadata and cognitive artifacts, without downloading or executing samples. Their first public finding is CLOSEDQUORUM, a Windows implant that uses multiple commercial LLMs to decide its next move and is designed to steal credentials and crypto wallets. #CiscoTalos #CAIRN #CLOSEDQUORUM #LAMEHUG #CERT-UA #DeepSeek #Qwen #Mistral #Gemini
Microsoft and industry partners disrupted EvilTokens, a phishing-as-a-service platform tied to more than 12,000 compromised Microsoft customer email inboxes across over 10,000 organizations worldwide. The operation used AI-driven tools to support business-email compromise and financial fraud, while law enforcement arrested two suspected operators in the U.K. and seized key infrastructure. #EvilTokens #Microsoft #Storm-2992 #FelixUtomi #WaidiSegunAdams