President Donald Trump defended a hands-off approach to AI regulation even after hacks involving U.S. commercial frontier models intensified calls for oversight. The debate now centers on whether innovation and U.S. competition with China should outweigh stricter safety and liability rules for companies like OpenAI and Anthropic. #DonaldTrump #OpenAI #Anthropic #China
Category: Cyber Security News
Microsoft and its partners disrupted the EvilTokens phishing-as-a-service platform, which compromised more than 12,000 Microsoft accounts across over 10,000 organizations worldwide. The operation used device-code phishing and AI-powered tools to evade MFA, target high-value inboxes, and drive business email compromise campaigns. #EvilTokens #Storm2992 #Microsoft #SpyCloud #HealthISAC
Abdelhamid Naceri, also known as Nightmare Eclipse, has publicly revealed his identity and released BigDiskBuster, a new proof-of-concept exploit that interferes with Windows Defender platform and signature updates. He says the tool works on all supported Windows versions, though it remains buggy, and he also recounted a bitter dispute with Microsoft…
Cyera has secured an additional $400 million in funding from Goldman Sachs Alternatives, lifting its valuation to more than $12 billion and bringing total funding to over $2.7 billion. The company plans to use the capital to expand its agentless data security platform, strengthen AI governance capabilities, and support its growth…
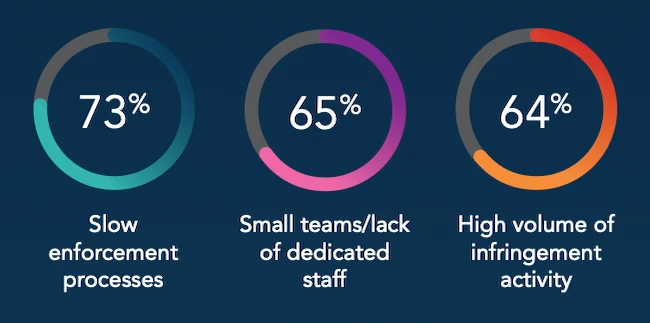
CSC’s State of Online IP Risk 2026 report says impersonation, phishing, and domain-name abuse are the most concerning forms of online intellectual property infringement, with internet branded content, online marketplaces, and paid search being the most targeted channels. The report also highlights how AI, executive impersonation, and large-scale domain registrations are making fraud faster, harder to detect, and more damaging to brands and consumers. #CSC #FIFA #ICANN #LinkedIn #FashionWeek

AI-powered social engineering is helping attackers bypass traditional phishing defenses by using deepfakes, vishing, smishing, and business email compromise across email, calls, and video meetings. Gartner says CISOs should make verification the default for risky requests, harden account recovery and privileged access, and correlate suspicious activity across channels to spot multimodal impersonation. #Gartner #CraigPorter #Deepfake #BusinessEmailCompromise #Vishing #Smishing #HongKong

A new SpyCloud study found that nearly 18% of U.S. water and wastewater organizations have identity data actively exposed by infostealers, with one infected vendor device exposing logins tied to about 167 utility metering tenants. The report warns that stolen credentials can enable cascading supply chain exposure and provide attackers with legitimate access paths into corporate email, VPNs, and operational technology systems. #SpyCloud #CISA #EnvironmentalProtectionAgency
Security researcher Abdelhamid Naceri, also known as Nightmare Eclipse, released BigDiskBuster, a Microsoft Defender zero-day that can block antivirus signature and platform updates on supported Windows versions. The disclosure is part of Naceri’s ongoing series of Windows and Defender exploits, following earlier tools like UnDefend and ShieldCrash, with several flaws still unpatched by Microsoft. #BigDiskBuster #UnDefend #ShieldCrash #NightmareEclipse #MicrosoftDefender
D-Link has warned about a maximum-severity flaw, CVE-2026-86296, in legacy DIR-822A routers that can be exploited without authentication to cause a stack-based buffer overflow in the DHCP server component. The company also said a public proof-of-concept exists and that it is investigating a second public-PoC issue, CVE-2026-86510, while advising customers to keep DIR-822A devices off the internet and restrict management access. #DLink #DIR822A #CVE202686296 #CVE202686510 #CISA
Real Google Workspace breaches often start with social engineering and malicious OAuth apps that trick users into granting access, not with stolen passwords or advanced exploits. This webinar with Material Security will examine how those attacks unfolded, what happened in the first hours of response, and which security controls matter most for fast-growing teams. #GoogleWorkspace #MaterialSecurity #RajanKapoor #RickFitzgerald #OAuth #BleepingComputer
The U.S. has proposed a new AI incident notification mechanism with China to improve transparency and reduce national security risks tied to advanced AI systems. The talks also advanced plans for a new Board of Trade ahead of the upcoming Trump-Xi meeting, while both sides continued discussions on tariffs and economic…
A joint advisory from Japan, the United States, Australia, and Germany attributes the WaterPlum, or Contagious Interview, operation to a North Korean scheme that impersonated companies to recruit developers and IT professionals. The campaign infected at least 30,000 devices in more than 100 countries, stole funds from over 7,000 cryptocurrency wallets,…

WordPress patched 11 vulnerabilities last week, including Click2Shell, a flaw that could allow remote code execution through specially crafted theme-preview URLs. pwn.ai found that an unauthenticated attacker could force installation of an attacker-selected theme and potentially execute PHP code on the server, earning a $300 bug bounty for the report. #Click2Shell…
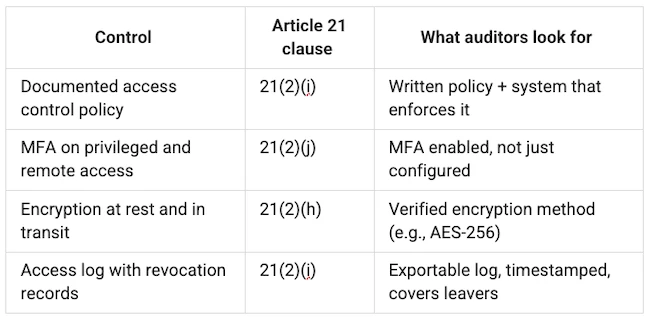
Passwork helps organizations align with NIS2 Article 21 by automating access control, MFA, credential hygiene, encryption, and audit logging without adding major IAM overhead. It also reduces password reset tickets and makes it easier to produce audit evidence for EU compliance reviews while keeping credentials inside self-hosted infrastructure. #NIS2 #Passwork #ENISA #ADLDAP #SAMLSSO #Yubikey
Researchers from the i2CAT Foundation, the University of Murcia, and NEC Laboratories Europe created 5G-Shark to lure phones onto a fake base station and test how commercial 5G networks handle identity privacy. Their tests found that while permanent IDs were mostly hidden, predictable temporary IDs still enabled subscriber tracking on some networks, and crafted reject messages could force phones into service loss, retry loops, or modem freezes. #5G-Shark #i2CATFoundation #UniversityofMurcia #NECLaboratoriesEurope #SamsungGalaxyS23