WordPress released version 7.1.2 to fix CVE-2026-87902, a critical path traversal flaw in get_page_template() that could let an unauthenticated attacker load an arbitrary PHP file from outside the active theme directory. Under certain server and theme conditions, this could lead to remote code execution, so WordPress recommends updating immediately. #WordPress #CVE-2026-87902
Category: Cyber Security News

Daily Recap, phishing and malware activity stayed active, including EvilTokens compromising 12,000 Microsoft accounts, Contagious Interview infecting 30,000 devices and stealing $10.71M in crypto, and TASK#STOMP exfiltrating Wi‑Fi passwords, screenshots, and business files. Attackers also used fake LastPass and Google sign-in lures to deploy the Rapuncel stealer and other components, while defenders tracked newly patched and actively exploited flaws like D-Link DIR-822A (CVE-2026-86296, CVE-2026-86510) and a CISA-flagged Zyxel issue plus three Linux kernel vulnerabilities. #EvilTokens #ContagiousInterview #TASKSTOMP #Rapuncel #LastPass #DIR-822A #CVE-2026-86296 #CVE-2026-86510 #Zyxel
F5 has issued security updates for a critical zero-day in BIG-IP APM, which is being actively exploited in remote code execution attacks when specific OAuth authorization server settings are enabled. CISA has added CVE-2026-94127 to its Known Exploited Vulnerabilities Catalog and ordered federal agencies to patch the flaw promptly. #F5 #BIG-IPAPM #CVE202694127 #CISA
Karen Serobovich Vardanyan was sentenced to 24 months in prison and 3 years of supervised release for helping carry out Ryuk ransomware attacks against multiple U.S. organizations. He and his co-conspirators breached victims including a Michigan company, a Texas school, and a technology company in Oregon, generating millions in ransom payments. #KarenSerobovichVardanyan #Ryuk #WizardSpider #Michigan #Texas #Oregon
ShinyHunters claims it breached FBI systems, stole sensitive data, and defaced the FBI jobs site to prove access. The group says it used an Oracle PeopleSoft zero-day and alleges it now has data on nearly all FBI agents and applicants. #ShinyHunters #FBI #PeopleSoft #CVE-2026-35273…
F5 and CISA warned that a critical BIG-IP Access Policy Manager (APM) flaw, tracked as CVE-2026-94127, has been exploited as a zero-day to enable unauthenticated remote code execution. The vulnerability affects specific BIG-IP APM configurations, and F5 has released hotfixes while CISA added the issue to its Known Exploited Vulnerabilities list….
Arista has issued urgent fixes for CVE-2026-93952, a critical zero-day in on-premises VeloCloud Orchestrator deployments that could let remote attackers reach privileged internal functions. The flaw affects VeloCloud Orchestrator On-Prem and has been added to CISA’s Known Exploited Vulnerabilities list, with admins urged to patch and review logs immediately. #Arista #VeloCloudOrchestrator…
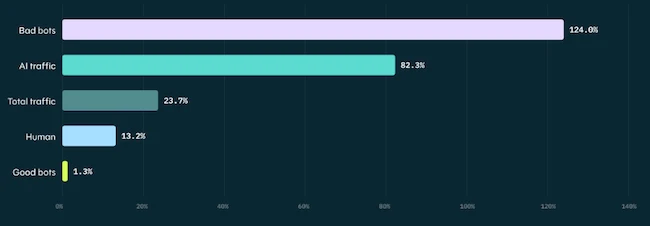
Malicious bot activity surged 124% from July 2025 to June 2026, far outpacing human traffic growth, while AI agent and LLM crawler traffic also rose sharply as attackers expanded scraping, credential stuffing, spam, and DDoS activity. DataDome’s report found that many websites still fail to detect simulated bots, and that AI assistants and malicious automation are increasingly targeting login pages, shopping carts, payment pages, and online forms. #DataDome #LLM #AIagents #CredentialStuffing #WebScraping
Scamwise from Savi is a free browser-based service that checks suspicious messages, websites, phone numbers, images, and situations for signs of fraud without requiring an account. It gives a verdict with explanations and sources, and in testing it flagged a phishing email, verified a legitimate company site, and returned an indeterminate result for a phone number. #Savi #Scamwise #CroatianGovernmentAgency #SpanishUniversity
Prismor is a free, open-source security layer for AI coding agents that checks each tool call against policy before it runs, helping stop risky actions like credential leaks, poisoned file redirections, and compromised package installs. PrismorSec says it logs by default, can block in real time, and includes package checks plus a semantic guard that improves prompt-injection detection. #Prismor #PrismorSec #ClaudeCode #Codex #Cursor #mini-shai-hulud #AntV
Britain’s NCSC warns that AI currently gives attackers an advantage because offensive cyber operations are easier to automate and measure than defensive ones. The agency says defenders should use AI carefully for low-risk tasks while continuing to strengthen security through traditional methods, even as Cyber Shield and new research aim to…
The FBI is investigating a breach of its own systems after ShinyHunters claimed responsibility for temporarily defacing the FBI jobs site and stealing sensitive data tied to agents and applicants. The attack appears to be an escalation aimed at pressuring the FBI over a public service announcement, raising the group’s profile but also increasing the risk of retaliation. #ShinyHunters #FBIjobs.gov #BrettLeatherman #KashPatel
A Chinese-speaking threat actor linked to the Red Heron group exploited WordPress wp2shell flaws and other vulnerabilities to steal sensitive data from organizations across dozens of countries. GreyNoise observed attacks against ZyXEL GS1900 switches, Ubiquiti, PAN-OS GlobalProtect, and several other platforms, including intrusions that exposed credentials, PII, and backend database records. #RedHeron #wp2shell #ZyXELGS1900 #WordPress #Ubiquiti #PANOSGlobalProtect #GreyNoise
Sweden’s IMY fined Miljödata $183,000 after finding that inadequate security measures contributed to a 2025 breach affecting 2.2 million people and exposing highly sensitive personal data. The attack, attributed to the “Datacarry” threat actor, disrupted services across more than 200 regions and is now linked to further investigations into affected municipalities and one region. #Miljödata #IMY #Datacarry #GDPR
Varonis Threat Labs developed TrustSink, an attack that abuses Microsoft Entra’s external MFA provider model to steal passwords during a normal sign-in flow. The technique requires a previously compromised highly privileged account and can persist until the rogue provider is removed, even if victims reset their passwords. #TrustSink #MicrosoftEntra #VaronisThreatLabs #MFA