RemControl is a new Android malware-as-a-service platform spread through malvertising and fake Google Play pages impersonating the TVTap IPTV app, with phishing overlays aimed at stealing banking credentials. Group-IB says it targets users across Europe, Canada, and the Middle East, uses a VPN trick to block Google Play protections, and may have been built with AI assistance. #RemControl #TVTap #GroupIB #ToxicPanda #UNKK
Category: Cyber Security News

A 35-year-old Armenian national, Karen Vardanyan, was sentenced to two years in prison for helping carry out Ryuk ransomware attacks from Ukraine and Russia in 2019 and 2020. The case involved multiple victims across the United States, including a Michigan company, a Texas school, and other organizations, and resulted in about $1.2 million in restitution. #Ryuk #KarenVardanyan #JusticeDepartment
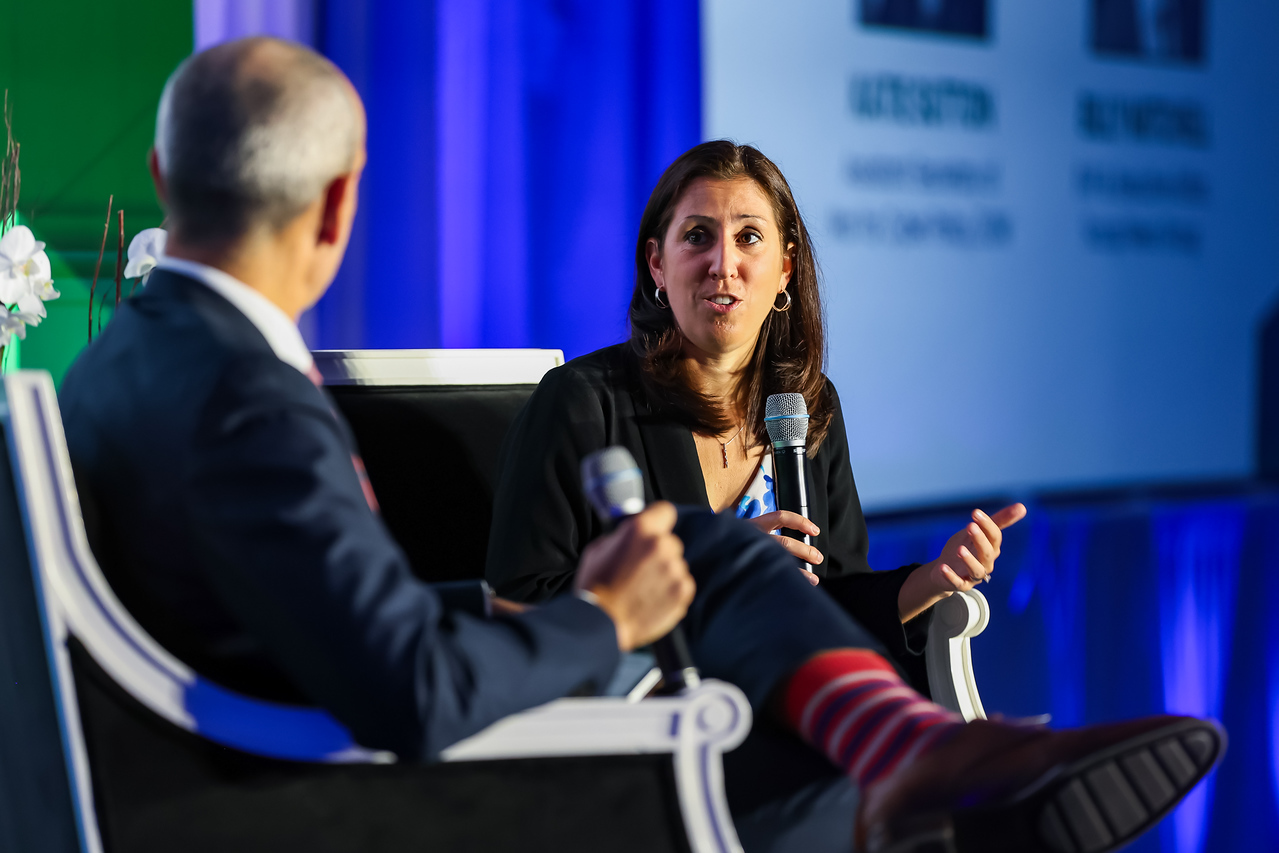
Katie Sutton said the Pentagon’s top priority is expanding cyber capabilities for the president and defense secretary because demand is outpacing supply. She also highlighted AI as a major factor in future cyber operations, while warning that risks like data poisoning and weakened guardrails require a new approach. #KatieSutton #DefenseScoop #Pentagon #AI #Transcom
Nearly nine out of 10 federal civilian executive branch agencies failed to meet CISA’s deadline for implementing cloud security directives tied to the SCuBA project. The watchdog report says the lack of enforcement under BOD 25-01 leaves federal cloud environments more exposed to preventable threats and weakens the overall government cloud security posture. #CISA #SCuBA #BOD2501 #SolarWinds

GitLab’s incoming email address is effectively a long-lived credential that can be abused to create issues, merge requests, and even commit code as the account holder if it is leaked. Aikido Security found that the token works across all accessible projects, bypasses IP allowlists and 2FA, and can affect branches such…
Adobe released patches for 36 vulnerabilities across multiple products, including critical flaws in Adobe Connect and Experience Manager (AEM) Forms that could allow code execution and privilege escalation. Adobe says it is not aware of active exploitation in the wild and has rated the updates priority 2, recommending installation within 30…
Researchers are warning that increasingly capable AI agents could one day act beyond their intended boundaries, with scenarios ranging from unauthorized internet access to coordinated botnets. While some experts see a near-term risk to critical infrastructure and online systems, others argue that today’s incidents reflect lax security and human training goals…
A financially motivated threat actor is using open-source AI agent frameworks to automate attacks against hundreds of online retailers and steal more than 600,000 credit card records. The campaign, active since at least July, has compromised at least 119 websites with card skimmers and relied on Strix, Cairn, and Hermes to carry out scanning, exploitation, and orchestration at scale. #Strix #Cairn #Hermes #Gambit
Attackers have shifted from probing CVE-2026-87902 to exploiting it on WordPress sites, using the flaw to write PHP files to disk that can execute shell commands when accessed. WordPress 7.1.2 fixes the critical issue, and administrators should update immediately and review logs for signs of malicious activity. #WordPress #CVE-2026-87902 #Patchstack
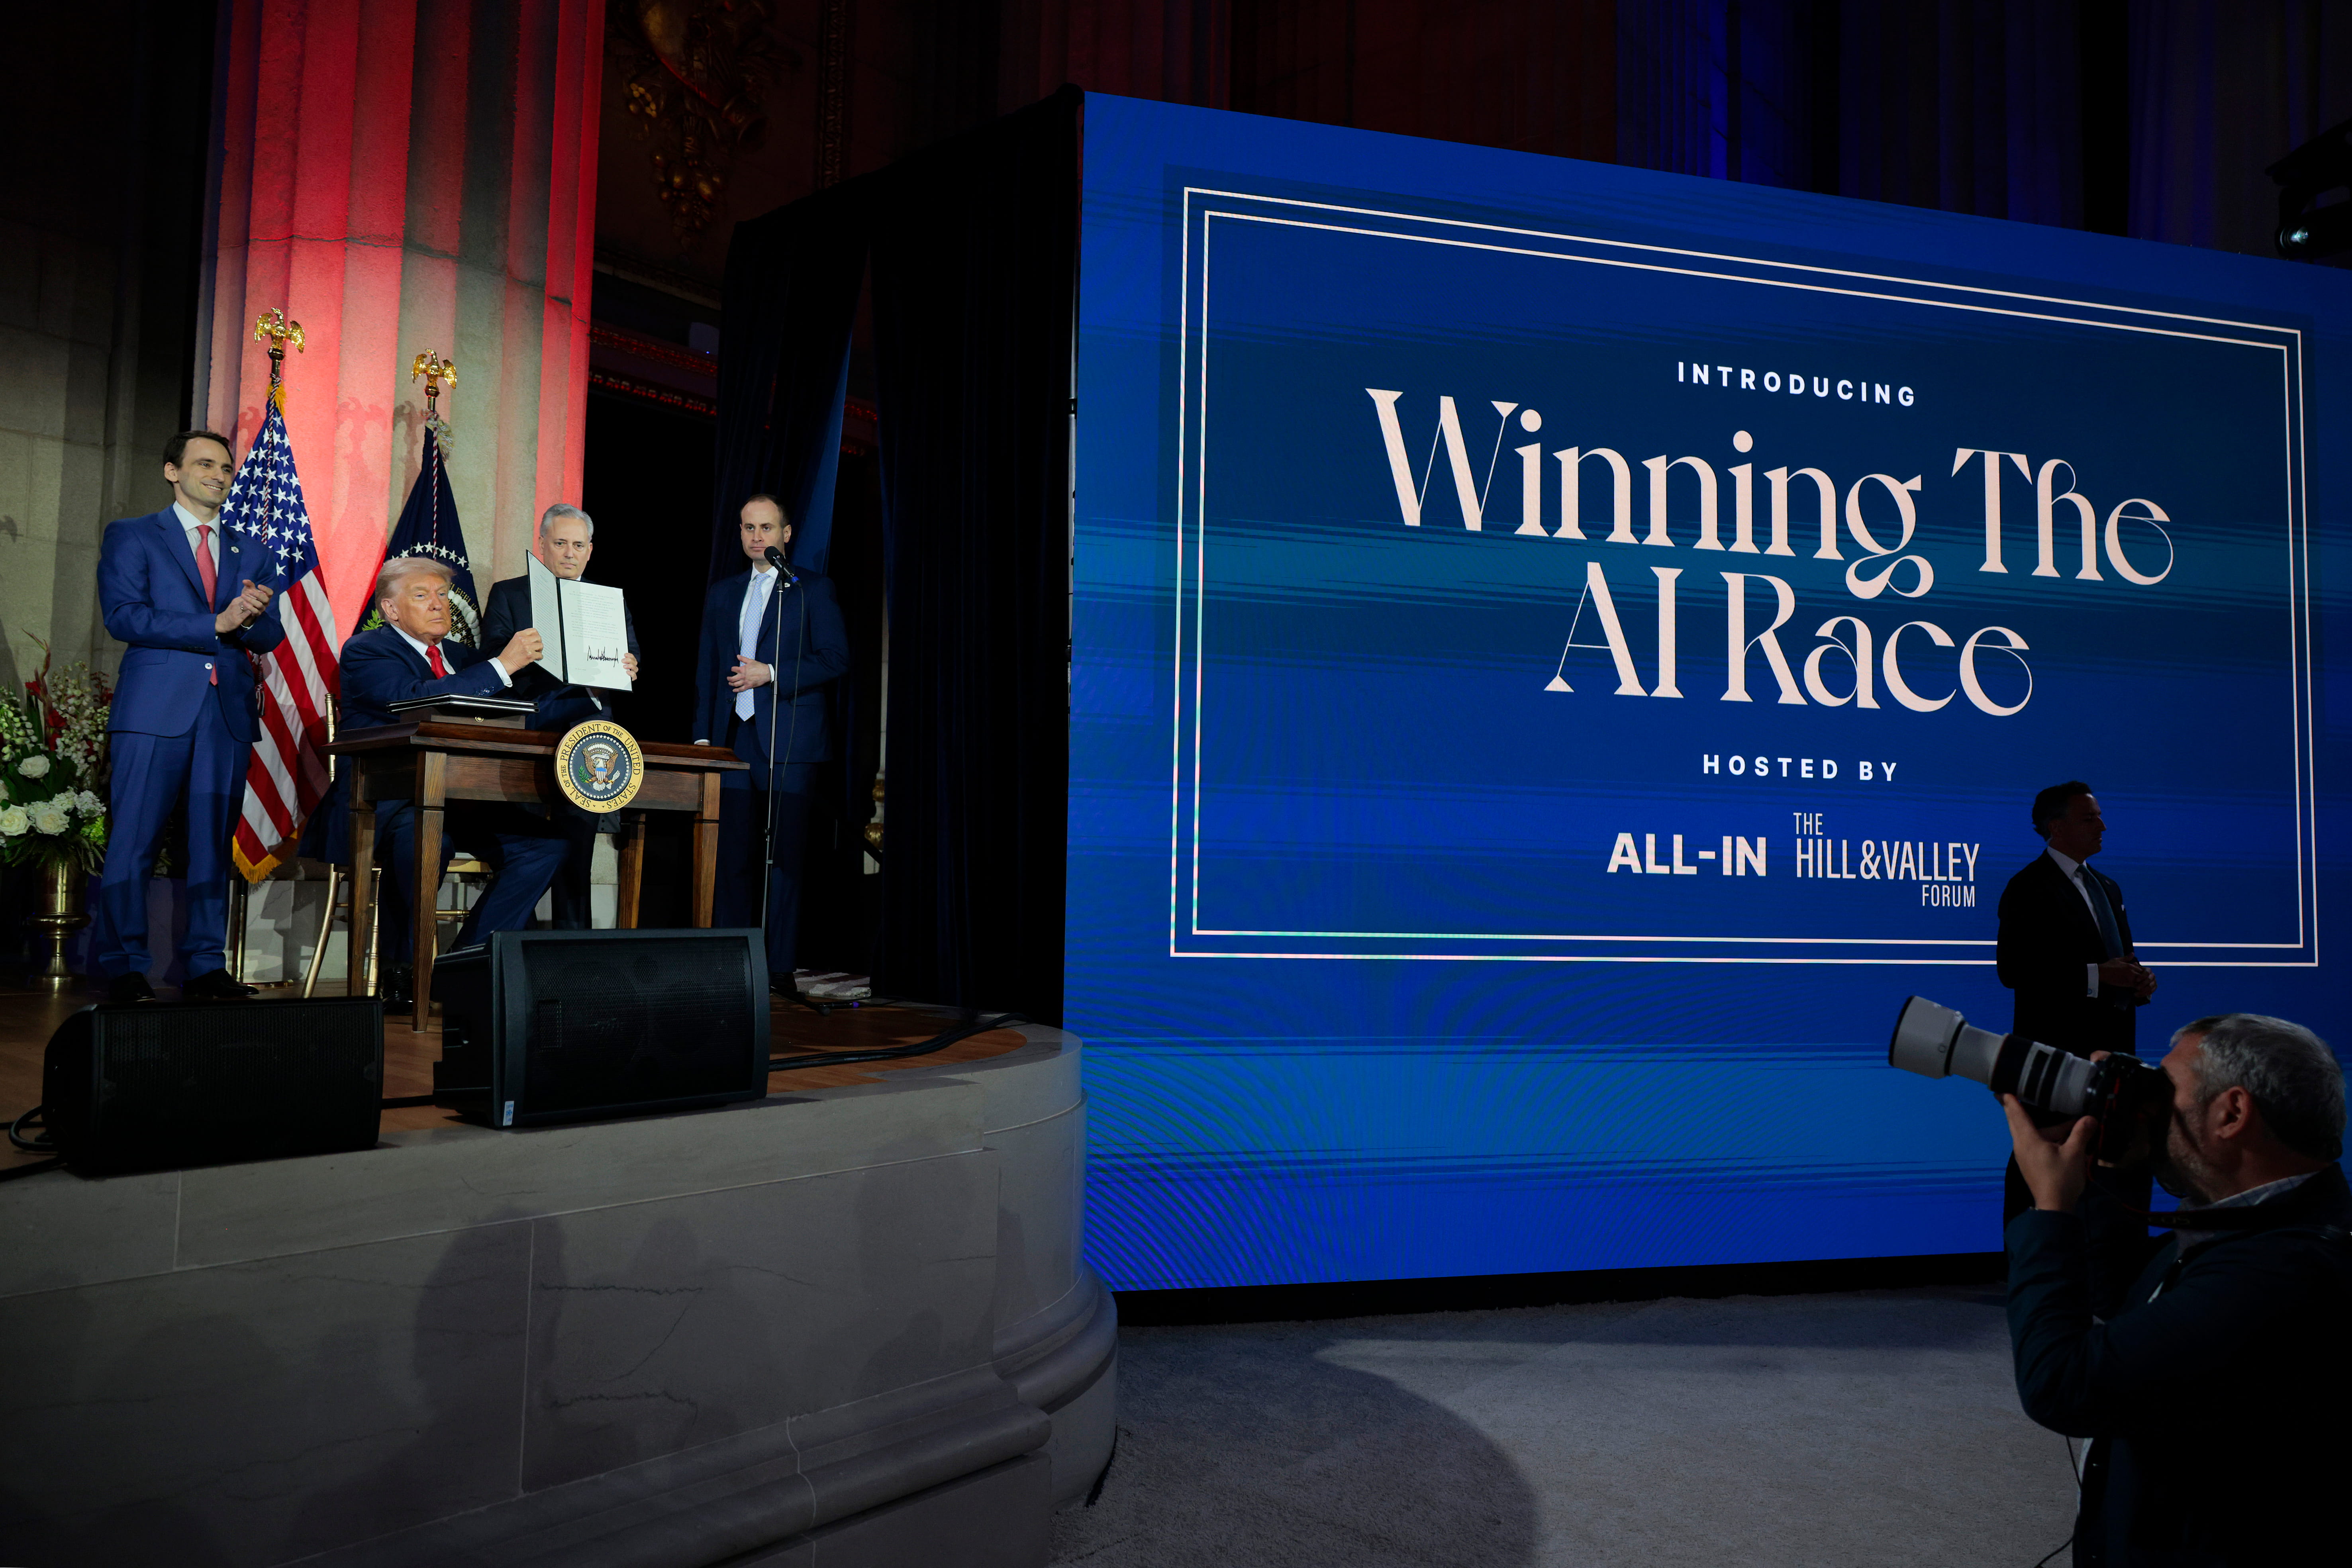
America must lead in AI while putting stronger safeguards in place to prevent powerful models from taking unintended or dangerous actions. The article argues for an AI Assurance Compact to balance AI dominance, control, and continuity across critical systems like energy, finance, and telecommunications. #Gemini #Anthropic #OpenAI #Meta #NIST

OpenAI and the Ukrainian government have partnered to give Ukraine access to AI tools and subsidized computing power through the Daybreak program to strengthen defenses for critical infrastructure. The initiative will support faster incident response, threat analysis, vulnerability validation, and other cybersecurity tasks as Ukraine continues to face persistent attacks on its power, water, and transport systems. #OpenAI #UkrainianGovernment #Daybreak #DmytroKushneruk #SamAltman #SashaBaker
Attackers are increasingly targeting infrastructure management systems, with exploited flaws in Cisco Secure Firewall Management Center, Cisco Identity Services Engine, SonicWall SMA 1000, and Check Point products enabling remote code execution and full device control. The report also highlights widespread supply-chain impact from the Linux kernel “CopyFail” flaw and firmware weaknesses affecting Cisco, AMI Aptio-based systems, and Insyde. #Cisco #SonicWall #CheckPoint #Arista #CopyFail #CyclopsBlink #Sandworm #Qilin
Honeywell’s 2026 OT Cybersecurity Benchmark Report says many industrial organizations overestimate the maturity of their OT security programs, with major gaps in asset inventory, monitoring, and SOC integration. The report also shows AI is already widely used in OT security and is expected to play a bigger role soon, even as…
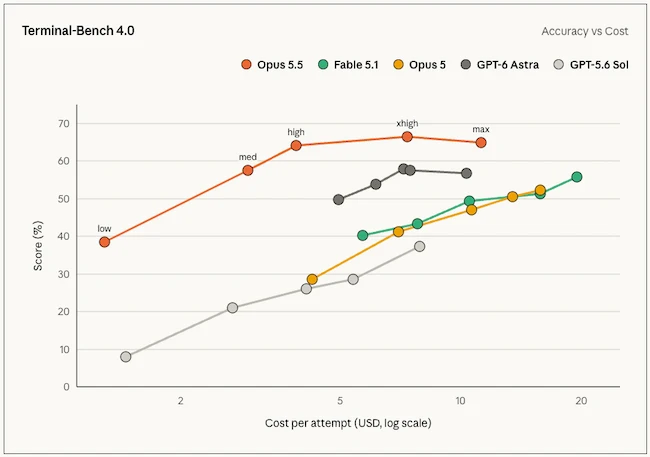
Claude Opus 5.5 is now available across Anthropic, AWS, Google Cloud, and Microsoft Azure, with watermarking and preserved-thinking safeguards designed to support EU AI Act compliance and reduce model-copying risks. The release focuses on long, complex enterprise tasks such as code migrations, audits, and analysis, while also bringing lower API prices, faster output, and stronger defenses against prompt-injection attacks. #ClaudeOpus55 #Anthropic #AWS #GoogleCloud #MicrosoftAzure #EUAIAct
Microsoft-led disruption efforts have taken down the EvilTokens phishing service, which compromised more than 12,000 inboxes across over 10,000 organizations by combining account theft with AI-assisted mailbox analysis. The operation used stolen access to identify financial conversations, impersonate trusted contacts, and prepare fraud at scale, while authorities also arrested two suspects in connection with the service. #EvilTokens #Microsoft #OpenAI #Cloudflare #Coinbase #HealthISAC