Cybersecurity News | Daily Recap [23 Sep 2026]

Daily Recap, AI and policy developments dominated the news as the U.K. warned attackers could benefit more than defenders, U.S. officials advanced AI-cyber test and defense initiatives, and researchers highlighted AI-enabled malware like ClosedQuorum that can choose attack actions dynamically. In addition, teams faced multiple exploited zero-days across major vendors and systems, while takedowns and disclosures targeted actors such as EvilTokens, ShinyHunters, and LAPSUS$, and organizations like BigCommerce and IDScan reported breach impacts.
#ClosedQuorum #EvilTokens #ShinyHunters #LAPSUS$ #Ryuk #Microsoft #F5 #BIG-IP #CheckPoint #Arista #WordPress #BigCommerce #IDScan #Twilio #Ribon #Miljödata #NightmareEclipse #NightmareEclipse #Zyxel #Miljödata

Read More
Astrana Health Data Breach Impacts Private, Confidential Information

Astrana Health disclosed that private and confidential information was stolen from its servers after employees were targeted in a social engineering attack. The company said attackers impersonated personnel, spoofed its main phone number, and accessed or exfiltrated sensitive data while it worked to contain the incident and investigate the impact. #AstranaHealth…

Read More
SolarWinds Patches Critical RCE Flaws in Observability Self-Hosted

SolarWinds has patched two severe vulnerabilities in Observability Self-Hosted, including CVE-2026-28324 and CVE-2026-28325, both of which could allow remote code execution by unauthenticated attackers. The company also recently fixed a separate unauthenticated RCE issue in Access Rights Manager, and there is no evidence that any of the flaws have been exploited…

Read More
Your security program knows about the firewall, but does it know about the elevator?

Attackers disrupted water systems in at least seven U.S. states by remotely accessing internet-facing programmable logic controllers, prompting federal investigators to examine possible links to Iran-backed hackers. Honeywell’s survey shows many critical infrastructure organizations still lack full visibility into building automation systems and IoT devices, which can slow recovery from outages and incidents. #FBI #EPA #HoneywellTechnologies

Read More
What to do first when you get 90 days to secure AI agent data

AI agents create exposure by widening access to enterprise data paths, especially when they can rapidly retrieve and combine sensitive information from systems like ticketing platforms, CRM tools, shared drives, and chat history. Kelly Herrell of Nol8 recommends enforcing deterministic policy in the data path so organizations can control what data enters, leaves, and is disclosed by agents. #Nol8 #AIDataPlane #Salesforce #Jira

Read More
CISA outlines improvement plan for CVE program

CISA has released a white paper describing its plan to move the CVE program into a “Quality Era,” focusing on better governance, broader participation, stronger infrastructure, and more reliable vulnerability records. The proposal comes as CVE volume continues to surge, with experts welcoming the emphasis on quality while questioning whether the document goes far enough to solve persistent data issues. #CISA #CVE #NIST #NationalVulnerabilityDatabase #Sonatype #OWASP #VulnCheck

Read More
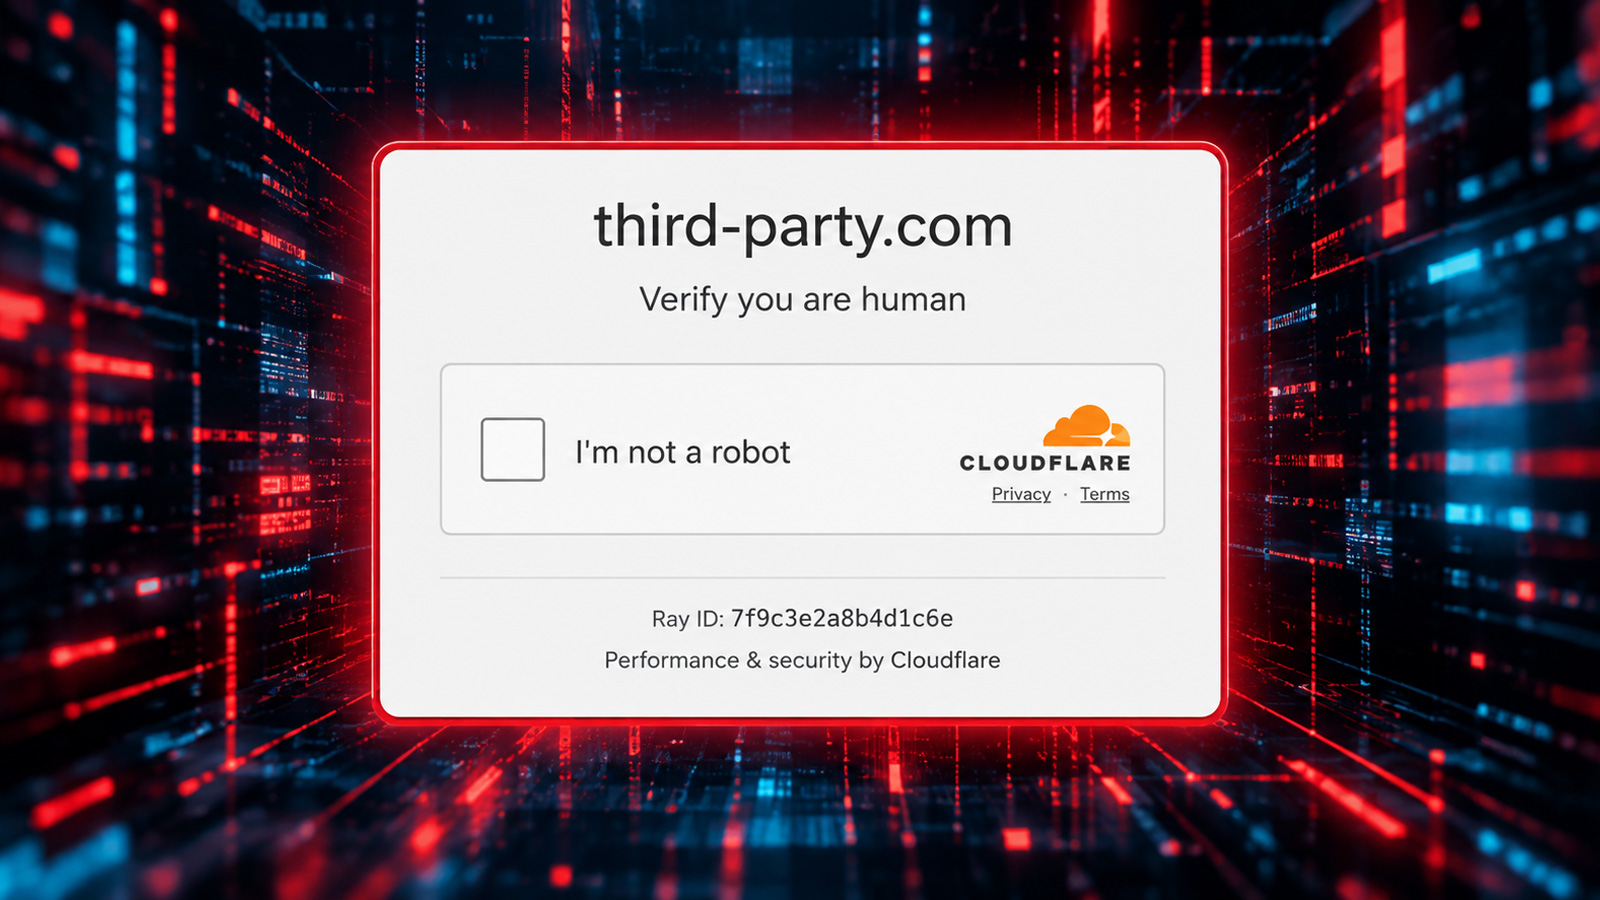
Placeholder domain used in dev docs now serves ClickFix attacks

The third-party.com domain, long used as a placeholder in developer documentation, is now serving a fake Cloudflare verification page that tricks Windows users into running malicious PowerShell commands. The ClickFix attack targets only Windows systems and may have been copied into code or docs across many repositories, creating risk if those references are ever opened or executed. #third-party.com #Cloudflare #ClickFix #PowerShell #Windows

Read More
No evidence of successful foreign meddling in 2024 election, spy agencies found

U.S. intelligence officials found no evidence that any foreign adversary successfully interfered in the 2024 presidential election, though Russia, Iran, and China each ran influence campaigns to varying degrees. The assessment also highlights growing concerns about AI-enabled election influence efforts and ongoing monitoring ahead of upcoming midterms. #Russia #Iran #China #ODNI…

Read More
UK regulator to investigate Pornhub parent company for alleged age verification failings

Ofcom has opened an investigation into Aylo, the parent company of Pornhub, over whether its age-verification controls comply with the UK Online Safety Act and effectively block minors from viewing adult content. The probe centers on Aylo’s use of Apple-based age assurance signals, with Ofcom warning that weak testing or due…

Read More
MikroTrick Chain Let Attackers Take Over MikroTik Routers Without a Password or SSH Key

CERT Polska says two MikroTik RouterOS SSH flaws, CVE-2026-67279 and CVE-2026-86060, can be chained to give attackers full administrative control of Internet-exposed routers without a password or completed authentication. Evidence of exploitation appeared before patches were released, with logs showing the suspicious SSH username -2 and post-exploitation activity tied to accounts…

Read More
Attackers Use Malicious Terraform Providers to Deliver Go Malware via HashiCorp Registry

Researchers uncovered Go-based malware distributed through two Go Modules and two Terraform providers, marking the first known abuse of HashiCorp’s centralized repository as a malware delivery channel. The activity overlaps with Graphalgo and other North Korea-linked campaigns that use fake job offers, npm, PyPI, Slack, and blockchain-based command channels to target…

Read More
IonQ Targets Quantum Error-Correction Bottleneck With Single-CPU DecoderIonQ Says Sin

IonQ says it has built a real-time quantum error-correction decoder that runs on a single standard CPU, aiming to reduce classical computing overhead in larger quantum systems. In simulations of up to 408 logical qubits, the decoder reportedly added as little as 0.02% processing time under standard noise conditions. #IonQ #QuantumErrorCorrection…

Read More
Check Point warns of hackers exploiting Security Gateway VPN RCE flaw

Check Point has confirmed active exploitation of CVE-2026-85102 and CVE-2026-93616, with attackers using VPNs and proxies to hide their origin while targeting Security Gateway and Management web service flaws. CISA has added both vulnerabilities to its KEV catalog, and Check Point has issued patching and mitigation guidance for affected customers. #CVE-2026-85102 #CVE-2026-93616 #CheckPoint #NCSC #CISA

Read More