
Brig. Gen. Matthew Lennox will take command of the Cyber National Mission Force on Friday, replacing Maj. Gen. Lorna Mahlock as part of a broader leadership turnover. The change comes after months of upheaval following last April’s abrupt firing of the Cyber Command/NSA head and the Senate’s recent confirmation of Lt….
Category: Cyber Security News

Two U.K. regulators, the Information Commissioner’s Office (ICO) and Ofcom, have demanded that major social platforms used by children — including Facebook, Instagram, Snapchat, TikTok, YouTube and Roblox — urgently implement robust age-assurance tools. They expect immediate action, with Ofcom requiring firms to report back by the end of April and…
Apple released security updates for legacy iPhone and iPad models to patch vulnerabilities exploited by the Coruna toolkit. Coruna is a 23-exploit, nation‑state‑grade kit linked to surveillance vendors and state-aligned actors that enables remote code execution on iOS devices, and Apple has backported fixes for older iOS and iPadOS releases. #Coruna…
The U.S. Department of Justice charged former DigitalMint employee Angelo Martino with conspiring to interfere with interstate commerce by extortion after allegedly collaborating secretly with the BlackCat (ALPHV) ransomware operation while acting as a ransomware negotiator. Court documents allege Martino and accomplices conducted ransomware attacks between April 2023 and April 2025 against at least five U.S. organizations — including a Tampa-based medical device manufacturer that paid $1.27 million — and DigitalMint says it terminated the employees and fully cooperated with law enforcement. #BlackCat #DigitalMint
Apple has released backported security updates for older iPhones and iPads to patch vulnerabilities exploited by the Coruna exploit kit in cyberespionage and crypto-theft campaigns. The fixes address kernel and WebKit issues across multiple CVEs and follow CISA actions that added some Coruna-targeted flaws to its Known Exploited Vulnerabilities list. #Coruna #UNC6691
Researchers discovered BeatBanker, a new Android trojan campaign in Brazil that infects phones via fake apps mimicking Starlink and the INSS Reembolso portal to steal banking credentials and manipulate cryptocurrency transactions. The malware also secretly mines Monero while using battery and activity monitoring plus a nearly inaudible audio loop to maintain…
Security teams must rigorously vet not only technical intelligence like IOCs and TTPs but also negative information about people or organizations to avoid false positives, wasted resources, downtime, and reputational damage. Simple practices—asking questions, requesting evidence, approaching the target directly, considering the source, and reviewing history—help reveal the truth and protect…

A SQL injection vulnerability (CVE-2026-2413) in the Ally WordPress plugin allowed unauthenticated attackers to perform time-based blind SQL injection and extract sensitive database information from over 200,000 sites. A patch included in Ally 4.1.0 adds wpdb prepare() sanitization to address the flaw, but as of March 11 roughly 60% of installations…
Meta announced a coordinated operation with the FBI, the DOJ Scam Center Strike Force, and Thai police that disrupted Southeast Asian scam centers targeting users in the US, UK, and the APAC region, resulting in 21 arrests and the shutdown of more than 150,000 accounts. The company also removed over 159…
Cyber operations have become a continuous instrument of statecraft, with persistent nation-state attacks, covert intrusion campaigns, and strategic influence operations increasingly mirroring real-world geopolitical conflicts. Critical targets now include governments, telecommunications, cloud platforms, and identity systems, while criminal ecosystems and AI-enabled automation are scaling espionage, impersonation, and financially motivated intrusions. #ShinyHunters…
Security researchers at Ledger’s Donjon team uncovered a boot‑chain vulnerability in certain MediaTek Android chipsets using Trustonic’s Trusted Execution Environment that could expose encryption keys and wallet seed phrases on roughly 25% of Android phones. They demonstrated an attack that, with brief physical USB access and no malware, recovered PINs and…
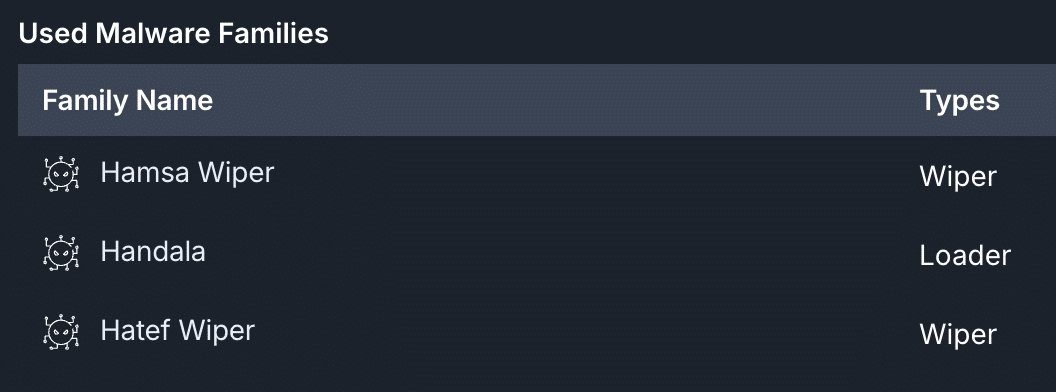
On March 11, Stryker suffered a global destructive cyberattack that defaced Microsoft login screens with the Handala logo and remotely wiped managed devices instead of deploying ransomware. The attack leveraged admin access to Microsoft Intune, causing outages across 79 countries, alleged exfiltration of 50 TB and claims of over 200,000 wiped…

Nearly 238,000 individuals were impacted by a February 2025 data breach at U.S.-based emergency medical services provider Bell Ambulance, which exposed names, Social Security numbers, birth dates, driver’s licenses, financial, medical, and health insurance information. The Medusa ransomware group claimed responsibility, leaked over 219 GB of allegedly stolen data, and Bell…
Check Point Research found China-linked hackers, including the Camaro Dragon group, targeting Qatar with conflict-themed lures that deliver backdoors like PlugX and loaders that lead to Cobalt Strike deployment. The campaign abuses DLL hijacking in Baidu NetDisk and hides a Rust-written loader inside NVDA components to hit Qatar’s military and energy…

ShinyHunters claims to have breached roughly 400 organizations by exploiting publicly accessible Salesforce Experience Cloud portals and is threatening to leak stolen records unless extorted. The group reportedly used a modified Aura Inspector to find guest-user configuration weaknesses and pulled names and phone numbers that are being used for vishing. #ShinyHunters…