
CISA added a critical n8n vulnerability, CVE-2025-68613, to its Known Exploited Vulnerabilities catalog after evidence of active exploitation. The expression injection flaw enables remote code execution, was patched by n8n in December 2025, and remains unpatched on thousands of exposed instances. #n8n #CVE-2025-68613…
Category: Cyber Security News

Following the February 2026 Operation Epic Fury strikes, Proofpoint observed a surge in state-aligned cyber operations exploiting the conflict for targeted intelligence collection. Iran-aligned TA453 (Charming Kitten/APT42) continued credential-phishing campaigns—using multi-stage lures and OneDrive-themed credential pages to target stakeholders and gather geopolitical intelligence. #TA453 #OperationEpicFury…

Rapid7 Labs reports a sharp uptick in retaliatory cyber activity against regional and Western infrastructure, blending state-directed espionage with a noisy layer of hacktivist disruption. State-linked groups are weaponizing high-impact CVEs for persistence while collectives stage DDoS and defacements, and many breach claims on Telegram and dark forums are exaggerated or…
AI child safety in India is being addressed through a mix of existing laws, new data protections, governance guidelines, enforcement mechanisms, and public awareness programs to mitigate risks from AI-powered toys, apps, and online platforms. Officials emphasize balancing innovation with strong safeguards, but experts warn that effective implementation, platform accountability, and…
UIDAI has launched a structured bug bounty program to strengthen the cybersecurity of the Aadhaar ecosystem by engaging independent security researchers. The initiative selects 20 experts to assess key platforms like the official website, myAadhaar portal, and the Secure QR Code app, with coordinated disclosure, severity-based rewards, and management support from…
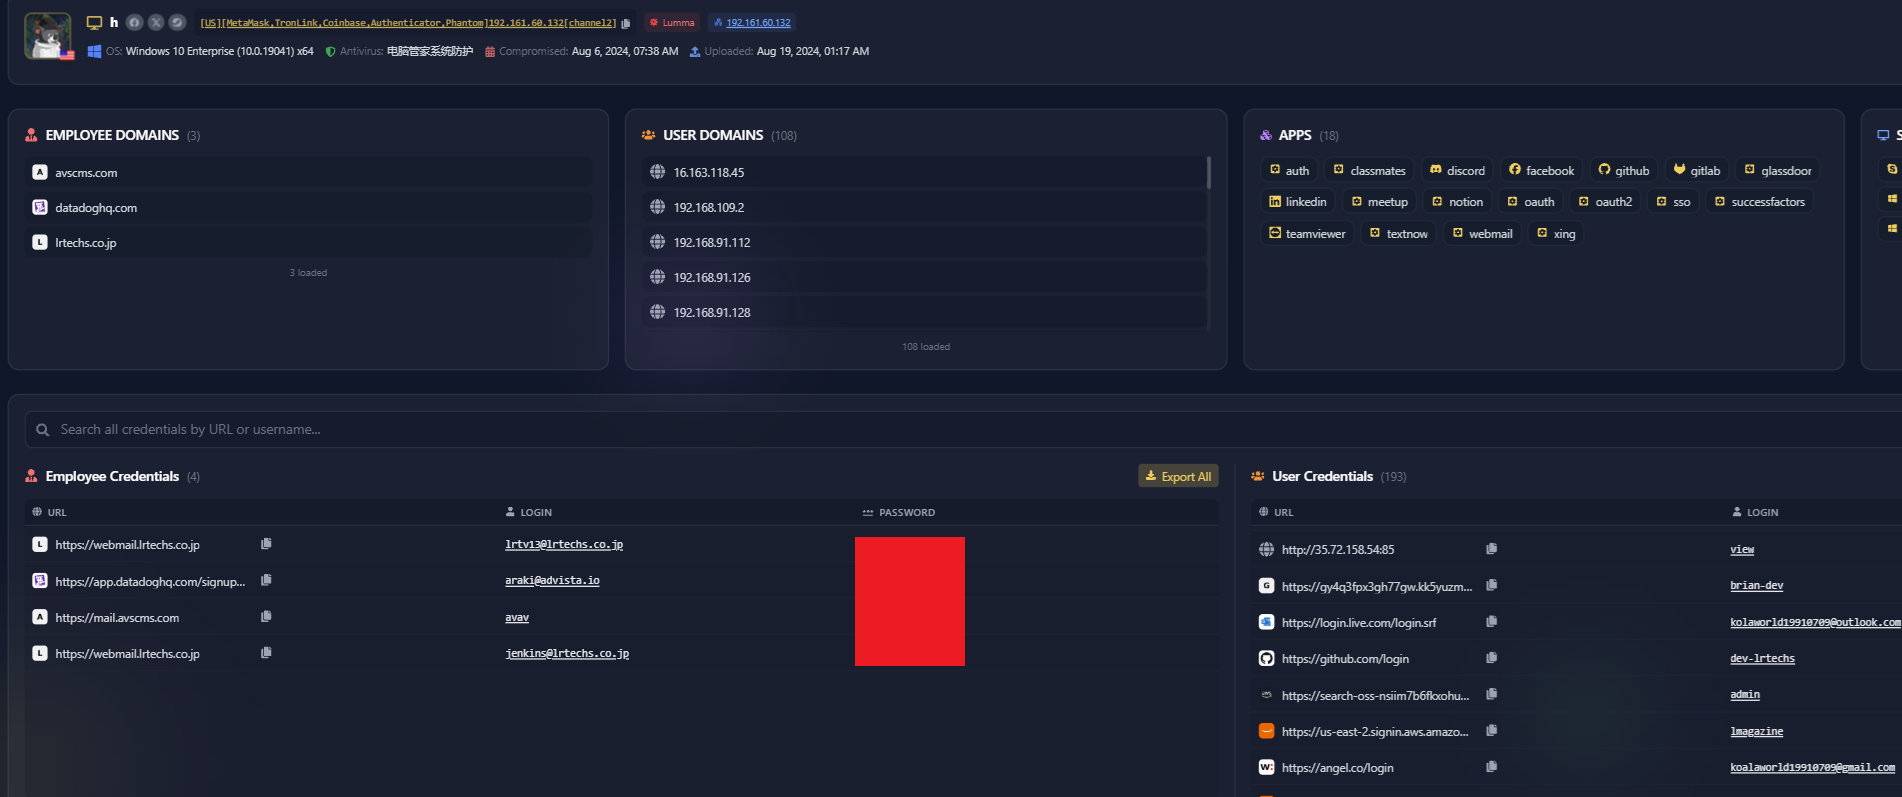
An infostealer infection on a compromised workstation produced definitive forensic evidence linking a North Korean state‑aligned operator to the Funnull CDN and the Polyfill.io supply‑chain attack while also revealing deep operational ties to transnational organized crime. The recovered telemetry and credentials (including LummaC2 exfiltrated data) show the actor administered weaponized CDN infrastructure, infiltrated Gate.us KYC workflows, exfiltrated NIMS air‑gapped blueprints, and operated an automated Telegram crypto‑laundering gateway. #LummaC2 #Polyfillio

Daily Recap, Microsoft released March Patch Tuesday addressing 79–84 vulnerabilities including two zero-days (CVE-2026-26127, CVE-2026-21262) across SQL Server, .NET, Office, Azure and Windows with hotpatch options. The coverage also highlights active attacks and supply-chain events such as the Medusa-linked Bell Ambulance breach, UNC6426’s QUIETVAULT deployment and other campaigns, KadNap botnet activity on ASUS devices, BeatBanker on Android, and the Zombie ZIP technique. #Medusa #BellAmbulance #UNC6426 #QUIETVAULT #KadNap #BeatBanker #ZombieZIP #IranInstagram
New waves of the PhantomRaven supply-chain campaign are targeting the npm registry with dozens of malicious packages designed to exfiltrate sensitive data from JavaScript developers. Researchers found the attacks use slopsquatting and Remote Dynamic Dependencies to bypass scanners and steal configuration files, CI/CD tokens, and environment variables. #PhantomRaven #npm
Stryker, a leading medical technology company, suffered a global wiper attack claimed by the Iranian-linked hacktivist group Handala, which says it stole 50 terabytes of data and wiped over 200,000 systems and devices. Employees across multiple countries reported remote wiping of managed and personal devices, defacement of Stryker’s Entra login page, and widespread outages as the company works with Microsoft to restore systems. #Handala #Stryker
CISA ordered federal agencies to patch an actively exploited n8n remote code execution vulnerability (CVE-2025-68613) and added it to its Known Exploited Vulnerabilities catalog with a BOD 22-01 compliance deadline. n8n, widely used for workflow automation and AI data ingestion and often storing API keys and other sensitive credentials, was patched in n8n v1.122.0 but Shadowserver reports over 40,000 exposed unpatched instances online. #n8n #CVE-2025-68613
An SQL injection vulnerability in the Ally WordPress plugin for Elementor (tracked as CVE-2026-2313) allows unauthenticated attackers to inject SQL via a URL parameter and potentially exfiltrate sensitive data. Elementor released a fix in Ally 4.1.0 after disclosure by Drew Webber of Acquia, but more than 250,000 sites remain vulnerable due to slow updates. #Ally #CVE-2026-2313
WhatsApp is rolling out parent-managed accounts for pre-teens that let guardians control who can contact them and which groups they can join while restricting features like Meta AI, Channels, Status, and location sharing. Child accounts remain end-to-end encrypted and include setup and control mechanisms such as device-to-device verification, a parent-set 6-digit PIN, activity alerts, and new anti-scam protections. #WhatsApp #Meta

Meta said it disabled over 150,000 accounts tied to scam centers in Southeast Asia and coordinated with international authorities, resulting in 21 arrests by the Royal Thai Police. It also rolled out new AI-driven protections across Facebook, WhatsApp, and Messenger while the U.K. launched a £30 million Online Crime Centre to…

AI-powered agentic browsers can be manipulated via their own reasoning and verbose narration—”Agentic Blabbering”—allowing attackers to lower model guardrails and lure agents into phishing and scam traps. Researchers showed that by intercepting agent traffic and using a GAN to iteratively craft pages, they made Perplexity’s Comet fall for a phishing scam…

Stryker confirmed a cyberattack has disrupted its global Microsoft network and says business continuity measures are in place while teams investigate. Employees reported wiped corporate devices and login pages displaying the Handala logo, and the group has claimed responsibility alleging massive system wipes and data theft. #Stryker #Handala…