The U.S. Senate confirmed Army Lt. Gen. Joshua Rudd in a 71–29 vote to lead the National Security Agency and U.S. Cyber Command in the dual-hat role that had been vacant since General Timothy Haugh’s firing in April 2025. His appointment, praised for operational leadership but criticized for limited cyber and…
Category: Cyber Security News

Researchers disclosed two now-patched critical vulnerabilities in the n8n workflow automation platform that could allow arbitrary command execution, including a sandbox escape in the expression compiler and an unauthenticated expression evaluation in Form nodes. n8n released fixes in versions 2.10.1, 2.9.3, and 1.123.22 and recommends restricting workflow permissions, disabling affected nodes,…

Albania’s parliament was hit by a sophisticated cyberattack that disrupted internal email services and temporarily prevented staff and lawmakers from accessing computers. A hacker group calling itself Homeland Justice claimed responsibility and posted alleged leaked documents while authorities and cybersecurity agencies continue to investigate the incident. #HomelandJustice #AlbanianParliament…

Aimee Cardwell rose from a product manager role at Netscape to senior technology and security leadership positions, including VP of engineering at American Express, CIO roles at Optum/UnitedHealth Group, CISO at UnitedHealth Group, and now CISO in Residence at Transcend. She stresses the need for CISOs to combine technical depth with…

Cloud security firm Wiz officially joined Google Cloud in a landmark $32 billion all-cash acquisition that closed on March 11, 2026. Google will integrate Wiz’s cloud and AI security platform—while preserving the Wiz brand and multi-cloud support—to create an AI-powered security offering leveraging Gemini and Google Threat Intelligence, and the deal…
Stryker was hit by a highly disruptive cyberattack claimed by Iran-linked group Handala, which says it wiped more than 200,000 servers and devices and stole roughly 50 TB of data, forcing office shutdowns in 79 countries. Cybersecurity firms note Handala—active since the US–Israel–Iran conflict and suspected to be a front for…
Meta is rolling out new anti-scam protections across WhatsApp, Facebook, and Messenger to detect device-linking fraud, suspicious friend requests, fake job offers, and impersonation using AI systems and user-facing warnings. The changes come amid warnings about state-backed phishing targeting Signal and WhatsApp accounts and follow major takedowns and a global law-enforcement operation to disrupt scam networks; #WhatsApp #Meta
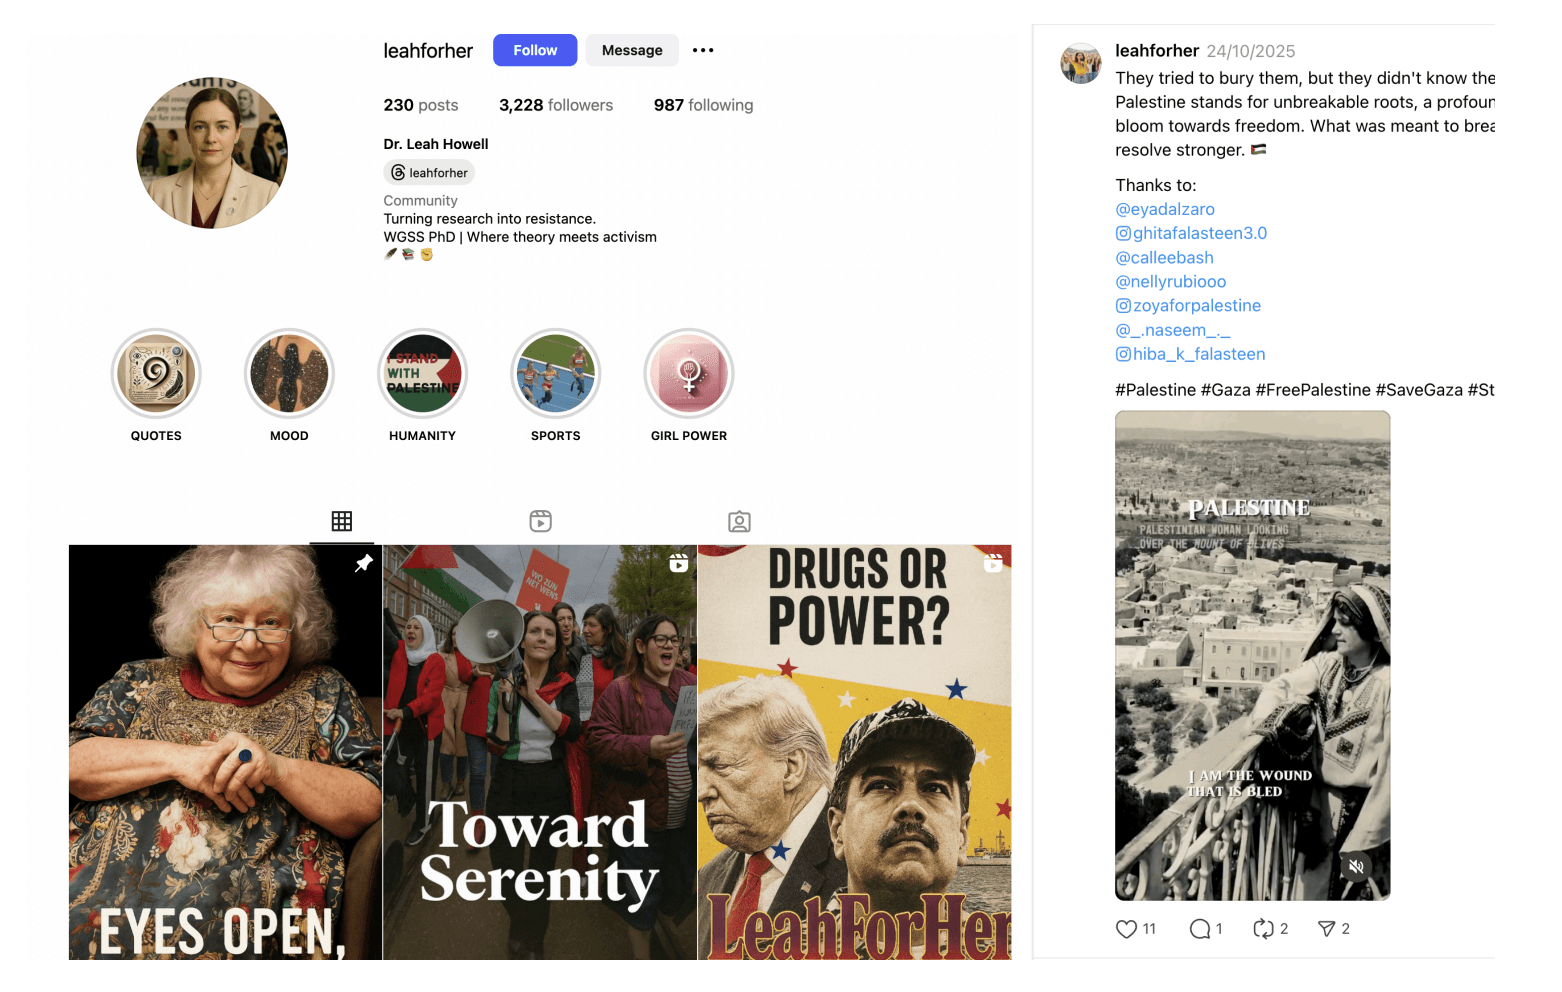
Meta said it disrupted an Iran-linked influence operation that used sophisticated fake personas on Instagram to cultivate relationships with U.S. users before introducing political messaging. The network relied on AI-generated profile photos, detailed backstories, and a second layer of amplifying accounts to pose as journalists and grassroots media brands targeting English-speaking…

Bell Ambulance in Milwaukee confirmed a 2025 cyberattack that exposed sensitive information for 237,830 people, including Social Security numbers, driver’s license numbers, financial accounts, and medical and insurance data. The Medusa ransomware gang claimed the attack, demanding $400,000 for 219 GB of stolen data while the FBI has tied Medusa to…

Fortinet, Ivanti, and Intel released security updates addressing dozens of vulnerabilities, including high-severity flaws that could allow remote code execution, privilege escalation, or protection bypasses. The fixes cover multiple products such as FortiWeb, FortiSwitchAXFixed, FortiManager, FortiClientLinux, Ivanti DSM, and Intel UEFI firmware, and none of the reported issues appear to have…
OpenAI is acquiring AI security company Promptfoo and plans to integrate its testing and red‑teaming capabilities into the Frontier platform used by enterprises to build and operate AI coworkers. Promptfoo’s platform automates adversarial testing of LLMs — including prompt injections, jailbreaks, and sensitive data‑leak simulations — and OpenAI will continue to…
Scanner raised $22 million in a Series A round led by Sequoia Capital to scale its cloud-native security data lake and AI-driven detection platform. Its Model Context Protocol (MCP) server links AI agents to indexed data lakes for fast threat hunting, continuous detection, and quicker responses than traditional SIEMs. #Scanner #SequoiaCapital…

Daily Recap, CISA added multiple high-severity flaws to the Known Exploited Vulnerabilities catalog, warning that the Ivanti EPM CVE-2026-1603 is actively exploited with over 700 internet-facing instances and federal patching deadlines. The report also notes a critical Nginx UI flaw CVE-2026-27944 fixed in 2.3.3, and coverage of APT campaigns and loader trends including PlugX against Qatar, UAT9244 implants such as PeerTime, TernDoor and BruteEntry, Seedworm and Dust Specter campaigns, UNC4899 breach, and malware like GhostLoader, ClipXDaemon, A0Backdoor, and LummaStealer. #IvantiEPM #CVE-2026-1603 #NginxUI #CVE-2026-27944 #PlugX #UAT9244 #PeerTime #TernDoor #BruteEntry #Seedworm #DustSpecter #Dindoor #UNC4899 #GhostLoader #ClipXDaemon #A0Backdoor #LummaStealer #SalesforceAura #EricssonBreach #React2Shell

A threat actor known as UNC6426 used credentials stolen via an August 2025 supply-chain compromise of the nx npm package to fully breach a victim’s cloud environment within 72 hours. They weaponized a postinstall script that deployed the QUIETVAULT credential stealer, abused GitHub-to-AWS OIDC trust to create an Administrator role via…

Microsoft released patches for 84 new vulnerabilities in its May 2026 update, including two publicly disclosed zero-days (CVE-2026-26127 in .NET and CVE-2026-21262 in SQL Server), with eight rated Critical and 76 rated Important addressing many privilege escalation and remote code execution issues. Notable fixes include a mitigated CVE-2026-21536 (9.8 RCE) in…