
Unit 42 uncovered CL-STA-1087, a suspected China-linked state-sponsored espionage cluster that has stealthily infiltrated Southeast Asian military networks since at least 2020. The group practices strategic operational patience and uses custom tools like AppleChris, MemFun, and Getpass to target C4I systems and harvest highly specific military intelligence. #CL-STA-1087 #AppleChris…
Category: Cyber Security News

Daily Recap, unauthenticated SQL injection in the Ally Elementor plugin exposed over 200,000–250,000 WordPress sites and remains widely unpatched. The roundup also highlights actively exploited n8n RCE flaws prompting CISA actions and federal patch orders, along with the Stryker wiper incident, the Bell Ambulance breach, ShinyHunters’ Salesforce data exfiltration, and related regional, mobile, supply-chain, and policy developments.
#AllyElementor #AllySQLi #n8n #StrykerWiper #BellAmbulance #ShinyHunters #QatarBackdoor #AlbaniaEmail #BeatBanker #AppleCoruna #MediaTekTEE #DPRKSupplyChain #PhantomRavenNPM #WizAcquisition #RuddConfirmed #MetaCrackdown #WhatsAppKids #AadhaarBounty #IndiaAISafety #CometPhish

England Hockey is investigating a possible data breach after the AiLock gang listed the organization as a victim, claiming to have stolen 129GB of data and threatening to publish the files unless a ransom is paid. The body says it has launched a priority inquiry with internal teams, external specialists and law enforcement while advising members to watch for suspicious activity and phishing attempts; #EnglandHockey #AiLock

Loblaw Companies Limited disclosed that hackers breached a contained portion of its IT network and accessed basic customer personal information, including names, phone numbers, and email addresses. The company says there is no evidence so far that financial, health, or account password data were compromised; it has logged out all customers as a precaution and recommends password changes, and PC Financial appears unaffected so far. #Loblaw #PCFinancial

Law enforcement in the U.S. and Europe disrupted the SocksEscort residential proxy network, seizing domains and servers, freezing $3.5 million in cryptocurrency, and linking the service to thousands of infected routers used to mask cybercriminal activity. The FBI warned that AVRecon malware targets routers and IoT devices across many models from…
IBM X-Force analyzed a new PowerShell backdoor called Slopoly, likely generated with a large language model, which was used in an Interlock ransomware campaign to maintain persistence and exfiltrate data. The attack began with a ClickFix social engineering flow, was attributed to the financially motivated group Hive0163, and highlights how AI-assisted builders can accelerate custom malware development and help evade detection. #Slopoly #Hive0163

Researchers disclosed Slopoly, a suspected AI-generated PowerShell backdoor used by financially motivated threat actor Hive0163 to maintain persistent access during post-exploitation. The script, likely produced via a builder and showing signs of LLM-assisted development such as extensive comments and accurate variable names, beacons system information and polls a C2 for commands,…

Researchers disclosed VENON, a Rust-written banking trojan targeting Brazilian Windows users that borrows overlay, active window monitoring, and LNK hijacking techniques from Latin American families like Grandoreiro, Mekotio, and Coyote. The campaign uses DLL side-loading, nine evasion techniques, Google Cloud Storage-hosted configs, Itaú-specific shortcut hijacking, and has links to WhatsApp-distributed SORVEPOTEL…
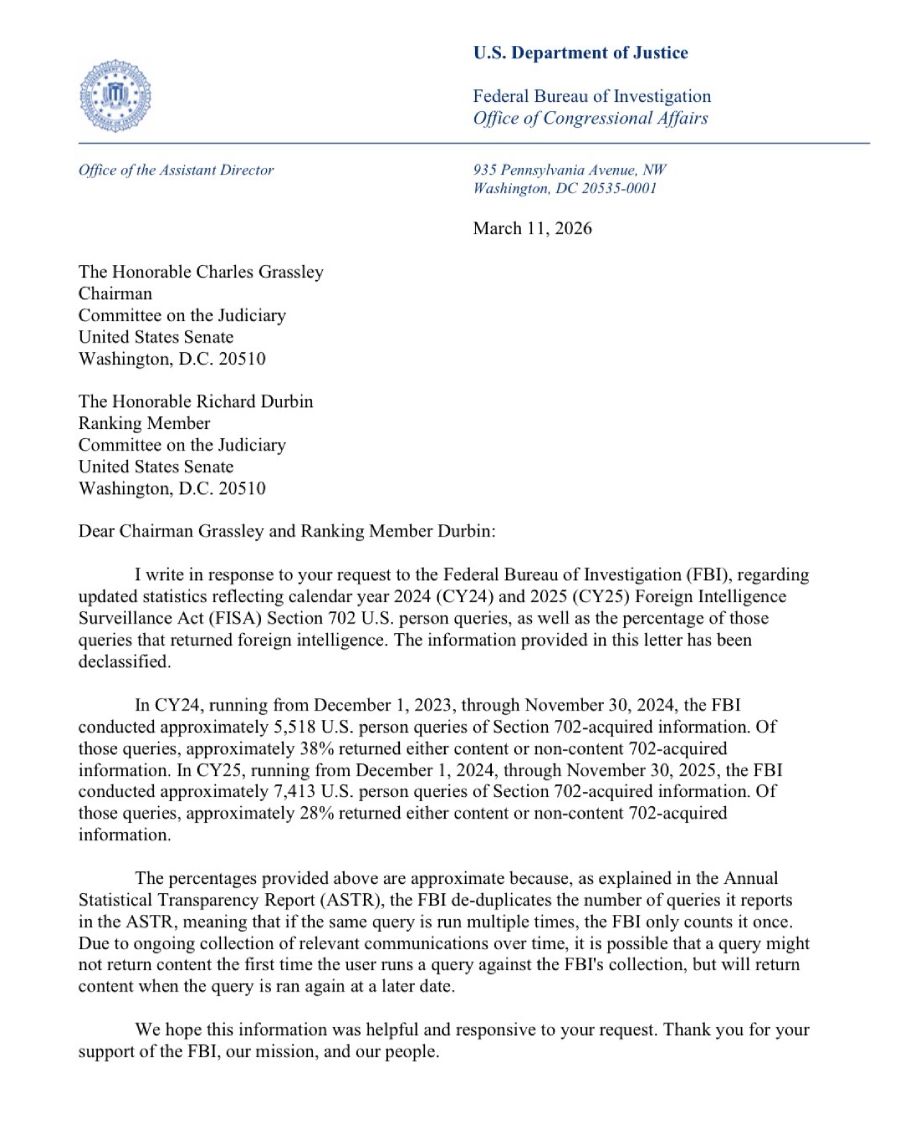
A senior FBI official’s letter disclosed that FBI searches of Section 702 data on Americans increased by roughly 35% in 2025, rising to 7,413 from 5,518 the previous year. The spike, alongside falling hit rates and White House support for an 18‑month extension, has intensified debate over warrantless “U.S. person” queries…
Stolen airline miles and hotel points are treated as tradable inventory in underground markets, with access commonly obtained through credential compromise and malware. Flare’s analysis of Telegram channels reveals organized sellers who redeem rewards into bookings and resell them, contributing to an estimated $1–$3 billion in annual losses. #Infostealers #United
Telus Digital confirmed a security incident after threat actors claiming to be ShinyHunters said they had stolen nearly 1 petabyte of data in a multi-month breach. Telus is investigating, has engaged cyber forensics and law enforcement, and says business operations remain fully operational while it notifies impacted customers as appropriate. #ShinyHunters #TelusDigital
U.S. and European law enforcement, assisted by private partners including Lumen’s Black Lotus Labs, disrupted the SocksEscort proxy network that routed traffic through edge devices compromised by the AVRecon Linux malware, which had averaged about 20,000 infected devices weekly and advertised “clean” ISP IPs. Authorities seized domains and servers, froze $3.5 million in cryptocurrency, disconnected infected devices, and warned that AVRecon and related threats like KadNap continue to target SOHO and ASUS routers. #AVRecon #SocksEscort
Veeam Software released patches for multiple vulnerabilities in its Backup & Replication product, including four critical remote code execution flaws (CVE-2026-21666, CVE-2026-21667, CVE-2026-21669, and CVE-2026-21708) that can be abused by low-privileged users and a Backup Viewer to execute code on backup servers. The fixes are included in Veeam Backup & Replication 12.3.2.4465 and 13.0.1.2067, and administrators are urged to upgrade immediately because ransomware groups such as FIN7 and Cuba have historically exploited VBR vulnerabilities for lateral movement and to prevent restorations. #VeeamBackupAndReplication #FIN7

Phishing has evolved into a fast, stealthy enterprise threat that abuses trusted infrastructure, legitimate-looking authentication flows, and encrypted HTTPS channels to hide credential harvesting and account takeover attempts. CISOs must scale detection with interactive sandboxing, automation that mimics analyst behavior, and SSL decryption to expose attacks early and reduce business impact….

Medical device maker Stryker disclosed a global cyber incident that wiped employee devices and locked about 5,500 staff out of company systems across Ireland, the US, Australia and India, disrupting its Microsoft environment and prompting external cybersecurity teams to contain the threat. The company says no ransomware or malware was confirmed,…