
The Justice Department alleges incident responder Angelo Martino carried out multiple ransomware attacks and secretly aided the ALPHV/BlackCat group while working as a negotiator. Martino surrendered, was released on bond with a ban on cyber industry work, and prosecutors say he passed confidential negotiation details that helped secure multimillion-dollar ransoms, prompting…
Category: Cyber Security News

SecurityWeek’s roundup highlights a surge in rapid, vulnerability-driven cloud attacks and a string of high-impact disclosures and breaches affecting vendors and services. The update also covers prosecutions, global takedowns, and emerging threats such as AI-generated Slopoly and activity by ShinyHunters. #Slopoly #ShinyHunters…

Starbucks disclosed a data breach impacting the personal information of nearly 900 employees after attackers accessed Partner Central accounts using credentials obtained via a phishing campaign. The company says its systems and networks were not directly compromised, law enforcement has been notified, and affected employees are being offered free identity protection…
Operation Synergia III, an Interpol-led campaign from July 2025 to January 2026, sinkholed tens of thousands of IP addresses, seized servers and electronic devices, and resulted in 94 arrests with 110 suspects still under investigation across 72 countries. The operation exposed widespread phishing and fraud infrastructures — including over 33,000 malicious sites in Macau impersonating casinos, banks and government services — and complements prior Interpol actions like Operation Synergia II and Operation Red Card 2.0, highlighting the impact of international cooperation. #OperationSynergiaIII #INTERPOL
Cybersecurity startup Bold Security emerged from stealth with $40 million in funding led by Bessemer Venture Partners, Picture Capital, and Red Dot Capital Partners. Co-founded by CEO Nati Hazut, the New York-based company runs custom AI agents directly on enterprise endpoints to provide real-time behavior monitoring, local data classification, policy enforcement,…
Pro‑Iranian hackers have broadened attacks from the Middle East into the United States, hitting organizations including medical device maker Stryker and probing cameras, data centers and industrial systems to support Iranian military aims. These groups, including Handala and aligned Russian operators, favor disruption and data destruction that threaten defense contractors, power…
Veeam released a security patch (version 12.3.2.4465, KB ID: 4830) on March 12, 2026 to address seven vulnerabilities in Backup & Replication, including critical remote code execution flaws. Customers are urged to install the update immediately because CVE-2026-21666 and CVE-2026-21667 both received CVSS 9.9 and attackers can reverse-engineer patches to target…
This week’s roundup covers destructive cyberattacks, state-backed espionage, and proactive defense measures impacting organizations, governments, and individuals worldwide. Notable incidents include the Handala wipe of over 200,000 Stryker devices and the ClipXDaemon Linux crypto‑wallet hijacker, alongside India’s Aadhaar bug bounty and Microsoft’s March 2026 patch releases—underscoring the urgent need for timely…
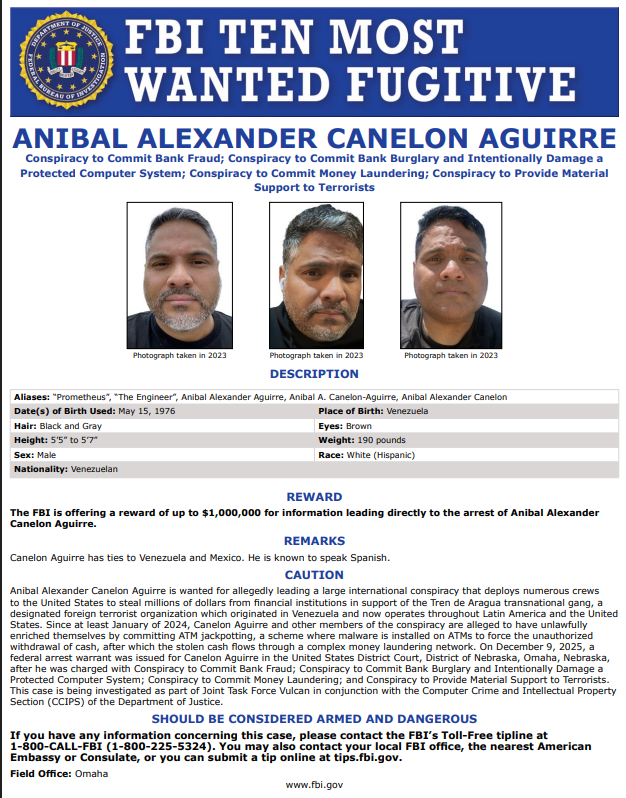
The FBI added Anibal Alexander Canelon Aguirre to its Ten Most Wanted list after alleging he led a global ATM jackpotting conspiracy that generated millions for the Tren de Aragua transnational gang. Authorities say the scheme used ATM malware to force machines to dispense cash, involved coordinated travel and money-laundering networks,…
Starbucks disclosed a data breach that compromised 889 Partner Central employee accounts, exposing names, Social Security numbers, dates of birth, and bank account and routing numbers. The company discovered the intrusion on February 6 after attackers obtained login credentials through websites impersonating Partner Central, notified law enforcement, and is offering two years of Experian identity protection while strengthening access controls. #Starbucks #PartnerCentral #Termite #BlueYonder #Experian

Google released Chrome updates to patch two high-severity zero-day vulnerabilities actively exploited in the wild: CVE-2026-3909 in the Skia graphics library and CVE-2026-3910 in the V8 JavaScript/WebAssembly engine. Users should update to Chrome 146.0.7680.75/76 (Windows/macOS) or 146.0.7680.75 (Linux) and apply vendor patches for other Chromium-based browsers. #Chrome #Skia…

Google released an emergency Chrome 146 update to address two zero-day vulnerabilities that are being actively exploited in the wild. The flaws—an out-of-bounds write in the Skia graphics library (CVE-2026-3909) and an implementation weakness in the V8 JavaScript engine (CVE-2026-3910)—were patched across Windows, macOS, Linux, and Android. #CVE-2026-3909 #CVE-2026-3910…
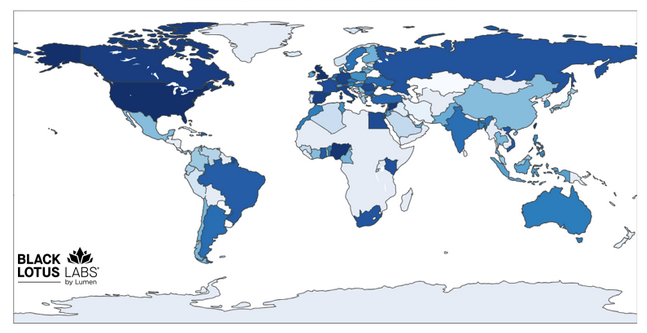
Law enforcement in the United States and Europe disrupted SocksEscort, a malicious proxy service built from compromised routers and IoT devices that enabled DDoS, ransomware, and the distribution of child abuse material. Authorities seized domains and servers, froze $3.5 million in cryptocurrency, disconnected infected modems, and the FBI warned that AVrecon…
Onyx Security announced a $40 million funding round led by Conviction and Cyberstarts to launch a secure AI control plane that discovers, monitors, and governs autonomous agents across cloud, endpoints, code, and SaaS. Their Onyx Guardian Agent and supervisory AI use proprietary models to understand agent reasoning in real time, providing…
Researchers identified a suspected case of AI-generated malware called Slopoly used by the financially motivated group Hive0163 during a 2026 ransomware intrusion. Slopoly acted as a PowerShell-based C2 persistence client deployed late in the attack chain alongside NodeSnake, InterlockRAT and Interlock ransomware, indicating threat actors are experimenting with LLM-assisted malware generation….