Hewlett Packard Enterprise released patches for a critical unauthenticated remote vulnerability in Aruba Networking AOS-CX (CVE-2026-23813) that can be exploited to reset administrator passwords and bypass authentication. The flaw affects multiple CX series switches and is fixed in AOS-CX 10.17.1001, 10.16.1030, 10.13.1161, and 10.10.1180; HPE also addressed three related high-severity CVEs…
Category: Cyber Security News
Women across the cybersecurity community urge moving beyond discussion to concrete actions that expand recruitment, mentorship, sponsorship, scholarships, and inclusion in real projects and leadership. Their practical recommendations include joining inclusive networks, hiring career‑pivoters, supporting scholarships, and tackling gender bias and burnout to build a stronger, more diverse cyber workforce. #WiCyS…

Daily Recap, global law enforcement actions dominated the week, with Interpol’s Synergia III sinkholing 45,000 IPs, seizing servers and 94 arrests across 72 countries, the FBI adding an alleged leader of an ATM jackpotting ring to its Ten Most Wanted list, and authorities disrupting the SocksEscort proxy network. In malware and breaches, Hive0163 was tied to the AI-assisted PowerShell backdoor Slopoly used with NodeSnake and Interlock ransomware, VENON targeted 33 Brazilian banks, and major incidents affected Starbucks, Loblaw, Telus Digital, and England Hockey, while patches from Google, Apple and Veeam mitigated critical flaws. #SynergiaIII #SocksEscort #ATMJackpotting #Hive0163 #Slopoly #VENON #Starbucks #Loblaw #Telus #EnglandHockey #Coruna #AiLock
The FBI’s Seattle Division is asking gamers who installed one of eight Steam titles containing malware between May 2024 and January 2026 to provide information as part of an ongoing investigation. Victims are being asked to report cryptocurrency transactions, account compromises, and any promotional communications via a short form or [email protected] for tracing and potential restitution. #BlockBlasters #Vidar
Microsoft is investigating a Windows 11 issue affecting some Samsung laptops after the February 2026 security updates that can make the C: drive inaccessible and prevent applications like Outlook, Office apps, and web browsers from launching. The company is working with Samsung and suspects the Samsung Share app may be involved, and users are advised not to apply a risky workaround that changes C: ownership because it weakens built-in security protections. #SamsungShare #Windows11

Meta will discontinue support for end-to-end encryption (E2EE) for Instagram chats after May 8, 2026, and affected users will be shown how to download any media or messages they want to keep. The move follows earlier testing and limited rollouts of E2EE, ongoing debates with law enforcement and child-safety advocates, and…

Palo Alto Networks Unit 42 says a suspected China-based, state-sponsored espionage campaign tracked as CL-STA-1087 has targeted Southeast Asian military organizations since at least 2020, focusing on precise intelligence collection rather than bulk theft. The operators deployed custom backdoors AppleChris and MemFun, a credential harvester Getpass, and Pastebin/Dropbox-based C2 resolution while…

The European Council released a proposal to streamline the EU AI Act, adding a ban on AI nudification tools and tougher standards for processing certain categories of personal data. The proposal, prompted in part by the Grok nudification incident on X, also reinstates registry and strict necessity rules for high-risk AI…

New York will require community water and wastewater systems serving more than 3,300 people to meet new cybersecurity regulations by year’s end, including mandatory operator training, incident response and recovery plans, reporting requirements, and a designated cyber lead for larger utilities. The state is providing a $2.5 million grant program plus…
Threat actor Storm-2561 is distributing spoofed enterprise VPN clients impersonating vendors like Ivanti, Cisco, and Fortinet by poisoning search results to redirect users to malicious sites. The fake MSI installs Pulse.exe, a loader (dwmapi.dll) and a Hyrax infostealer (inspector.dll) that captures credentials and VPN configuration data, uses a revoked Taiyuan Lihua certificate, and persists via RunOnce while redirecting victims to the real vendor site after stealing data. #Storm-2561 #Hyrax
Broadcom’s 2023 acquisition of VMware has accelerated large-scale migrations to alternatives like Microsoft Hyper‑V, Nutanix AHV, Proxmox VE and KVM as customers respond to price, licensing and support changes. Successful migration is technically risky and requires verified, platform-agnostic backups, recovery drills, immutability and unified protection—capabilities highlighted by Acronis Cyber Protect. #VMware #AcronisCyberProtect
Microsoft is investigating multiple bugs in the classic Outlook desktop client that cause group creation failures when Exchange Web Services (EWS) is enabled, Gmail/Yahoo synchronization errors (0x800CCC0F, 0x80070057), and intermittent disappearance of the mouse pointer. Workarounds include using the new Outlook client or Outlook Web Access for groups, deleting affected Identity registry entries for sync issues, submitting diagnostic logs via a Microsoft 365 admin support case, or temporarily restarting or switching apps while Microsoft prepares a REST-based group fix and further updates. #EWS #Outlook
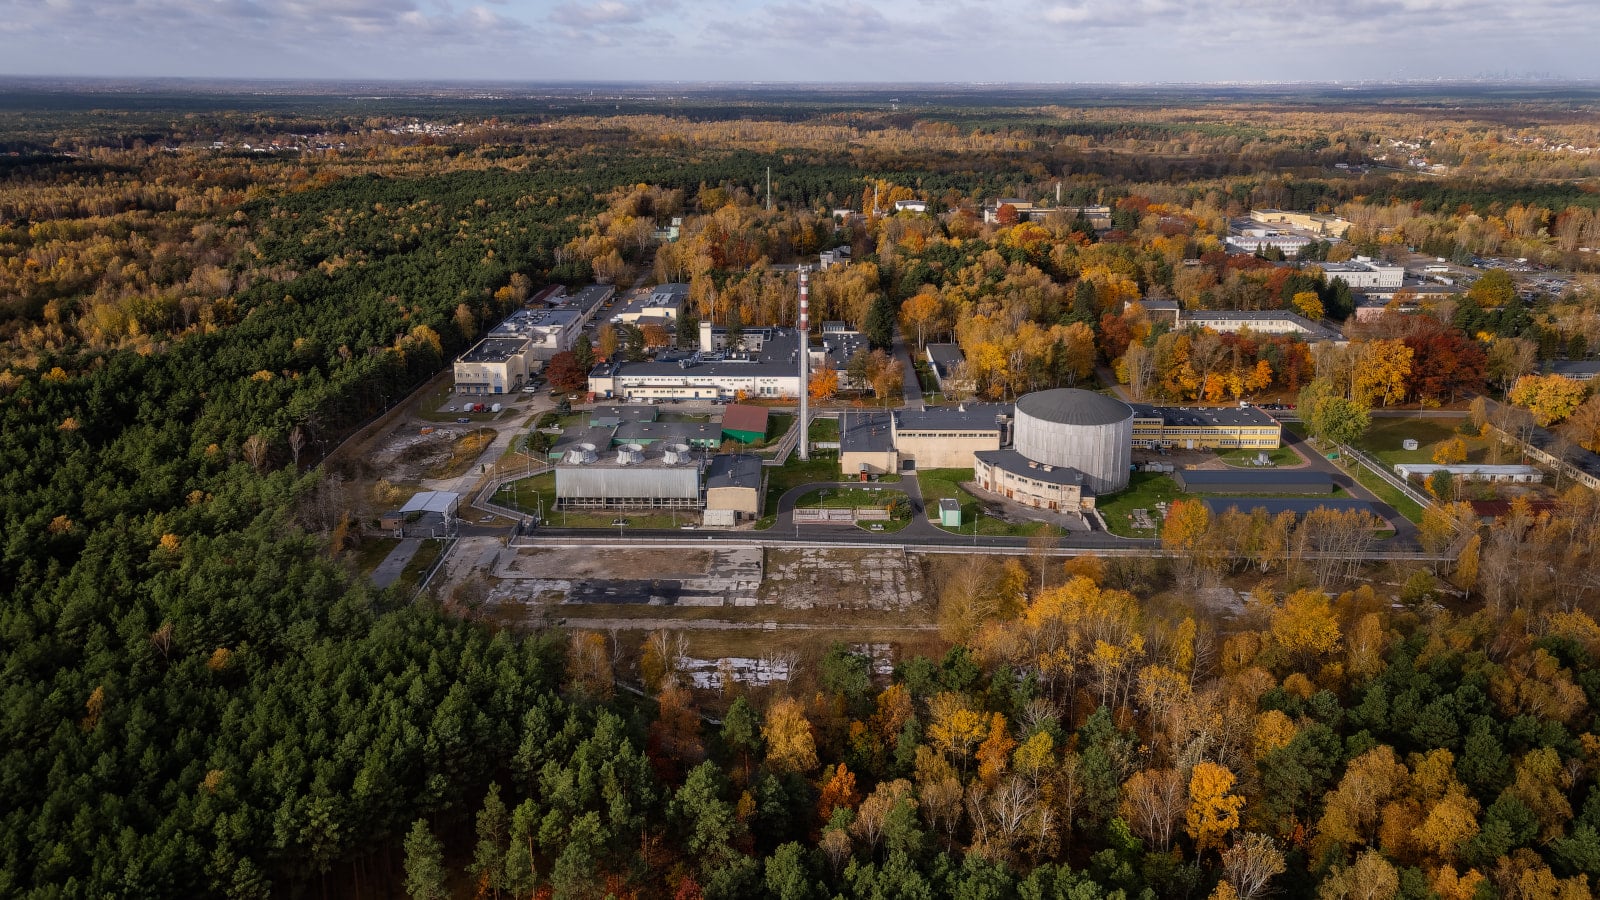
Poland’s National Centre for Nuclear Research (NCBJ) says its security systems detected and blocked a cyberattack on its IT infrastructure before any systems were compromised. The MARIA research reactor remained fully operational, authorities have been notified and an investigation is underway amid reporting that indicators may point to Iranian involvement and past APT44 activity. #NCBJ #MARIA #APT44

Microsoft disclosed a credential theft campaign that uses SEO poisoning to trick users into downloading fake VPN clients that harvest VPN credentials. The activity, attributed to Storm-2561, delivers digitally signed trojans via attacker-controlled sites and abused GitHub repositories to sideload malicious DLLs and deploy information stealers. #Storm-2561 #Hyrax #Bumblebee #Ivanti #SonicWall…

INTERPOL coordinated an international law enforcement operation that dismantled 45,000 malicious IP addresses and servers linked to phishing, malware, and ransomware, resulting in 94 arrests, 110 people under investigation, and the seizure of 212 electronic devices. India’s CBI also targeted a transnational fraud syndicate leveraging the Dubai-based fintech platform Pyypl, arresting…