Oracle released an emergency out‑of‑band patch for a critical unauthenticated remote code execution vulnerability tracked as CVE‑2026‑21992 that affects Oracle Identity Manager and Oracle Web Services Manager. Organizations should apply the Security Alert patches immediately for supported versions to mitigate the high‑severity risk posed by remote attackers. #OracleIdentityManager #OracleWebServicesManager…
Category: Cyber Security News

Daily Recap, Microsoft rolled back a newly introduced virtual account after it intermittently blocked access to cloud-based Exchange Online via Outlook Mobile and the new Outlook for Mac, and published an optional out-of-band KB5085516 emergency update to fix Microsoft account sign-in failures caused by KB5079473 affecting Windows 11 apps (Teams, OneDrive) with a restart workaround. The patching and threat activity also covers QNAP CVEs 62843–62846 and Oracle CVE-2026-21992 (CVSS 9.8), with CVE-2025-32975 impacting Quest KACE SMA, plus FBI warnings about Handala using Telegram and Russian Intelligence phishing via Signal, new DarkSword iOS flaws, a Trivy supply-chain compromise with CanisterWorm and TeamPCP, and Tycoon 2FA phishing.
#Handala #Telegram #RussianIntelligence #Signal #DarkSword #KACE #SMA #Trivy #CanisterWorm #TeamPCP #Tycoon2FA #AWSBedrock #NIST80081r3 #OperationAlice #AlexanderPaulTravis #NKITWorkers

The Tycoon2FA phishing-as-a-service platform disrupted by Europol and Microsoft on March 4 briefly saw activity fall after 330 domains were seized, but it returned to previous operational volumes within days. CrowdStrike reported daily campaign volumes dropped to about 25% on March 4–5 before rebounding to early 2026 levels, with the service continuing to target Microsoft 365 and Gmail accounts for BEC and cloud takeovers. #Tycoon2FA #Microsoft365
Mazda Motor Corporation disclosed that unauthorized access to a warehouse management system handling parts procured from Thailand exposed 692 records containing employee and business partner user IDs, full names, email addresses, company names, and business partner IDs, with no customer data affected. The company reported the incident to Japan’s Personal Information Protection Commission, implemented security measures and an external investigation, and warned impacted individuals to remain vigilant for phishing; no ransomware group has claimed responsibility, though Clop later posted Mazda domains. #Mazda #Clop

North Korean threat actor WaterPlum (aka Contagious Interview) is distributing the Node.js StoatWaffle malware through malicious Visual Studio Code projects that auto-run tasks.json to fetch and execute payloads. The campaign delivers a browser credential stealer and a RAT, abuses npm packages and compromised GitHub repositories, targets developers and crypto professionals via…

Decentralized finance platform Resolv suffered a breach after a compromised private key allowed an attacker to mint about $80 million of uncollateralized USR and trade much of it for roughly 11,408 ETH (≈ $24.5M), causing USR to depeg to about $0.26. Resolv has paused its app, enabled redemptions for verified users,…
Varonis Atlas is an end-to-end AI security platform that discovers, secures, and governs AI systems across the enterprise by connecting AI inventory, posture management, runtime guardrails, and compliance to data context. Built on the Varonis Data Security Platform, Atlas continuously detects and remediates risks such as prompt injection and jailbreaks while supporting regulatory frameworks and third-party AI risk management. #VaronisAtlas #PromptInjection
Crunchyroll is investigating a breach after attackers claimed to have stolen personal information for approximately 6.8 million users by compromising an Okta SSO account of a Telus International support agent. The attackers say they used malware to obtain credentials, accessed multiple Crunchyroll applications including Zendesk to download 8 million support tickets, and demanded $5 million in extortion while credit card exposure appears limited to data customers shared in tickets. #Crunchyroll #Zendesk
TeamPCP is conducting a campaign against Kubernetes clusters that installs the CanisterWorm backdoor on non-Iranian systems and deploys a geopolitically targeted destructive payload that wipes machines configured for Iran. Aikido links this activity to the Trivy supply-chain compromise and notes variants that spread via SSH and exploit unauthenticated Docker API access. #TeamPCP #CanisterWorm
James Junior Aliyu, a Nigerian national who used the aliases “Old Soldier” and “Ghost”, was sentenced to 90 months in U.S. prison for his role in an international scheme that hacked business email accounts and redirected millions in wire transfers. The ring, active since at least 2017, is estimated to have…

Kaplan disclosed that a fall 2025 cybersecurity incident exposed names, Social Security numbers, and driver’s license numbers for at least 230,000 people. Company filings show hackers had access to Kaplan servers from October 30 to November 18, law enforcement was notified, state breach notices were filed and class-action lawsuits are pending;…
The FBI warned that Russian and Iranian cyber campaigns are exploiting messaging platforms to compromise accounts and deploy malware, with Russian actors using phishing to hijack Signal accounts and Iranian actors using Telegram-linked malware attributed to Handala Hack. These campaigns have resulted in thousands of unauthorized accesses, allowed remote data exfiltration…
Trio-Tech’s Singapore subsidiary suffered a ransomware attack on March 11 that encrypted certain files and prompted the company to take systems offline and activate response protocols. After attackers published stolen data and listed Trio-Tech on a Tor-based leak site, management said the incident may be a material cybersecurity event as the…
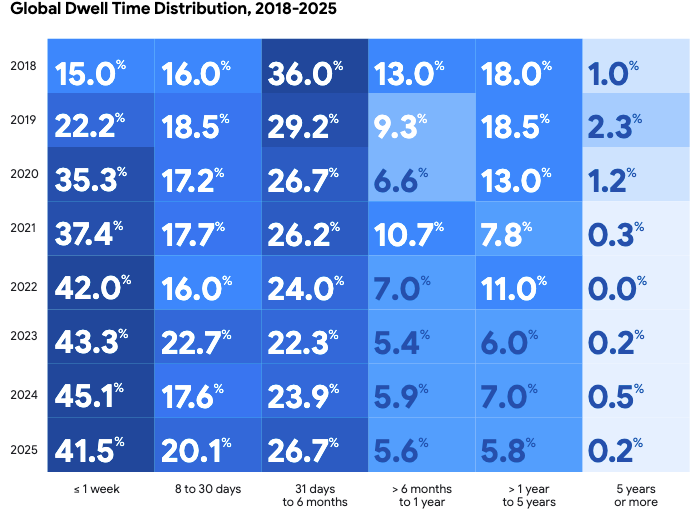
Google’s M-Trends 2026, based on Mandiant’s 500,000+ hours of incident investigations, reports that the time from initial access to handoff to secondary groups has collapsed from hours to a median of 22 seconds in 2025, often driven by automated access brokers. The report also highlights exploits as the top initial vector…
The TeamPCP hackers continued to target Aqua Security by compromising its GitHub organization and pushing malicious Trivy Docker images that delivered an infostealer. The attackers abused a compromised service account and CI runner tokens to inject credential-harvesting code, tamper with repositories, and publish unauthorized Docker Hub tags, prompting Aqua to rotate secrets and engage Sygnia for response. #TeamPCP #Trivy