SecurityWeek is publishing a daily digest of key product and service announcements ahead of RSAC 2026 to cut through the event noise. The roundup highlights dozens of AI-native and agent-focused security launches—from credential and access governance to agentic detection, identity resilience, SIEM/SOC automation, and closed-loop exposure remediation across cloud, endpoint, and…
Category: Cyber Security News
The FBI warned that Iranian-linked hackers tied to the Ministry of Intelligence and Security (MOIS) and the IRGC are using Telegram as command-and-control infrastructure to deliver Windows malware against journalists, dissidents, and other opponents. The alert links campaigns to the Handala hacktivist group, state-aligned Homeland Justice, and actors like Karma Below, noting seizure of leak domains and citing the Handala attack on Stryker that used Microsoft Intune to wipe devices. #Handala #HomelandJustice #KarmaBelow #MOIS #IRGC #Stryker #Telegram #MicrosoftIntune #Signal #WhatsApp
Microsoft is addressing an ongoing service issue that has intermittently prevented some users from accessing cloud-based Exchange Online mailboxes via Outlook mobile and the new Outlook for Mac. After investigating incident EX1256020, the company identified a newly introduced virtual account as the root cause and is reverting the change to remediate the outage. #Microsoft #ExchangeOnline

Microsoft warns of new tax‑season phishing campaigns that impersonate tax authorities and professionals to harvest credentials, deploy remote‑access software, and exfiltrate data. Attackers use Phishing‑as‑a‑Service kits and layered redirection to evade detection and abuse legitimate RMM tools like ScreenConnect, Datto, and SimpleHelp for persistent access. #Energy365 #SneakyLog #ScreenConnect #Datto #SimpleHelp #IRS…

AWS Bedrock’s connectivity to enterprise systems enables powerful AI workflows but also creates rich attack surfaces that can be exploited via permissions, configurations, and integrations. XM Cyber mapped eight validated attack vectors — from log manipulation and knowledge-base compromise to agent hijacking, flow injection, guardrail degradation, and prompt poisoning — and…

Three men were sentenced after admitting they allowed North Korean IT workers to use their identities to secure employment at U.S. companies, collect pay, and remotely access employer laptops, generating roughly $1.3 million in illicit salary payments. One defendant, Army Specialist Alexander Paul Travis, was sentenced to one year in prison…
QNAP released patches for multiple vulnerabilities across its products, including four SD‑WAN router bugs demonstrated at Pwn2Own Ireland 2025 (CVE-2025-62843 to CVE-2025-62846). The vendor also issued fixes for QuNetSwitch and QVR Pro defects, urged updates to patched versions, and noted the Pwn2Own exploits were performed by Team DDOS but not observed…

Security researchers found trojanized Trivy images and other malicious artifacts on Docker Hub following a Trivy supply-chain compromise that widened the blast radius across developer environments. The campaign, attributed to TeamPCP, used a compromised Aqua Security GitHub Actions credential to push a credential stealer, deface repositories, infect npm packages with CanisterWorm,…

Tycoon 2FA remains operational despite an international takedown and quickly returned to pre-disruption levels. The subscription-based PhaaS has generated over 30 million malicious emails monthly, was linked to roughly 96,000 victims, and accounted for 62% of Microsoft’s blocked phishing attempts in 2025. #Tycoon2FA #CrowdStrike…
Hackmanac CEO Sofia Scozzari warns that attackers are increasingly collaborating, scaling via as-a-service models, and exploiting organisational blind spots while defenders often treat cybersecurity as a purely technical issue instead of a business risk. She urges stronger information sharing, embedding security by design, and aligning cyber strategy with business priorities to…
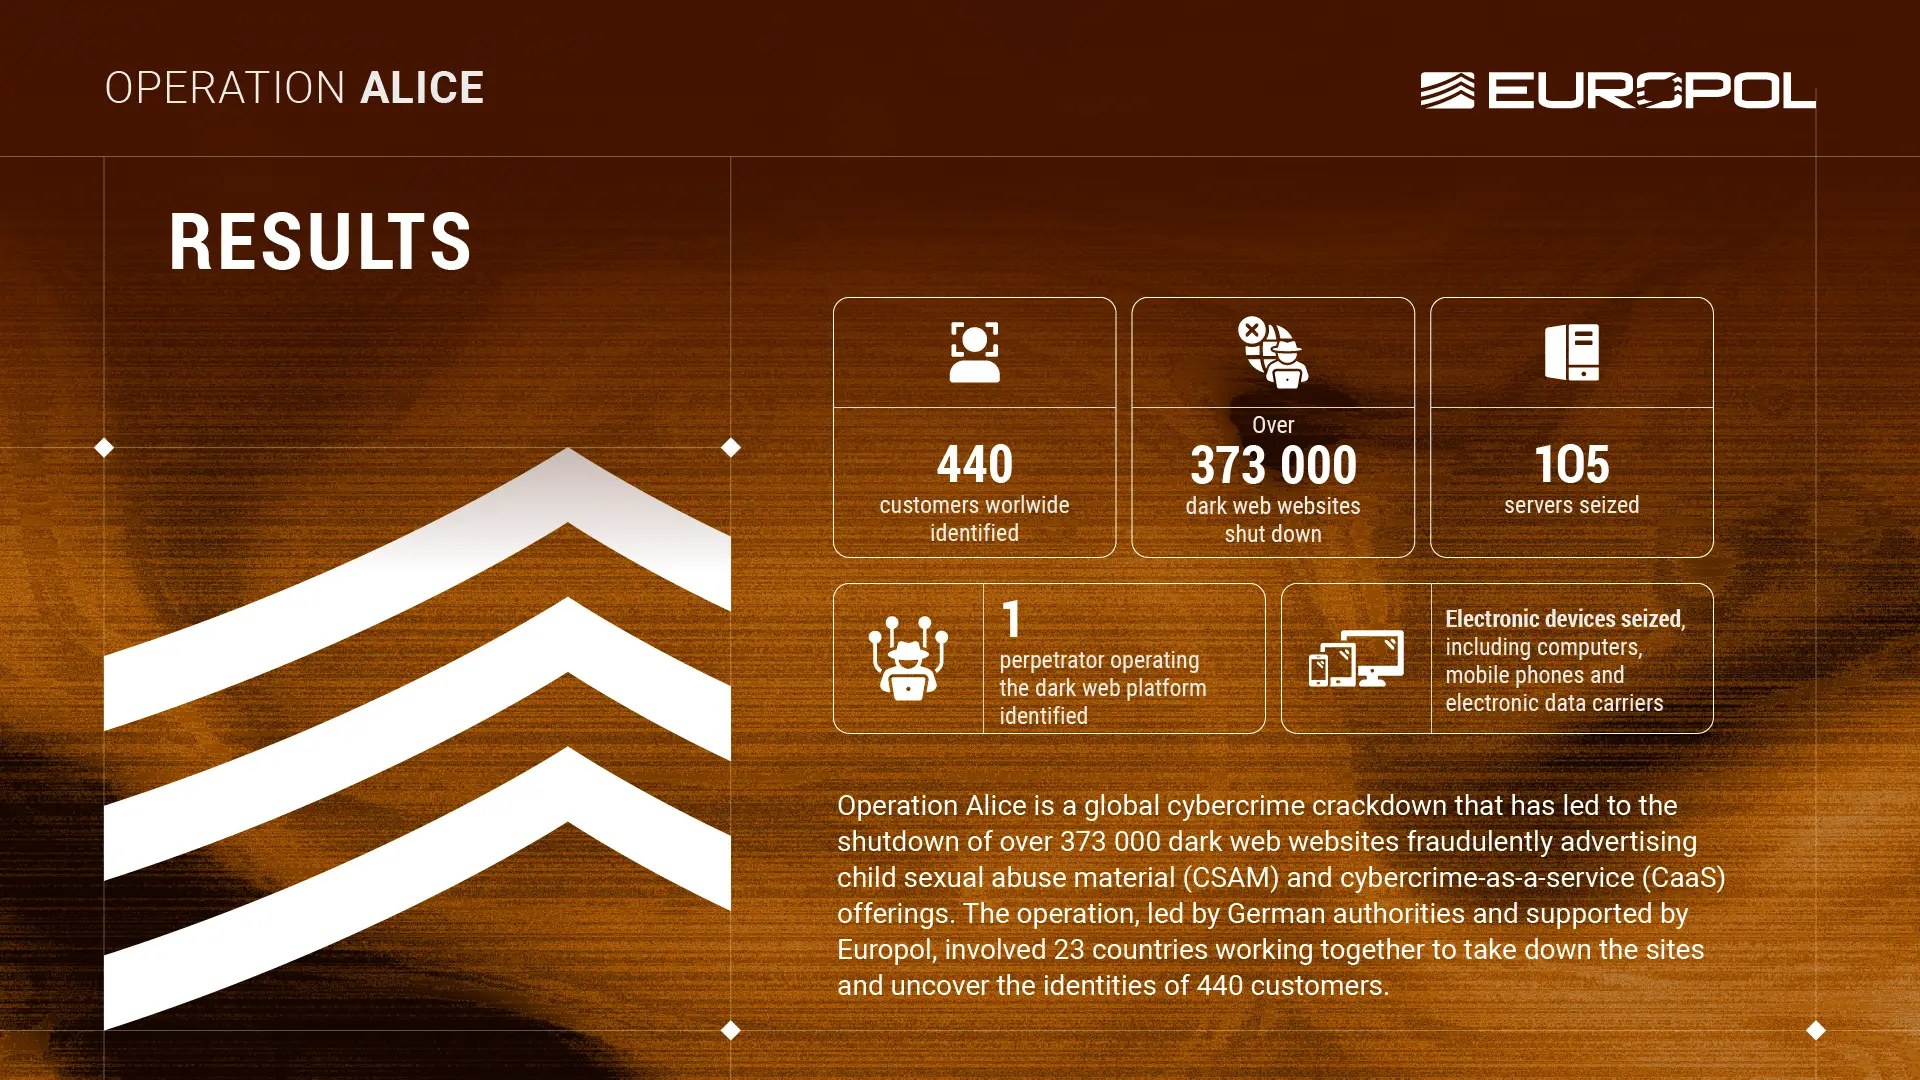
A 35-year-old man operating from China ran the largest fraudulent dark web network ever dismantled, creating over 373,000 onion domains to advertise child sexual abuse material and cybercrime-as-a-service offerings. German authorities led Operation Alice with Europol’s support, seizing servers and devices after uncovering that buyers paid in Bitcoin for nonexistent content,…
NIST SP 800-81r3 modernizes DNS security guidance for the first major revision since 2013, recasting DNS as an active enforcement layer and addressing protective DNS, encrypted DNS, DNSSEC, and operational resilience. The guidance recommends hybrid cloud/on‑prem protective DNS deployments, mandates encrypted DNS for U.S. federal civilian agencies where feasible, updates cryptographic…
Microsoft released an emergency update after the KB5079473 cumulative update caused Microsoft account sign-ins to fail across multiple apps, displaying a false “You’ll need the Internet…” error even when devices were online. Microsoft rolled out an optional out-of-band KB5085516 fix for Windows 11 25H2 and 24H2 devices, recommended installing the latest updates, and noted that Entra ID (Azure AD) sign-ins for businesses were not affected; a temporary restart workaround was also provided. #Microsoft #KB5079473 #KB5085516 #Windows11 #Teams #OneDrive #EntraID #SamsungGalaxyConnect
CISA ordered U.S. federal agencies to patch three iOS vulnerabilities exploited by the DarkSword exploit kit in campaigns that stole cryptocurrency and conducted cyberespionage. The exploit chain enabled sandbox escapes, privilege escalation, and remote code execution on iPhones running iOS 18.4–18.7 and has been linked to threat groups including UNC6353 and UNC6748. #DarkSword #UNC6353

Threat actors have been observed exploiting CVE-2025-32975 in unpatched Quest KACE Systems Management Appliance (SMA) instances, enabling authentication bypass and administrative takeover. Arctic Wolf detected activity from the week of March 9, 2026, including dropping Base64 payloads from 216.126.225[.]156, account creation via runkbot.exe, credential theft with Mimikatz, and RDP access to…