Oracle released out-of-band patches to address a critical remote code execution vulnerability in Identity Manager and Web Services Manager. The flaw, tracked as CVE-2026-21992 with a CVSS score of 9.8, affects REST WebServices and Web Services Security and can be exploited by an unauthenticated attacker; Oracle has not confirmed in-the-wild exploitation….
Category: Cyber Security News
India’s mobile-first digital economy has made mobile applications the primary attack surface where money, identities, and sensitive customer data are exposed. Women leaders are reshaping cybersecurity by promoting security-by-design, embedding runtime protections in apps, and fostering cross-industry collaboration to detect and respond to mobile threats in real time. #ProtecttAiLabs #RuntimeApplicationSelfProtection…
A North Carolina man pleaded guilty to running an AI-assisted scheme that generated hundreds of thousands of songs and used bots to stream them, stealing over $8 million in royalties from legitimate artists. The case demonstrates how scalable AI-generated content and automated accounts can evade basic detection on music streaming platforms…

Cybersecurity Threat Research ‘Weekly’ Recap: this overview surveys vulnerabilities, supply-chain and developer-tooling abuse, phishing and malware campaigns across Langflow (CVE-2026-33017), CanisterWorm, CursorJack, SnappyClient, Vidar Stealer, AsyncRAT, GhostMail, Boggy Serpens, DieNet and Konni, with notable operational exposures such as Myclaw360 TLS key and Larva26002. Cybersecurity Threat Research ‘Weekly’ Recap: it also highlights evolving trends in AI-assisted threats, container security with Defend for Containers (D4C) guidance and TeamPCP container attack scenarios, plus CI/CD risk from Trivy action hijacking and related supply-chain abuses. #Langflow #CVE-2026-33017 #CanisterWorm #CursorJack #SnappyClient #VidarStealer #AsyncRAT #GhostMail #BoggySerpens #DieNet #Konni #Myclaw360 #Larva26002 #DefendForContainers #TeamPCP #TrivyAction #Kubernetes
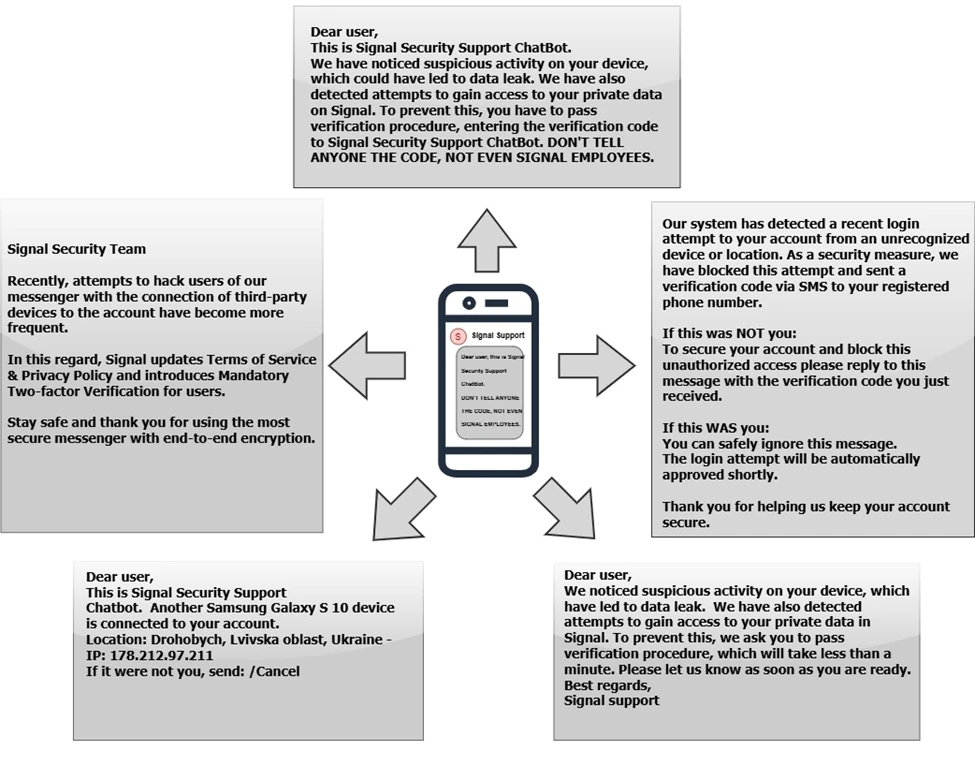
The FBI and CISA issued a joint PSA warning of a global phishing campaign by the Russian Intelligence Services that targets Commercial Messaging Applications to compromise individual accounts and steal private communications. The actors use social engineering and abuse of linked-device features—especially against Signal users—to take over accounts, monitor messages, infiltrate…
VoidStealer, an infostealer seen in the wild, bypasses Chrome’s Application-Bound Encryption (ABE) by using hardware breakpoints to extract the v20_master_key directly from browser memory. The malware attaches as a debugger to suspended browser processes at startup, reads the register holding the plaintext master key, and uses ReadProcessMemory to steal it, a technique likely adopted from the open-source ElevationKatz project. #VoidStealer #v20_master_key

Daily Recap, The FBI and allied agencies warn that Russian intelligence-linked actors are conducting mass phishing campaigns targeting Signal and WhatsApp, hijacking accounts via verification-code requests and malicious QR/links, compromising thousands of high-value targets. The report also details a supply-chain attack involving the CanisterWorm that infected npm packages and breached Trivy GitHub Actions, with ties to TeamPCP and hackerbot-claw, alongside enforcement actions such as Operation Alice and the Handala takedown. #CanisterWorm #OperationAlice
Threat actors are abusing Microsoft Azure Monitor to send callback phishing emails that impersonate the Microsoft Account Security Team and warn of unauthorized billing charges. These alerts are sent from [email protected] and pass SPF, DKIM, and DMARC checks, using editable alert descriptions and attacker-controlled mailing lists to deliver urgent invoice-themed messages urging victims to call fraudulent phone numbers. #AzureMonitor #WindowsDefender
The Trivy vulnerability scanner was compromised in a supply-chain attack that trojanized the v0.69.4 release and multiple trivy-action GitHub Actions to distribute credential-stealing malware. Researchers link the campaign to TeamPCP, which exfiltrated harvested secrets to a typosquatted C2 or public GitHub repos, established persistence, and later spread a self-propagating npm worm named CanisterWorm. #Trivy #TeamPCP
Google announced Advanced Flow, a new Android mechanism rolling out in August that lets power users sideload APKs from unverified developers while adding protective controls. The one-time, multi-step setup — enabling Developer Mode, confirming no coercion, restarting and reauthenticating, waiting 24 hours, and final confirmation — introduces friction to thwart scammer coaching and supports the upcoming developer identity verification plan; #AdvancedFlow #GASA

Oracle has released security updates to fix a critical, remotely exploitable vulnerability (CVE-2026-21992) in Oracle Identity Manager and Oracle Web Services Manager that could allow unauthenticated remote code execution. Oracle and the NVD warn the flaw is easily exploitable over HTTP and urge affected users to apply the updates immediately. #CVE-2026-21992…

U.S. and French agencies warn that Russian intelligence‑affiliated threat actors are running phishing campaigns to compromise commercial messaging apps like Signal and WhatsApp to seize accounts of high‑value individuals such as officials, military personnel, journalists, and political figures. The attacks rely on social engineering—asking for verification codes or using malicious QR/link…
Arctic Wolf observed activity tied to exploitation of CVE-2025-32975 that allows unauthenticated attackers to impersonate users and potentially gain full administrative control of internet-exposed Quest KACE SMA appliances. Organizations still running unpatched KACE SMA instances are urged to apply the May 2025 patches immediately to prevent intrusions. #CVE-2025-32975 #QuestKACE…
Daily Recap, Iran-linked Handala resurged with a new domain after U.S. seizures, with authorities tying the actor to MOIS and investigators linking destructive Stryker wipes to the campaign as CISA/FBI warned about hardening Microsoft Intune. In the nation-state and supply-chain space, APT28 exploited a high-severity Zimbra CVE-2025-66376 against Ukrainian government mail, Lazarus/Bluenoroff suspected in Bitrefill, Speagle hijacked Cobra DocGuard to exfiltrate data, and Interlock ransomware abused a Cisco zero-day CVE-2026-20131.
#Handala #MOIS #Stryker #Intune #APT28 #Lazarus #Bluenoroff #Speagle #CobraDocGuard #Interlock #Zimbra #Cisco

Threat actors behind the Trivy supply-chain compromise are conducting follow-on attacks that have infected dozens of npm packages with a self-propagating worm named CanisterWorm. The worm uses an Internet Computer (ICP) canister as a decentralized dead-drop for C2, allowing attackers (suspected TeamPCP) to swap payload URLs and remotely update all infected…