Researchers at Huntress say a phishing campaign abusing Railway cloud-hosting infrastructure has given attackers access to hundreds of Microsoft cloud accounts. The campaign used AI-generated, highly individualized lures and exploited Microsoft’s device OAuth flow to obtain long-lived tokens, prompting Huntress to push conditional access blocks for Railway domains. #Railway #Microsoft…
Category: Cyber Security News
The Dutch Ministry of Finance confirmed that some of its systems were breached after an intrusion detected on March 19, and access to affected systems has been blocked while an investigation continues. Officials say tax, customs and benefits systems were not affected, the ministry has not disclosed the number of employees impacted or whether data was exfiltrated, and no threat actor has claimed responsibility. #DutchMinistryOfFinance #DutchNationalPolice
Aleksey Olegovich Volkov pleaded guilty to acting as an initial access broker and was sentenced to 81 months in prison for selling corporate network access to the Yanluowang ransomware operation. Federal investigators recovered chat logs, stolen data, and financial records linking Volkov to roughly $1.5 million in ransom proceeds and ordered restitution and forfeiture exceeding $9.16 million. #Yanluowang #AlekseyVolkov
Infinite Campus warned customers of a data breach after an extortion attempt by the ShinyHunters group, which claims to have accessed an employee’s Salesforce account. The company says most exposed records were publicly available directory information, will not negotiate with the attacker, and has disabled some customer-facing services while scanning for affected Salesforce data. #ShinyHunters #InfiniteCampus
Bug bounty platform HackerOne notified hundreds of employees that their personal data was stolen after attackers breached Navia, a U.S. benefits administrator serving over 10,000 employers. The breach, caused by a Broken Object Level Authorization (BOLA) vulnerability that exposed Social Security numbers and other sensitive details for 287 employees and their dependents, increases the risk of phishing and social engineering despite Navia saying claims and financial accounts were not affected. #HackerOne #Navia
As the workforce disperses beyond the corporate perimeter, Zero Trust is essential to tie identity to device posture rather than assuming anything inside the network is safe. Because MFA alone cannot detect compromised endpoints or stolen session tokens, solutions like Specops Device Trust bind identity to a verified device and enforce continuous posture checks to secure access. #SpecopsDeviceTrust #ActiveDirectory

The Dutch Ministry of Finance is investigating a cyberattack that compromised several internal systems after a third party alerted officials. Affected systems were taken offline and access blocked while investigators determine the entry point and whether sensitive data was exposed, though core taxation and customs services remain unaffected. #DutchMinistryofFinance #Odido…

SecurityWeek and CIS are hosting a live webinar on Tuesday, March 24, 2026 at 1PM ET to demonstrate how the CIS Critical Security Controls® and CIS Benchmarks® can be used together to support secure configuration at scale. Attendees will learn to track hardening progress, manage exceptions, generate remediation and compliance-ready reports,…

Google released Chrome 146 to patch eight high-severity memory-safety vulnerabilities, including heap buffer overflows, out-of-bounds reads, use-after-free bugs, and an integer overflow. Notable fixes include CVE-2026-4673 and CVE-2026-4677 in WebAudio (the former earned a $7,000 bounty), and users should update to Chrome 146.0.7680.164/165 immediately to reduce exposure to active exploits. #Chrome146…
Lapsus$ claims to have hacked AstraZeneca and stolen roughly 3GB of sensitive enterprise data, including credentials, internal code repositories, and employee information. If verified, the leaked assets posted on the group’s Tor site could impact employees, partners, intellectual property, and the supply chain. #Lapsus$ #AstraZeneca…

Aleksei Volkov, a 26-year-old Russian national, was sentenced to 81 months in prison for acting as an initial access broker who sold stolen network credentials that enabled numerous ransomware attacks against U.S. organizations. His sales of unauthorized access to groups like Yanluowang helped cause over $9 million in actual losses and…

Aleksei Olegovich Volkov was sentenced in the U.S. to 6.75 years (81 months) after admitting he acted as an initial access broker who facilitated dozens of ransomware attacks for groups including the Yanluowang crew, causing more than $9 million in actual losses and over $24 million in intended losses. U.S. prosecutors…
Stryker has confirmed investigators identified a malicious file used in the March 11 Iran-linked attack claimed by Handala, and evidence suggests the actor likely abused the company’s Microsoft Intune environment—possibly after obtaining credentials via infostealer malware—to wipe devices. The company reports no evidence of widespread malware or ransomware affecting customers or…

Dr. Sheeba Armoogum argues that the greatest cybersecurity vulnerabilities are often human—requiring AI-enhanced, ethically transparent systems and a focus on cyberpsychology to preserve trust. Her book Digital Afterlife and her work at the University of Mauritius call for lifecycle governance of digital assets, structural mentoring to elevate women into advanced research…
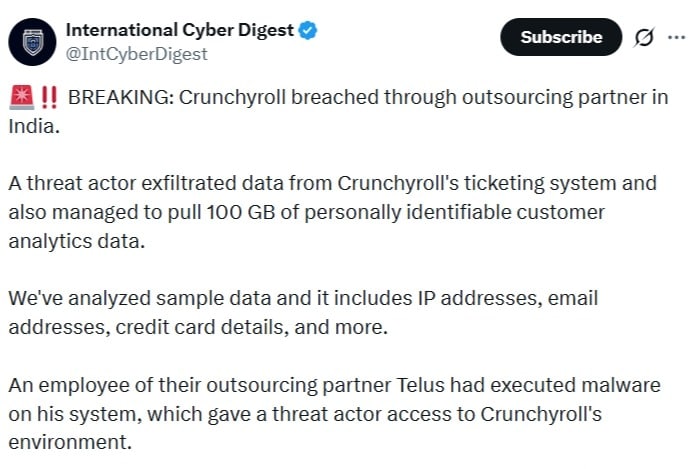
Reports allege a March 12, 2026 data breach at Crunchyroll that exposed nearly 100GB of user data—including email addresses, IPs, passwords, and some credit card information—after an attacker gained access via a third‑party vendor. Crunchyroll has not confirmed the full scope, but the incident underscores risks from outsourced ticketing and support…