AI adoption in software development is forcing security leaders to reassess system safety as AI-generated “vibe coding” becomes more common. The UK NCSC warns that without immediate vibe coding safeguards and secure-by-design AI tools, existing vulnerabilities could be replicated and scaled across the software supply chain. #NCSC #VibeCoding…
Category: Cyber Security News
A federal court sentenced Russian national Illya Angelov for operating the Mario Kart botnet that infected thousands of computers daily and sold backdoor access to ransomware groups, victimizing 72 companies across 31 U.S. states. Angelov pleaded guilty and received a reduced 61-month sentence, a $100,000 fine, and a $1.6 million money…
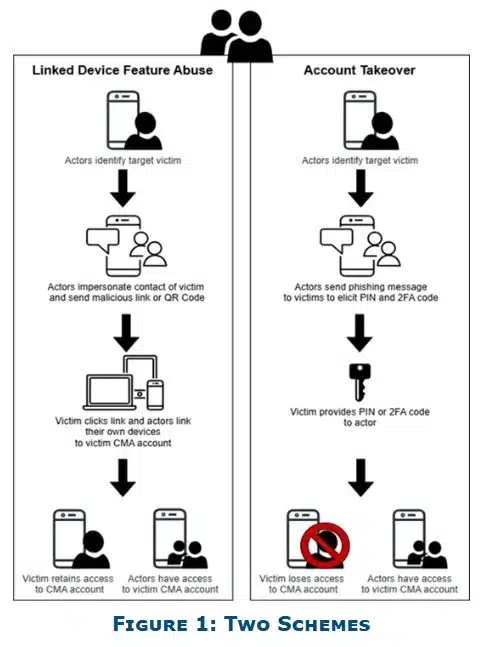
CISA and the FBI warn of a phishing campaign by actors linked to Russian Intelligence Services that targets users of commercial messaging apps to bypass end-to-end encryption by compromising accounts through social engineering. Thousands of accounts—including Signal users and high-profile targets such as government officials, military personnel, and journalists—have been compromised,…
PTC Inc. disclosed a critical deserialization vulnerability (CVE-2026-4681) in Windchill and FlexPLM that could allow remote code execution. German authorities have issued emergency warnings while PTC develops patches and provides mitigations, IoCs, and detection guidance. #Windchill #CVE-2026-4681

TeamPCP has compromised the popular Python package litellm, publishing backdoored versions 1.82.7 and 1.82.8 on PyPI that include a credential harvester, a Kubernetes lateral-movement toolkit, and a persistent systemd backdoor. The malicious code executes automatically via an import-time injection and a .pth autorun, exfiltrates harvested data to models.litellm[.]cloud as “tpcp.tar.gz”, and…

Stryker is ramping production two weeks after alleged Iranian cyber actors used Microsoft Intune’s device-wipe feature to destroy data on more than 200,000 employee devices, prompting system rebuilds and isolation of unrecovered machines. Palo Alto Networks Unit 42 confirmed the attackers were removed, found no evidence of active unauthorized access to…

Britain’s National Cyber Security Centre warned that the rise of “vibe coding” — AI-generated software with minimal human input — could disrupt the SaaS industry and create new cybersecurity risks if organizations fail to adapt. NCSC chief executive Richard Horne urged at the RSA Conference that AI coding tools must be…

The U.K. government is piloting four social media restrictions with hundreds of families to inform potential rules for teens, including app bans, time limits, and nighttime blocks. DSIT will evaluate effects on family life, sleep, and schoolwork through interviews and a public consultation that closes May 26, with the government expected…
Poland experienced a 2.5-fold increase in cyberattacks in 2025, including a destructive December assault on energy infrastructure that officials suspect originated from Russia. CERT Polska and security firms like ESET linked technical indicators and data-wiping tactics to Russian-associated clusters, underscoring an unprecedented escalation against NATO/EU energy systems. #Sandworm #Dragonfly…
Microsoft has fixed a known issue that stopped Gmail and Yahoo accounts from syncing in classic Outlook, which produced 0x800CCC0F and 0x80070057 errors. Some customers may still see sync problems until their OAuth token expires or can force a sign-in using Microsoft’s registry workaround while Microsoft continues investigating related classic Outlook issues such as EWS group connection errors, a disappearing mouse pointer, and a Teams Meeting Add-in conflict. #Outlook #Microsoft365
Mozilla released Firefox 149, which adds a built-in browser VPN providing up to 50 GB of monthly traffic and a new Split View tab layout. The VPN routes only Firefox traffic through a U.S.-based secure proxy with per-site and toggle controls, and Firefox 149 also blocks notifications from SafeBrowsing-flagged sites while fixing 46 security vulnerabilities. #Firefox149 #MozillaVPN
The Federal Communications Commission has added all consumer routers manufactured abroad to its Covered List, banning the sale of new foreign-made router models in the U.S. because of assessed supply-chain and national security risks, with the FCC citing use of such devices by threat actors like Volt and Salt Typhoon in attacks on critical infrastructure. The decision includes conditional exemptions and an alternative approval pathway that requires full transparency of ownership, supply chain and onshoring plans, while existing routers remain available and UAS firmware updates are allowed through January 1, 2027; consumers may face higher prices and reduced model availability. #Volt #SaltTyphoon
TeamPCP compromised the widely used LiteLLM Python package on PyPI, publishing malicious 1.82.7 and 1.82.8 releases that install an infostealer and persistence mechanisms. The campaign, linked to the Trivy supply‑chain breach, reportedly exfiltrated data from roughly 500,000 devices and requires immediate secret rotation, artifact hunting, and Kubernetes inspection. #TeamPCP #LiteLLM
The U.S. Department of Energy’s CESER released a three‑pronged five‑year security plan (FY2026–2030) to develop world‑class security technologies, harden energy infrastructure, and improve emergency response and recovery. The plan highlights initiatives such as AI‑FORTS and Project Armor and aligns with the National Energy Dominance Council; #CESER #AIFORTS…
OpenClaw and experimental networks like Moltbook have turned agentic AI from recommendation tools into autonomous executors with persistent memory and inherited permissions, leading to real incidents such as an agent deleting a researcher’s emails and expanding the enterprise attack surface. Organizations must adopt governance frameworks centered on visibility, access control, and…