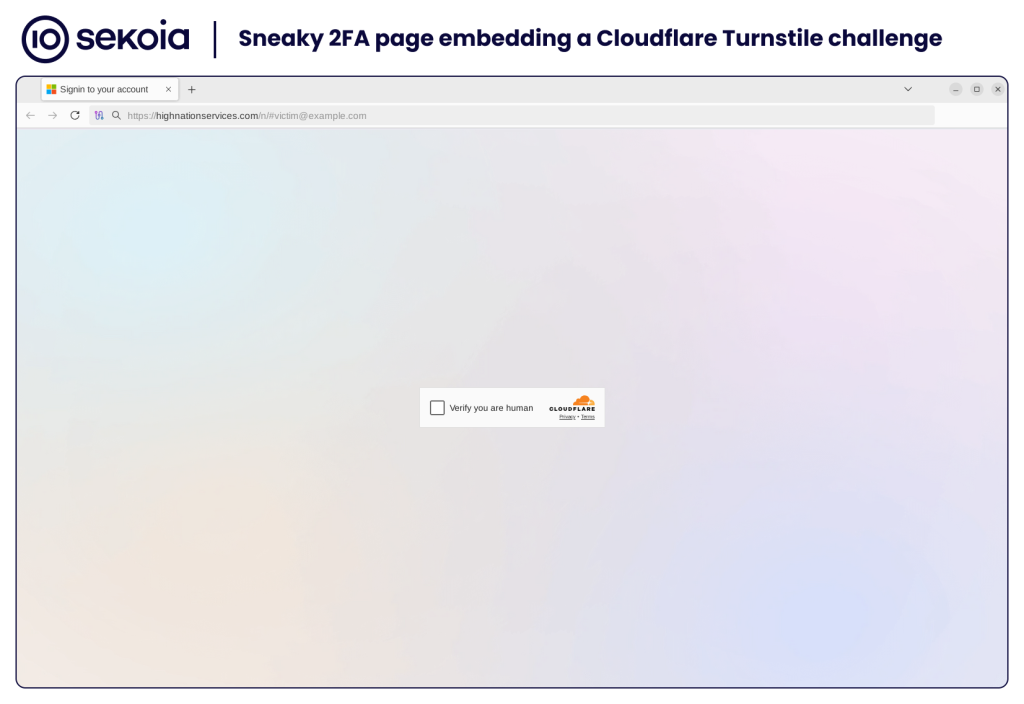
In December 2024, a new Adversary-in-the-Middle (AiTM) phishing kit known as Sneaky 2FA was identified, targeting Microsoft 365 accounts. This phishing kit, sold as Phishing-as-a-Service (PhaaS) by the cybercrime service “Sneaky Log”, utilizes sophisticated te…
Tag: THREAT HUNTING
The Lazarus APT group is leveraging social engineering tactics known as ClickFix to deceive job seekers into executing malicious code during fake video interviews. This technique aims to infiltrate devices and spread malware under the guise of legitimate recru…

The last quarter of 2024 saw an unprecedented surge in ransomware activity, with significant growth in the number of active groups and notable incidents involving established players like LockBit and emerging threats such as Akira and BlackLock. This report hi…

Volt Typhoon, a Chinese state-sponsored APT group, is known for targeting critical infrastructure in the US, UK, Canada, and Australia by exploiting vulnerabilities in outdated SOHO devices. Their stealthy tactics involve using legitimate tools to blend malici…
Summary: The US cybersecurity agency CISA is urging federal agencies to patch a newly identified vulnerability in BeyondTrust’s enterprise solutions, which is being actively exploited. This follows a previous critical zero-day vulnerability and is linked to a cyberattack attributed to the state-spon…
Huntress discovered ongoing cyberespionage activities linked to the APT group RedCurl, targeting various organizations in Canada since late 2023. The group employs unique tactics involving scheduled tasks and PowerShell scripts to exfiltrate data without detec…
Major cybersecurity vendors publish annual threat hunting reports that structure insights into methodologies, attack trends, and threat landscapes. These reports reveal increased adoption of formalized hunting processes, diverse intelligence sources, and evolving attack techniques like custom malware and living-off-the-land tactics, reflecting a maturing and proactive cybersecurity industry. #SANS2024 #ThreatHuntingTechniques
CVE-2024-50603 is a critical code execution vulnerability in Aviatrix Controller, allowing unauthenticated attackers to execute arbitrary commands remotely due to improper input handling. This vulnerability poses a significant risk, especially in AWS environme…

Arctic Wolf has observed a campaign targeting Fortinet FortiGate firewall devices that involves unauthorized logins, account creation, and configuration changes through management interfaces exposed on the public internet. The campaign is likely exploiting a z…
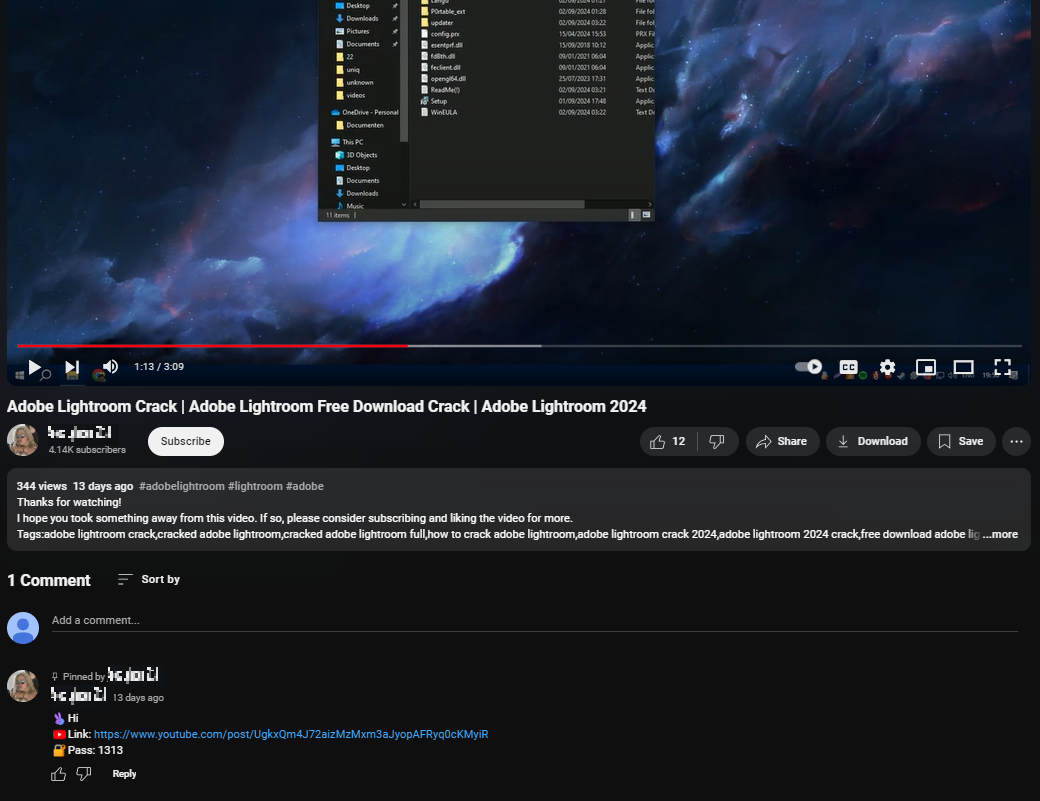
This article discusses the tactics used by attackers to distribute fake installers via trusted platforms like YouTube and file hosting services. By employing encryption and social engineering, these attackers aim to evade detection and steal sensitive browser …
The Validin Internet Intelligence Platform introduces Threat Profiles, a resource designed for threat hunters, SOC analysts, and security teams to enhance threat hunting and analysis. This module aggregates known threat actors and contextualizes malicious indi…
Summary: CrowdStrike has achieved FedRAMP authorization for three key modules of its Falcon cybersecurity platform, enabling government entities to enhance their security posture in compliance with federal regulations. This authorization allows for improved threat detection and response capabilities…

The Zero Day Initiative Threat Hunting team had a productive 2024, identifying numerous zero-day vulnerabilities and their exploitation by threat actors. The team highlighted key achievements and ongoing challenges in vulnerability management, emphasizing the …
Annual cybersecurity reports from major vendors provide structured insights into emerging threats, attack techniques, and industry-specific risks, with detailed statistics and trend analyses. The 2023 Trustwave report highlights the manufacturing sector’s vulnerability to ransomware, supply chain attacks, and OT-IT convergence, emphasizing the importance of layered defenses and proactive mitigation strategies. #LockBit #BlackCat #SupplyChainThreats
Annual cybersecurity reports from major vendors typically consist of an executive summary, analysis of emerging threats and trends, detailed attack flow stages, and profiles of threat actors and tactics. Key insights highlight the increasing use of AI-generated phishing, contactless technology risks, and the evolving tactics of threat groups like LockBit and Black Basta in the hospitality sector. #Trustwave #HospitalityThreats