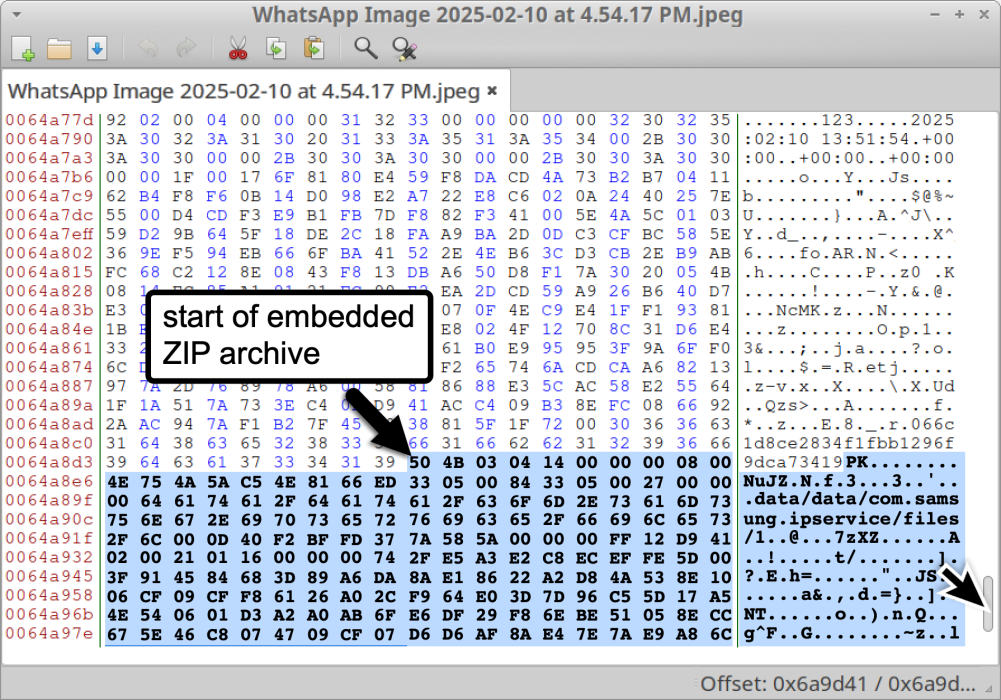
Cybersecurity researchers have uncovered a sophisticated Android spyware campaign called LANDFALL that exploits a zero-day vulnerability in Samsung Galaxy devices to deliver surveillance tools via malicious images in WhatsApp messages. The campaign demonstrates the widespread use of DNG image processing vulnerabilities across mobile platforms, highlighting targeted intrusion activities mainly in the…
Tag: SPYWARE

Cybersecurity Threat Research ‘Weekly’ Recap. Adversaries persist with phishing, credential theft, supply-chain compromises, and AI-enabled threats, targeting individuals, organizations, and critical infrastructure across multiple sectors. The report highlights notable campaigns, new backdoors, ransomware evolutions, vulnerabilities, and the increasing use of AI for malware development, detection evasion, and incident response improvements.
#Tycoon 2FA #Fake DMCA #RaccoonO365 #Booking.com “I Paid Twice” #AdE crypto-tax phishing #Bank of Italy phishing #Remcos #SleepyDuck #Gootloader #LANDFALL #Fantasy Hub #Cephalus #Midnight ransomware #DragonForce #MuddyWater #SesameOp #OpenAI C2 #Balancer #Great Firewall

Daily Recap, Malicious NuGet time bombs threaten industrial systems, while Landfall spyware exploits a Samsung zero-click flaw to target devices across regions. State-backed actors continue to use legacy flaws for espionage and destructive campaigns, with new zero-day fixes and AI-powered malware emerging in the threat landscape. #NuGet #Landfall #Log4j #Sandworm #CavalryWerewolf #QNAP #UPenn #CyberCommand

A security flaw in Samsung Galaxy devices was exploited as a zero-day to deliver the espionage tool LANDFALL, targeting Middle Eastern users. The campaign involved malicious WhatsApp images and exploited two unpatched vulnerabilities, revealing advanced command-and-control techniques. #CVE-2025-21042 #LANDFALL #StealthFalcon…

Security researchers uncovered LANDFALL, a sophisticated spyware campaign targeting Samsung Galaxy phones using a zero-day exploit. The campaign appears to be driven by espionage motives, with potential links to Middle Eastern threat actors. #LANDFALL #ZeroDay #SamsungGalaxy #Espionage #MiddleEast…
A new Android spyware called Landfall exploited a zero-day vulnerability in Samsung devices for remote code execution, primarily targeting users in the Middle East and North Africa. The attack involved infected DNG images sent via WhatsApp, allowing spying capabilities such as microphone recording and data theft. #CVE-2025-21042 #Landfall #SamsungGalaxy #StealthFalcon…
This week’s cybersecurity news highlights governmental efforts to remove Chinese Huawei technology from critical networks and ongoing law enforcement operations targeting criminal organizations through covert messaging apps. The stories also cover new vulnerabilities, industry-specific threats, and incident responses that shape the current cybersecurity landscape. #Huawei #AN0M…
A zero-day vulnerability in Samsung’s Android image processing library was exploited to deploy the ‘LandFall’ spyware via malicious WhatsApp images. The attack targeted Samsung Galaxy devices in the Middle East and involved sophisticated techniques for persistence, evasion, and device fingerprinting. #CVE-2025-21042 #LandFall #SamsungGalaxy
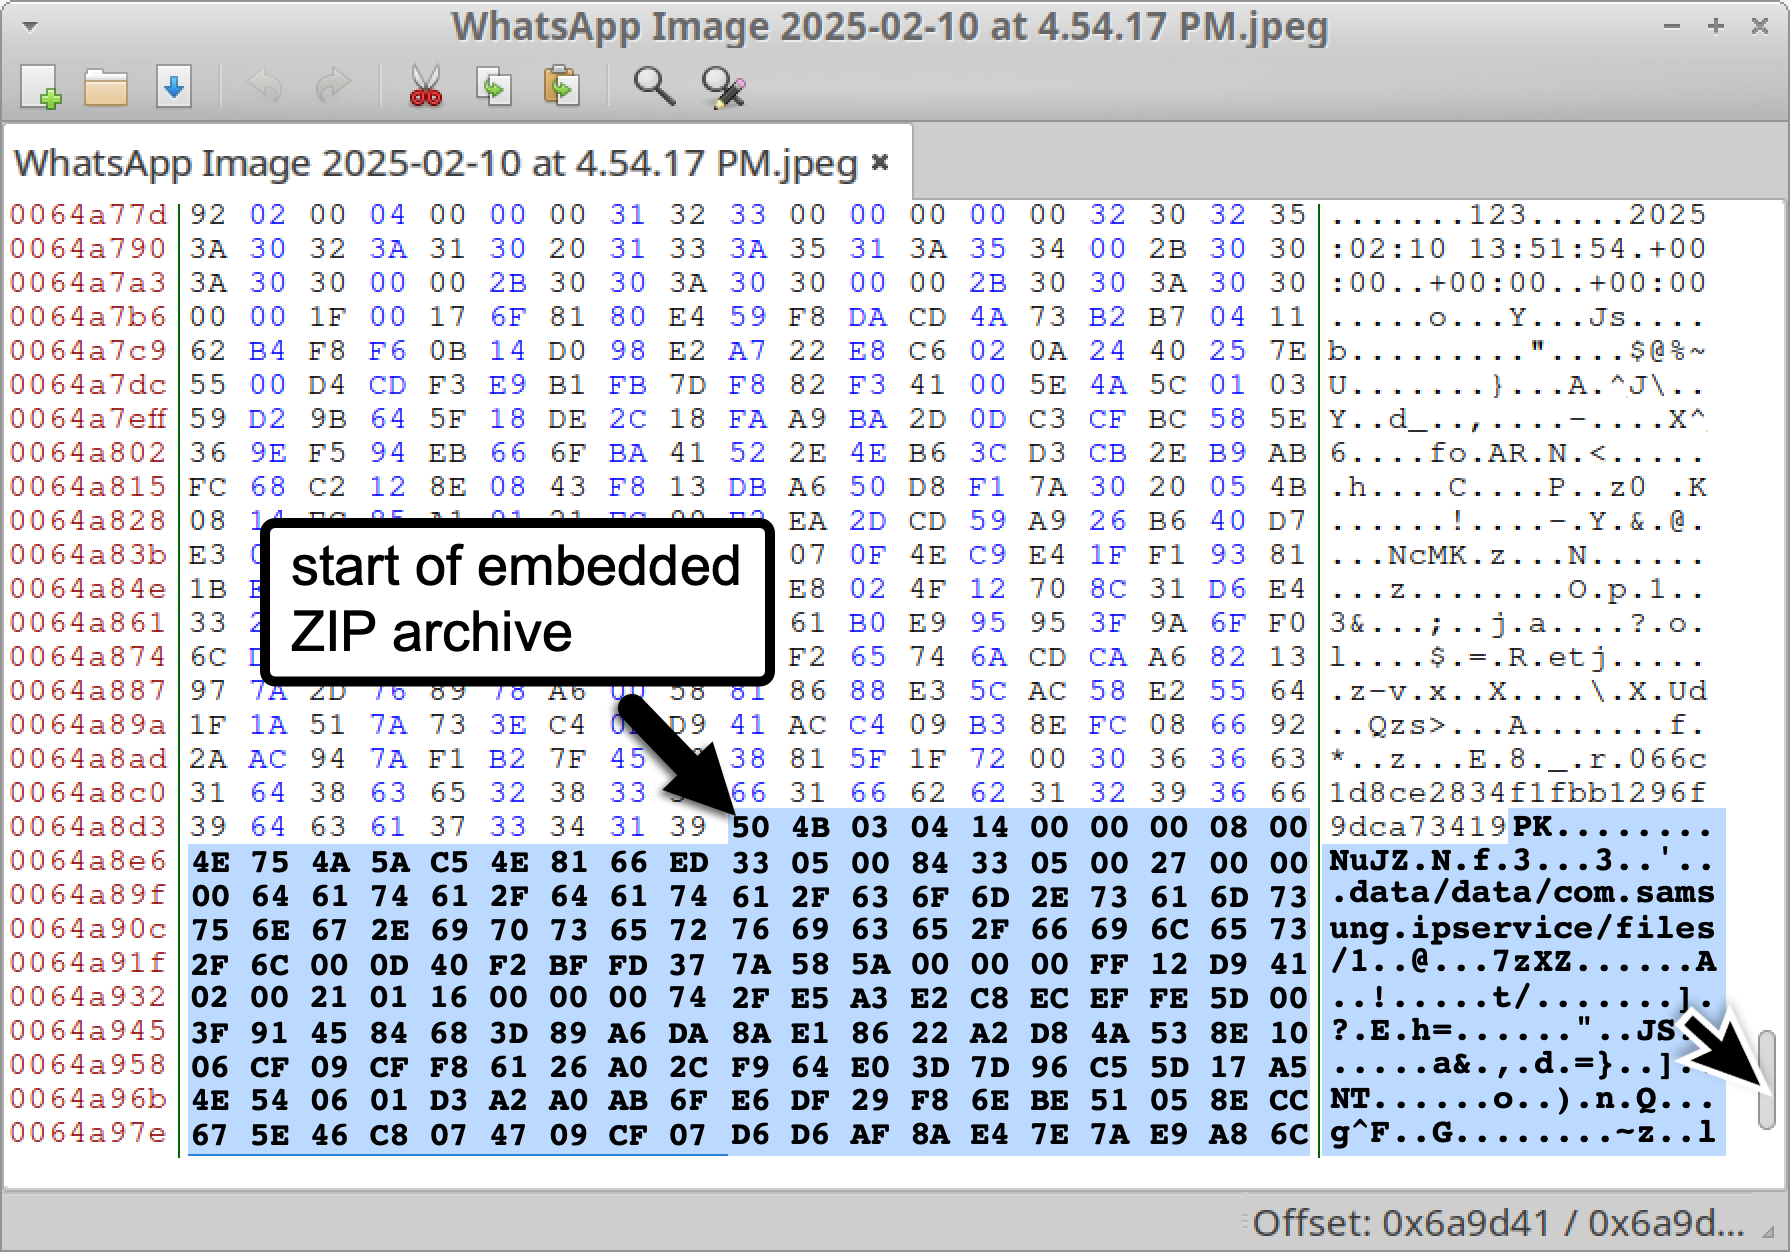
Unit 42 uncovered LANDFALL, a previously unknown Android spyware family targeting Samsung Galaxy devices that was delivered via malformed DNG image files exploiting a zero-day in Samsung’s image processing library (CVE-2025-21042) and active in mid-2024 through early 2025. The campaign used embedded shared object payloads and infrastructure consistent with commercial spyware…
Google has released a Chrome update to fix five vulnerabilities, including three high-severity flaws related to memory safety and UI security. These fixes come at a time when browser vulnerabilities are increasingly exploited by threat actors targeting user systems and organizations. #ChromeVulnerabilities #WebGPU #V8JavaScript…
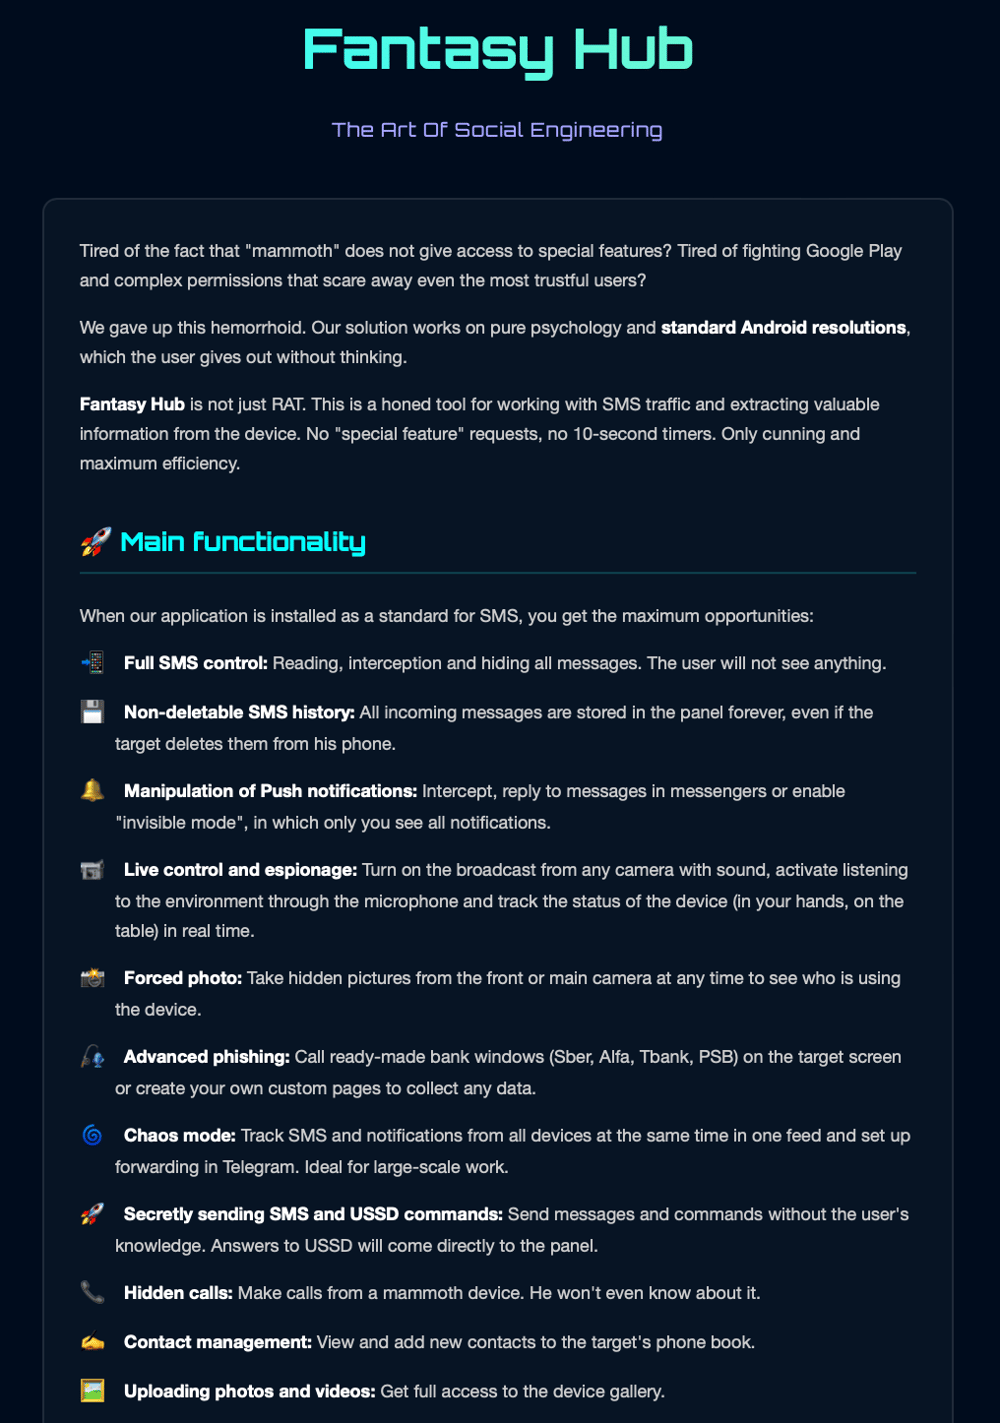
zLabs discovered “Fantasy Hub,” an Android Remote Access Trojan sold as Malware‑as‑a‑Service with documentation, builder bot, and instructions to create fake Google Play pages to deploy spyware and phishing windows targeting banks. The malware abuses default SMS handler privileges, uses a native dropper and WebRTC for live streaming, and has been observed targeting institutions including Alfa, PSB, Tbank, and Sber. #FantasyHub #Alfa #Sber
This report highlights a significant increase in malicious Android apps on Google Play, with over 40 million downloads and a 67% rise in mobile malware targeting users. Key threats include spyware, banking trojans, and adware, with attackers shifting toward social engineering tactics like phishing, smishing, and SIM-swapping to exploit mobile payments. #Anatsa #SpyNote
Google has released security updates for Android to fix two critical vulnerabilities, including one that could allow remote code execution without user interaction. These updates mark a shift from monthly patches, with the latest focusing on Android versions 13 to 16. #CVEs #AndroidSecurityVulnerabilities…
Google has rolled out Chrome 142 with patches for 20 vulnerabilities, some of which could be exploited for remote code execution. Google paid a total of $130,000 in bug bounties for the critical security fixes. #V8JavaScript #ChromeSecurity…
Cybersecurity Threat Research ‘Weekly’ Recap. A wide range of topics cover Tor-based SSH backdoors, supply-chain and dev-tooling compromises, cloud abuse and credential theft, active vulnerabilities and exploits, diverse malware families and ransomware trends, phishing and mobile propagation, botnets and anonymized infrastructure, APTs and regional campaigns, detection frameworks and risk management, and a large leak exposing Great Firewall internals.