Summary: Cellebrite, an Israeli company, has decided to cease licensing its mobile unlocking software to Serbia after allegations of misuse by Serbian authorities, including the illegal break-in of citizens’ phones. This decision follows an Amnesty International report that highlighted the use of Ce…
Tag: SPYWARE

This article discusses the ongoing cyber warfare between Russia and Ukraine, highlighting various attacks perpetrated by both sides against government entities, military targets, and human resources. It details significant events, cyber techniques, and implica…

Summary: Cybersecurity researchers have identified updates to the LightSpy implant, a modular spyware with expanded capabilities for data extraction from social media platforms like Facebook and Instagram. This updated version supports an extensive range of commands across multiple operating systems…

Summary: This week’s cyber news highlights a record-breaking .5 billion crypto theft linked to the Lazarus Group, the banning of ChatGPT accounts for malicious activities by OpenAI, and Apple’s withdrawal of its Advanced Data Protection feature in the UK. These incidents underscore the evolving land…
Summary: The head of Poland’s Central Anti-Corruption Bureau, Agnieszka Kwiatkowska-Gurdak, resigned amid criticism for allegedly withholding information during an investigation into widespread spyware abuse. The resignation follows accusations from the commission investigating these abuses that she…
Summary: A report by ESET reveals that freelance software developers, particularly in the cryptocurrency sector, have been targeted by North Korean hackers through a campaign known as DeceptiveDevelopment. The attackers employed fake job offers to distribute malware that enables them to exfiltrate s…
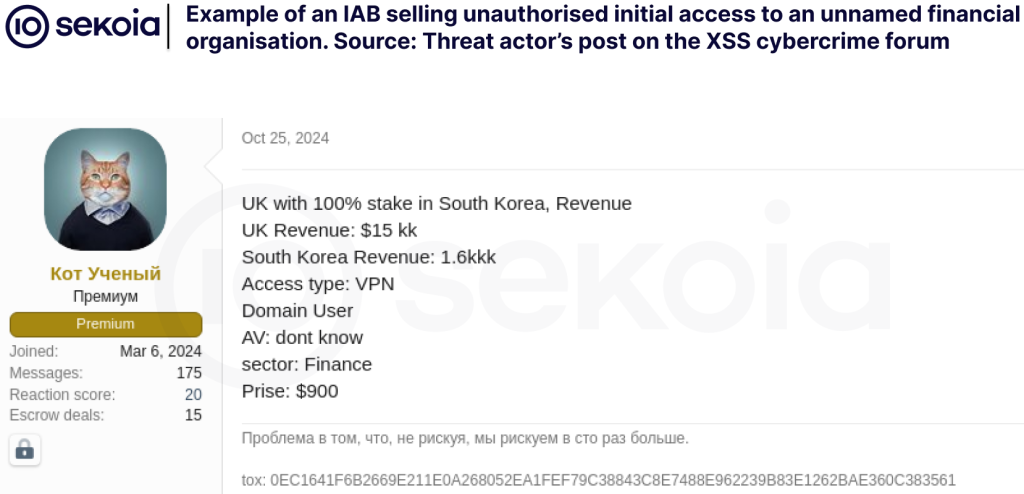
This report discusses the evolving landscape of cybercrime and state-sponsored threats targeting the financial sector, focusing on Initial Access Brokers (IABs), ransomware groups, and Trojan operators. It highlights the roles of various actors and techniques,…
Summary: Researchers have uncovered a hacking group, dubbed Green Nailao, targeting European healthcare organizations with spyware and ransomware, potentially linked to state-backed Chinese hackers. The campaign exploited a vulnerability in cybersecurity products, enabling unauthorized access to sen…
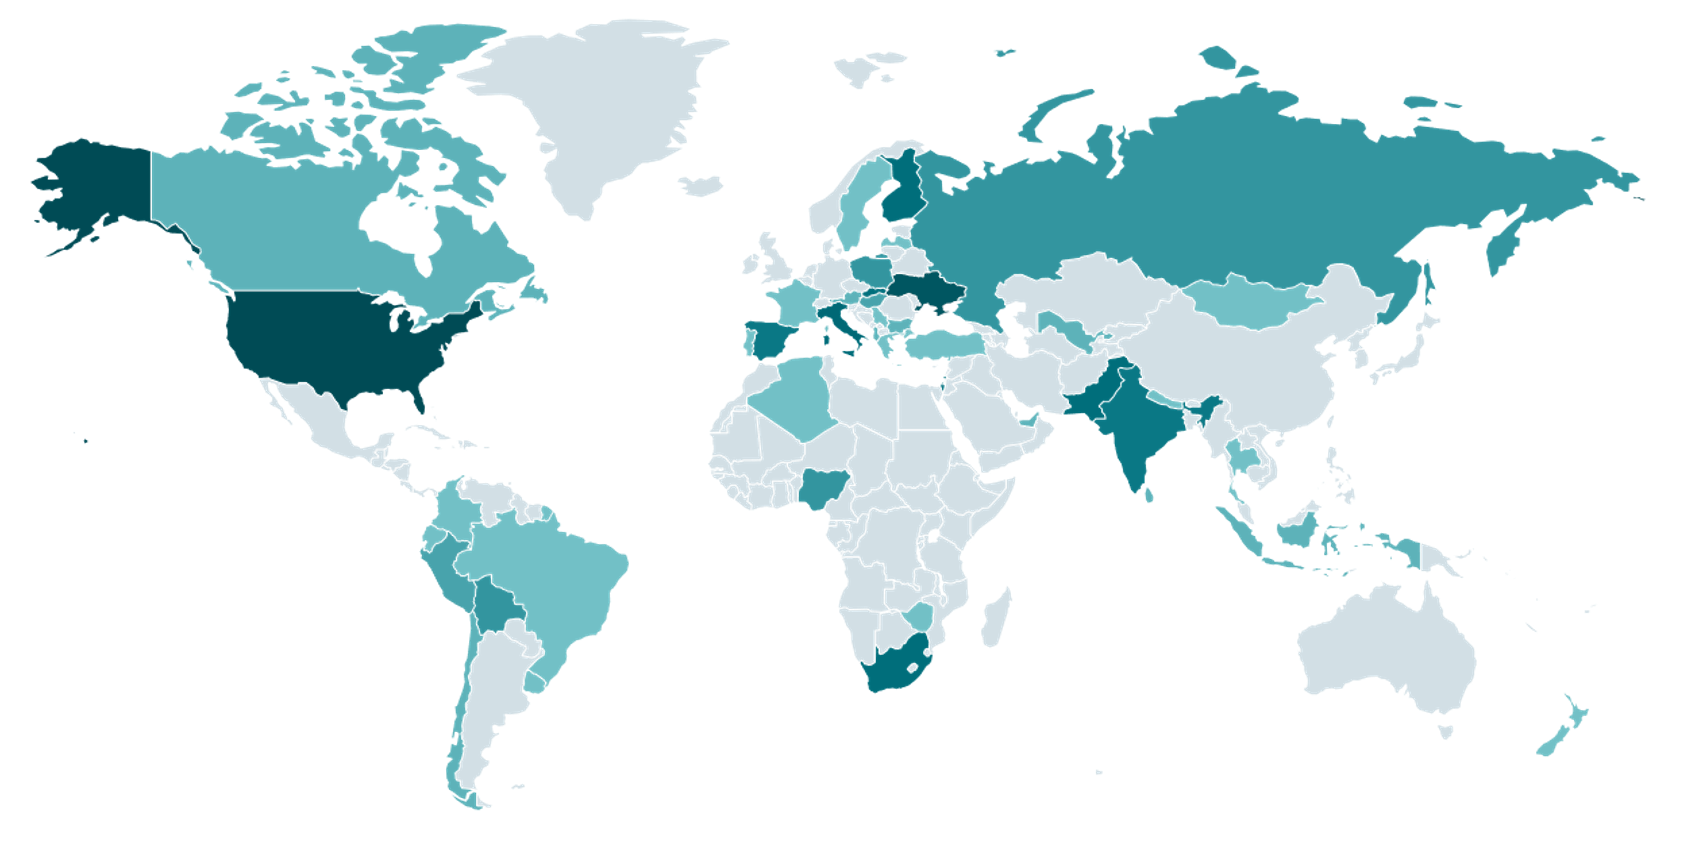
Cybercriminals, under the guise of recruiters, have targeted freelance software developers in a deceptive malware campaign named DeceptiveDevelopment. This campaign, linked to North Korea, has been promoting fake job offers that lead to the installation of mal…
Summary: New findings by iVerify reveal that zero-click Pegasus spyware is affecting a broader range of individuals, including business executives, not just members of civil society. During December alone, Pegasus was detected on 11 out of 18,000 tested devices. This alarming trend increases concern…

Summary: Israeli cybersecurity startup Dream has secured 0 million in Series B funding, bringing its total funding to 5 million and establishing a valuation of .1 billion. Founded in 2023, Dream focuses on enhancing cyber resilience for nations using AI-powered solutions designed to anticipate and e…
Summary: A new post-exploitation malware kit named PathLoader has been identified, targeting both Windows and Linux systems through Microsoft Outlook as a communication channel. It is associated with an espionage campaign labeled REF7707, which has previously attacked a South American nation’s Forei…

FIN7, also known as Carbon Spider, is a financially motivated cybercriminal group that has evolved from targeting Russian financial institutions to a wide range of sectors globally. They employ sophisticated techniques such as ransomware and malware for financ…

Zero-click exploits represent a dangerous form of cyberattack that allows hackers to infiltrate devices without any user interaction, posing significant threats to personal privacy and security. These attacks exploit vulnerabilities in various messaging apps a…
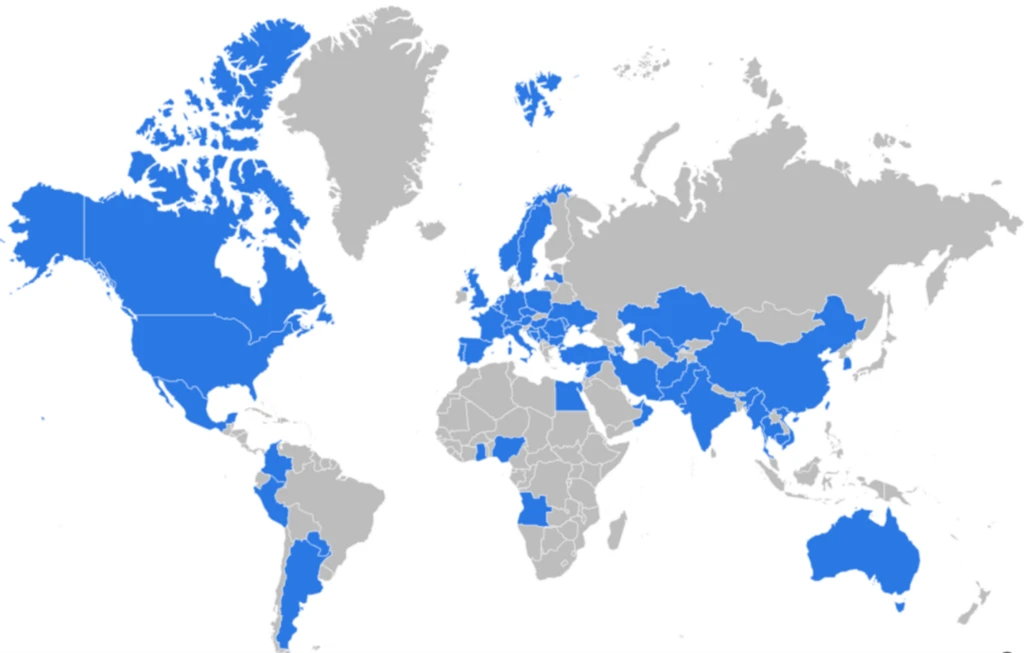
Microsoft has revealed insights into a subgroup of the Russian state actor Seashell Blizzard, known for its “BadPilot campaign.” This group has been active since at least 2021 and utilizes a variety of opportunistic access techniques to compromise global infra…