Keypoints
- Spetsvuzavtomatika leaked documents appear to come from a broad internal archive, not a single isolated system.
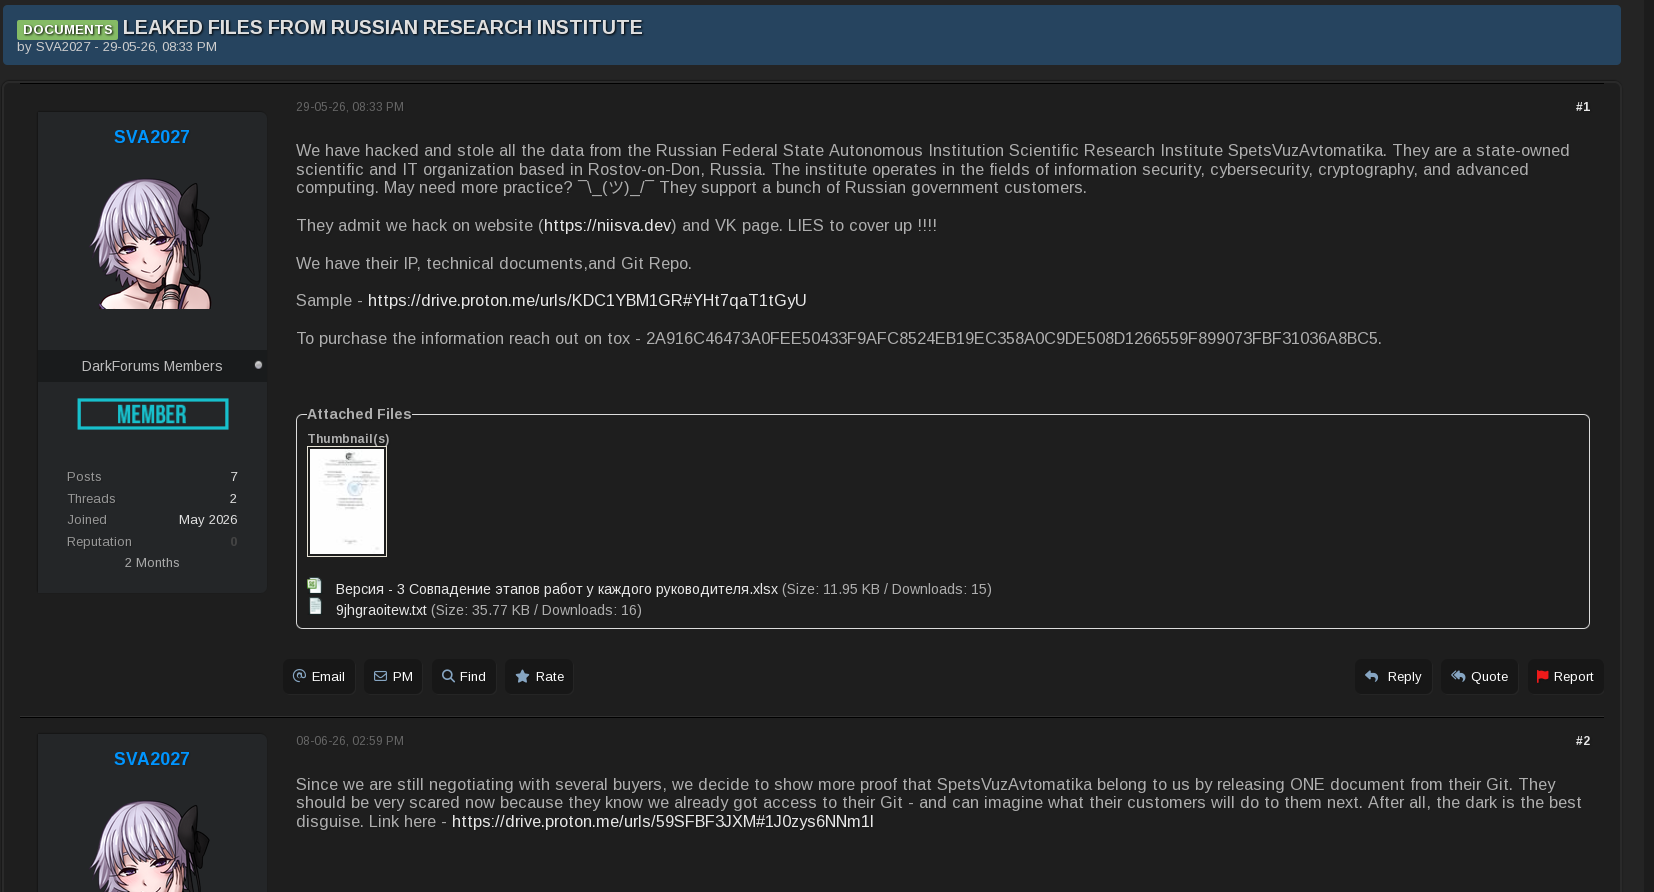
- The sale was advertised by the handle SVA2027 in May 2026 using forum posts, Proton Drive, and private negotiation via Tox.
- Evidence supports the authenticity of the leaked institute material, including matching filenames and consistent metadata.
- Felix-23 and HAD are reconnaissance and targeting platforms built for scanning, enrichment, testing, and campaign management.
- Putnik enables internal-network access, credential theft, lateral movement, and privilege escalation inside target environments.
- Initiative-24 focuses on cloud services for controlling agents and moving data out of corporate networks, while Botany, Blik, Glare, and Chain-24 cover Android collection, covert storage, and anonymous service procurement.
- The leak suggests a coordinated cyber-development ecosystem supporting automated intelligence collection and espionage operations.
MITRE Techniques
- [T1595 ] Active Scanning – Used to discover remote infrastructure, services, and targets through scanning and enrichment (‘target discovery, scanning, enrichment, and active testing’).
- [T1589 ] Gather Victim Identity Information – Collected and stored emails, machine names, personnel, contract numbers, and project codes to tie documents to the institute (’email addresses of individuals and machine names both in English and Cyrillic’).
- [T1110 ] Brute Force – Felix-23 was designed to test credentials and try brute-force attacks against targets (‘Test credentials’ ‘Try brute-force attacks’).
- [T1210 ] Exploitation of Remote Services – The platform was built to confirm and exploit vulnerabilities such as remote code execution and SQL injection (‘Check for remote code execution’ ‘Test SQL injection’).
- [T1078 ] Valid Accounts – Putnik and related workflows focused on credential theft and pass-the-hash use to access systems with reused credentials (‘credential theft’ ‘execute commands through pass-the-hash’).
- [T1021 ] Remote Services – Used TAP-mode VPN and tunneling to interact with internal networks as if locally connected (‘bridge Ethernet traffic so an outside operator can interact with the network as though locally connected’).
- [T1557 ] Adversary-in-the-Middle – Putnik scenarios included ARP spoofing, DHCP abuse, LLMNR/NBT-NS poisoning, and NTLM capture (‘ARP’ ‘DHCP’ ‘LLMNR and NBT-NS poisoning’ ‘NTLM capture’).
- [T1114 ] Email Collection – Initiative-24 examined cloud and email services for staging and transfer, including hidden Exchange folders (’email, virtual-machine, and serverless services’ ‘hidden Exchange folders’).
- [T1095 ] Non-Application Layer Protocol – Botany referenced multiple communications channels including SIP, WebRTC, torrent, and Matrix (‘HTTP, SIP, WebRTC, torrent… and Matrix communications’).
- [T1407 ] Download New Code in an Existing Module – Botany’s modular Android design supports interchangeable modules and background updates (‘interchangeable modules’ ‘support for background monitoring and updates’).
- [T1027 ] Obfuscated Files or Information – Blik and Glare hide protected data inside disguised apps and encrypted containers (‘camouflage application’ ‘protected ZIP or EPUB containers’).
- [T1105 ] Ingress Tool Transfer – The leak describes offline transfer and moving data into concealed containers for exchange (‘offline transfer’ ‘create, open, add files to, edit, or review the contents of a container’).
- [T1587 ] Develop Capabilities – The institute’s documents show research and development of tools, prototypes, and specialized hardware for cyber operations (‘turning intelligence and security-service requirements into software, operator procedures, prototypes, and specialized hardware’).
- [T1071 ] Application Layer Protocol – Initiative-24 leveraged trusted public cloud services to blend communications into normal business traffic (‘cloud platform services can be used for remote control… while blending into normal business traffic’).
- [T1090 ] Proxy – Felix-23 used proxies, TOR, and rotating IPs to conceal activity (‘TOR, proxies, distributed VPS nodes, rotating IP addresses’).
Indicators of Compromise
- [Handles / usernames ] threat actor or related account names – SVA2027, Spetsvuvatom
- [Project names ] leaked internal program names – Felix-23, HAD, Putnik, Initiative-24, Botany, Blik, Glare, Chain-24
- [Organizations / systems ] affected or referenced entities – Spetsvuzavtomatika, Proton Drive, DarkforumsRU
- [Accounts / infrastructure identifiers ] customer or operational references – Military Units 33949, 64829, niisva.org
- [File names ] referenced dump artifacts – 9jhgraoitew.txt, Const.kt, 6.pdf, project-management spreadsheet
- [Network data ] public IP inventory and ranges – 2,403 individual IPv4 addresses, three CIDR ranges, and 1,656 distinct /24 networks
- [External services / tools ] operational services referenced in the dump – Tox, Shodan, VirusTotal, WHOIS, Responder, Nettacker, BoNeSi