
A Chinese threat actor tracked as UTA0560 used spear-phishing and a Chrome-Windows exploit chain to deliver the GRIMWEDGE JavaScript backdoor to NGOs. Around the same time, JungleBamboo (APT31) used the same chain to deploy SUPERSTOMP and the LONGTALE credential-stealing Chrome extension. #UTA0560 #GRIMWEDGE #JungleBamboo #APT31 #LONGTALE #SUPERSTOMP #Chrome #Windows #BlueMoon…

Cisco has warned that CVE-2026-76461 is being actively exploited in Cisco Secure Email Gateway, allowing unauthenticated attackers to run commands as root by sending a crafted email. The disclosure also follows reports of large-scale credential attacks against Fortinet VPN appliances, prompting CISA to add the Cisco flaw to its KEV catalog…
Cisco warned that CVE-2026-76461, a critical zero-day in Secure Email Gateway appliances, is being actively exploited in the wild and can let attackers run commands as root through a specially crafted email. CISA has added the flaw to its KEV catalog and ordered federal agencies to patch it, while Cisco released…
Acronis TRU uncovered Red Heron, a Chinese-speaking threat actor that rapidly weaponized CVE-2026-60004 against internet-facing Gitea servers to steal source code, collect credentials, and gain deeper access into victim environments. The exposed staging server revealed JITTERLY and the embedded SIXZUT rootkit, showing a campaign that moved from repository theft to persistence and lateral movement across systems like Proxmox, Synology NAS, and compromised Gitea instances. #RedHeron #CVE-2026-60004 #Gitea #JITTERLY #SIXZUT #Proxmox #Synology

Winston Contracting, LLC in the US reported a ransomware incident attributed to the qilin threat actor. The attack resulted in data disruption and encryption-related impacts for the organization. #UnitedStates
Better Accounting Solutions, impacted by the Anubis ransomware threat actor, faced a Wall Street accountants data breach involving unauthorized access and extortion. The impacted country(s) is/are: #countryname
Geieg, located in ES, was impacted by ransomware attributed to threat actor qilin. The incident resulted in encrypted or disrupted data and demands for ransom, affecting #Spain.
Homebrew 7.0.0 closes eight security advisories, including a High-severity flaw that could let unsigned cask removal metadata run commands with sudo and a Moderate issue involving LaunchServices sandbox escape. The release also adds built-in vulnerability scanning with brew vulns, expands provenance checks, and tightens sandboxing across macOS and Linux. #Homebrew #LaunchServices #OSV.dev

The Supreme Court rejected the Trump administration’s petition to change how the U.S. Postal Service handles mail-in ballots for the 2026 midterm elections, calling the effort “arbitrary and capricious.” The ruling blocks a USPS rule that would have added voter citizenship checks, barcode tracking for ballot envelopes, and DHS-based “State Citizenship Lists” amid claims of rushed implementation and legal overreach. #USPS #TrumpAdministration #JusticeKetanjiBrownJackson #JusticeBrettKavanaugh #JusticeSamuelAlito #JusticeClarenceThomas #DepartmentOfHomelandSecurity
Cybercriminals have built more than 360 fake government and news websites to scam people in Uzbekistan, Belarus, and Tajikistan with promises of cash payments or passive income. The campaign tricks victims into sharing contact details, installing malicious apps, and providing passport scans, enabling fraud, device compromise, and identity theft. #F6 #Uzbekistan…
Researchers say the pro-Ukraine hacktivist group Hacking Cat has moved from defacements and leaks to more destructive attacks on Russian targets, using custom tools like Gorilla RAT and Monkey Ransomware. Kaspersky also found overlaps with other Ukraine-linked groups and noted that shared malware and infection chains make attribution difficult. #HackingCat #GorillaRAT…
Five alleged members of the Black Axe cybercriminal organization will appear in U.S. court after extradition from South Africa, facing wire fraud and money laundering charges tied to romance scams that targeted more than 100 victims. Prosecutors say the Cape Town branch, led by Perry Osagiede, used fake identities, dating sites,…
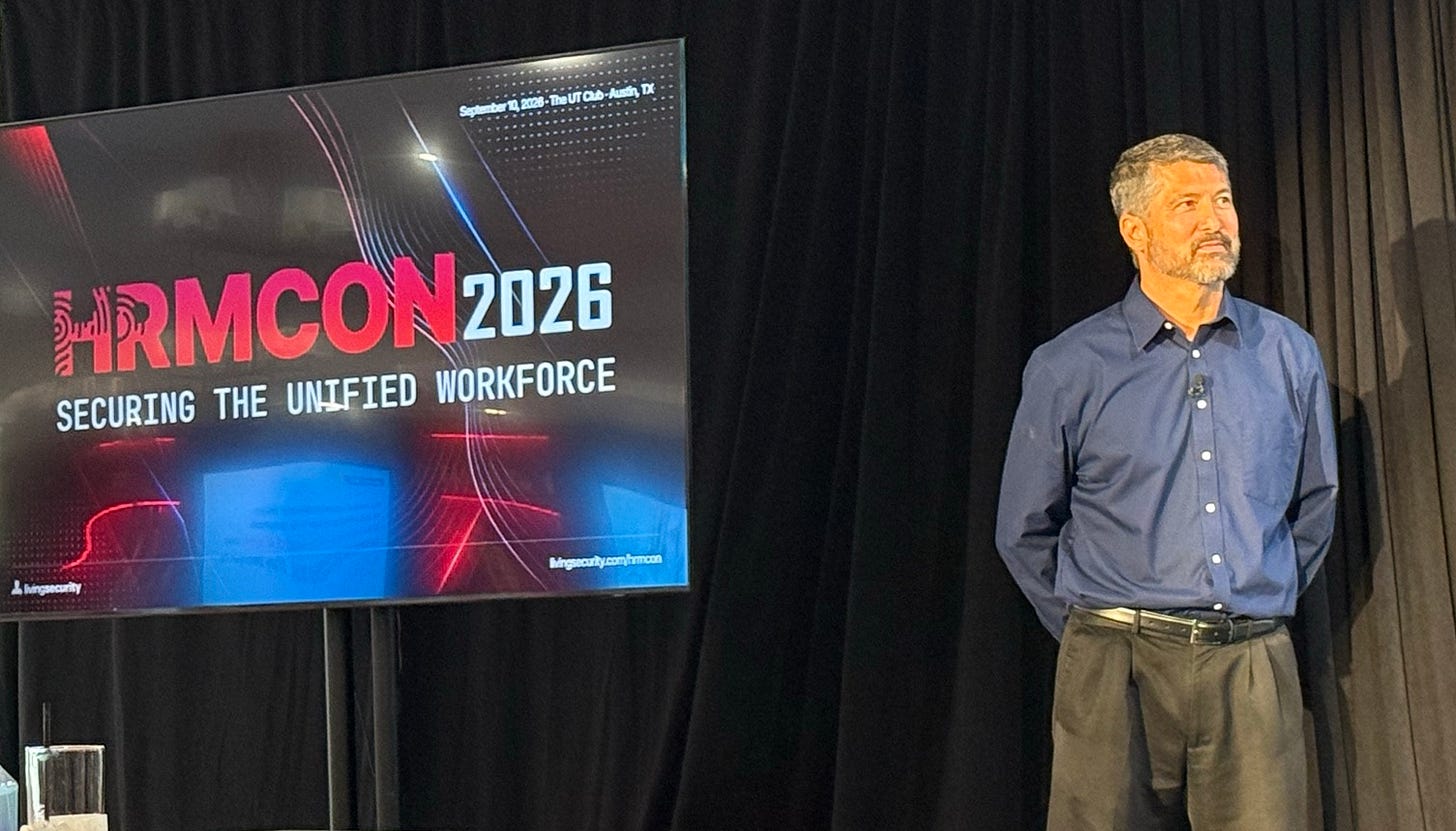
The Human Risk Management conference in Austin brought together experts to discuss the evolving cybersecurity risks created by both human and AI behaviors. The event highlighted practical guidance for adapting to artificial intelligence across technology, business, government, and academic environments, with thanks to Living Security and the speakers who contributed. #LivingSecurity #AustinTexas #AshleyRose #EdnaConway #SumonaBanerji
HandyTrac in Litchfield Park, AZ (US) has been targeted by the ransomware group ShadowByt3$, with claims that stolen sensitive data includes Physical-to-Digital Key Maps, property intelligence/vulnerability logs, employee identity & credential data, financial/vendor records, and administrative portal control. The threat actor alleges the data will be leaked unless negotiation occurs within 72 hours, and proof is referenced on a provided onion URL. #unitedstates
Veritiv in the United States reported a ransomware incident attributed to threat actor iah6477, involving approximately 1.9 TiB of affected data. The impacted country is #UnitedStates