Community Property Management (US) reported a ransomware incident involving the dragonforce threat actor, with full data impact reported at 200+ GB. #UnitedStates

Aarsleff in Sweden was hit by ransomware attributed to the qilin threat actor, resulting in disruption and potential encryption of data. The impacted country is #Sweden

FortiGuard Labs identified Evooo1Bot, a previously undocumented Linux botnet that repurposes Mirai’s DDoS engine while adding encrypted C2, credential theft, SOCKS relay, SSH brute forcing, and a multi-vulnerability exploit framework. Active since July 2026, it targets Internet-facing devices through a loader hosted at 91.92.40[.]118 and uses campaigns against products from Alcatel, NETGEAR, Tenda, Mitsubishi Electric, D-Link, Telesquare, Hikvision, and others. #Evooo1Bot #Mirai #FortiGuardLabs #Alcatel #NETGEAR #Tenda #MitsubishiElectric #DLink #Telesquare #Hikvision

UltraViolet Cyber has launched Equinox, an AI- and automation-driven detection engineering platform that maps customer telemetry and detections against MITRE ATT&CK and MITRE ATLAS to identify coverage gaps quickly. The platform helps SOC teams validate what actually works against their data, improve detection coverage without raising alert volume, and strengthen defense for both traditional and AI-targeted threats. #UltraVioletCyber #Equinox #MITREATTACK #MITREATLAS #TIDE
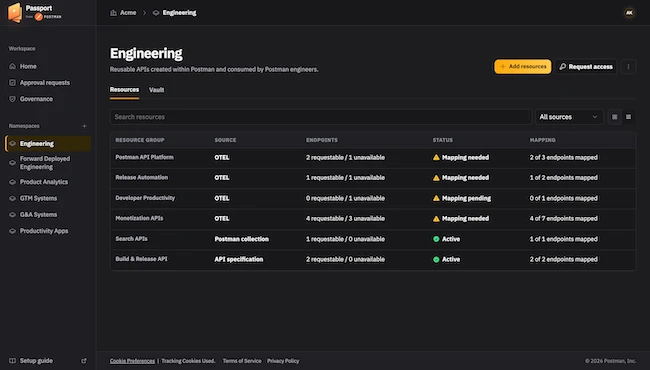
Postman has launched Passport by Postman as a standalone API security product, giving organizations secretless access to approved APIs for both human users and AI agents. The platform keeps real API credentials inside customer environments while providing granular control, full attribution, and fast revocation to reduce exposure from leaked secrets. #Postman #PassportbyPostman #AbhinavAsthana

Acronis has disclosed CVE-2026-87886, a high-severity Linux local privilege escalation flaw in its backup plugins for cPanel & WHM and Plesk. The company says the issue has been exploited in limited, targeted attacks in the wild, and urges affected users to patch immediately. #CVE-2026-87886 #Acronis #cPanel #WHM #Plesk

Researchers uncovered BambooToken, a multi-platform malware campaign that uses MQTT for command-and-control to target Windows and Linux systems across Asia and South America. The campaign appears to rely on DLL sideloading through Tendyron OnKey software, with infrastructure and targeting suggesting extensive data collection and possible China-linked activity. #BambooToken #Tendyron #OnKey #MQTT…

U.S., U.K., and Dutch agencies say an Iran-linked Windows malware campaign known as HEAVYGRAM and CHOSEN BRICK is used to spy on dissidents, journalists, and activists by stealing messages, screenshots, passwords, and audio. The malware spreads through deceptive files, uses Telegram for command and data theft, and has indicators tied to…

Researchers uncovered KREMLIN, a previously undocumented Brazilian banking malware operation tracked as REF9334 that uses fake bank lures, malicious browser extensions, and multi-stage loaders to steal credentials and session data. The campaign hides its infrastructure with Ethereum smart contracts, and Elastic observed 1,515 infected systems checking into a network canary domain,…
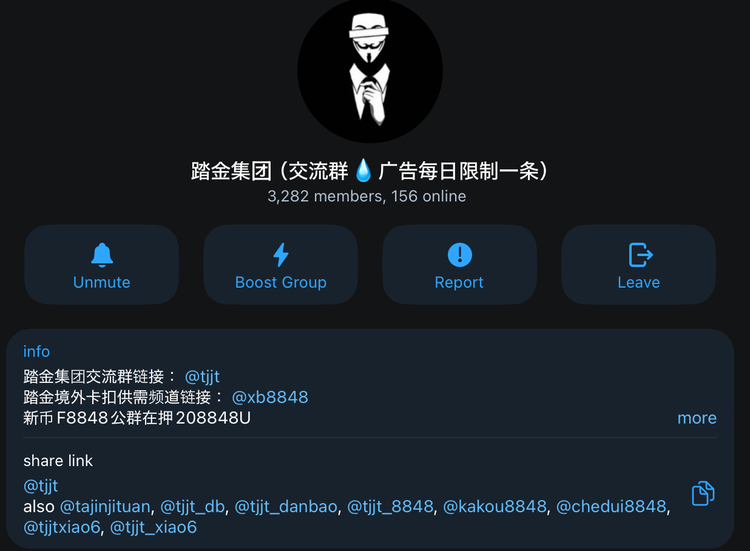
Tajin Group is a Chinese-speaking threat group that uses Telegram-based guarantee marketplaces, Fragment Market, and multiple payment gateways to run phishing, carding, money laundering, and cash-out operations across many countries. The group has shifted from Dabai Guarantee to Xinbi Guarantee, while buying Telegram usernames and anonymous numbers to improve OPSEC and expand its financial crime services. #TajinGroup #DabaiGuarantee #XinbiGuarantee #FragmentMarket #CCAvenue #Geidea #NGenius #Selfridges #ChowTaiFookJewelleryHongKong

A unified dashboard does not always mean a unified incident workflow, so the article recommends testing one real incident end to end to measure console switches, handoffs, containment, and clean recovery. It highlights Acronis Cyber Protect as a platform that combines security, backup, recovery, and endpoint management, and says buyers should verify six practical workflow tests before trusting consolidation claims. #AcronisCyberProtect #AcronisCyberProtectCloud #EDR #XDR #KasperskyEDR #EICAR
F5 has enhanced Distributed Cloud Bot Defense with persistent device intelligence and agentic AI protections to help organizations distinguish trusted users and AI agents from malicious automation. The updates use continuous risk decisioning and multi-signal telemetry to stop fraud, account abuse, and disruptive bot activity without blocking legitimate digital interactions. #F5 #DistributedCloudBotDefense #F5ADSP #AgenticAI
Attackers are exploiting CVE-2026-76461, a critical zero-day in Cisco Secure Email Gateway that allows unauthenticated remote command execution with root privileges. Cisco says it has seen active exploitation and has contacted affected cloud customers, while CISA quickly added the flaw to its Known Exploited Vulnerabilities catalog. #Cisco #CVE-2026-76461 #CiscoSecureEmailGateway #CiscoAsyncOS #CISA
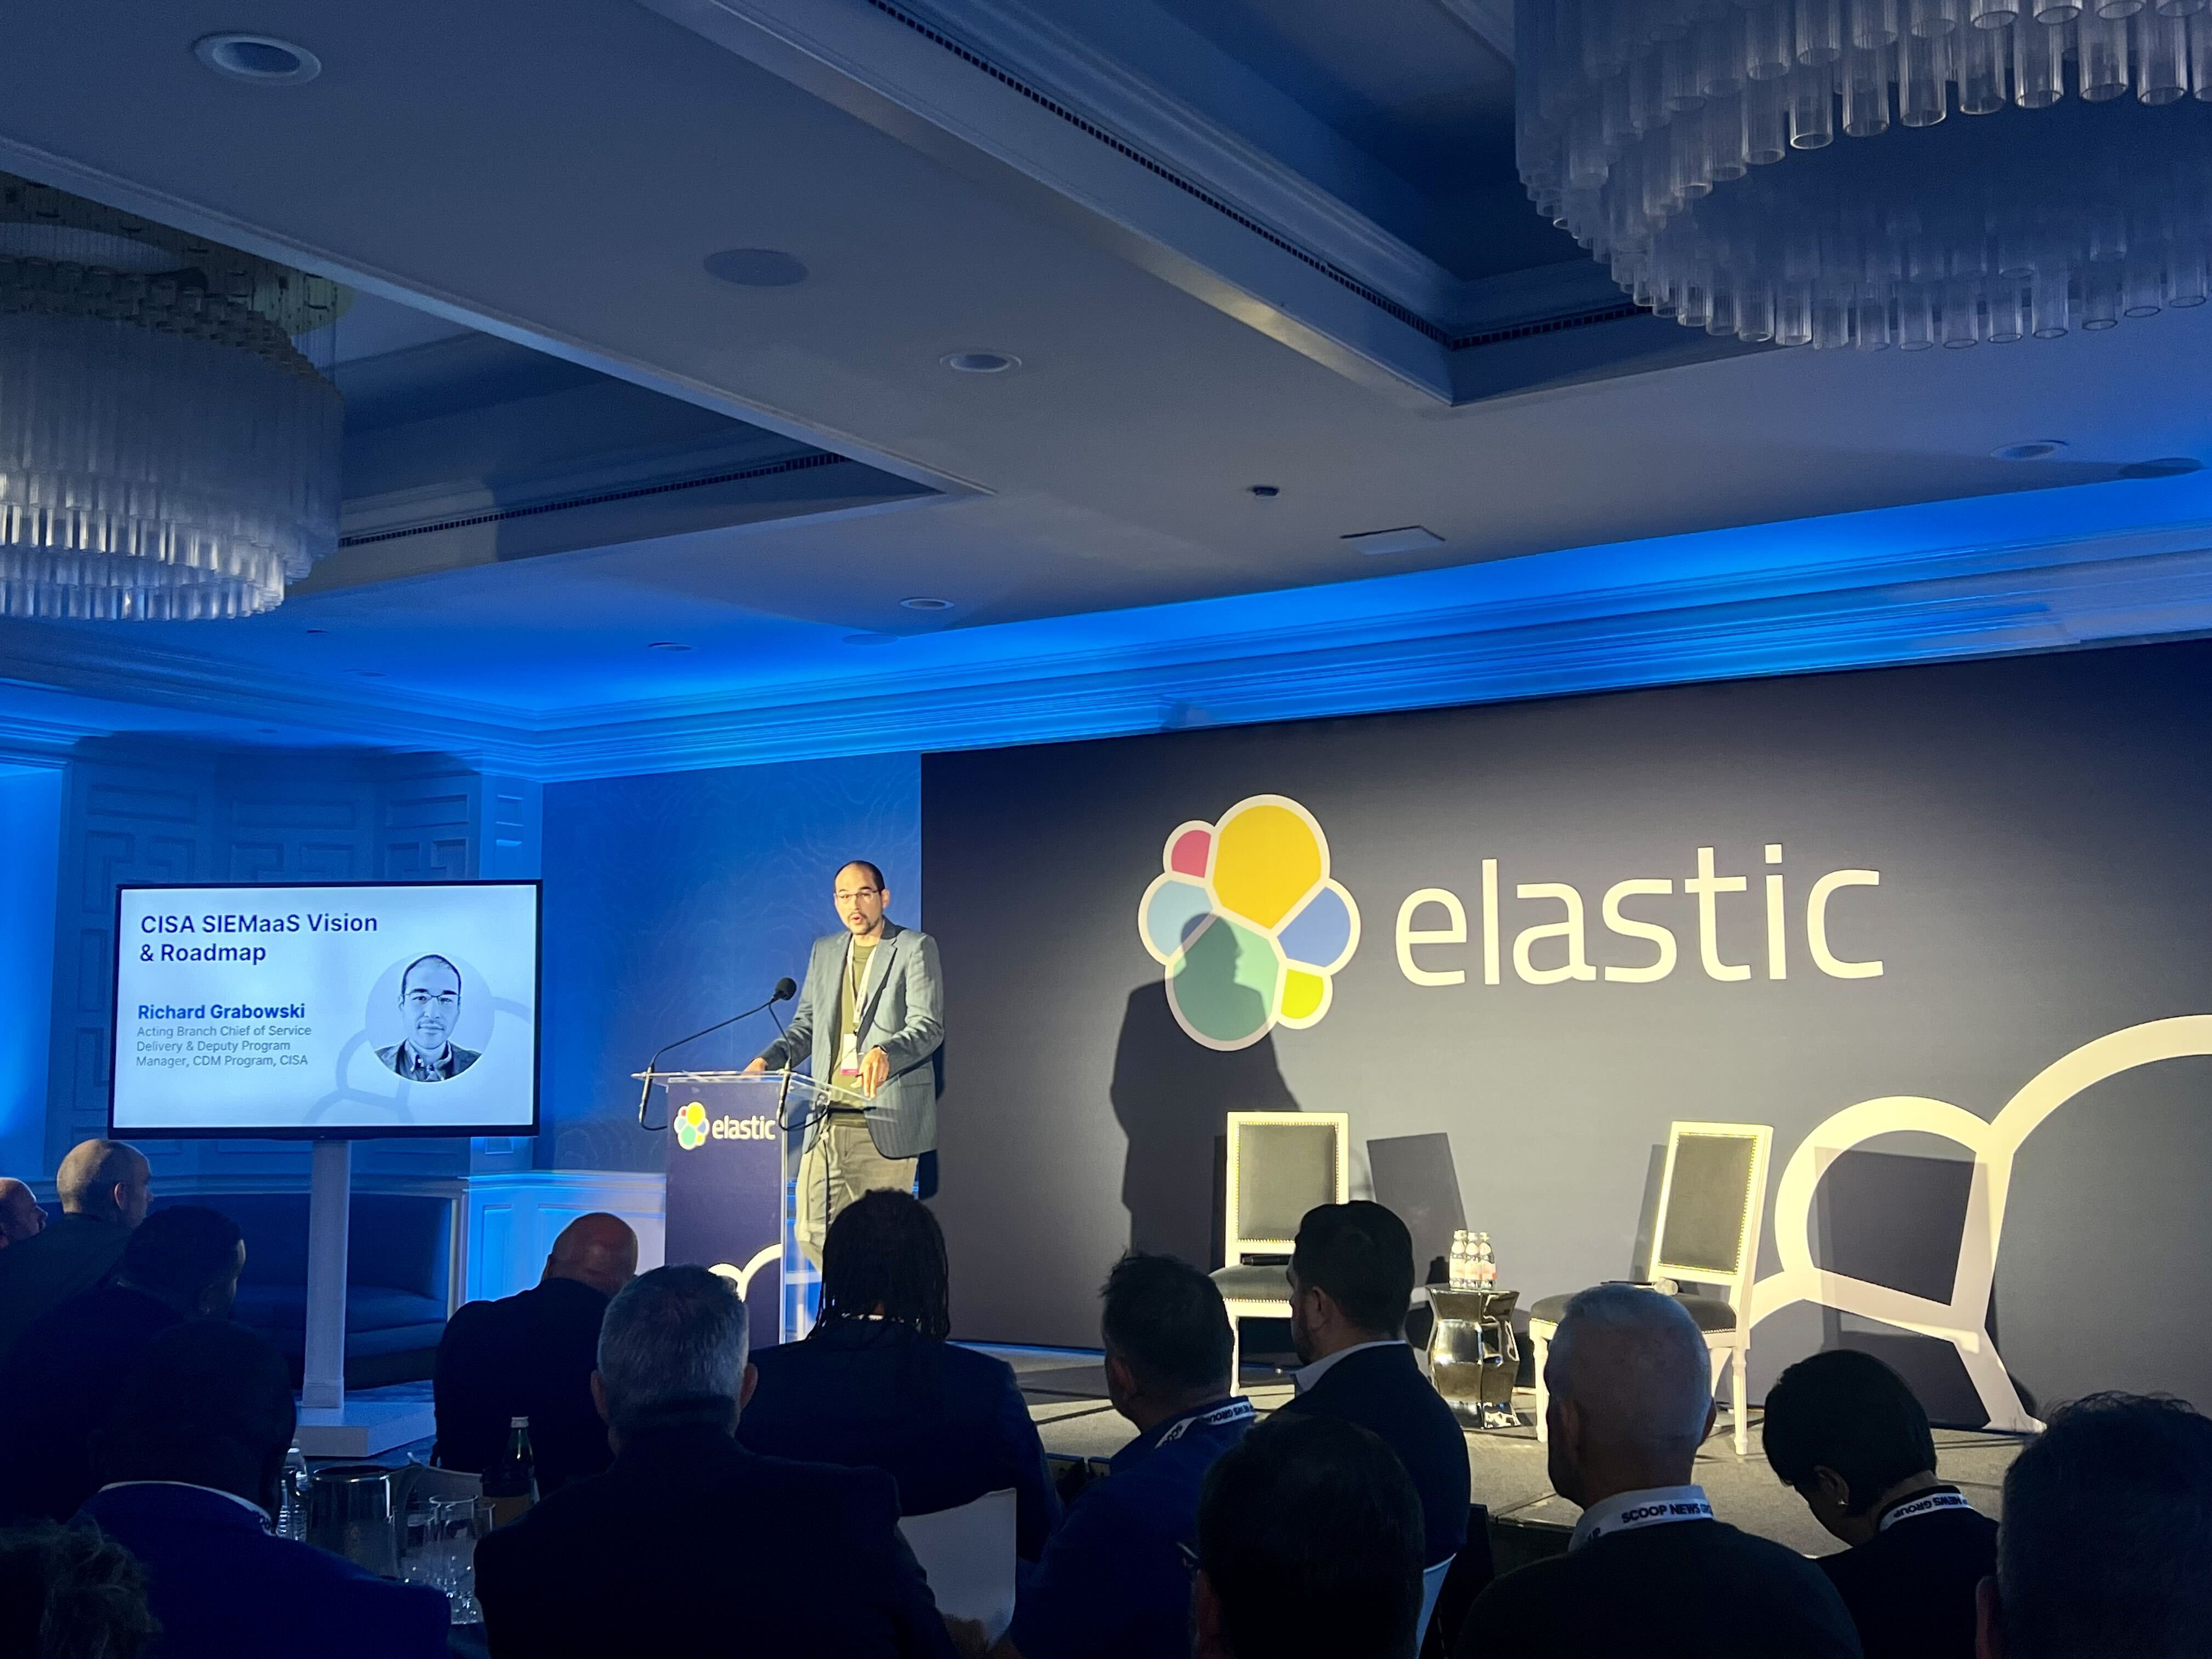
CISA’s Continuous Diagnostics and Mitigation (CDM) program is being pushed to move faster by expanding automation, improving unification, and strengthening data-driven risk management across federal agencies. Officials also said CDM’s evolution has been shaped by the SolarWinds breach, which exposed the need for a common operating picture and better government-wide visibility. #CISA #ContinuousDiagnosticsAndMitigation #SolarWinds

A Swiss court has sentenced a 52-year-old Ukrainian ransomware developer to 12 years and nine months in prison for helping power LockerGoga, MegaCortex, and Nefilim operations. The case is tied to attacks on Stadler Rail, Meier Tobler, and Crealogix, while alleged mastermind Volodymyr Tymoshchuk remains on the FBI’s most wanted list. #LockerGoga #MegaCortex #Nefilim #StadlerRail #VolodymyrTymoshchuk