
AI agents are inherently unpredictable, so security should focus on the credentials, tools, and enterprise systems they can actually reach rather than trying to enumerate every possible action. The article argues for mapping agent blast radius, reducing local secret exposure, and enforcing controls at the moment credentials are accessed to limit damage from tools like Cursor, MCP, AWS IAM, Microsoft Entra, and Okta. #Cursor #MCP #AWSIAM #MicrosoftEntra #Okta #GitGuardian

Optimum First Mortgage (Pear’s acting group’s promotional blog) in the USA reported a ransomware claim by blacknevas involving the alleged theft and encryption of approximately 9.3TB of financials, HR, clients’ private data, PII/PHI, email correspondence/mailboxes, database exports, and OneDrive-stored data. The threat actor is said to have leveraged access via dark-web download links for optimumfirst.com. #UnitedStates
RDA MOTORS S.P.A., an Italian premium car company, reportedly experienced a ransomware attack attributed to threat actor emperador, resulting in the compromise of customer documents and employee data. The incident involved 7.3 GB of data across Technology and other sectors and impacted Italy #Italy
HandyTrac Greystar AZ (US) claims ransomware activity by Threat Actor “ShadowByt3$,” stating they locked out management and staff and are extending negotiations to September 22, 2026 at 3:00pm while possessing key maps/reports, property intelligence and vulnerability logs, employee credential data, financial/vendor records, and administrative portal control. The claim includes “proof of lockout” imagery and asserts the attacker disabled systems and data, with the impacted country listed as #UnitedStates.
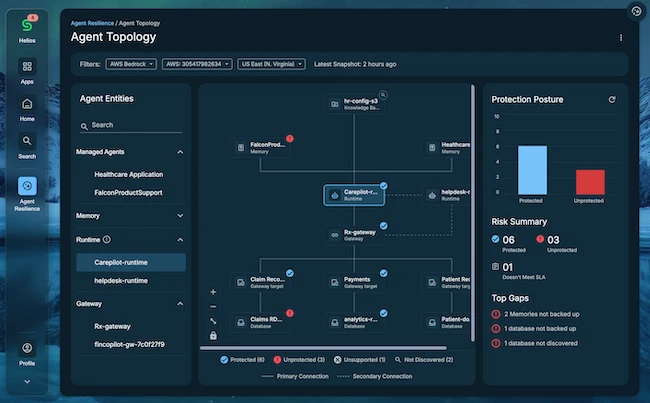
Cohesity has launched Agent Resilience to discover, protect, and recover the infrastructure behind enterprise AI agents, closing a critical gap when agent actions corrupt or change systems. The company also unveiled its vision for Autonomous Cyber Resilience and a free AI Resilience Academy course to help organizations manage the risks of AI agents as they move from advising to acting. #Cohesity #CohesityAgentResilience #AutonomousCyberResilience #CohesityDataCloud #AmazonBedrock #CohesityRecoveryAgent #CohesityMaestro #CohesityGaiaCatalog
Ursula von der Leyen urged frontier AI development to slow down, warning that upcoming models could enable hacking at an unprecedented level and that self-improving systems may pose growing security risks. She said the EU will work with Canada, the U.K., and other partners on model evaluation, verification, early warning, and AI security, while also pushing AI use across key sectors like health, transport, agrifood, manufacturing, and defense. #UrsulaVonDerLeyen #EuropeanCommission #AIAct #CETA #HuggingFace
CISA has released new guidance encouraging critical infrastructure operators to use cyber decoys, such as fake systems, accounts, and data, to detect and distract intruders already inside their networks. The 22-page guide explains how honeytokens and other decoy techniques can support zero-trust and assume-compromise defenses at low cost. #CISA #CyberDecoys #Honeytokens

Daily Recap, Cisco patched an actively exploited Secure Email Gateway zero-day that enables command execution as root, while China-linked actors chained a Chrome-Windows zero-day to deploy GRIMWEDGE. Attackers also targeted WooCommerce/WordPress via a third-party plugin, abused exposed Vite dev servers for AWS/Azure secrets, and leveraged a Telegram Desktop HTML export flaw to exfiltrate messages, alongside ongoing ransomware exploitation of a VMware vCenter RCE flaw.
#Cisco #GRIMWEDGE #WooCommerce #WordPress #Vite #AWS #Azure #TelegramDesktop #VMwarevCenter #ClickFix #PasteSwitch #DDROP #BlackAxe
The Spanish Data Protection Agency (AEPD) was notified of a breach allegedly carried out by an AI agent using a known large language model, which autonomously searched for vulnerabilities, logged into systems, and accessed personal and financial data. The incident underscores how AI can speed up, scale, and adapt attacks, prompting a review of identity security, response procedures, and data protection models. #AEPD #OpenAI #HuggingFace #GoogleGemini #AnthropicClaude
A banking malware campaign active since mid-2025 has used the KREMLIN toolkit to silently install malicious Chrome and Edge extensions that steal credentials, session tokens, and browser data. Elastic Security Labs linked the operation to a Brazilian threat actor, confirmed 1,515 infected systems, and disrupted part of the campaign by registering a key anti-sandbox domain. #KREMLIN #ElasticSecurityLabs #REMCOS #PulsarRAT #Brazil
Government agencies warn that Iranian state-linked hackers are using CHOSEN BRICK to spy on dissidents, activists, and journalists by stealing messages, screenshots, and audio. The malware is spread through social engineering on WhatsApp and Telegram, hides with Windows persistence, and sends stolen data through Telegram and cloud services. #CHOSENBRICK #Iranian #Telegram #WhatsApp #FBI
Microsoft is investigating reports that the Windows 11 KB5124008 security update is breaking domain trust relationships on some enterprise systems, causing valid domain credentials to fail after reboot. Administrators say the issue appears linked to the Machine Identity Isolation feature in Windows 11 25H2, with some systems recovering after disabling it and repairing the secure channel. #Microsoft #Windows11 #KB5124008 #MachineIdentityIsolation #ActiveDirectory
Zscaler reports that APT36 ran Operation RapidRust in August 2026, targeting government and defense organizations in India and Afghanistan with new tooling including RUSTYSHADE, RUSTYMOVE, PSNATCH, and BASHNATCH. The campaign used private GitHub repositories, typosquatted Indian media domains, and Backblaze-hosted payloads to enable encryption, exfiltration, persistence, and USB-based propagation. #APT36 #RUSTYSHADE #RUSTYMOVE #PSNATCH #BASHNATCH #GitHub #Backblaze
Wise IT (wiseit.com.ua), a Kyiv-based Ukrainian system integrator, was targeted by AuditTeam ransomware, resulting in disruption to its IT services. The incident is attributed to the threat actor AuditTeam and impacts Ukraine. #Ukraine
AuditTeam ransomware claimed to have compromised palletshop (palletshop.ru) in Russia and exfiltrated sensitive information. The claim indicates disruption and potential further harm to the victim in #Russia