
Qilin ransomware targeting Invincible GG involved unauthorized access and encryption of files to extort payment. The attack’s impacted country is #N/A
Brevo confirmed that attackers stole a Cloudflare API key and used a malicious Cloudflare Worker to inject ClickFix scripts into Brevo pages and customer-embedded JavaScript for several hours on September 14. The compromise also pushed a fake WordPress plugin called “Web Media Optimizer” to some sites, while Brevo says its core app, API, email delivery systems, and customer account data were not affected. #Brevo #Cloudflare #ClickFix #WebMediaOptimizer #WordPress
Two oil tankers bound for Texas were boarded by US Coast Guard and FBI personnel after cyberattacks disrupted onboard systems during their voyage. Investigators found evidence of a malicious cyber actor aboard the VL Prosperity and are still determining whether Iran or another state actor was responsible. #VLProsperity #USCoastGuard #FBI #Iran…
Authorities seized the primary domain and related sites of NightmareStresser, a long-running DDoS-for-hire service that had enabled hundreds of thousands of attacks since at least 2022. The takedown, part of Operation PowerOFF, highlights ongoing efforts by the FBI and Royal Canadian Mounted Police to disrupt booter services, though similar networks may quickly replace it. #NightmareStresser #OperationPowerOFF #FBI #RoyalCanadianMountedPolice
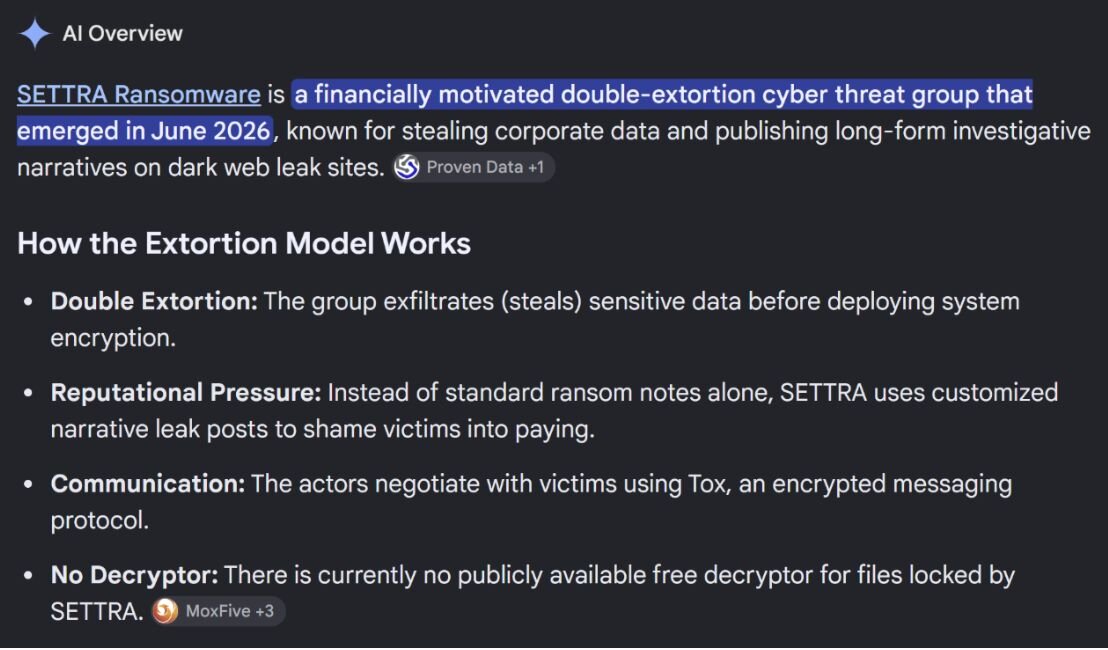
Huntress observed two Settra ransomware incidents, one in July and one in September, affecting organizations in consumer services and retail and in manufacturing. The attackers used MeshAgent RMM, attempted to hide their activity, and in one case showed evidence of BYOVD while also disabling recovery options and clearing Windows Event Logs. #Settra #MeshAgent #gdrvsys #RESTOREFILES
The FBI has seized the domains of NightmareStresser, one of the longest-running DDoS-for-hire platforms, as part of Operation PowerOFF. The service allegedly enabled hundreds of thousands of attacks worldwide using rented botnets and IoT devices, and previous actions have already disrupted other booter services and arrested multiple suspects. #NightmareStresser #OperationPowerOFF #FBI
Microsoft warned that Windows 11 24H2 Home and Pro editions will stop receiving updates on October 13, 2026, and urged users to move to Windows 11 25H2. Enterprise and Education editions of Windows 11 24H2 remain supported until October 2027. #Windows11 #Windows1124H2 #Windows1125H2
Google Threat Intelligence Group reported that AI is rapidly lowering the cost and time needed for credential theft, including a campaign that compromised thousands of third-party credentials in under six hours. The article warns that strong password hygiene is not enough on its own and emphasizes device trust as a critical defense against AI-enabled abuse of stolen credentials. #GoogleThreatIntelligenceGroup #SpecopsPasswordAuditor #SpecopsDeviceTrust #Unit42 #Microsoft

Hackers are demanding $3 million from Revolut after using fake government requests over several months to siphon customer data, including passports, email addresses, phone numbers, and financial information. The campaign is linked to the compromised account of an Italian government employee and reportedly affected around 680 Revolut customers, while Italy’s police…
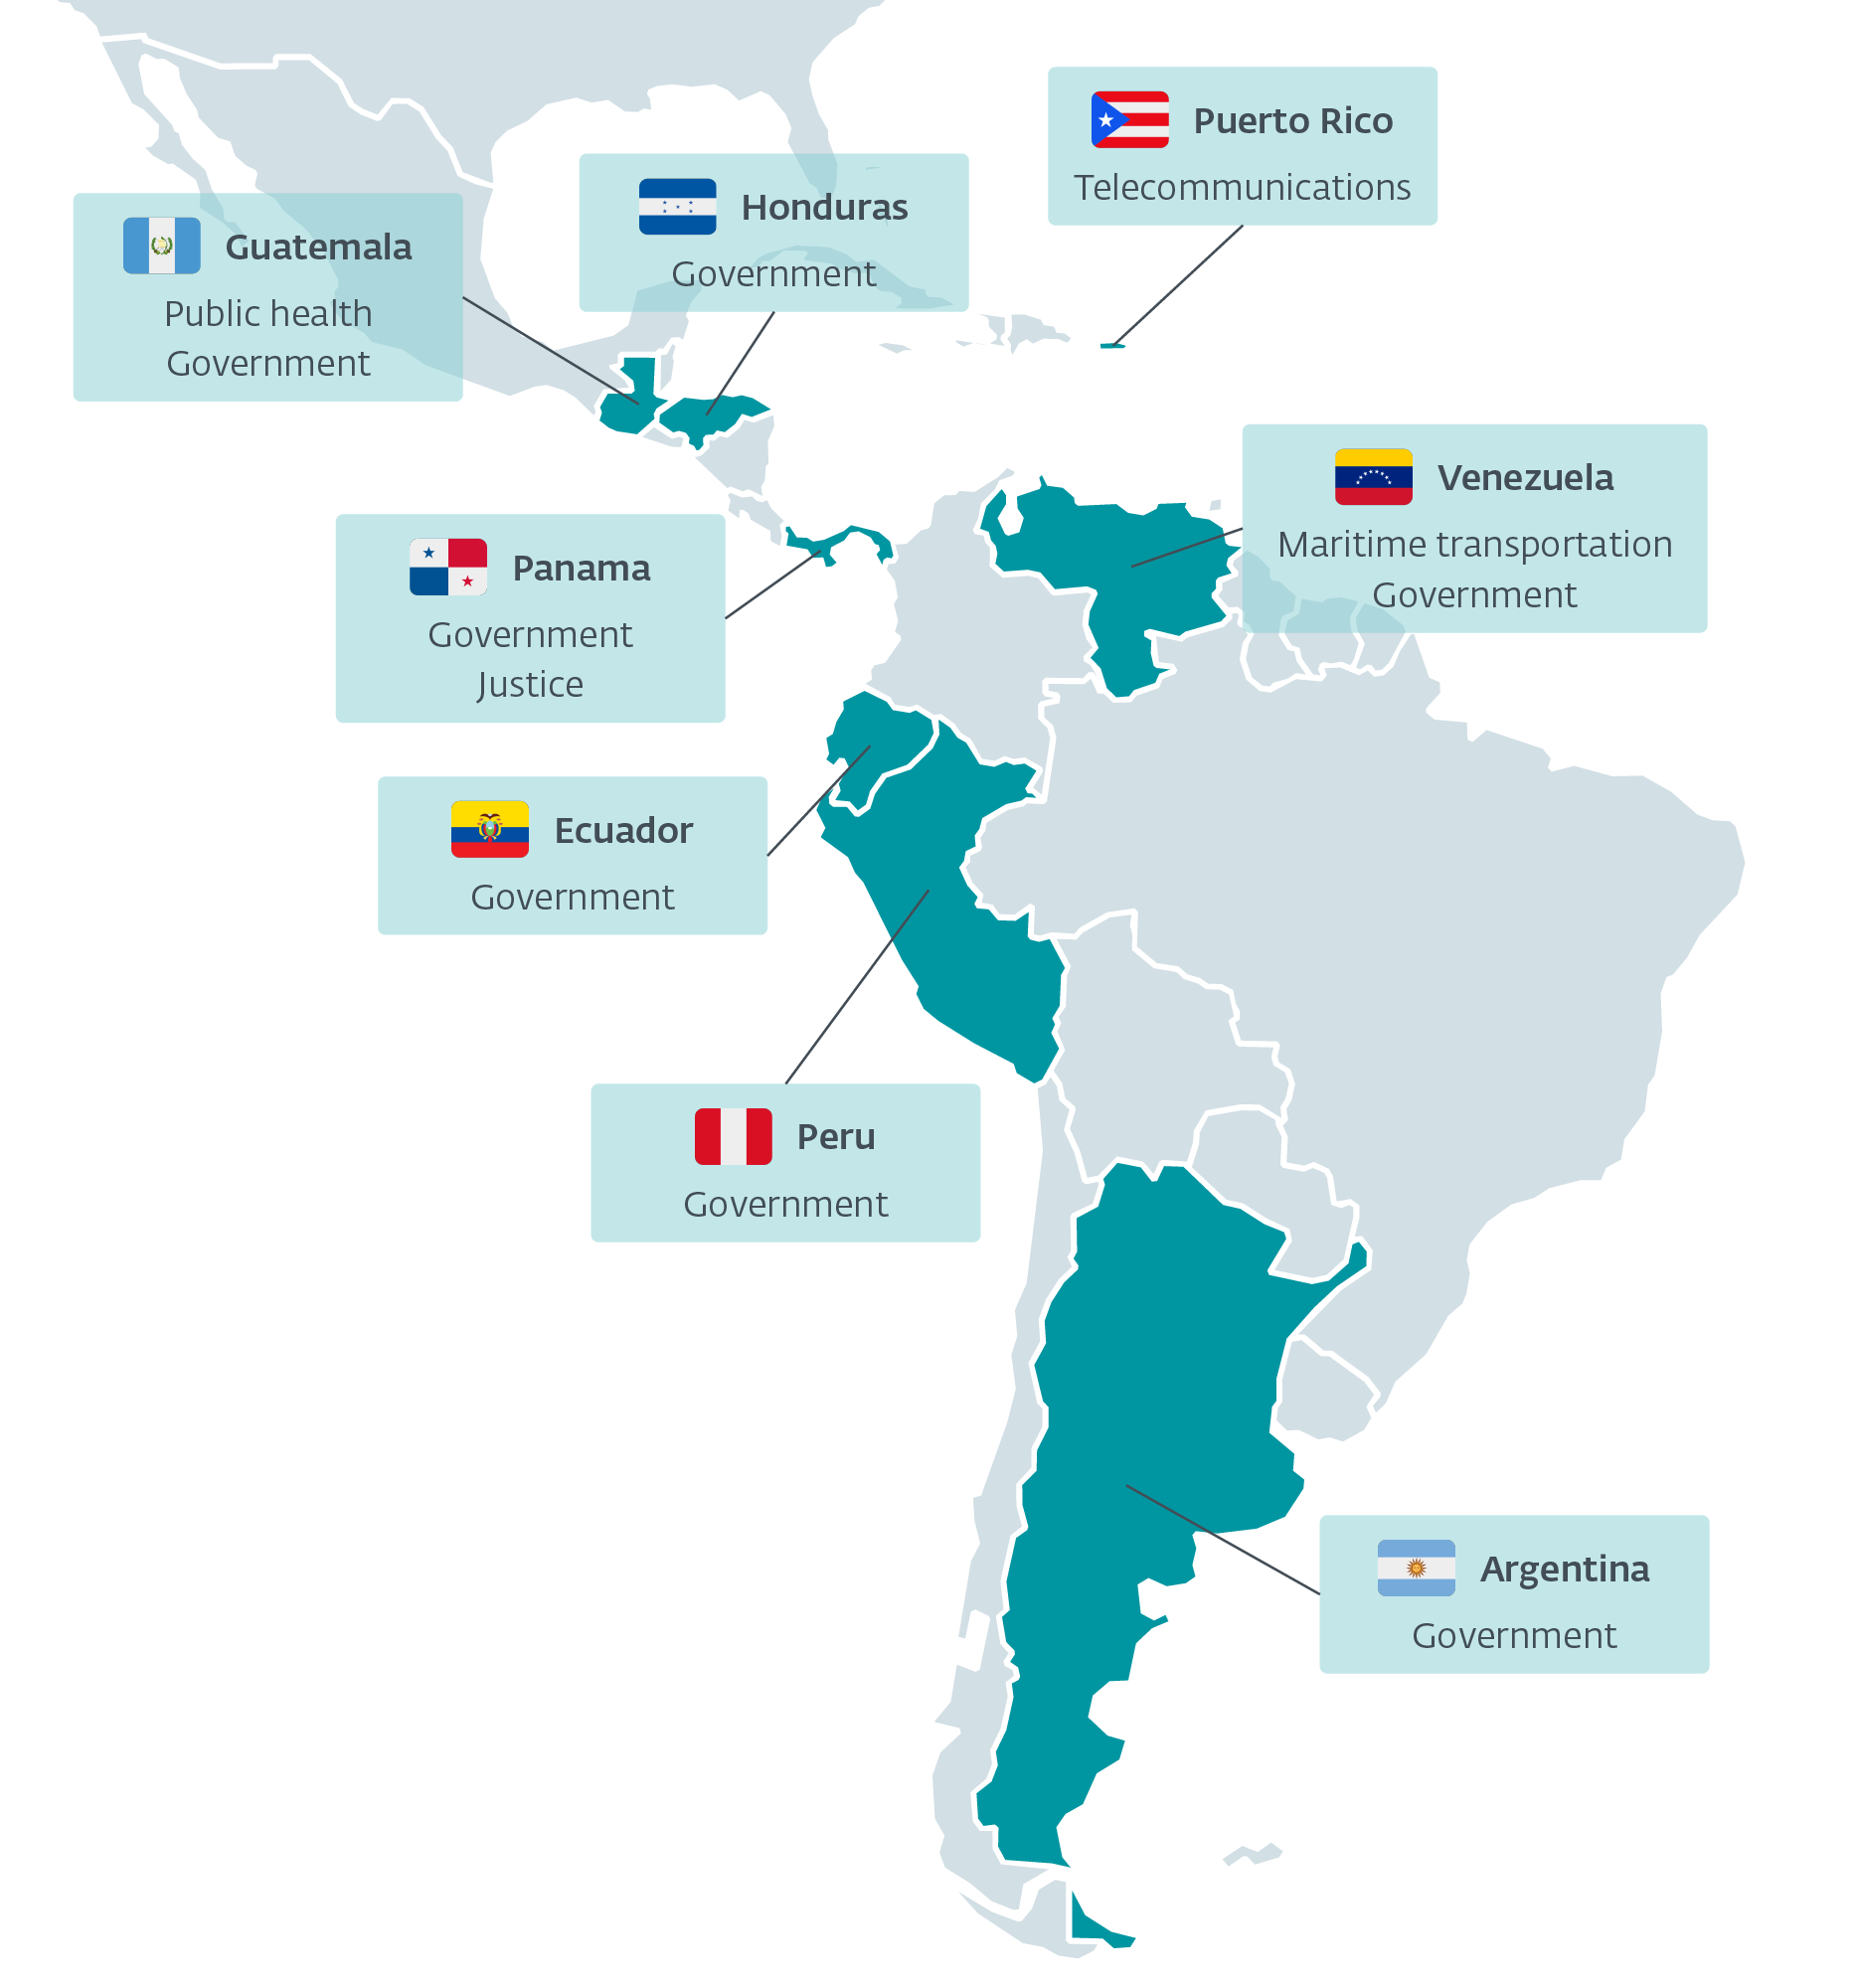
ESET Research reports that FamousSparrow, a China-aligned APT, has shifted from SparrowDoor to a new modular C++ backdoor called SparroWocky and has used it against governmental targets across Latin America since at least August 2025. The new implant adds stealthy loading, persistence, and data theft features, while its infrastructure and targeting show a strong focus on regional government entities and open-source tooling integration. #FamousSparrow #SparrowDoor #SparroWocky #LatinAmerica

Riverbed has launched Network 360, a new set of intelligent network observability solutions that combine expanded visibility with agentic AI to speed troubleshooting, identify root causes, and predict issues before users are affected. The offering integrates Riverbed IQ and Q into AppResponse and NetProfiler, while NPM+ extends coverage across remote users, Zero Trust, and public cloud environments. #Riverbed #RiverbedIQ #RiverbedQ #AppResponse #NetProfiler #NPMplus #Aternity
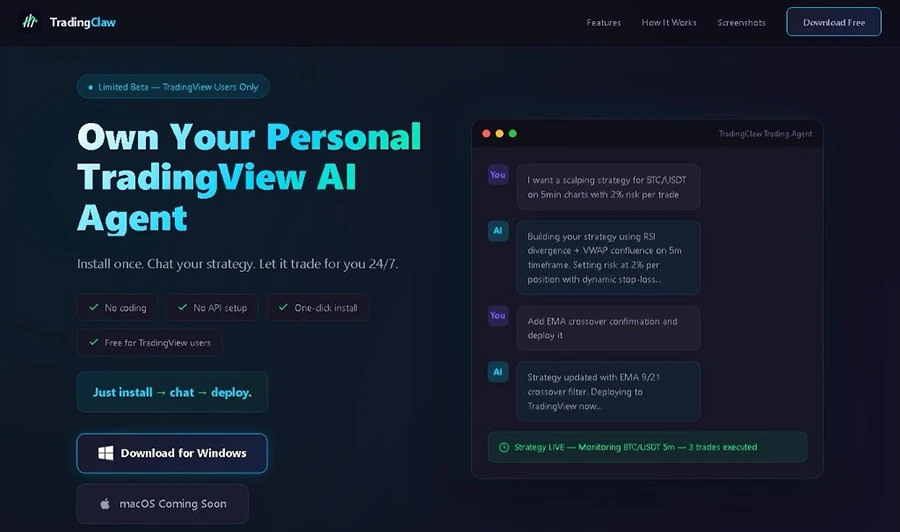
HP identified a fake AI crypto trading agent website that delivered Needle Stealer, which swaps browser wallet extensions to steal passwords and give attackers control of funds. The company also tracked QR code phishing, Phantom Stealer, and other fake installer campaigns that used image-based payloads, DLL side-loading, and process injection to spread theft tools. #NeedleStealer #PhantomStealer #MetaMask #CoinbaseWallet #Phantom #TradingClaw #CloudflareTurnstile #OneDrive #XWorm #PureLogsStealer #Formbook
Spain’s AEPD reported its first data breach allegedly caused by an autonomous AI agent that scanned a company network, found a flaw, altered personal records, and accessed invoice data. The incident highlights how AI agents are accelerating offensive operations, with related cases also involving Hugging Face and Anthropic during security evaluations. #AEPD #HuggingFace #Anthropic
The Court of Appeal for Ontario ruled that Panasonic Canada’s ransomware-related insurance claim is subject to a $3 million USD retention under XL Specialty’s Endorsement #023, not the $1.5 million USD retention under the base policy. Because Panasonic’s loss was valued at about $2 million USD, the court held the claim was wholly self-insured and dismissed Panasonic’s application. #PanasonicCanada #XLSpecialty #Endorsement023

There were 2 defacement incidents reported, targeting websites in Cambodia and Indonesia. The attackers involved were UnM@SK and HACKED BY MR. HANZ X. #Cambodia #Indonesia…