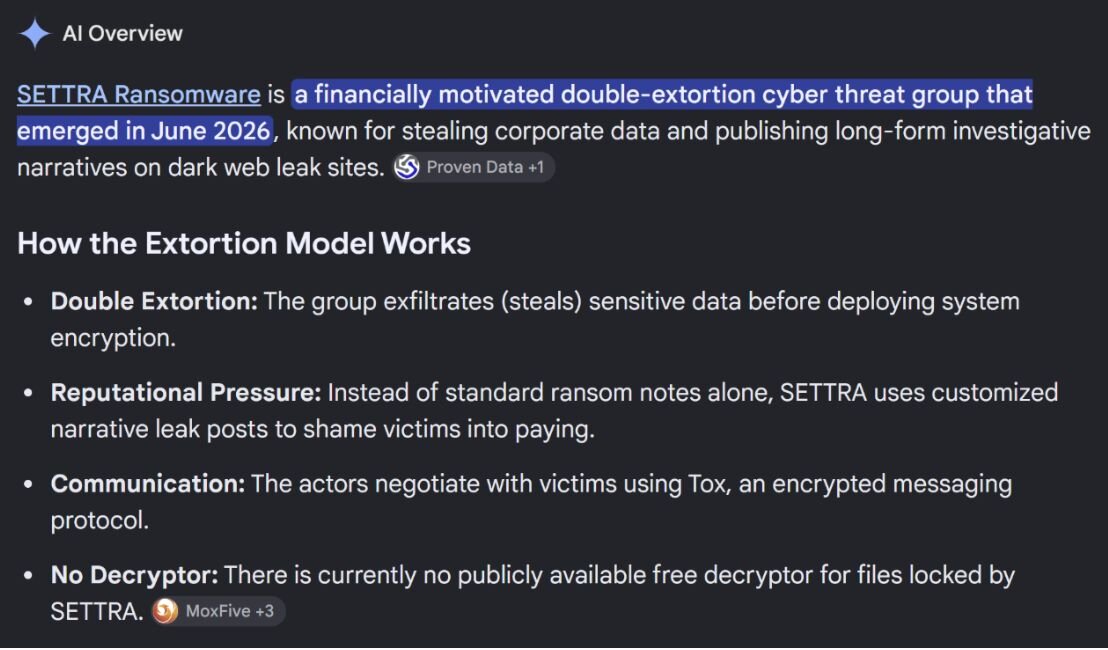
Huntress observed two Settra ransomware incidents, one in July and one in September, affecting organizations in consumer services and retail and in manufacturing. The attackers used MeshAgent RMM, attempted to hide their activity, and in one case showed evidence of BYOVD while also disabling recovery options and clearing Windows Event Logs. #Settra #MeshAgent #gdrvsys #RESTOREFILES
Keypoints
- Settra is a newer ransomware variant first seen in June.
- Huntress investigated two Settra incidents in July and September.
- The attackers used MeshAgent RMM for persistent access.
- One incident showed evidence of BYOVD using gdrv.sys.
- The ransomware tried to hinder recovery by deleting logs and disabling Windows Recovery Environment.
Read More: https://www.huntress.com/blog/new-settra-ransomware-variant