A ZIP file uploaded from Afghanistan contained a renamed Windows executable and a malicious DLL that side-loaded a targeted backdoor likely aimed at an Afghanistan government agency. The backdoor used 185.235.137[.]35:9000 for command-and-control, dropped a decoy Pashto PDF, and supported extensive remote-control commands after establishing persistence. #ApplicationFrameHost.exe #dgxi.dll #HZHostingLtd

Incransom ransomware targeted www.kendallhunt.com, a US-based publisher of hands-on, inquiry-based science, mathematics, and gifted curricula for PreK-12, founded in 1944. The attack impacted the organization’s print and digital educational materials for students, teachers, and parents in the United States. #UnitedStates
The ransomware claim targets www.roancampingholidays.com, a Dutch tour operator, with the threat actor incransom. The alleged impact is on Roan Luxury Camping Holidays in the Netherlands. #Netherlands
On behalf of akira, Anderson Industries suffered a ransomware incident in which approximately 9GB of corporate data was exfiltrated, including employee personal information, client data, project files, specifications, orders, financial records, and NDAs. #unknown
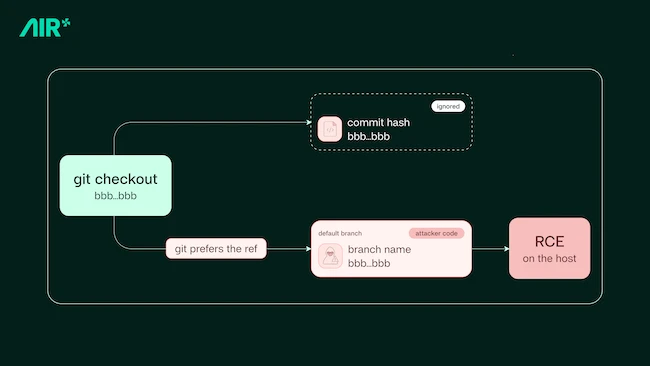
AIR uncovered Plugin4Shell, a zero-click RCE affecting Claude Code, Codex, GitHub Copilot, and Gemini CLI through a shared plugin SHA-pinning bypass. The flaw lets attackers swap in malicious code during background updates, with vendor responses ranging from patches to deprecation and no fix yet for GitHub Copilot. #Plugin4Shell #ClaudeCode #Codex #GitHubCopilot #GeminiCLI #AIR #Anthropic #OpenAI #Microsoft #Google #Antigravity

Arcjet has introduced agent runtime security to help engineering teams secure AI agents in production while giving security teams the observability, enforcement, and audit evidence they need. The product tracks agent workflows across sessions, applies deterministic controls to risky actions, and preserves execution context for reviews and compliance. #Arcjet #OpenTelemetry #Rego #OpenPolicyAgent #ClaudeAgentsSDK #OpenAIAgentsSDK #LangChain #LangFuse #Strands #Mastra #MicrosoftsAgentFramework
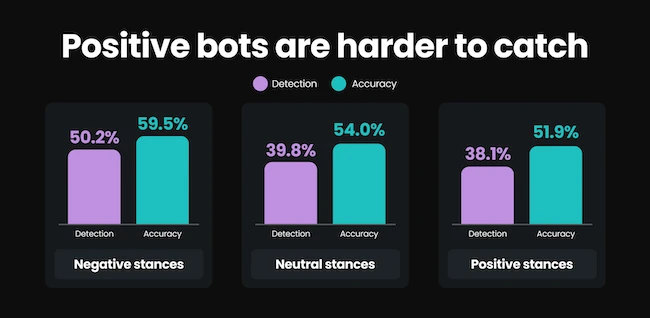
A Surfshark study found that most people struggle to tell bots from humans online, correctly identifying only 40% of AI-generated comments in a social media test. Polite, friendly, and logical-sounding bots were the hardest to detect, making them a greater concern for manipulation and privacy than hostile accounts. #Surfshark
Microsoft has fixed a known issue in KB5002914 that caused silent copy-and-paste, autofill, and formula dragging failures in Excel for some users. The released workaround update KB5002665 only addresses Microsoft Installer-based Office 2016, while affected users of other Excel versions are advised to use Paste Special or temporarily uninstall KB5002914. #Microsoft #KB5002914 #KB5002665 #Excel2016
Check Point Software has issued security updates for CVE-2026-91843, a critical stack-based buffer overflow flaw that can allow unauthenticated attackers to achieve root remote code execution on Security Management Server and Log Server systems. The company has also shared mitigation steps and detection guidance, while noting that its recently patched CVE-2026-85102 and CVE-2026-85103 vulnerabilities are considered likely to face exploitation attempts soon. #CheckPoint #CVE-2026-91843 #CVE-2026-85102 #CVE-2026-85103 #NCSC-NL #Qilin
Brevo suffered a supply chain attack after a compromised Cloudflare API key was used to inject malicious scripts into Brevo assets and customer-embedded JavaScript, impacting more than 100,000 websites. The attack followed an earlier SAML SSO abuse that exposed 138 accounts, including Trezor, and used fake Cloudflare verification pages to trick…
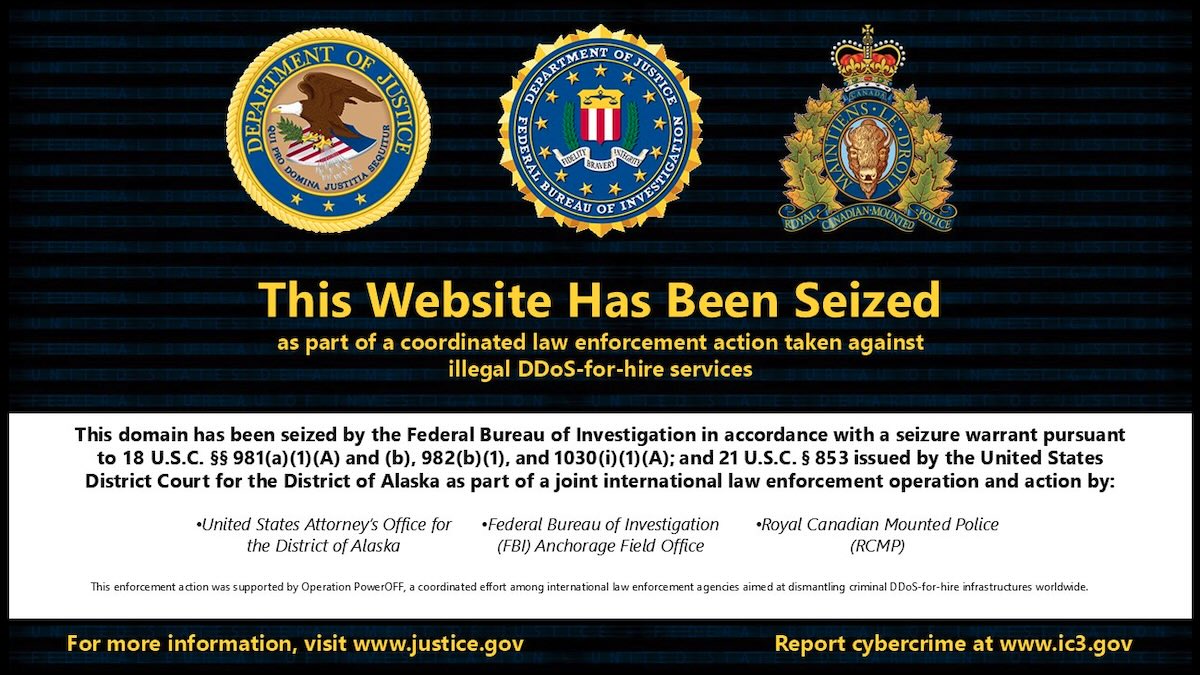
The FBI has seized the domains of NightmareStresser, a long-running DDoS-for-hire service that was used to launch hundreds of thousands of attacks worldwide. The takedown was part of Operation PowerOFF, a global effort to disrupt booters and stressers and hold their operators accountable. #NightmareStresser #OperationPowerOFF #FBI #USDepartmentofJustice…
Microsoft released patches for 18 vulnerabilities across Azure services and Copilot-branded AI products, with most issues involving elevation of privilege and several information disclosure flaws. The company said none of the bugs are known to be exploited, and all Azure and Copilot fixes were handled server-side, while Windows users must update…

The Intermunicipal Community of the Leiria Region was hit by a ransomware attack that led to the isolation of its email server. Although security systems and backups worked, Porto de Mós was temporarily cut off from email as a precaution while the incident was reported to authorities. #CIMdaRegiaoDeLeiria #PortodeMós
Nipigon District Memorial Hospital was hit by a ransomware incident that encrypted files containing personal and health information, disrupting its systems and some patient services. The hospital has activated its incident response procedures and is working with external experts and law enforcement while managing longer wait times and temporary service closures. #NipigonDistrictMemorialHospital #ransomware
Sutton officials are still investigating a cybersecurity incident that affected part of the town’s network and Sutton Public Schools, while taking immediate steps to secure systems and contain the impact. Independent cybersecurity and forensic experts have been engaged, and law enforcement has been notified. #Sutton #SuttonPublicSchools