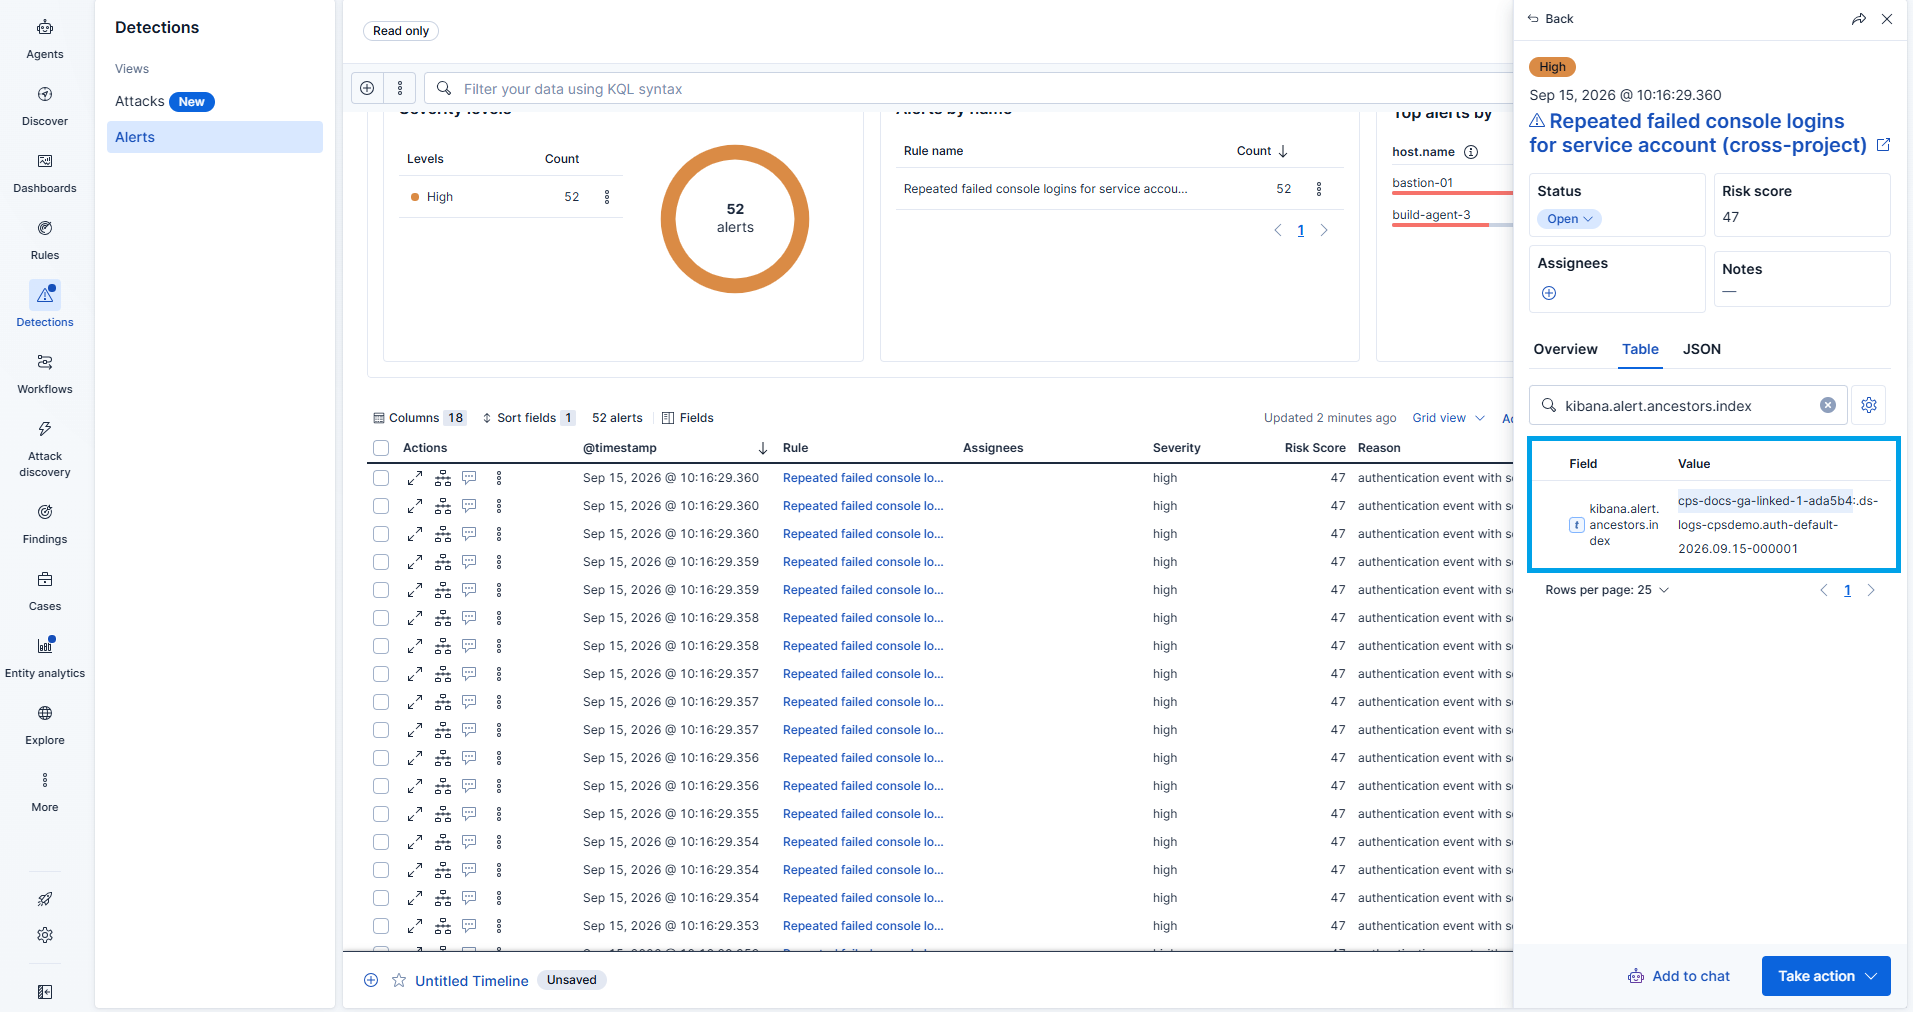
Elastic Cloud Serverless Cross-project search (CPS) lets one Elastic Security origin project run detection, triage, investigation, and response workflows across linked projects while keeping each tenant’s data isolated. In testing, a single origin handled about 2,100 prebuilt detection rules across 100 linked projects, with ES|QL guidance, operational limits, and clear boundaries on what CPS can and cannot do. #ElasticCloudServerless #ElasticSecurity #CrossProjectSearch #ES|QL
NightEagle, also known as APT-Q-95, has expanded its cyberespionage operations from China to Russian companies, using stolen VPN credentials, Microsoft Exchange abuse, and the GhostContainer backdoor to infiltrate networks. The group also relied on GitHub for tool storage and exploited Active Directory to deepen access, steal credentials, and attempt control of…
Multiple countries have taken legal and sanctions actions after a UN-linked report exposed North Korea’s illicit IT worker scheme and the network of local facilitators supporting it. The MSMT said the program has spread across dozens of countries, generated hundreds of millions of dollars, and is now facing tighter scrutiny in…

Identity visibility gives security teams a continuous view of every identity, its real permissions, and how those permissions are used across cloud, SaaS, and on-prem environments. The article explains why hidden identities, machine accounts, and cross-cloud trust relationships create blind spots that traditional IAM reporting often misses, and how identity visibility…

Arcusmedia ransomware claims to have targeted AKAZZO, leveraging access to akazzo.com.br to disrupt its operations and extort payment. The impacted country(s): #Brazil
arcusmedia ransomware allegedly targeted Schneider’s Computing & Websites Ltd. (Canada) and its website at www.scomputing.ca, encrypting data and disrupting services. The claim indicates an impact to CA #Canada
The ransomware claim targets ambpvc in France, attributed to the ZaWoo threat actor. The incident results in encrypted and compromised systems for the victim, potentially disrupting operations across FR. #France
FRANCARETRAD in France reported a ransomware attack attributed to ZaWoo, as referenced in an unpublished claim. The incident resulted in disruption due to encrypted or inaccessible data, impacting France. #France
HEOLIS in France reported a ransomware incident attributed to the ZaWoo threat actor, as described in an unpublished advisory. The attack resulted in disruption of operations and encryption of data, with the impacted country being France #france

There were 5 defacement incidents reported, targeting sites in Indonesia and Brazil. The attackers involved were UnM@SK and Antonkill, with UnM@SK responsible for four incidents and Antonkill for one. #Indonesia #Brazil…
Tilly Norwood’s viral Piers Morgan appearance drew fresh attention after the AI actress glitched and began speaking Chinese, sparking questions about whether the moment was accidental or a publicity stunt. The accompanying “Talking Tilly” service also revealed strict biometric age checks, emotion monitoring, recorded calls, and short-lived paid access tied to Xicoia’s rollout and UK online safety rules. #TillyNorwood #TalkingTilly #Xicoia #PiersMorgan #Misaligned
ShinyHunters breached Clop’s data leak site, defaced its Tor page, and claimed to steal server data, logs, source code, and the private keys for Clop’s onion service. The incident appears tied to an escalating feud between the two groups over earlier Oracle E-Business Suite attacks and alleged threats. #ShinyHunters #Clop #OracleEBusinessSuite #CVE202561882
Security researcher Gal Weizman of Forever Security revealed BragJack, a new attack technique that can hijack AI assistants inside popular browsers through a single malicious extension. The findings affected Google Chrome’s Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and Claude in Chrome, and led to two CVEs and bug bounty rewards from multiple vendors. #BragJack #GalWeizman #ForeverSecurity #GoogleChrome #GeminiLive #PerplexityComet #MicrosoftEdge #OperaNeon #ClaudeinChrome #CVE-2026-0628 #CVE-2026-55945
The ransomware incident targeted Kreishandwerkerschaft Borken in Germany by the threat actor rhysida, resulting in data disruption and potential file encryption. Kreishandwerkerschaft Borken was impacted in Germany #Germany
Threat actor emperador claimed to have accessed Electrolux’s Azure database in Sweden (SE) and exfiltrated approximately 41GB of data, threatening to leak the password-locked archive Electro_backup.7z unless the ransom is paid. The actor said the victim would receive ransom instructions by email and warned that the password and data would be released if they did not comply. #Sweden