Zscaler ThreatLabz tracked Vidar’s string obfuscation as it evolved from XOR and ChaCha20 into a per-build virtual machine and custom stream cipher designed to frustrate static analysis. The report details how these changes affect deobfuscation, shows example VM opcodes and ARX/ChaCha-based cipher logic, and includes Zscaler detections for Vidar. #Vidar #Zscaler #ThreatLabz
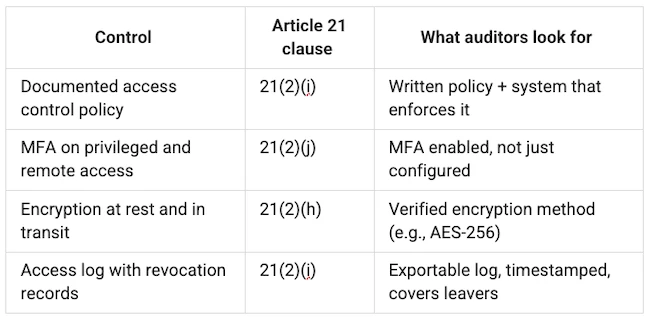
Passwork helps organizations align with NIS2 Article 21 by automating access control, MFA, credential hygiene, encryption, and audit logging without adding major IAM overhead. It also reduces password reset tickets and makes it easier to produce audit evidence for EU compliance reviews while keeping credentials inside self-hosted infrastructure. #NIS2 #Passwork #ENISA #ADLDAP #SAMLSSO #Yubikey
Researchers from the i2CAT Foundation, the University of Murcia, and NEC Laboratories Europe created 5G-Shark to lure phones onto a fake base station and test how commercial 5G networks handle identity privacy. Their tests found that while permanent IDs were mostly hidden, predictable temporary IDs still enabled subscriber tracking on some networks, and crafted reject messages could force phones into service loss, retry loops, or modem freezes. #5G-Shark #i2CATFoundation #UniversityofMurcia #NECLaboratoriesEurope #SamsungGalaxyS23
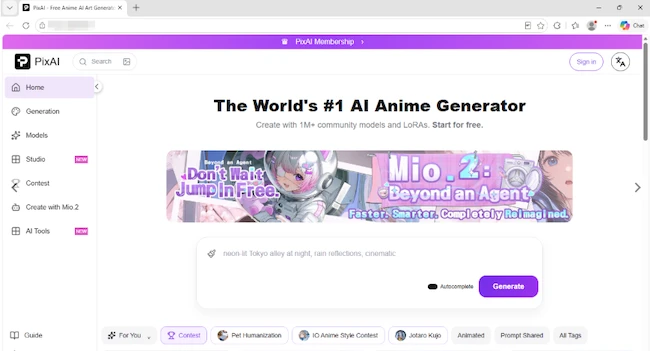
Scammers are using a $249 website toolkit to create polished fake subscription sites that imitate products like GPT-6 Astra, PixAI, DaVinci Resolve, and Omegle, then steer visitors to paid plans through genuine Google sign-in pages. Malwarebytes found more than 100 linked sites with shared files and developer details, warning that the real Google login does not prove the service behind it is legitimate. #Google #Malwarebytes #PixAI #DaVinciResolve #Omegle #GPT6Astra

Enterprise AI and shadow AI create new governance challenges because employees increasingly use AI on mobile devices and may expose sensitive data, IP, and business knowledge. The article argues that trustworthy AI depends on on-device processing, centralized cloud controls, managed identities, and a trusted device foundation such as Samsung Knox. #GalaxyAI #SamsungKnox #SamsungGalaxy

Daily Recap, Vendors and platforms news covered Accenture deepening its OT security push after Dragos completed the NetRise and runZero acquisitions, Microsoft urging admins to move Entra ID users to passkeys while noting September File History backup breakage, and Google confirming Gemini AI was used to breach three firms. Threats and response updates included the AI-enabled RatHat Android trojan, North Korean job-interview scams, fake police and federal agent extortion schemes, warnings about three exploited Linux kernel vulnerabilities, and targeted attacks on Rust team members and popular crate maintainers, alongside a GDPR fine against Google, FBI CJIS v6.1 updates, and OT-focused cyberattacks on Colorado water utilities.
#Accenture #Dragos #NetRise #runZero #EntraID #passkeys #FileHistory #Gemini #RatHat #NorthKorea #LinuxKernel #Rust #GDPR #Ireland #FBI #CJISv61 #Colorado #OTSystems #SAP_ECC #Helmit #Gopass
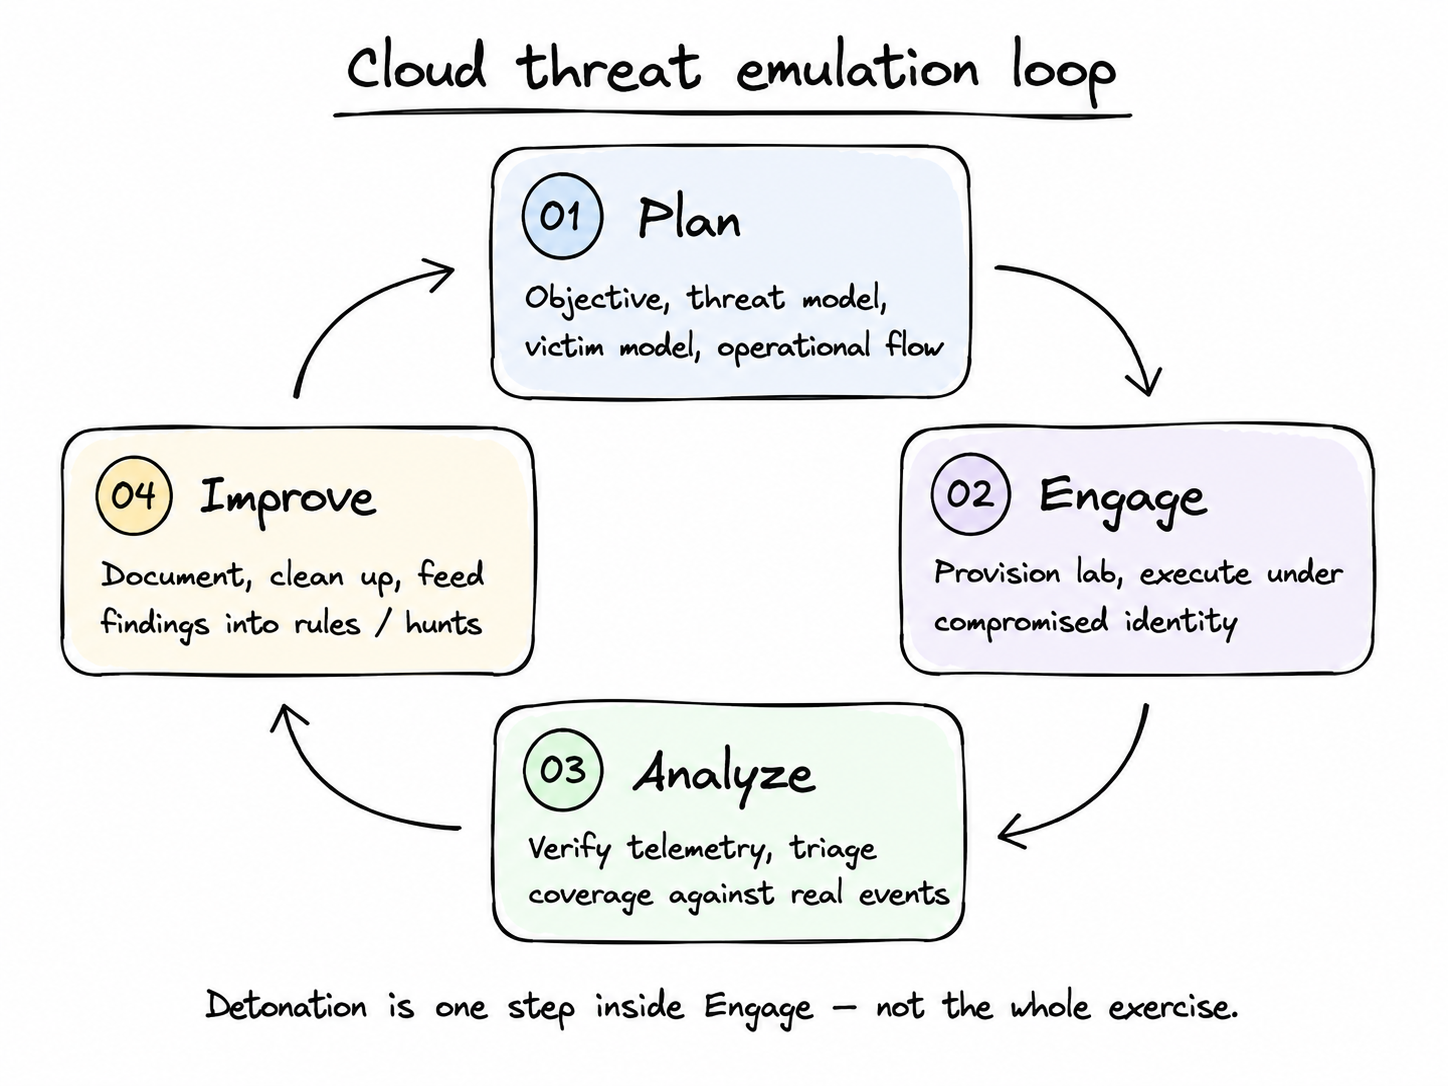
Cloud threat emulation in AWS, Azure, SaaS, and identity environments requires a plan-first lifecycle that models the victim, identity, permissions, telemetry, and cleanup rather than simply detonating API calls. The article argues that useful detection engineering depends on realistic footholds, verified logs, controlled labs, and coverage analysis against exercises using tools like Stratus Red Team, Atomic Red Team, CloudGoat, ROADTools, Splunk ATT&CK Range, and CTID-style plans. #StratusRedTeam #AtomicRedTeam #CloudGoat #ROADTools #SplunkATTCKRange #CTID #AWS #Azure #Entra #M365
Attackers are actively exploiting CVE-2026-7273 in Zyxel GS1900 series switches, a high-severity stack-based buffer overflow that can let unauthenticated LAN users execute OS commands through malicious HTTP requests. CISA has added the flaw to its Known Exploited Vulnerabilities catalog and ordered federal agencies to patch affected devices, while GreyNoise reports nearly 1,000 compromised switches across 48 countries. #CVE-2026-7273 #ZyxelGS1900 #CISA #GreyNoise

ASEC reports that Larva-25012 resumed distributing Proxyware in the second half of 2026 by exploiting already infected systems, with recent cases involving DigitalPulse, SOAX, Appsalt, and IPRoyal. The campaign uses DPLoader, PowerShell downloaders, scheduled tasks, and loader/DLL sideloading to install Proxyware and disable defenses on systems in Korea. #Larva-25012 #DPLoader #DigitalPulse…
GTIG reported on three Russian threat groups—UNC6293, UNC7005, and UNC5976—while the analysis identified 33 network IoCs and uncovered risky subdomains, typosquatting domains, and malicious infrastructure linked to the campaign. Additional DNS and WHOIS investigation revealed victim-related IP communications, email-connected domains, and weaponized domains such as dsapdlqpwd[.]icu. #UNC6293 #UNC7005 #UNC5976 #globsecnet #wa-connectnet #miov2iaiaoubqosiqoiajwowiwjsoonline #dsapdlqpwdicu

Termite ransomware operators targeted Sealcon, a US-based cable management provider headquartered in Colorado, encrypting data and disrupting operations. The incident highlights the risks to critical manufacturing and electrical component suppliers in the United States. #UnitedStates
termite ransomware claimed responsibility for an attack on theLender in the US, threatening operations for a US-based wholesale mortgage company. theLender was founded to change the stagnant wholesale mortgage landscape; impacted country(s): #UnitedStates
Threat actor termite claimed a ransomware attack against TruAmerica Multifamily, a vertically integrated US real estate investment and asset management firm focused on multifamily housing, citing disruption and unauthorized access to its systems. The impacted country(s) are: #UnitedStates
In Uzbekistan, the N0n ransomware group claims to have compromised FinSoft’s Kolibri retail back-office software, impacting client databases and the platform/API data used by 10+ retail chains (keddo, marc, lancaster, comf_rus, ek, cr, bas_at, bas_juk, bas_nov, bas_zar) including sales, stock, pricing, and financial records. The group alleges it will publish one client database per day after the deadline, starting with keddo, so clients will know exactly whose software failed them. #Uzbekistan
ENISA launched the CRA Single Reporting Platform to centralize reporting of actively exploited vulnerabilities and severe incidents, while EU and national regulators issued new guidance on privacy, AI oversight, cloud identity token security, and healthcare breach response. Courts and officials in California, Florida, and Texas also sharpened scrutiny of AI-generated filings and privacy demand-letter tactics, underscoring the growing legal and operational pressure on organizations handling digital systems and personal data. #ENISA #CRA #JRC #Europol #CNIL #MyDr #California #CISA #NIST #Lisandrillo #VivekShah