Microsoft released KB5124010, a non-security preview update for Windows 11 24H2 and 25H2 that includes 46 changes, Bluetooth fixes, and the ability to remap the Copilot key. It also adds features like Emoji 17.0, new accessibility and recovery tools, and marks the final preview update for Windows 11 24H2 before end of support in October 2026. #KB5124010 #Windows11 #CopilotKey
MacSync is a rapidly evolving macOS infostealer family that has shifted from AppleScript-based payloads to binary droppers and executables written in Objective-C and Swift, with a new infection chain first observed in September 2026. The campaign uses fake apps, malicious DMG images, iCloud calendar abuse, and layered persistence and exfiltration mechanisms to steal browser, wallet, Telegram, keychain, and system data. #MacSync #AMOS #Toria #iCloud #curve25519_donna
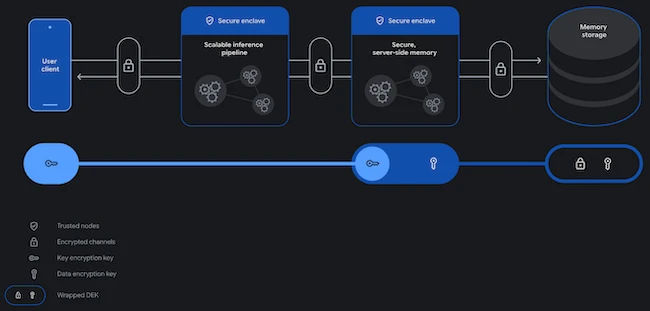
Google is adding private, server-side memory to Private AI Compute so AI assistants can retain context across devices while preserving strong privacy protections. The platform uses encrypted storage, device-held keys, and secure enclaves so even Google cannot access the data, with transparency measures like a public technical brief and independent audit. #PrivateAICompute #Gemini
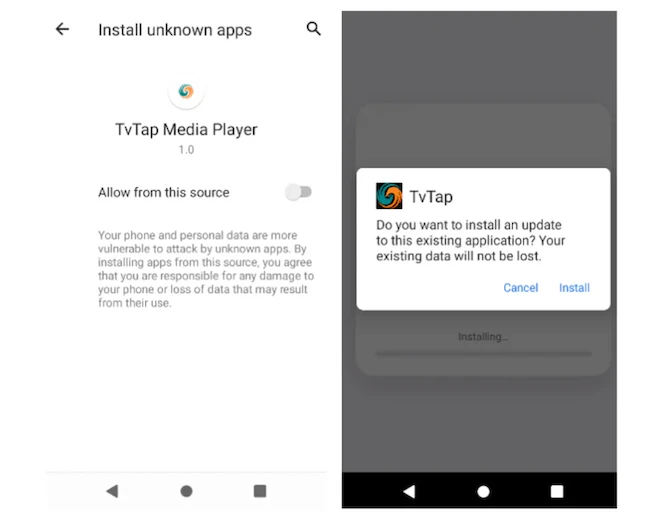
RemControl is a new Android banking trojan that lures victims with fake TVTap app pages, then abuses permissions to take over devices and steal banking PINs and other sensitive data. Group-IB found that it targets customers of more than 30 banks across several countries and appears to use AI-assisted infrastructure and malware-as-a-service delivery. #RemControl #GroupIB #TVTap #UNKK #UNKN #Medusa
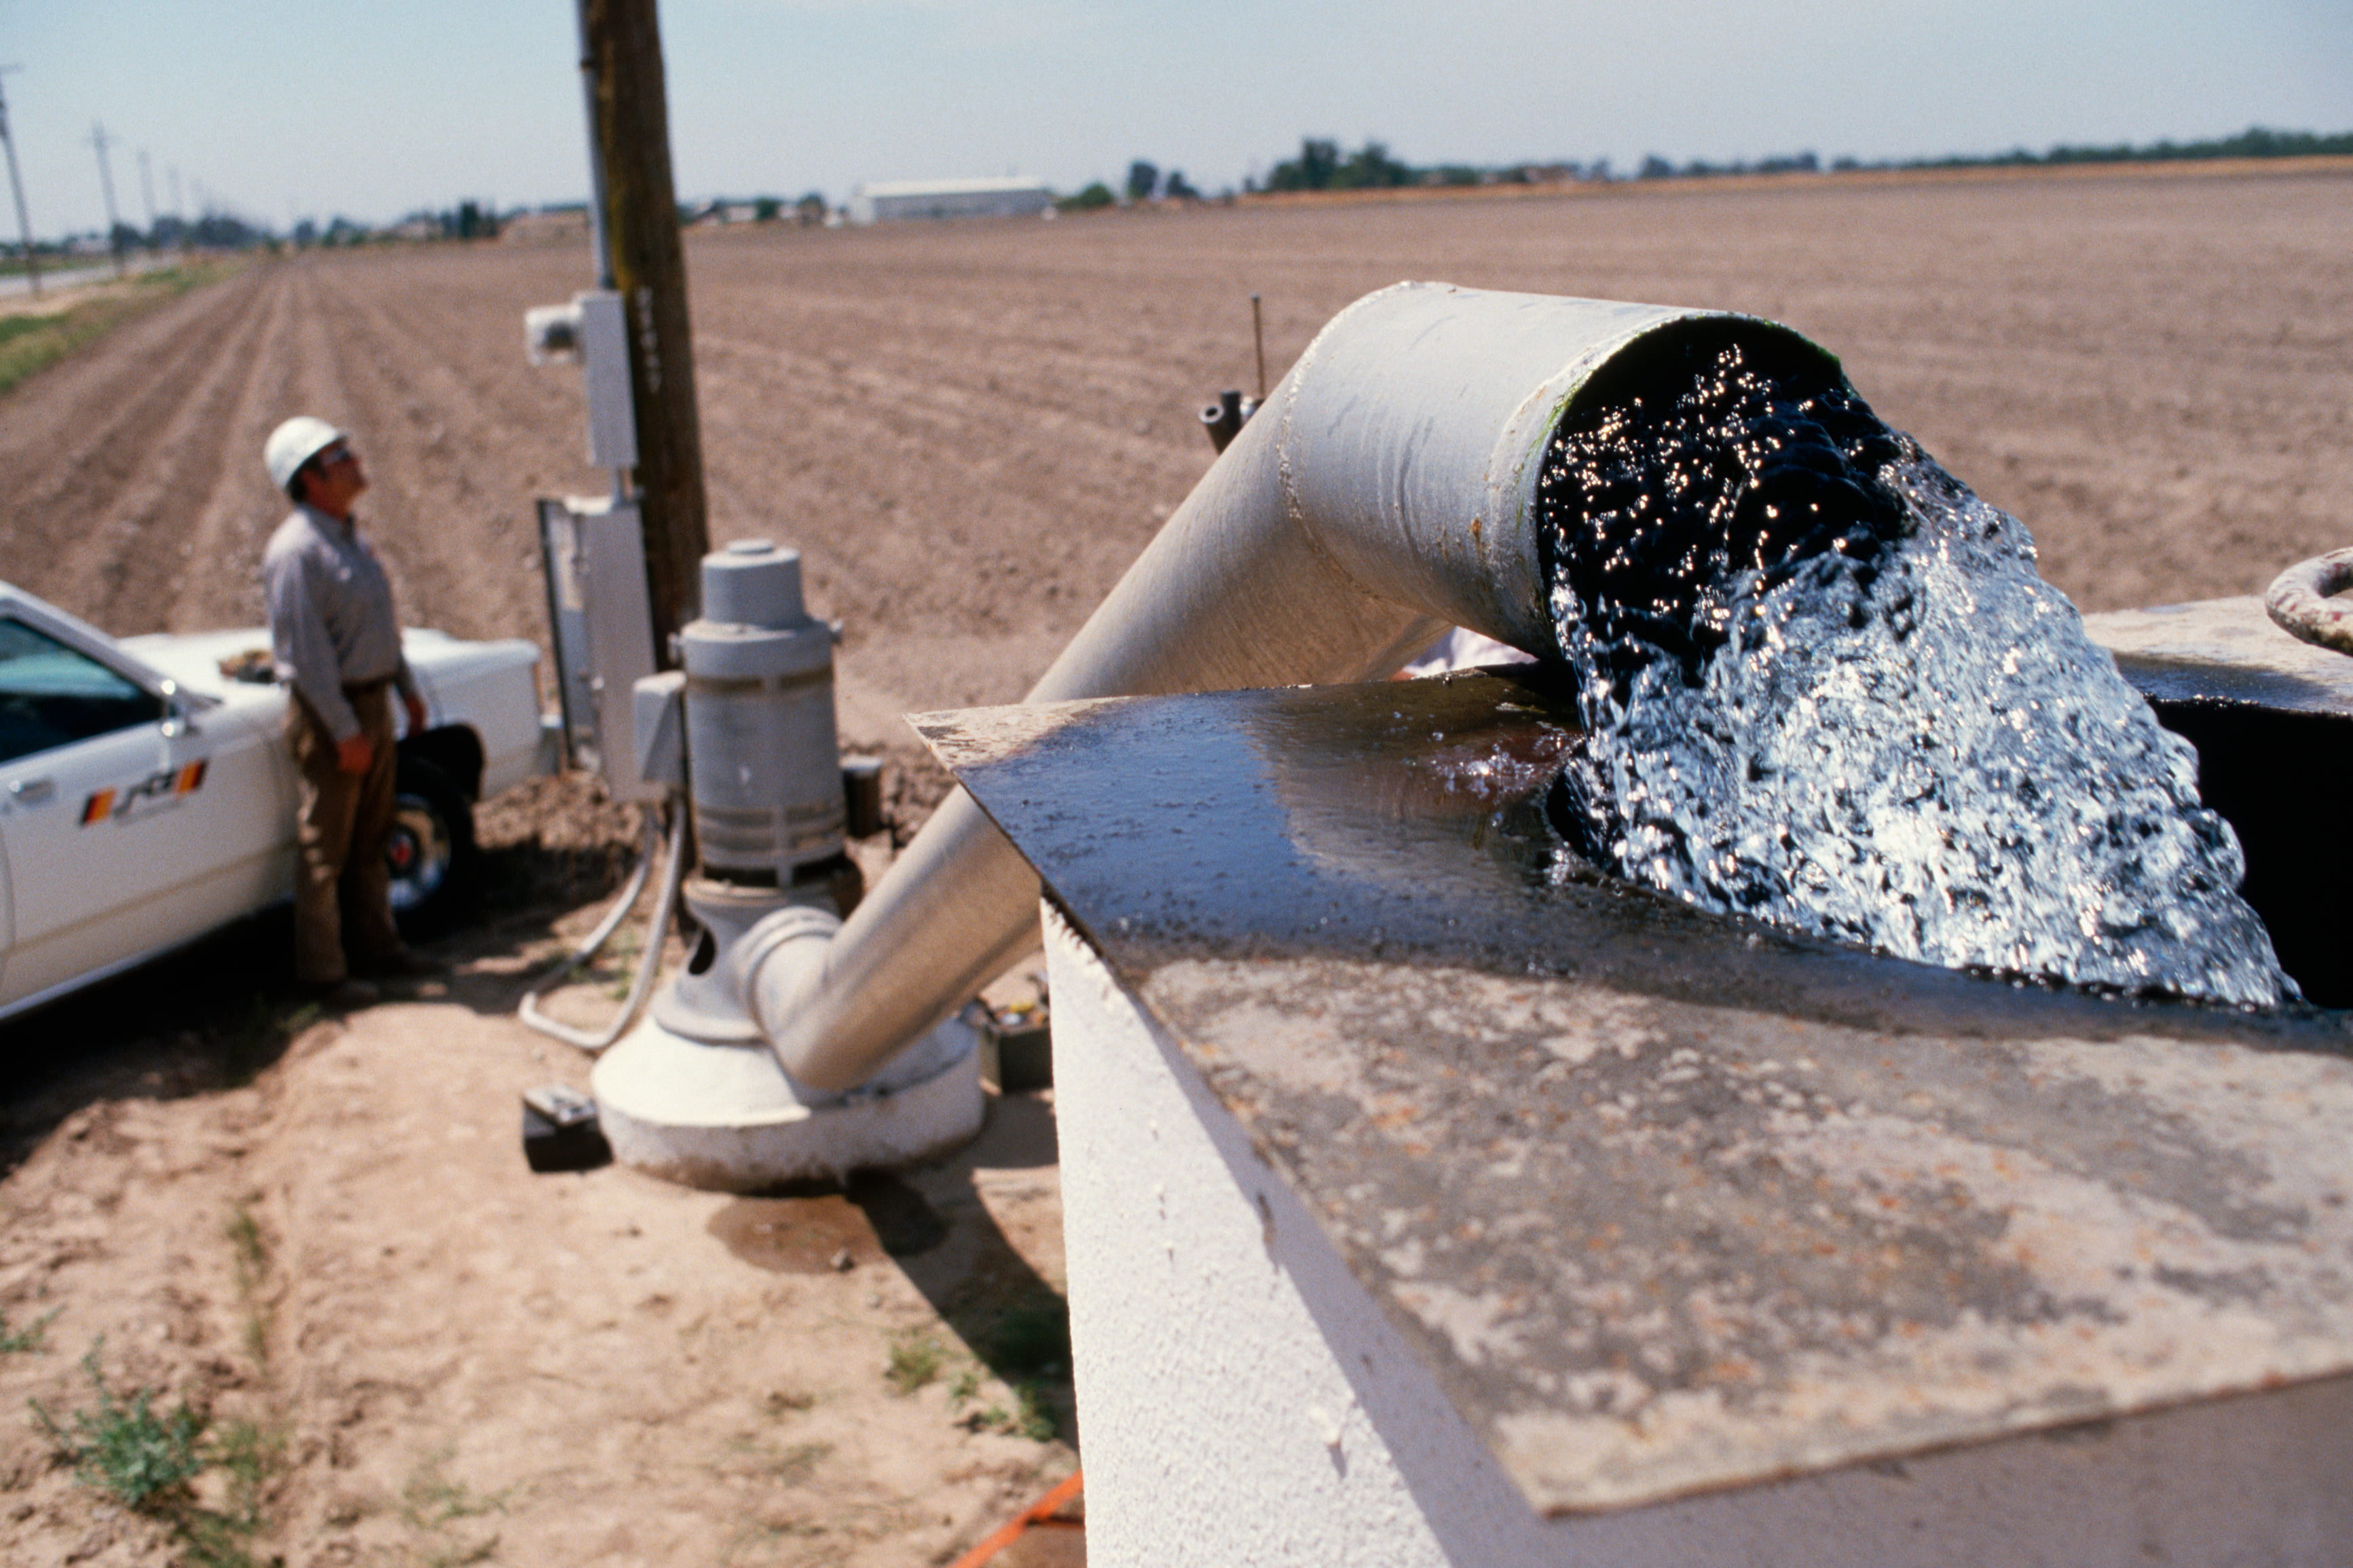
State and local governments in the U.S. are increasingly targeted by state-backed threat actors, with critical infrastructure like water systems, hospitals, and industrial controllers facing active threats. The article argues that tax incentives, clearer Section 174A guidance, and faster investment in cybersecurity software are needed to help protect vulnerable organizations such as Siemens S7 PLC users and small municipalities like Braham, Minnesota. #SiemensS7 #Braham #Section174A #TomCotton #ScottBessent #CISA

ENISA’s 2025 Threat Landscape shows that ransomware, ideology-driven DDoS campaigns, and vulnerability exploitation continue to dominate cyber activity affecting the European Union. The report also highlights growing use of AI by threat actors, with public administration remaining the most targeted sector and incidents increasingly blurring the lines between cybercrime, hacktivism, and state-linked operations. #ENISA #NIS2 #DDoS #Ransomware #ClickFix

Daily Recap, AI and policy developments dominated the news as the U.K. warned attackers could benefit more than defenders, U.S. officials advanced AI-cyber test and defense initiatives, and researchers highlighted AI-enabled malware like ClosedQuorum that can choose attack actions dynamically. In addition, teams faced multiple exploited zero-days across major vendors and systems, while takedowns and disclosures targeted actors such as EvilTokens, ShinyHunters, and LAPSUS$, and organizations like BigCommerce and IDScan reported breach impacts.
#ClosedQuorum #EvilTokens #ShinyHunters #LAPSUS$ #Ryuk #Microsoft #F5 #BIG-IP #CheckPoint #Arista #WordPress #BigCommerce #IDScan #Twilio #Ribon #Miljödata #NightmareEclipse #NightmareEclipse #Zyxel #Miljödata
Two defacement incidents are reported, targeting Tunisia and Peru. The attackers involved were Panataran and Trenggalek Cyber Army. #Tunisia #Peru…
Astrana Health disclosed that private and confidential information was stolen from its servers after employees were targeted in a social engineering attack. The company said attackers impersonated personnel, spoofed its main phone number, and accessed or exfiltrated sensitive data while it worked to contain the incident and investigate the impact. #AstranaHealth…
SolarWinds has patched two severe vulnerabilities in Observability Self-Hosted, including CVE-2026-28324 and CVE-2026-28325, both of which could allow remote code execution by unauthenticated attackers. The company also recently fixed a separate unauthenticated RCE issue in Access Rights Manager, and there is no evidence that any of the flaws have been exploited…
AI adoption in cybersecurity is moving beyond dashboards and chatbots toward agentic remediation that can close the loop on exposure management. The article argues for “Shift Zero,” where automated, bounded agents help eliminate vulnerability backlogs by fixing known issues at the source. #CTEM #ShiftZero #agenticremediation…
FBI and CISA issued guidance for critical infrastructure owners and operators on reducing risk when using third-party ICS integrators, with emphasis on least privilege, secure contracts, and monitoring remote access. The fact sheet cites a 2025 incident in which foreign cyber actors accessed a U.S. industrial automation company, searched for SCADA-related…
Attackers disrupted water systems in at least seven U.S. states by remotely accessing internet-facing programmable logic controllers, prompting federal investigators to examine possible links to Iran-backed hackers. Honeywell’s survey shows many critical infrastructure organizations still lack full visibility into building automation systems and IoT devices, which can slow recovery from outages and incidents. #FBI #EPA #HoneywellTechnologies
AI agents create exposure by widening access to enterprise data paths, especially when they can rapidly retrieve and combine sensitive information from systems like ticketing platforms, CRM tools, shared drives, and chat history. Kelly Herrell of Nol8 recommends enforcing deterministic policy in the data path so organizations can control what data enters, leaves, and is disclosed by agents. #Nol8 #AIDataPlane #Salesforce #Jira
CISA has released a white paper describing its plan to move the CVE program into a “Quality Era,” focusing on better governance, broader participation, stronger infrastructure, and more reliable vulnerability records. The proposal comes as CVE volume continues to surge, with experts welcoming the emphasis on quality while questioning whether the document goes far enough to solve persistent data issues. #CISA #CVE #NIST #NationalVulnerabilityDatabase #Sonatype #OWASP #VulnCheck