MacSync is a rapidly evolving macOS infostealer family that has shifted from AppleScript-based payloads to binary droppers and executables written in Objective-C and Swift, with a new infection chain first observed in September 2026. The campaign uses fake apps, malicious DMG images, iCloud calendar abuse, and layered persistence and exfiltration mechanisms to steal browser, wallet, Telegram, keychain, and system data. #MacSync #AMOS #Toria #iCloud #curve25519_donna
Keypoints
- MacSync is a MaaS macOS infostealer family that evolved from AppleScript-based payloads into Objective-C and Swift binaries.
- The newly observed infection chain starts with malicious DMG images and can stage payload delivery through an iCloud calendar.
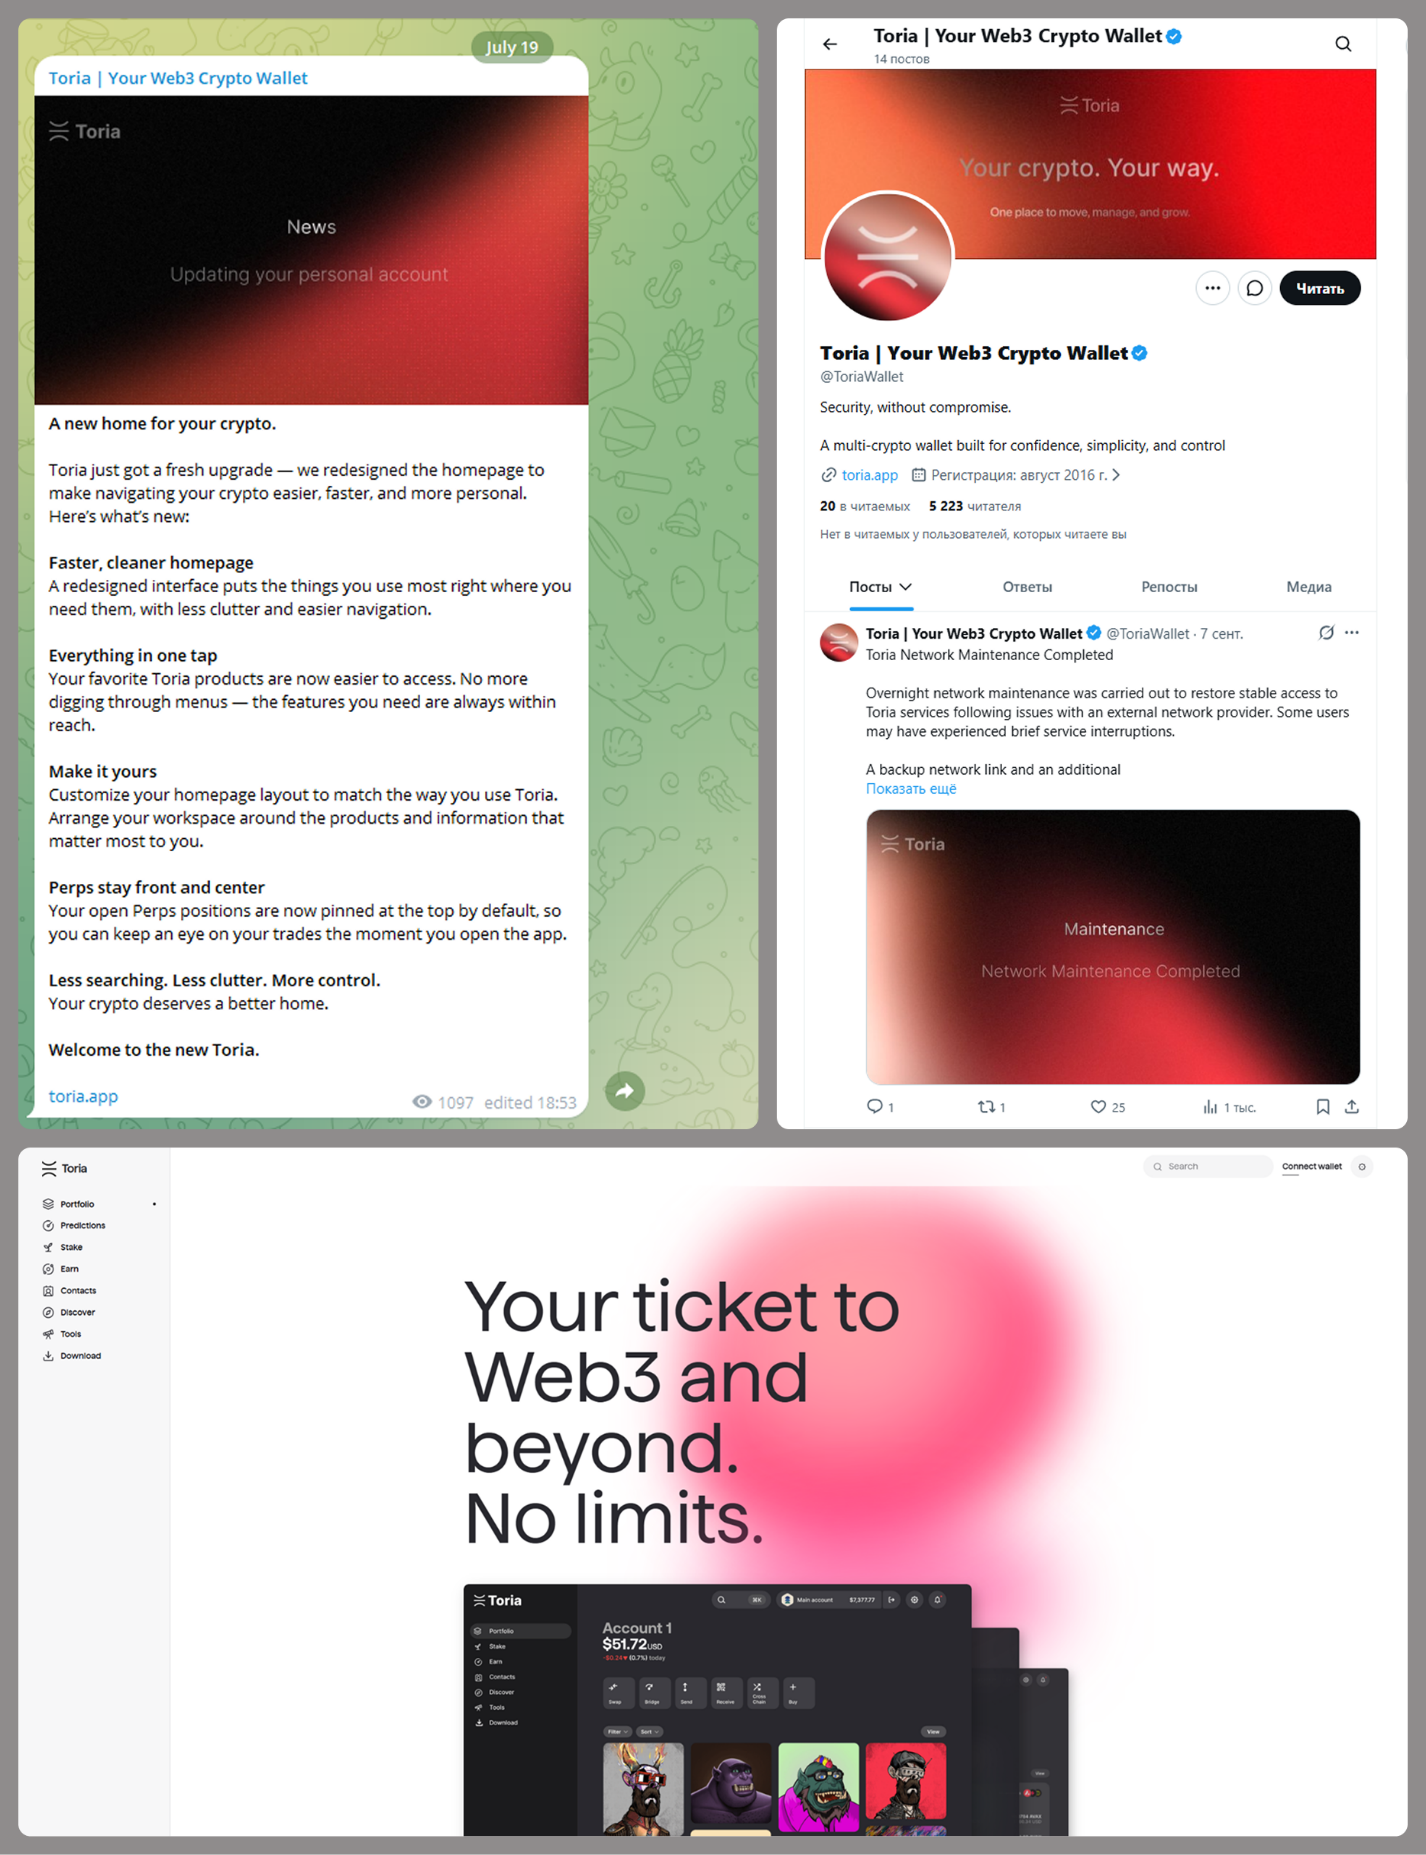
- Attackers disguise MacSync as fake or cracked apps, including a nonexistent crypto wallet called Toria, promoted via web pages, X, and Telegram.
- The chain uses multiple droppers/loaders, anti-debugging checks, ad-hoc signing, and removal of quarantine attributes to run on macOS.
- The infostealer collects browser data, crypto wallet data, Telegram data, keychain secrets, SSH/ZSH/AWS/Kubernetes/GIT configs, and other sensitive information.
- The backdoor supports persistence through LaunchAgents, ZSHRC, and Git hooks, and uses custom HTTP headers and token-based C2 communication.
- The campaign targets users likely tied to developers and crypto activity, increasing risk to both personal and corporate environments.
MITRE Techniques
- [T1059.002 ] Command and Scripting Interpreter: AppleScript – Used in earlier stages and in command delivery to execute malicious logic and wrappers (‘payloads were implemented as AppleScripts’; ‘extract the base64-encoded AppleScript script… and execute it’).
- [T1059.004 ] Command and Scripting Interpreter: Unix Shell – Used to run zsh, feed commands from the calendar, and execute scripts directly in memory (‘launches the interpreter to read commands from standard input (zsh -s)’).
- [T1027 ] Obfuscated Files or Information – Multiple strings, URLs, configs, and payloads were XOR/AES encrypted and hidden in overlays or static arrays (‘XOR-encrypted URL’; ‘Many strings… are XOR-encrypted’).
- [T1140 ] Deobfuscate/Decode Files or Information – Malware decodes XOR-encrypted URLs and decrypts AES-wrapped payloads and keys (‘decrypts it with the key’; ‘The ciphertext is decrypted with AES in GCM mode’).
- [T1218 ] System Binary Proxy Execution – Legitimate macOS utilities were abused to run attacker content, including xattr, zsh, ptrace, sysctl, and security (‘runs the xattr -cr command’; ‘launches the interpreter’).
- [T1105 ] Ingress Tool Transfer – Payloads and modules were downloaded from attacker servers and iCloud locations (‘download a .TAR.GZ archive from iCloud’; ‘retrieves the next-stage payload from the command-and-control server’).
- [T1132.001 ] Data Encoding: Standard Encoding – Base64 was used to encode keys and public keys sent to the server (‘The public key is encoded in base64’).
- [T1041 ] Exfiltration Over C2 Channel – Stolen data was uploaded to the command-and-control server via PUT requests and chunked uploads (‘The stolen data is uploaded to the command-and-control server via PUT requests’).
- [T1547.001 ] Boot or Logon Autostart Execution: Launch Agent – Persistence was established with a LaunchAgent named com.apple.finder.agent (‘A LaunchAgent named com.apple.finder.agent’).
- [T1546.008 ] Event Triggered Execution: System Profile / Shell Configuration Modification – Persistence was added by injecting commands into .ZSHRC and Git hooks (‘inject a malicious command into the .ZSHRC’; ‘global GIT pre-commit and post-checkout hooks’).
- [T1057 ] Process Discovery – The stealer collects a list of running processes as part of system information (‘list of installed applications and running processes’).
- [T1082 ] System Information Discovery – The stealer gathers hardware, device model, UUID, and other host details (‘device model, hardware, UUID, and so on’).
- [T1555 ] Credentials from Password Stores – The malware targets keychain and browser credential stores (‘Keychain file’; ‘browser data… saved logins and passwords’).
- [T1552.001 ] Unsecured Credentials: Credentials In Files – It searches for configuration files and history files that may contain secrets (‘Configuration files for SSH, ZSH, AWS, Kubernetes, GIT’).
- [T1562.001 ] Impair Defenses: Disable or Modify Tools – It uses anti-debugging and kills notification-related processes to hinder analysis and user notification (‘sets the PT_DENY_ATTACH flag’; ‘kills the BTMNotificationAgent, NotificationCenter, and BackgroundTaskManagementAgent’).
Indicators of Compromise
- [File hashes ] Sample identifiers and component hashes – 26a0f7cdb9f7dc5ace9a40af825b15382d69812584269699fade26622e6490c57, f97d24212fa6a21be0c4d211e10f044c, and other 8 hashes.
- [URLs ] Distribution, staging, and C2 infrastructure – hxxps://toria[.]app, hxxps://caldav.icloud[.]com/published/2/MTk1NDMwMDMzNTUxOTU0M1aHCZ-nMxiyGzBTzPiodOf44DtKJ6PpjftAG28_ui2NCYMpL_vu4pF4ddsJ8ysg0QI7pR0VEIEbZYdilVZRw08, and other 11 URLs.
- [Custom HTTP header values ] C2 authentication tokens used by the backdoor – b8b4b88205a8f594b95a841bc37342898f34cad8a5a9e4a22ce69a31a1208650, ff3ab9ef841630364818396f62e696b72aed162cf0b895b6643ef25dad79b51d.
- [File names ] Malicious or auxiliary components – .repair-run, osalogging.zip, and other named artifacts such as stage2.enc and Helper.pkg.enc.
- [Paths ] Persistence and storage locations – /tmp, /tmp/.sys-, $HOME/Library/Application Support/System, and $HOME/Library/Logs/.sysnotif-agent.log.
- [C2 API paths ] Backdoor endpoints – /v1/agent/ping, /v1/agent/refresh, /v1/asset//init, and /v1/agent/.
- [Magic strings / constants ] Protocol and config markers – SONOMAC1, AGNT1, BLD-150, and sn-dek-wrap-v1.
- [Encryption-related values ] Keys and IVs used across stages – 73 6f 6e 6f 6d 61 62 6c 64 07, cb09ff86cabde4f8cee2d3cdec370c623bfa6c2b72ae9750fc9a7b299c65d7ca, and other crypto material.
Read more: https://securelist.com/macsync-new-version/121383/