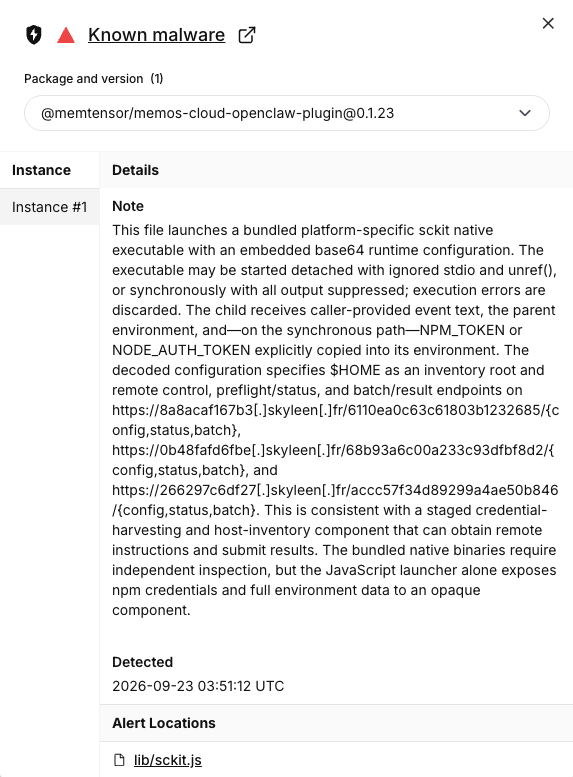
Malicious releases of MemTensor’s @memtensor/memos-cloud-openclaw-plugin and MemoryOS package were published on npm and PyPI, respectively, and they drop a cross-platform Go payload named sckit that searches developer home directories for secrets and sends them to C2 infrastructure under skyleen[.]fr. The compromise spans GitHub repository commits, registry releases, and release-tooling changes, putting users, CI runners, and developer machines at risk while exposing tokens and credentials from services such as GitHub, GitLab, AWS, Vault, SSH, and PyPI. #MemTensor #MemOS #OpenClaw #MemoryOS #sckit #skyleenfr
Keypoints
- Malicious releases were published for npm package @memtensor/memos-cloud-openclaw-plugin and PyPI package MemoryOS.
- The compromised versions are npm 0.1.21, 0.1.23, and 0.1.25, plus MemoryOS 2.0.34.
- Each malicious release bundles a cross-platform Go binary named sckit for Linux, macOS, and Windows on x64 and arm64.
- The payload launches automatically on package load or import and can run repeatedly during OpenClaw memory recall.
- sckit searches $HOME for secrets, including credential files, environment variables, and API tokens, then reports to C2 servers under skyleen[.]fr.
- The compromise also touched GitHub repositories and release tooling, suggesting attacker access to publishing workflows or tokens.
- Users are advised to pin clean versions, rotate exposed secrets, remove affected packages, and monitor for connections to the attacker infrastructure.
MITRE Techniques
- [T1195.001 ] Supply Chain Compromise: Compromised npm and PyPI releases were published and made latest, so default installs pulled malicious builds. [‘a default install from either registry therefore pulls a compromised build’]
- [T1105 ] Ingress Tool Transfer: The malicious packages delivered the bundled sckit payload to target systems as part of normal package installation. [‘Each malicious release bundles a Go binary named sckit’]
- [T1204.002 ] User Execution: Malicious Code Execution: The payload runs when the plugin starts or when the Python module is imported, meaning normal application use triggers execution. [‘The PyPI package starts it as soon as the memos module is imported’]
- [T1056.001 ] Input Capture: Keylogging: The npm plugin passes user prompt text to the payload, exposing user input to the attacker-controlled binary. [‘runs again for every recall, with the prompt text in SCKIT_EVENT_TEXT’]
- [T1005 ] Data from Local System: The payload searches developer home directories and credential files for secrets stored locally. [‘the binary searches $HOME for credentials’]
- [T1041 ] Exfiltration Over C2 Channel: Collected secrets are reported to command-and-control servers under skyleen[.]fr. [‘reports to command and control (C2) servers under skyleen[.]fr’]
- [T1543.002 ] Create or Modify System Process: The launchers start sckit detached or in a new session so it continues running in the background. [‘starts it in the background’, ‘start_new_session=True’]
- [T1068 ] Exploitation for Privilege Escalation: Not directly shown as privilege escalation, but the package logic marks binaries executable before running them on import. [‘marks it executable (0o700) if needed’]
- [T1588.002 ] Obtain Capabilities: Tool: The actor appears to have embedded a custom payload to steal secrets and potentially republish packages using stolen tokens. [‘may be able to republish packages with stolen registry tokens’]
Indicators of Compromise
- [Package names and versions ] Malicious registry releases – @memtensor/memos-cloud-openclaw-plugin 0.1.21, 0.1.23, 0.1.25; MemoryOS 2.0.34
- [Domain ] C2 infrastructure – skyleen[.]fr, 8a8acaf167b3[.]skyleen[.]fr and 0b48fafd6fbe[.]skyleen[.]fr
- [Domain ] Additional C2/CI endpoints – c747d139e7e9[.]skyleen[.]fr, 73376a079d87[.]skyleen[.]fr and 10729e014d0e[.]skyleen[.]fr
- [URL patterns ] C2 API paths – hxxps://[.]skyleen[.]fr//config, /status, /batch
- [URL pattern ] CI helper endpoint – hxxps://10729e014d0e[.]skyleen[.]fr/eb57efaa7365698fc1e4decc/initial-ci-v2
- [SHA256 hash ] PyPI wheel and sdist – 39ee644406829a4b630b31759c20478bc22d576d6a59b253ed86f72c360aa5ef, 92b46d18fc553c494eda714f204459edb74c205bf53b18a9092bcf02c7a6c5be
- [SHA256 hash ] npm sckit binaries – 381ac6dc1715d9298fe81b2a53a11f7b7d78e361ee3a6619ad54f8c4b062cc18 and e077c387b223811064b7bbc5a55a0182fca9bf50894f949ff284d4be87d44b26, plus 4 more hashes
- [SHA256 hash ] PyPI sckit binaries – c1b0998347b489582bae7b7f4930f9831d9ef4b6bc150cfd488ee1a43272dd36 and 8f647f17a1934679c4095e21bee2b9bd83e28476603758bc91408a0c8443e3b4, plus 4 more hashes
- [File names and paths ] Embedded payload files – .sckit/-/sckit, sckit.exe, lib/sckit.js, lib/tls-trust.js, memos/_stage0.py, memos/_sckit_config64
- [File names and paths ] Release-pipeline artifacts – memos/_pypi_bridge.sh, memos/_initial_ci_delivery.py, sckit_poetry_build.py
- [Command line and environment ] Runtime artifacts – sckit stage0 –config64 eyJzY2hlbWEiOiJzY2tpdC5ydW50aW1lLnYxIi…, SCKIT_EVENT_TEXT
Read more: https://socket.dev/blog/memtensor-compromise