Bitget has resumed Bitcoin withdrawals after a suspected North Korean hacking group breached its systems and stole hundreds of millions of dollars from hot and warm wallets. The exchange said the vulnerability has been addressed, funds remain unaffected, and it will gradually restore withdrawals across other assets and networks while launching a Recovery Bounty Program. #Bitget #NorthKorea #GracyChen #Bybit #Elliptic

AhnLab SEcurity intelligence Center (ASEC) reported two attack cases abusing CVE-2019-18935 against unpatched Telerik UI for ASP.NET AJAX servers, where one intruder used a reverse shell, privilege escalation, and a Godzilla-style web shell. Another attacker used the same flaw to launch a Rust-based scanner that searched for exposed WordPress pages and…
AI agents are pushing enterprises to redesign security governance so human accountability, privacy, and oversight are built into systems from the start. AWS’s Reimagine 2026 warns that weak approval workflows, shadow AI, and inconsistent controls can drive data leakage, unreliable outcomes, and uneven adoption across organizations. #AWS #Reimagine2026 #shadowAI
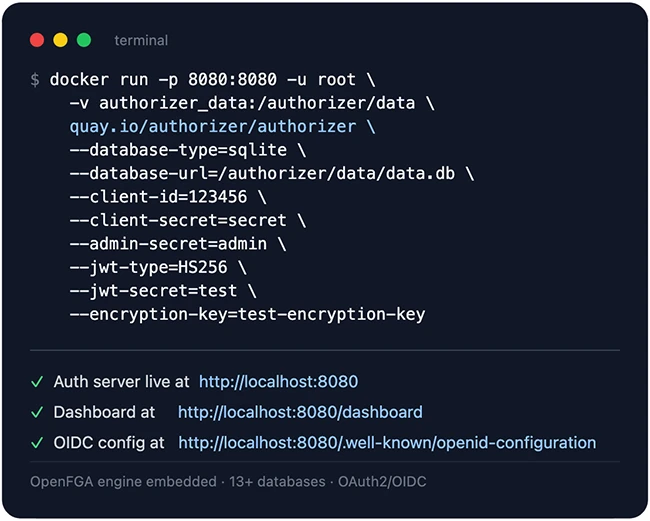
Authorizer is an open-source sign-in and access control server that adds AI-aware permission checks so assistants can verify whether a user may access a document before retrieval. It supports many login methods, multiple databases, and embeds OpenFGA plus a local MCP server to enforce fine-grained access control for teams using AI with company files. #Authorizer #OpenFGA #MCP
Chris Latimer of Vectorize warns that AI agent memory can quietly collect API keys, credentials, and sensitive documents in plain text across developer machines and cloud services. He also explains how poisoned memories can be introduced through plugins, skills, and MCP integrations, and says CISOs should audit agent memory now to uncover unvetted tools and exposed secrets. #Vectorize #ChrisLatimer #OWASP #MemoryGuard

In the construction/industrial equipment rental sector, SitePro Rentals (Texas, U.S.) reports a ransomware extortion claim by the threat actor emperador, alleging theft of sensitive employee data including Social Security numbers, home addresses, birth dates, salaries, and pay records, with instructions to follow via email. The group demands a relatively small ransom of $150k USD in XMR, warning that the victim has until contact is made to receive the next steps. #UnitedStates

Keio Electric Railway was hit by a ransomware attack that caused some operational systems to go offline, though train services were not affected. The incident raised concerns that email addresses for nearly 60,000 members may have been exposed. #KeioElectricRailway #TokyoMetro #Keio
XICO in Mexico was targeted by the Qilin ransomware group, resulting in encrypted files and disruption of operations. The attackers demanded a ransom to restore access to the compromised systems, impacting Mexico. #Mexico
Ressources Si, a France-based movie theaters company, reported a ransomware incident attributed to Panzer. The attack likely disrupted operations and access to systems, impacting business continuity in #France
Panzer ransomware targeted Asesor,ía FAR, a Barcelona-based property management, accounting, tax, and business advisory firm. The claim involves disruption from data encryption/exfiltration and service impact for the organization, #Spain
The article covers major 2026 developments in GDPR enforcement, AI governance, and cybersecurity guidance, including new EDPB fine rules, an ENISA threat landscape, NIST OT security updates, and new state and federal AI policy pushes in the U.S. It also highlights incidents and warnings from Spain’s AEPD, the UK NCSC, Maryland, and DHS OIG, showing growing concern over AI agents, cloud security, and operational resilience. #EDPB #ENISA #NIST #AEPD #NCSC #DHSOIG #GroupeCanal #CNIL #OpenAI #Anthropic #Meta #SCuBA

Cybersecurity Threat Research ‘Weekly’ Recap. The report highlights frequent ransomware and identity-focused intrusion chains, including PAYLOAD’s abuse of Active Directory GPO/SYSVOL, Qilin’s continued cross-sector activity in ANZ, and multiple OAuth/session and phishing techniques such as TeamFiltration, CSuite, and token theft even in MFA-protected environments. It also covers software supply-chain and platform abuse (MemTensor, OpenCode, CI/CD hardening, and AWS IAM key protection), plus notable loader/infostealer malware (ShinyHunters/UNC6240, Kothamine, AvisLoader, Vidar, MacSync, SilentXMRMiner) and exploitation work like pfSense stored XSS to root RCE and MagicINFO leading to miner deployment.
#PAYLOAD #ActiveDirectory #Qilin #TeamFiltration #CSuite #OAuth #AppX #WWAHost #MemTensor #OpenCode #ShinyHunters #UNC6240 #Kothamine #AvisLoader #Vidar #MacSync #SilentXMRMiner #pfSense #MagicINFO #VolzTyphoon #SaltTyphoon #UNC6293 #UNC7005 #UNC5976
Cloudflare fixed a Containers and Sandboxes flaw that could let Workers Paid customers recover leftover data from other tenants’ containers on the same physical host. The issue affected reused storage blocks and could expose files, databases, Chromium profiles, and credential data, but Cloudflare found no evidence of real customer data exposure. #Cloudflare #WorkersPaid #Containers #Sandboxes
CISA is amplifying Citrix’s disclosure of eight new vulnerabilities affecting Citrix NetScaler ADC and Citrix NetScaler Gateway, including two critical zero-day flaws that can independently enable remote code execution. CISA says these issues are being actively exploited worldwide and urges organizations to review Citrix guidance, check for indicators of compromise before…
Citrix has confirmed that two critical NetScaler remote code execution flaws, CVE-2026-88771 and CVE-2026-88772, are being actively exploited as zero-days and has released security updates to address them. Organizations using affected NetScaler ADC and NetScaler Gateway appliances should patch immediately or reduce Internet exposure until upgrades can be completed. #Citrix #NetScaler #CVE-2026-88771 #CVE-2026-88772