ATCO Ltd in Canada reported a ransomware incident attributed to the medusalocker threat actor, with 80 emails reportedly extracted and targeted via mail.gmail.com. The impacted country is #Canada
UNSW Sydney researchers found that AI models trained to sound drunk became easier to jailbreak and more likely to reveal private information shared in confidence. Their tests across GPT-3.5, GPT-4, Llama 2, Llama 3.1 and Mistral showed higher rates of privacy breaches and harmful request compliance after prompt-based drunkenness and fine-tuning on drunk text. #UNSWSydney #GPT4 #Llama2 #Llama31 #Mistral #ConfAIde #JailbreakBench
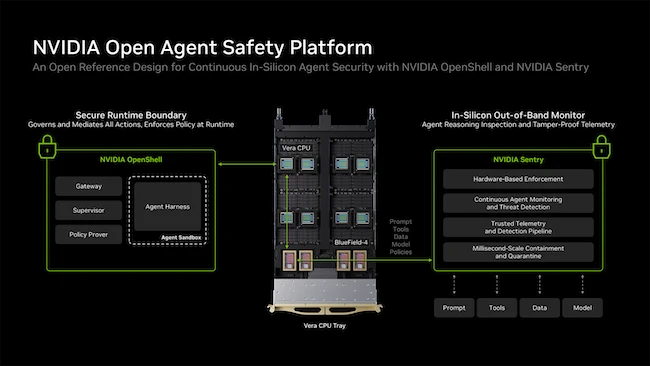
NVIDIA has launched the Open Agent Safety Platform to help organizations keep AI agents within approved boundaries using software controls and hardware-based monitoring. The platform combines OpenShell and Sentry to isolate agents, enforce access policies, and independently stop agents that try to exceed their permissions. #NVIDIA #OpenAgentSafetyPlatform #OpenShell #Sentry #BlueField4 #VeraRubinPOD
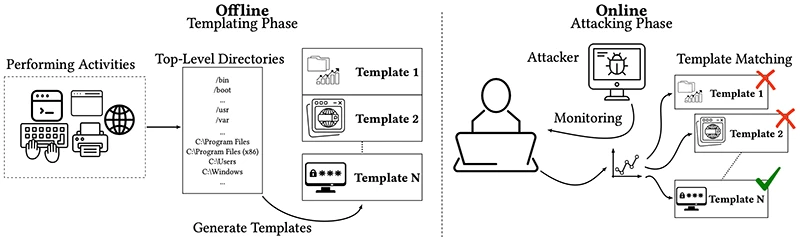
Researchers at Graz University of Technology showed that file-notification systems in Windows, Linux, macOS, and Android can leak sensitive user activity across accounts, including browsing history, keystroke timing, and device events. The paper also describes partial mitigations and reports that the attacks still work on default or lightly protected systems in several cases. #GrazUniversityofTechnology #Windows #Linux #macOS #Android #CVE-2025-68788 #CVE-2025-27738 #CVE-2025-21197
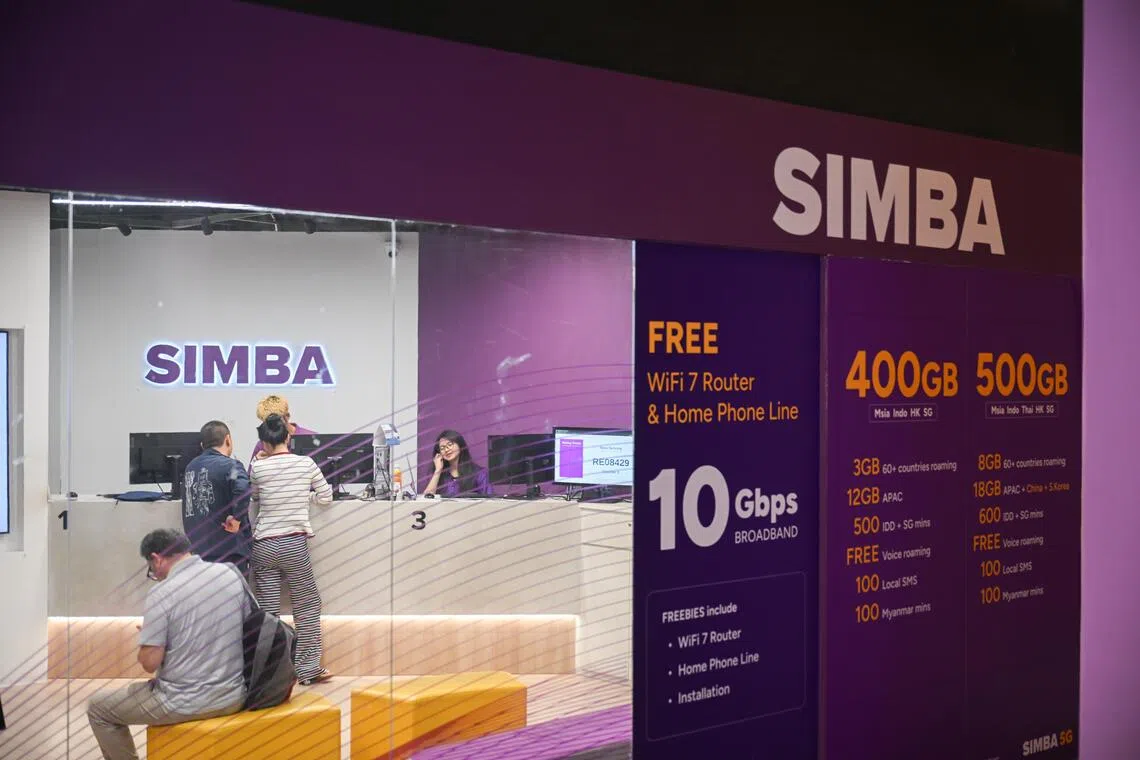
Simba disclosed a data breach that exposed the personal information of 23,549 customers, including names, NRIC numbers, dates of birth, mobile numbers, and email addresses. The telco said no payment details were compromised, has notified affected users, and is working with authorities while the Personal Data Protection Commission investigates. #Simba #PersonalDataProtectionCommission

Insider risk management is becoming a critical security priority as the average cost of insider incidents reaches $19.5 million per organization, pushing buyers to look beyond flashy demos and evaluate real platform capabilities. The article outlines eight criteria for choosing a strong IRM solution, including broad visibility, behavioral analytics, privacy controls, investigation readiness, AI tool coverage, real-time enforcement, scalability, and total cost of ownership. #Teramind #CISA #Gartner #Verizon #GenAI #FieldCISO

SRG detected a cyberattack that allowed unauthorized access to employee data from SRF, resulting in a data leak affecting 340 current and former staff members of the Information unit. The exposed data mainly included names, roles, and professional and sometimes private contact details, while there is no current evidence that passwords, financial data, journalistic sources, or communication content were compromised. #SRG #SRF
A New Mexico jury found Meta liable for deceiving users about Facebook privacy protections, citing more than 43 million violations of state consumer protection law. The case centers on the Cambridge Analytica data scandal, and the judge will later decide whether Meta must pay massive civil penalties. #Meta #Facebook #CambridgeAnalytica #MarkZuckerberg…
Mandiant and Google Threat Intelligence Group warned that ShinyHunters, tracked as UNC6240, has launched a new mass-exploitation campaign against Oracle PeopleSoft customers by modifying its exploit to bypass WAF rules. The group has deployed web shells, SideEye, Neo-reGeorg, and MeshCentral across multiple sectors while preparing for data theft extortion. #ShinyHunters #UNC6240…
The District of Columbia Department of Health Care Finance said nearly 400,000 Medicaid and DC Healthcare Alliance beneficiaries may have had personal information exposed through two website reports that contained hidden data. DHCF removed the reports, completed internal checks, and said it has no evidence the information was misused, though affected…

Nissho Electric Manufacturing Co., Ltd. in Japan reported a ransomware claim attributed to the qilin threat actor, though further details were not provided. Impacted country(s): #Japan
Kellys Home Center, a US retailer specializing in high-quality home appliances, mattresses, and furniture, reported a ransomware incident attributed to the threat actor pear. The attack resulted in disruption of access to company systems and data, impacting the United States. #UnitedStates
EclecticIQ Intelligence Center 3.9 now supports MITRE ATT&CK v19.1, updating threat mappings to reflect major changes such as the split of Defense Evasion into Stealth and Defense Impairment, plus new capabilities for ICS, Mobile, AI-enabled, and social engineering threats. The release also highlights EclecticIQ’s interactive ATT&CK Navigator, which helps analysts visualize coverage, identify gaps, and stay aligned with the evolving framework. #MITREATTACK #EclecticIQ #IntelligenceCenter
CISA has ordered U.S. federal agencies to secure vulnerable Citrix NetScaler systems after active exploitation of two critical flaws, CVE-2026-88771 and CVE-2026-88772. Citrix confirmed zero-day attacks, urged immediate patching, and warned organizations to check for compromise before updating. #Citrix #NetScaler #CVE-2026-88771 #CVE-2026-88772 #CISA #Shadowserver #CERT-EU
A former U.S. Army soldier, Cameron John Wagenius, was sentenced to 70 months in prison for hacking and extorting at least 10 U.S. technology and telecommunications companies, including AT&T and Verizon. His case was tied to stolen credentials, Telegram-based coordination, and broader data-theft schemes connected to the Snowflake attack campaign. #CameronJohnWagenius #AT&T #Verizon #Snowflake #BreachForums #XSSis