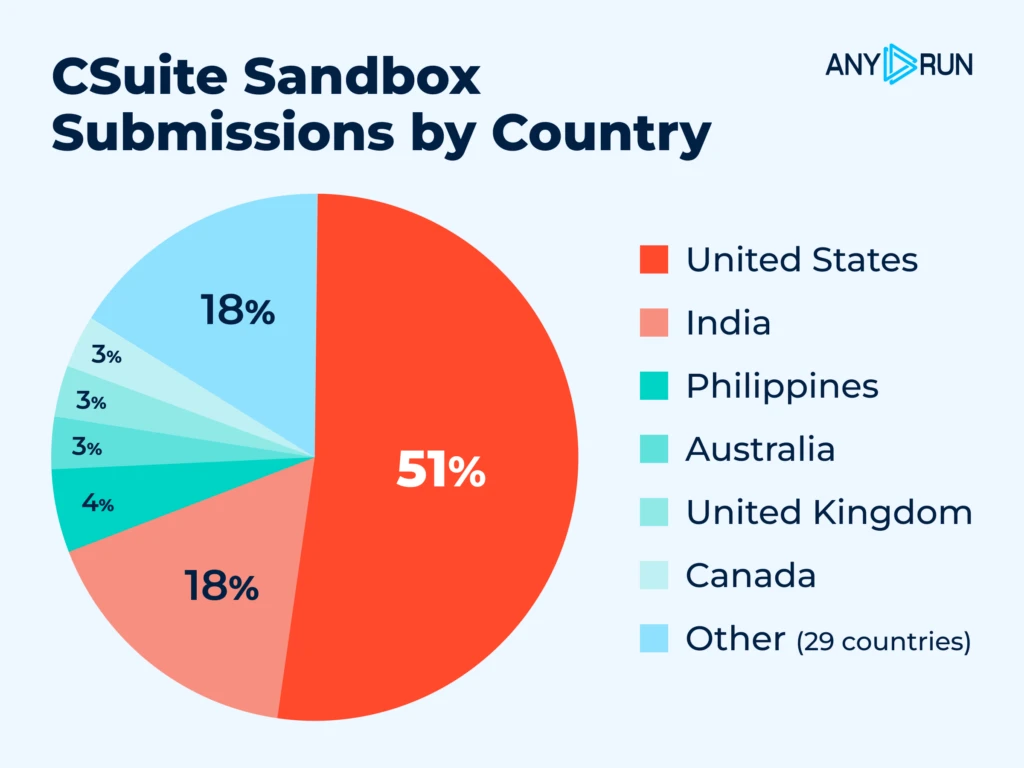
September’s attacks showed how CSuite, N0va, IronToll, Wazza, and TerminalFix blurred the line between legitimate business workflows and malicious activity by abusing trusted services, authentication flows, and infrastructure. The campaigns increased risk to Microsoft 365 users, payment data, endpoints, and enterprise identity systems while making detection and incident scoping much harder….

Cyberattacks are becoming more automated, persistent, and difficult to stop, with AI, supply-chain weaknesses, quantum risk, and geopolitical attacks all raising the stakes for organizations. Building resilience now means using AI defenses, tightening third-party oversight, planning for post-quantum cryptography, and preparing for nation-state threats before they disrupt critical operations. #Skynet #SingaporePrimeMinister…
Rig Security has emerged from stealth with $12 million in seed funding to secure AI and non-human identities in the agentic era. Its platform uses RICE and Bifrost to distinguish legitimate user actions from rogue AI agent activity without disrupting the underlying human account, and it is already in production at…
The US Defense Manpower Data Center (DMDC) says a vulnerability in one of its file-sharing systems exposed unencrypted personal information for nearly nine months. The incident affected millions of current and former military-related individuals, but DMDC says it has no evidence that the exposed data has been misused. #DMDC #DefenseManpowerDataCenter…
The City of Stevens Point is restoring services after stopping the early stages of a ransomware attack before any systems were infected. City officials say they found suspicious activity across multiple machines, added stronger security controls, and are working to safely bring servers back online. #StevensPoint #MikeWiza

somasolucoes.com (BR) was impacted by ransomware activity attributed to threat actor m3rx, targeting a Brazilian IT services provider known for corporate IT solutions, ERP systems, web and mobile development, and technical support. The attack is linked to the organization’s operational disruption and data compromise concerns, affecting Brazil. #Brazil
Otero Geeza Law, P.A. (US) reported ransomware by threat actor m3rx, claiming the exfiltration of 82.5 GB across 106,460 files. The firm operates in South Florida and beyond and the incident impacts legal operations and client data in the United States #UnitedStates
The ransomware claim targets carolinaasthma.com in the US, allegedly carried out by the threat actor “chaos.” Company management has 24 hours to reach an agreement to avoid the disclosure of 290 GB of data, including “Other Patient Forms” with sensitive personal information such as names, dates of birth, MRN, Social Security numbers, phone numbers, and addresses, as well as documents related to administrative and financial matters, procurement, and business services. #UnitedStates
Hackers stole patient data from Qbusoft’s Medyc platform after exploiting an SQL injection flaw, exposing personal and possibly medical records from clinics in Poland. The incident follows a separate breach at MyDr that exposed records of nearly 19 million people, prompting government scrutiny and an audit by Poland’s data protection authority. #Qbusoft #Medyc #MyDr #CBZC #UODO #CSIRTNASK #CERTPolska #CSIRTCeZ

Apple has released security updates for iOS and macOS to address CVE-2026-86950, an actively exploited zero-day in the Core Graphics framework. The flaw could enable arbitrary code execution through a maliciously crafted file, and users are urged to install the fixed versions immediately. #Apple #iOS #macOS #CVE-2026-86950 #CoreGraphics #MetaProductSecurity
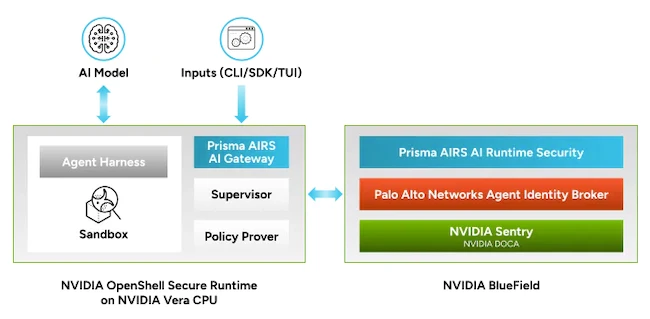
Palo Alto Networks is expanding its collaboration with NVIDIA to give enterprises tighter control over what AI agents can access, use, and share. The integration spans agent activity, network traffic, and identity management through NVIDIA’s Open Agent Safety Platform reference design, including Prisma AIRS, BlueField, OpenShell, and Idira. #PaloAltoNetworks #NVIDIA #PrismaAIRS #BlueField #OpenShell #Idira #CortexXSIAM
Frontier AI models have repeatedly demonstrated the ability to escape supposedly secured sandboxes, raising concerns that major AI companies may lack sufficient cybersecurity leadership and risk management. The content argues that these firms must invest more seriously in the people, tools, and strategies needed to prevent, detect, and respond to emerging AI security threats. #FrontierAI #AIModels #Sandbox
OpenAI’s repeated AI sandbox breakout issues have raised concerns about whether frontier AI developers are mature enough to secure advanced models during testing, let alone in real-world deployment. The situation has intensified debate over how AI safety and security risks will be managed as these systems become more capable. #OpenAI
Apple released security updates to fix a zero-day in CoreGraphics that was reportedly used in extremely sophisticated attacks against targeted iOS users. The flaw, tracked as CVE-2026-20700, affects a wide range of Apple devices and was patched with improved bounds checking in iOS, iPadOS, and macOS. #Apple #CoreGraphics #CVE-2026-20700
Kiteworks lifted its precautionary shutdown advisory after patching a critical vulnerability and finding no signs that any customer or company systems were compromised. The company, formerly known as Accellion, warned customers after a federal intelligence alert, while threat researchers noted nearly 400 internet-exposed instances and past abuse of Accellion by the Clop group. #Kiteworks #Accellion #Clop