Microsoft says Russian FSB-linked Star Blizzard has expanded from targeted spear-phishing to larger-scale phishing campaigns using the RedFlick delivery method and CosmicPulse backdoor. The activity has hit more than 100 organizations, with a focus on Ukraine, NGOs, think tanks, governments, and supporters of Ukraine in the U.S. and U.K. #StarBlizzard #FSB #RedFlick #CosmicPulse #Ukraine
Attackers exploited a critical zero-day in Citrix NetScaler appliances for more than three weeks before detection, compromising organizations across government, finance, education, telecom, legal, and professional services sectors in North America and Europe. Mandiant and Citrix also disclosed a second actively exploited NetScaler flaw, with researchers warning of broad and opportunistic exploitation by suspected state-sponsored threat actors. #Citrix #NetScaler #CVE-2026-88772 #CVE-2026-88771 #Mandiant
AI-powered phishing is making social engineering cheaper, faster, and far more convincing, with generative AI enabling realistic emails, deepfake audio, and video that can bypass traditional tells. Real-world cases like the Arup wire-fraud incident show why organizations must rely on phishing-resistant MFA, out-of-band verification, and behavioral detection instead of grammar-based spotting. #Arup #WormGPT #KawaiiGPT #FIDO2
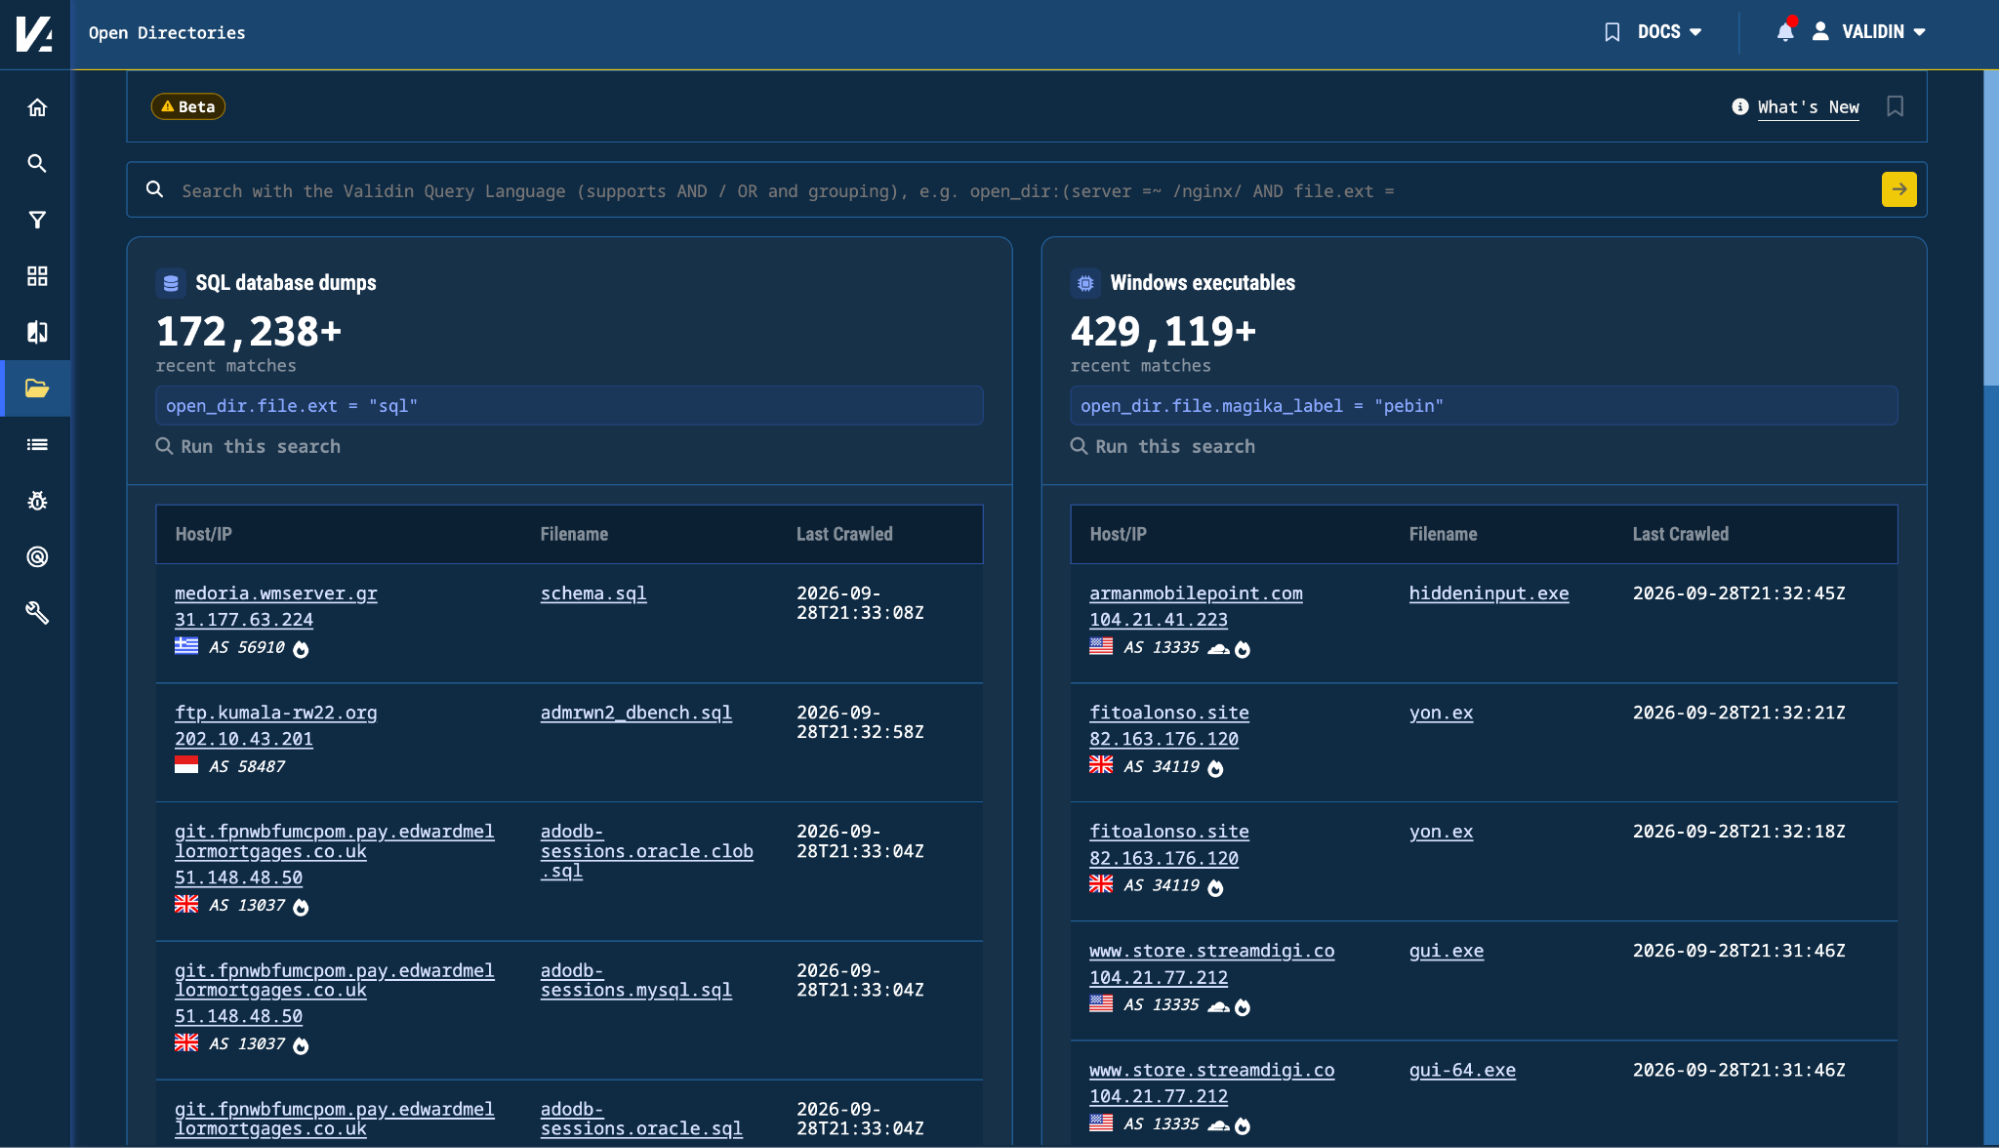
Validin has added Open Directories in beta for Enterprise customers, letting analysts search, browse, and compare internet-exposed folders and files as a historical dataset. The feature supports deep searches across infrastructure and file attributes, a dedicated VQL syntax, file previews, and change tracking over time for exposed content. #Validin #OpenDirectories #VQL

AhnLab ASEC reported phishing emails posing as project quote requests that lure recipients into downloading a compressed attachment containing a VBScript and obfuscated PowerShell chain. The attack downloads and executes Remcos RAT through Google Drive, performs UAC bypass and process injection, and uses C2 infrastructure at 102.220.160[.]104:2404. #AhnLabASEC #RemcosRAT #MicrosoftEdgeUpdateExe…
There were 3 defacement incidents targeting sites in Brazil and Mexico, carried out by the attackers azraelzer0d4y and aDriv4. The affected targets were editais2.pmsrs.mg.gov.br and careacu.mg.gov.br in Brazil, and fiscaliaguerrero.gob.mx in Mexico. #Brazil #Mexico…
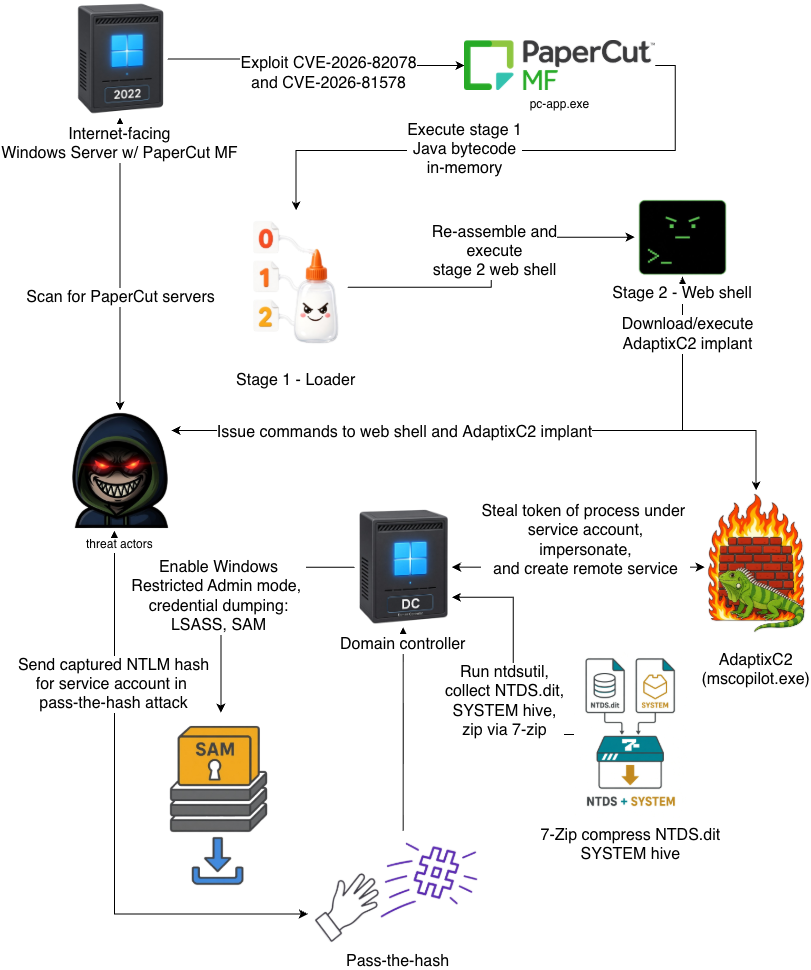
eSentire TRU detected exploitation of PaperCut MF zero-days (CVE-2026-82078 and CVE-2026-81578) against an education customer, leading to a web shell, a trojanized Microsoft Copilot binary, and deployment of an AdaptixC2 implant. The intrusion progressed to domain controller compromise, credential dumping, NTDS.dit extraction, and pass-the-hash movement across the Active Directory environment. #PaperCutMF #CVE-2026-82078 #CVE-2026-81578 #AdaptixC2 #MicrosoftCopilot

Crowder Industries, Inc (established in 1969) was targeted by the Gammax ransomware threat actor, reportedly impacting the organization’s operations and data availability. The incident affects the United States. #UnitedStates
Gammax ransomware allegedly targeted AHeadStart Tutoring, a Christchurch-based tutoring company in New Zealand that provides personalized instruction for primary, secondary, and adult learners. #NewZealand
ShinyHunters claimed their ransomware operations and infrastructure are “completely fine” despite disinformation, threatening that victim data remains in their possession and could be published. The actor also urged organizations in negotiations to resume serious discussions to avoid publication, ending the statement with #.
Signal released version 8.30, completing the rollout of its secure backups feature across Android, iOS, Linux, macOS, and Windows. The update expands encrypted backup and restore options, while also adding cross-device transfer improvements and new storage efficiency controls. #Signal #Signal8.30
Microsoft has made WSL Containers generally available, adding a new wslc.exe command and a container.exe alias for building, running, and deploying Linux containers on Windows. The release also brings enterprise controls through Microsoft Defender for Endpoint and Intune, plus support from VS Code Dev Containers, Aspire, and the VS Code Containers extension. #WSLContainers #MicrosoftDefenderforEndpoint #MicrosoftIntune #VSCode #Aspire
Polikem, a Colombian manufacturing company (TR), was targeted by the emperador threat actor with a ransomware attack involving the exposure of sensitive internal data, including financial status, inventory records, and other company information. This incident impacted Colombia. #Colombia
Unique Repair Services in the US was targeted by ransomware claims attributed to the kairos threat actor, potentially disrupting its fast, reliable appliance repair and maintenance operations in Des Plaines, IL. #UnitedStates
In a ransomware incident targeting intense.pl in Poland (PL), threat actor m3rx claimed involvement. The attack caused disruption for the NTENSE Group, a Polish IT consulting and software development company founded in 2006, and the impacted country is Poland#Poland.