
CISA has added CVE-2026-104286, a critical Fortinet FortiMail flaw, to its Known Exploited Vulnerabilities catalog after confirming active exploitation in the wild. Fortinet says the issue can let unauthenticated attackers write arbitrary files on affected FortiMail systems, and it has issued mitigations and upgrade guidance for impacted versions. #Fortinet #FortiMail #CVE-2026-104286…
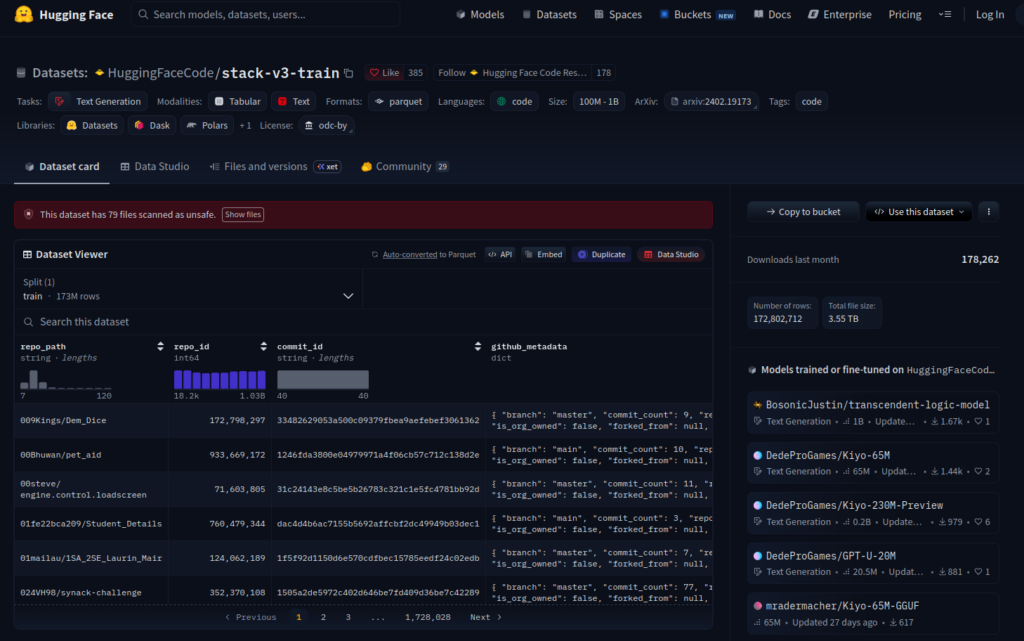
Truffle Security found 543,699 still-valid credentials inside code from public GitHub repositories after analyzing The Stack v3 dataset, which was built from about 224 million repositories. The research showed exposed API keys, access tokens, database credentials, and service accounts, and recommends revoking or rotating any leaked credentials because they may already exist in forks or copies of the repository. #Truffle Security #GitHub #The Stack v3 #Hugging Face #TruffleHog

Superior Plating Technology Co., Ltd. (superiortec.com) reportedly became a ransomware victim in an incident attributed to the morpheus threat actor, impacting its Taiwanese industrial metal surface treatment and electroplating operations with estimated $30M in revenue exposure. The attack affected the company’s ability to maintain normal production and IT operations across the organization in Taiwan. #Taiwan
kairos ransomware reportedly targeted the Slate Valley Unified School District in Vermont, US. The claim states the actor encrypted data, including 647 GB of SQL databases with personal and medical information about students and employees. #UnitedStates
Barracuda allegedly targeted Automovil Club del Ecuador ANETA (EC) and claims access to sensitive customer data, applications, and photos, along with financial documents and a complete dump of the mail server emails for the entire year. The actor states the stolen information is being sold, impacting Ecuador. #Ecuador
Config Connector (KCC) removes the need for developers to handle Google Cloud credentials by letting Kubernetes controllers manage resources on their behalf through GitOps. But if KCC has broad organization-level IAM permissions, a user with limited Kubernetes access can exploit the confused deputy flaw in ConfigConfusion to gain Google Cloud control. #ConfigConnector #KCC #ConfigConfusion #WorkloadIdentity #GoogleKubernetesEngine
Metalware Corporation (CA) in Montreal, Quebec—an established industrial steel shelving and storage systems manufacturer—was targeted by the ransomware threat actor known as thegentlemen. The attack on Metalware impacted Canada #Canada
The ransomware claim states that the threat actor qilin targeted XICO in Mexico, resulting in unauthorized access and data encryption. The incident is reported to have impacted MX #Mexico
MetaMask has disclosed an ongoing infrastructure security incident affecting part of its internal systems, but says there is no immediate threat to MetaMask wallets. As a precaution, MetaMask Staking is exiting affected Ethereum validators in coordination with clients and partners, while Lido Finance says the process may result in missed rewards and possible penalties. #MetaMask #Consensys #LidoFinance #Ethereum
CIS CTI tracked Remus infostealer distribution from March to September 2026, showing how the MaaS operation uses browser-session theft, EtherHiding C2 rotation, and multiple delivery chains to spread the payload. The investigation tied Remus to Lumma Stealer lineage and highlighted activity involving ClickFix, PLYCHIP, DonutLoader, GoFlateLoader, LandUpdate808, and domains such as…
Hospital Hermilio Valdiz in Peru, operated by MINSA, was targeted in a ransomware claim attributed to the ransomhouse threat actor, disrupting services at the public psychiatric hospital in Lima. The facility delivers specialized mental health and related medical care for low-income patients, many covered by SIS, with the impacted country(s) being #Peru
The netrunner ransomware incident allegedly targeted Main Place Mall in Malaysia, part of a mixed development featuring residences, leisure, retail, and dining. The threat actor is reported to have compromised systems at the victim site, impacting operations in Malaysia. #Malaysia
Incransom claims to have compromised a substantial volume of sensitive information belonging to Sangre de Cristo Electric Association (SDCEA), including US customer PII, financial/payment data, utility account details, and highly sensitive authentication and security information such as control-system credentials, API keys, and OT security configurations. The leaked data is also alleged to cover SDCEA’s energy infrastructure and operational technology environment, including electrical distribution systems, substations, transformers, outage information, and SCADA/EMS-related environments. #UnitedStates
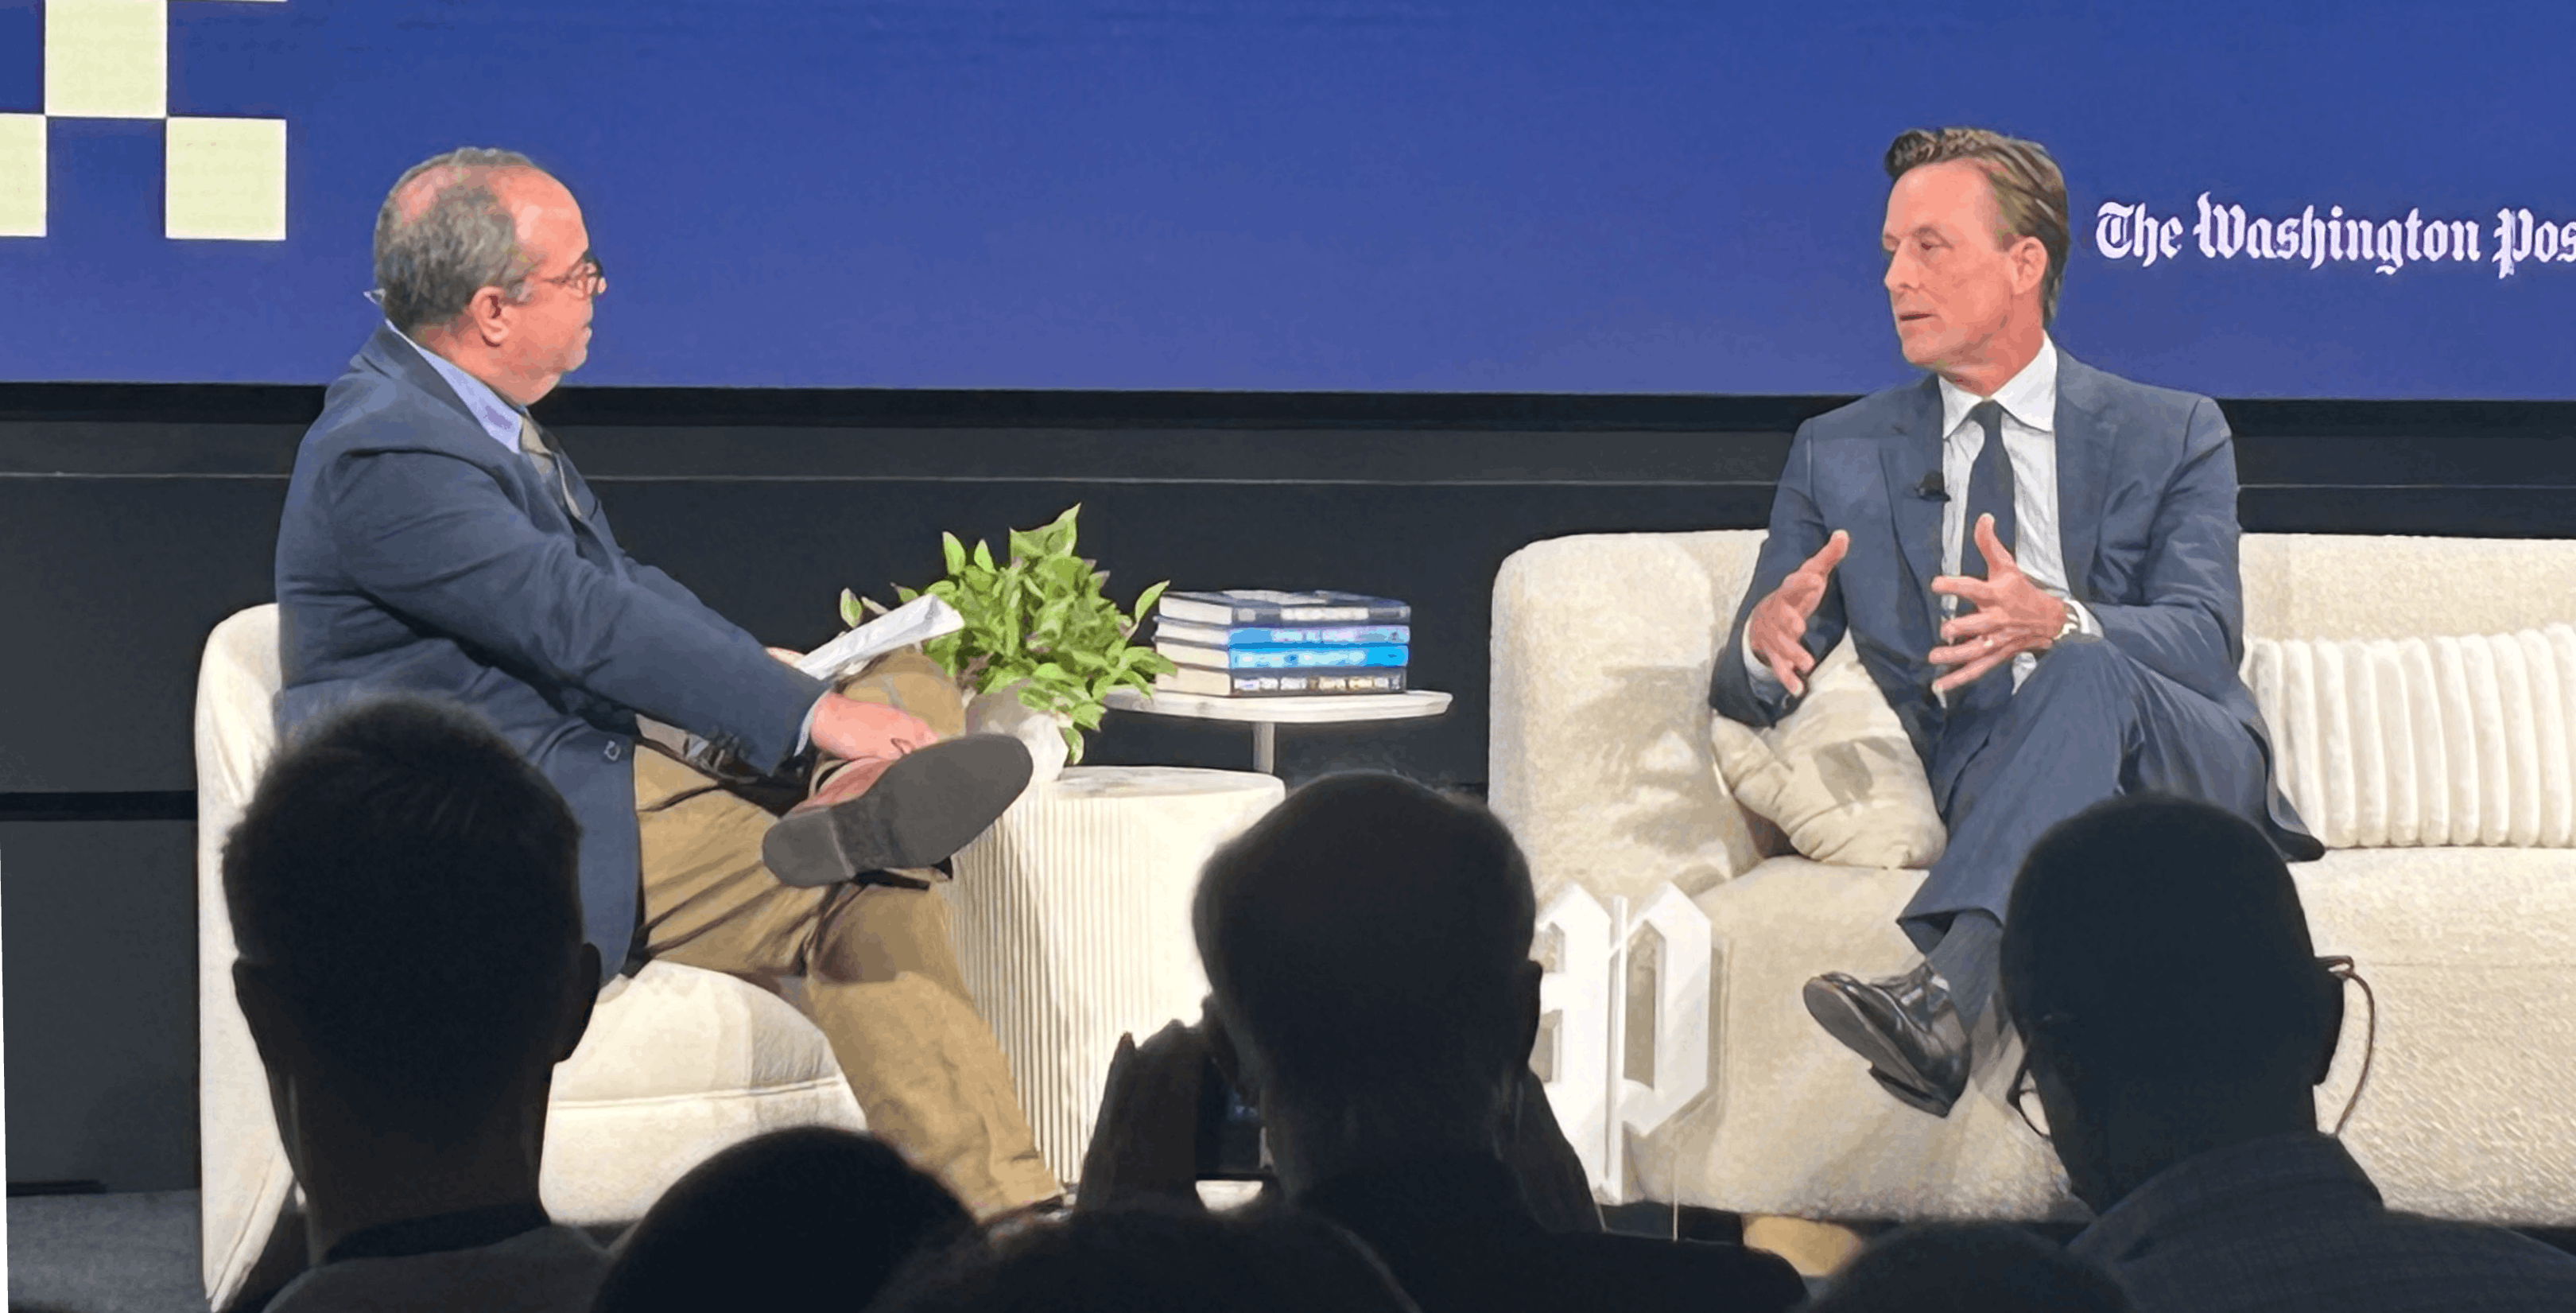
Sean Cairncross said the U.S. must work closely with industry to balance AI innovation and security while staying ahead of China and other adversaries. He highlighted collaboration on testing, guardrailing, and sandboxing through CAISSI, and pointed to incidents involving OpenAI, Hugging Face, Moonshot AI, and Anthropic as evidence of the need for stronger system protections. #OpenAI #HuggingFace #MoonshotAI #Anthropic #CAISSI

Authorities arrested the alleged 16-year-old leader of KillSec and two other members as part of Operation KillSwitch, a coordinated international effort targeting the group’s infrastructure and members. Investigators say the teen-run extortion crew compromised about 500 organizations since 2024 and stole large amounts of data for extortion, including from Instituto de Ojos, US BioTek Laboratories, and Accelerated Academy. #KillSec #OperationKillSwitch #Europol #FBI #JusticeDepartment