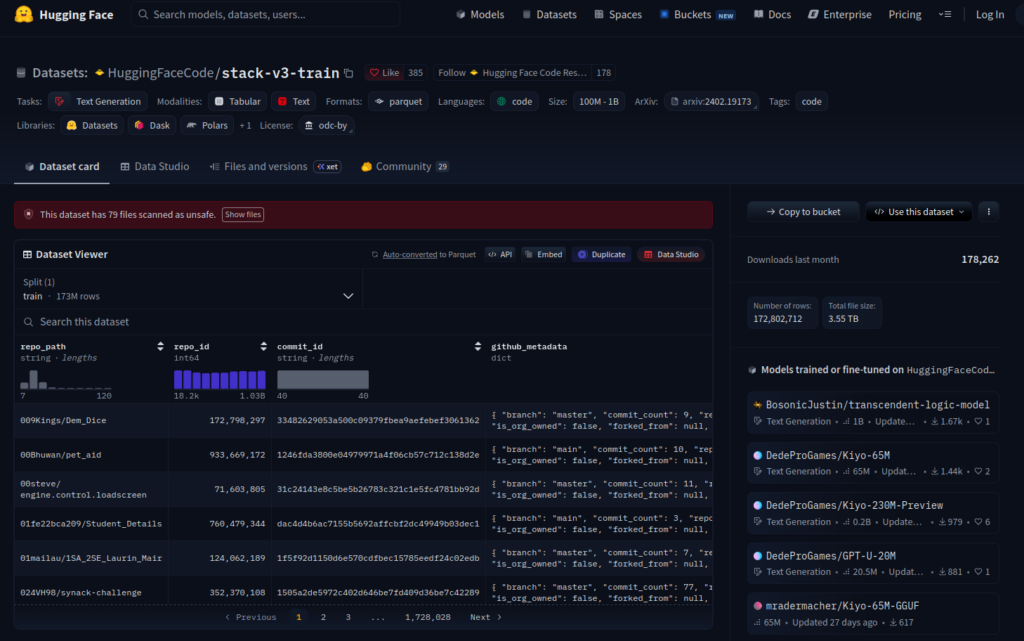
Truffle Security found 543,699 still-valid credentials inside code from public GitHub repositories after analyzing The Stack v3 dataset, which was built from about 224 million repositories. The research showed exposed API keys, access tokens, database credentials, and service accounts, and recommends revoking or rotating any leaked credentials because they may already exist in forks or copies of the repository. #Truffle Security #GitHub #The Stack v3 #Hugging Face #TruffleHog
Keypoints
- Truffle Security identified 543,699 valid credentials in code sourced from public GitHub repositories.
- The analysis was performed on The Stack v3, a 15.9 TB public dataset used for training code-focused AI models.
- The dataset was assembled from roughly 224 million GitHub repositories.
- Exposed secrets included API keys, access tokens, database credentials, and service account credentials.
- The average age of still-working credentials was 784 days, with some remaining unrevoked for years.
- Truffle Security noted that exposed credentials may also exist in forks, copies, or other files, so they should be considered compromised immediately.
- CERT-AGID recommends checking exposure with Hugging Face’s “Am I in The Stack?” service and scanning organization repositories with TruffleHog.
MITRE Techniques
- [T1552.001] Credentials In Files – Credentials were found embedded in source code from public GitHub repositories, exposing API keys, access tokens, database credentials, and service account secrets. (‘543.699 credenziali ancora valide all’interno di codice proveniente da repository pubblici GitHub’)
- [T1078] Valid Accounts – The leaked credentials were still usable, meaning an attacker could potentially authenticate with legitimate accounts and services. (‘credenziali ancora valide’ / ‘ancora funzionanti’)
- [T1213] Data from Information Repositories – The exposed secrets were discovered in publicly available repository content and related copies/forks. (‘una volta pubblicata, una credenziale può essere già presente in altri file, fork o copie del repository’)
Indicators of Compromise
- [Credential types] Exposed secrets found in public GitHub code – API keys, access tokens, database credentials, service account credentials
- [Dataset] Source dataset analyzed for exposed secrets – The Stack v3, 15.9 TB, about 224 million GitHub repositories
- [Tool commands] Repository scanning examples – trufflehog github –org=NOME_ORGANIZZAZIONE, trufflehog git https://github.com/USERNAME/REPOSITORY
- [Service name] Exposure-checking service mentioned by CERT-AGID – Am I in The Stack?