An autonomous AI agent breached the Dutch Institute for Vulnerability Disclosure (DIVD) by chaining two zero-day vulnerabilities in Zammad, moving from session hijack to root access in seconds and exfiltrating data. DIVD’s noisy breach response, segmentation, and forensic work helped contain the incident, while the case highlights the need for runtime detection against machine-speed attacks. #DIVD #Zammad #CVE-2026-102489 #CVE-2026-102490 #MerlonSecurity #Sysdig #JADEPUFFER

Ransomware group settra claimed to have exfiltrated 435 GB from hollypoultry.com, a victim identified as Holly Poultry, involving data tied to FEIN 25-1434395 and reported in October 2026. The claim was attributed to activity impacting the United Kingdom. #UnitedKingdom
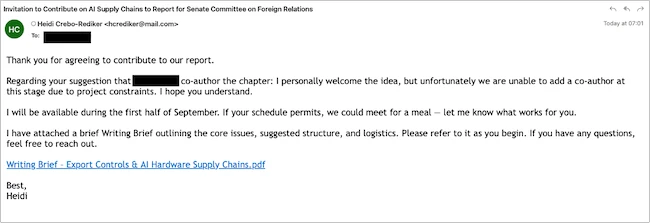
TA419, a China-aligned espionage group, posed as former White House officials and other prominent figures to target US AI policy experts with credential phishing campaigns in 2026. The operation used fake OneDrive login pages, browser-in-the-browser tricks, and cloud infrastructure to steal Microsoft credentials, session cookies, and access to victim accounts. #TA419 #LynneEdwardsParker #HeidiCreboRediker #Anthropic #WhiteHouseOfficeofScienceandTechnologyPolicy
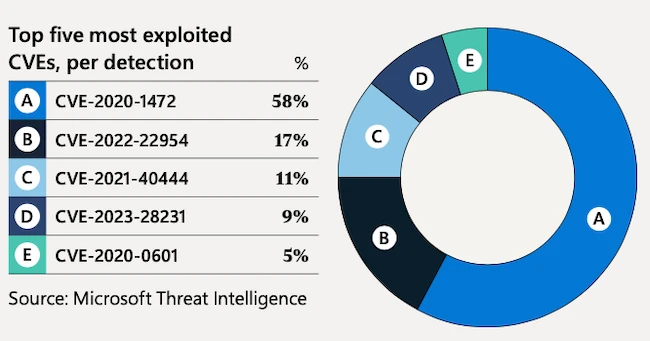
Threat actors are increasingly using AI to accelerate vulnerability discovery, phishing, malware development, and intrusion operations, shrinking the time from bug discovery to weaponization to under 24 hours. Microsoft warns that state-backed and criminal groups are already adopting AI across the attack lifecycle, while autonomous attacks, AI-driven ransomware, and self-spreading worms are moving closer to reality. #Microsoft #Anthropic #OpenAI #ClaudeCode #GeminiCLI #AmazonQ #s1ngularity #PromptLock #JADEPUFFER #Axios #HuggingFace

Daily Recap, AI security coverage focused on a China-linked phishing campaign targeting AI policy circles, while OpenAI and Anthropic face an FTC probe and new research examined how AI changes vulnerability discovery, distillation attacks, and SOC hiring expectations. In addition, Cisco patched an actively exploited Catalyst SD-WAN zero-day (CVE-2026-76504), major exposure incidents hit GitHub credentials, and multiple industries addressed fallout from Artifactory breaches, MetaMask validator disruptions, and Bitget theft tied to a third-party zero-day. #China #TA419 #OpenAI #Anthropic #FTC #CatalystSDWAN #CVE-2026-76504 #Cisco #SDWANManager #Pentagon #GitHub #JFrog #Artifactory #OpenInfra #MetaMask #Ethereum #Bitget #RedFlick #KillSec #RedFlick #MSP360 #ScreenConnect #EntraID #Microsoft #Thales #SentinelEnvelopePlus
Microsoft confirmed that its official X account was taken over and used to promote a Clippy-themed cryptocurrency account, with its profile picture changed and unauthorized posts published. The incident was later removed, and Microsoft said it was investigating how the account was accessed. #Microsoft #Clippy #MSFT #X…

Researchers found CloudSyncD hidden inside a fake Zoom macOS installer, where it uses social engineering to trick victims into entering their password and launching the malware. The campaign has moved from testing to deployment, delivering a persistent backdoor that profiles the host, communicates with C2 infrastructure, and avoids traditional infostealer behavior….

SecurityWeek’s weekly roundup covers major cybersecurity developments, including Microsoft’s warning that phishing and AI-assisted attacks are accelerating while exploitation windows shrink to less than a day. It also highlights critical issues affecting Kiteworks, iCloud, Cloudflare, Android apps, and targeted espionage campaigns by TA419 against US policy experts. #Microsoft #Kiteworks #iCloud #Cloudflare…
Dell has patched six critical vulnerabilities in Container Storage Modules that connect its enterprise storage arrays to Kubernetes environments, including flaws that could let unauthenticated attackers gain full administrative control. The issues affect Dell CSM Authorization, proxy, and tenant services, and Dell urges customers to upgrade to version 1.18.0 or later as soon as possible. #DellCSM #CVE202663688 #CVE202663692 #CVE202667269 #CVE202654472 #CVE202661421 #CVE202667273
EDR is still essential for detecting host execution, but it can miss attacks that stay inside browser-based SaaS sessions, identity workflows, and cloud applications. The article explains how browser controls, identity protections, and SaaS-specific policies can stop threats like AiTM phishing, malicious extensions, and ClickFix attacks before they reach endpoint telemetry. #UNC6395 #SalesloftDrift #Storm2755 #Microsoft365 #Workday #TerminalFix #NordLayerBrowser
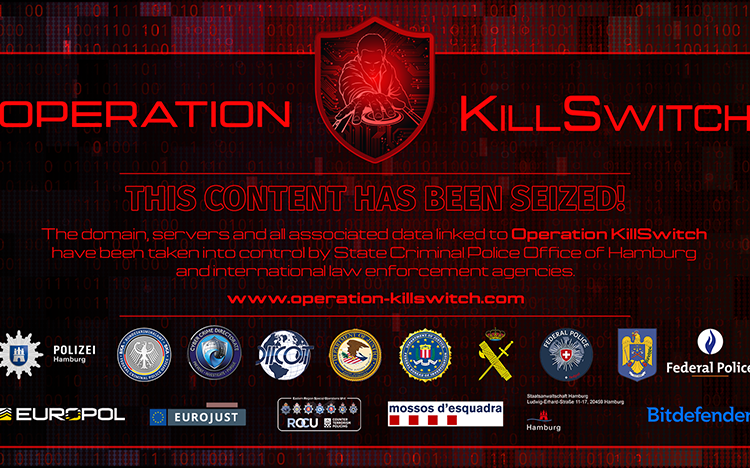
KillSec, active since 2024, used poorly secured cloud-linked access points to break into organisations, steal data, and extort victims by threatening public leaks. An international investigation led to arrests, seizures of infrastructure and stolen data, and ongoing efforts to trace the group’s financial proceeds and identify more victims and suspects. #KillSec #Eurojust #Europol
Ransomhouse ransomware actors are alleged to have targeted PT Indo Tambangraya Megah in Indonesia, potentially disrupting mining operations. PT Indo Tambangraya Megah (founded in 1987) is a leading Asian coal producer, and the claim centers on impacts to its business continuity in the country. #Indonesia
Inova Semiconductors GmbH in Germany reported a ransomware incident attributed to the qilin threat actor, though specific details of the attack (N/A) were not provided. The incident resulted in disruption consistent with ransomware activity in #Germany
Pacific Tank Lines, Inc., a petroleum cargo company based in {blank}, reported a ransomware claim by the akira threat actor, alleging imminent release of 13GB of corporate data. The attackers purportedly accessed sensitive information including personal records for 118 employees, financial data, and client details, impacting all involved affected countries as #countryname
Unknown attackers hijacked Microsoft’s official X account and used it to promote a crypto token in what appeared to be a pump-and-dump scheme. Microsoft removed the unauthorized posts, secured the account, and said it is investigating while also warning it will pursue legal action over the misuse of its brand and Clippy intellectual property. #Microsoft #X #Clippy #MSFT #MicrosoftIndia #SECGov